
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
73 results
MercilessAmd preview

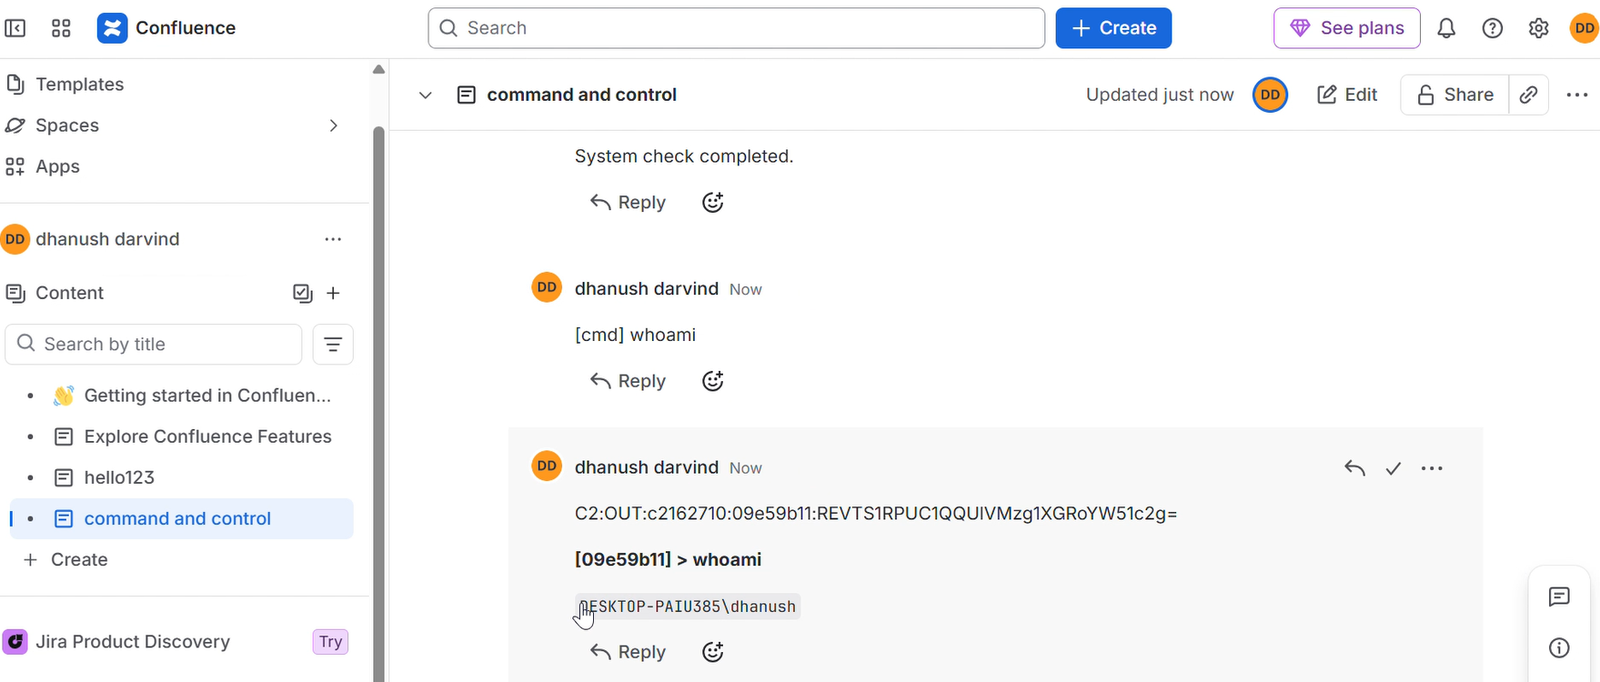
MercilessAmd

GitHubmein-0/mercilessamd

Proof-of-concept exploiting AMD AmdTools64.sys MSR read/write IOCTLs to overwrite IA32_LSTAR, bypass SMEP and escalate from administrator to SYSTEM…
binary-exploitationexploitationprivilege-escalation+4
4 days ago
ConfluenceC2 preview

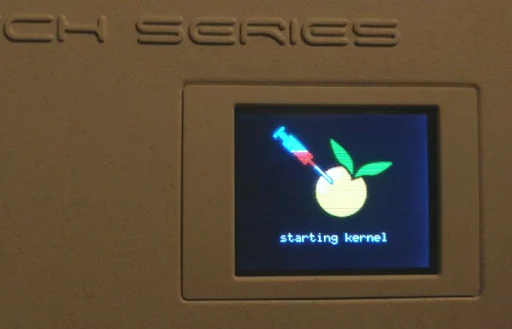
ConfluenceC2

GitHubdagowda/confluencec2

This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
command-and-controldata-exfiltrationlateral-movement+9
2112 days ago
Chimay-Red preview

Chimay-Red

GitHubbignerd95/chimay-red

Working POC of Mikrotik exploit from Vault 7 CIA Leaks
binary-exploitationembedded-systems-securityexploitation+8
6694 years ago
glimmer preview

glimmer

GitHublinnemanlabs/glimmer

Adversary emulation and C2 framework for security research

command-and-controlcryptographydata-exfiltration+8
65 months ago
LazZzy_Dump preview

LazZzy_Dump

GitHubtrustedsec/lazzzy_dump

Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…

binary-analysiscode-analysisdigital-forensics+6
11 month ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…
binary-exploitationdefensive-toolseducation+7
514 days ago
CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter preview

CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter

GitHubsneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter

Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.

binary-exploitationexploitationmemory-forensics+3
51 month ago
radare2-scripts preview

radare2-scripts

GitHubwithsecurelabs/radare2-scripts

Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
binary-analysisdigital-forensicsmalware-analysis+3
328 years ago
ThreadlessInject preview

ThreadlessInject

GitHubccob/threadlessinject

Threadless Process Injection using remote function hooking.

adversarial-attackpayload-developmentpayload-generation+4
8242 years ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.2k1 month ago
nasm_linux_x86_64_pure_sharedlib preview

nasm_linux_x86_64_pure_sharedlib

GitHubtherealdreg/nasm_linux_x86_64_pure_sharedlib

NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection

exploitationpayload-developmentpost-exploitation+2
323 years ago
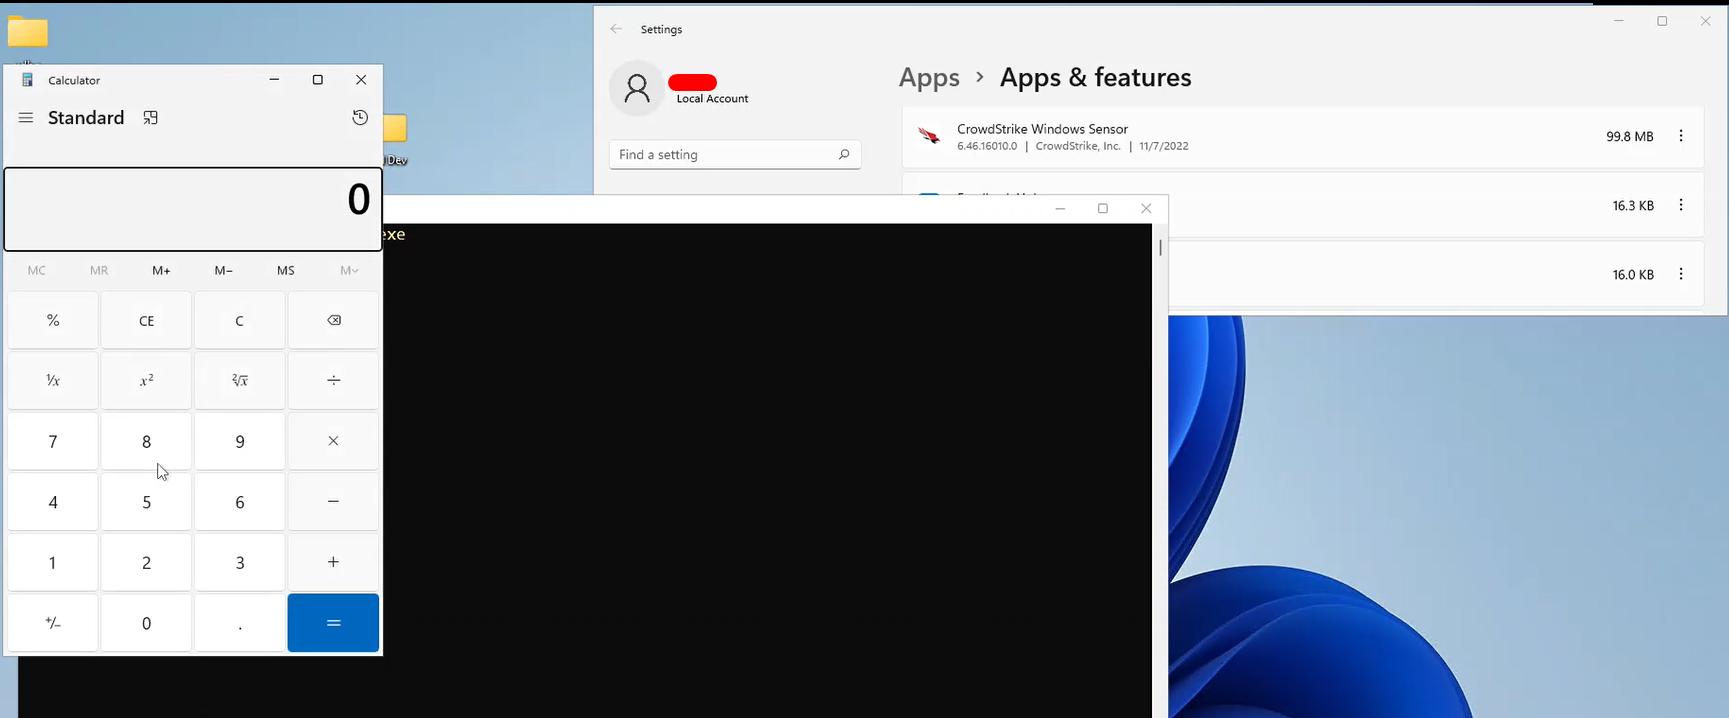
NimShellcodeFluctuation preview

NimShellcodeFluctuation

GitHubs3cur3th1ssh1t/nimshellcodefluctuation

ShellcodeFluctuation PoC ported to Nim
adversarial-attackpayload-developmentpost-exploitation+2
774 years ago
D1rkLdr preview

D1rkLdr

GitHubsaadahla/d1rkldr

Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…

ids-ips-evasionpayload-developmentred-teaming+1
3233 years ago
DEFCON-31-Syscalls-Workshop preview

DEFCON-31-Syscalls-Workshop

GitHubvirtualalllocex/defcon-31-syscalls-workshop

Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".

educationlabs-practicepayload-development+2
7731 year ago
DataInject-BOF preview

DataInject-BOF

GitHubiilegacyyii/datainject-bof

Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
binary-exploitationexploitationpayload-development+3
1551 year ago
ManualRsrcDataFetching preview

ManualRsrcDataFetching

GitHubnul0x4c/manualrsrcdatafetching

Get your data from the resource section manually, with no need for windows apis

binary-analysispayload-developmentred-teaming+1
672 years ago
bin2shell preview

bin2shell

GitHubtouhidshaikh/bin2shell

bin2shell is very small utils for extract shell code from the binary file
exploitationpayload-developmentpayload-generation+3
129 years ago
asminject preview

asminject

GitHubbishopfox/asminject

Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…

container-escapepayload-developmentpenetration-testing+2
1484 years ago
Previous12345Next