house_of_apple_2
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
binary-exploitationdebuggerseducation+7
5
jazho76/house_of_apple_2Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 buzzer-re/shinigami
A dynamic unpacking tool
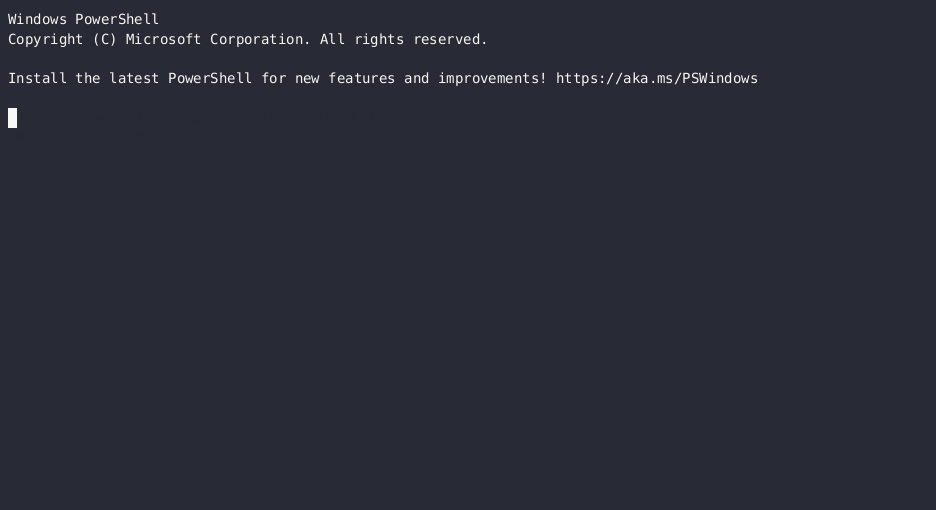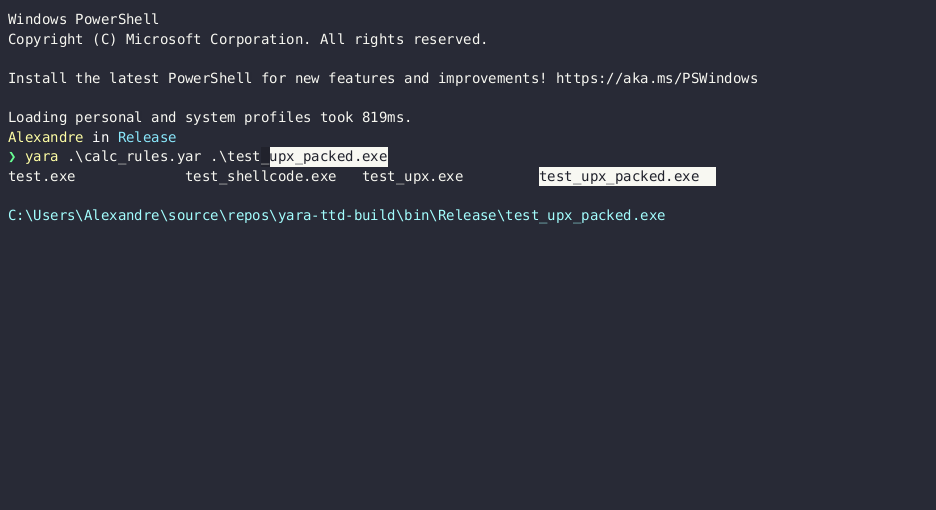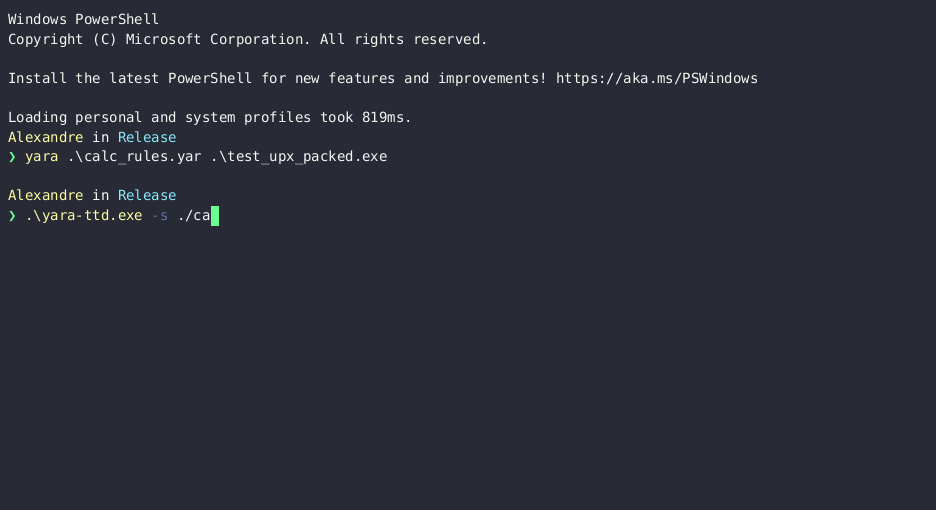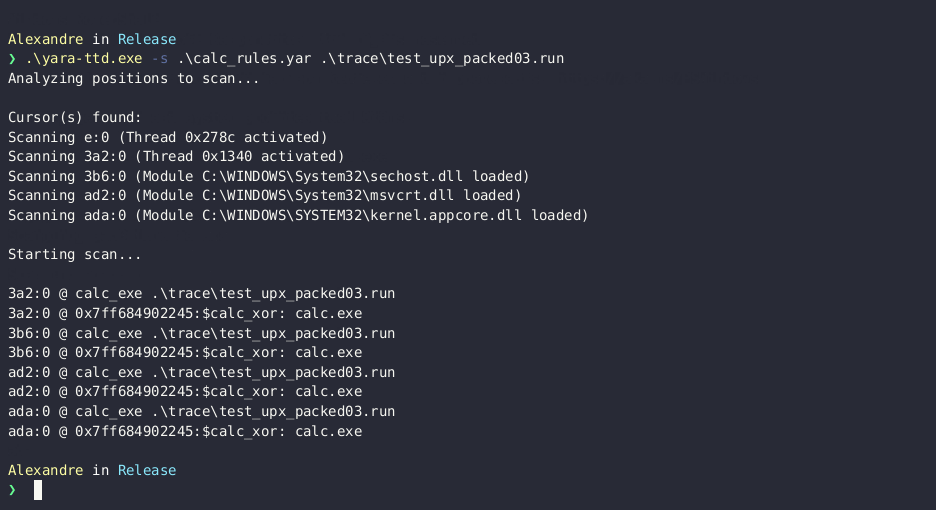 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 buffer/pylibemu
A Libemu Cython wrapper
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 struppigel/hedgehog-tools
Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
 cecio/xenoboxx
Hardware Sandbox Toolkit
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 oddcod3/phantom-evasion
Python antivirus evasion tool