
MS09-050
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
exploitationinformation-gatheringnetwork-security+7
bytejmp/ms09-050Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
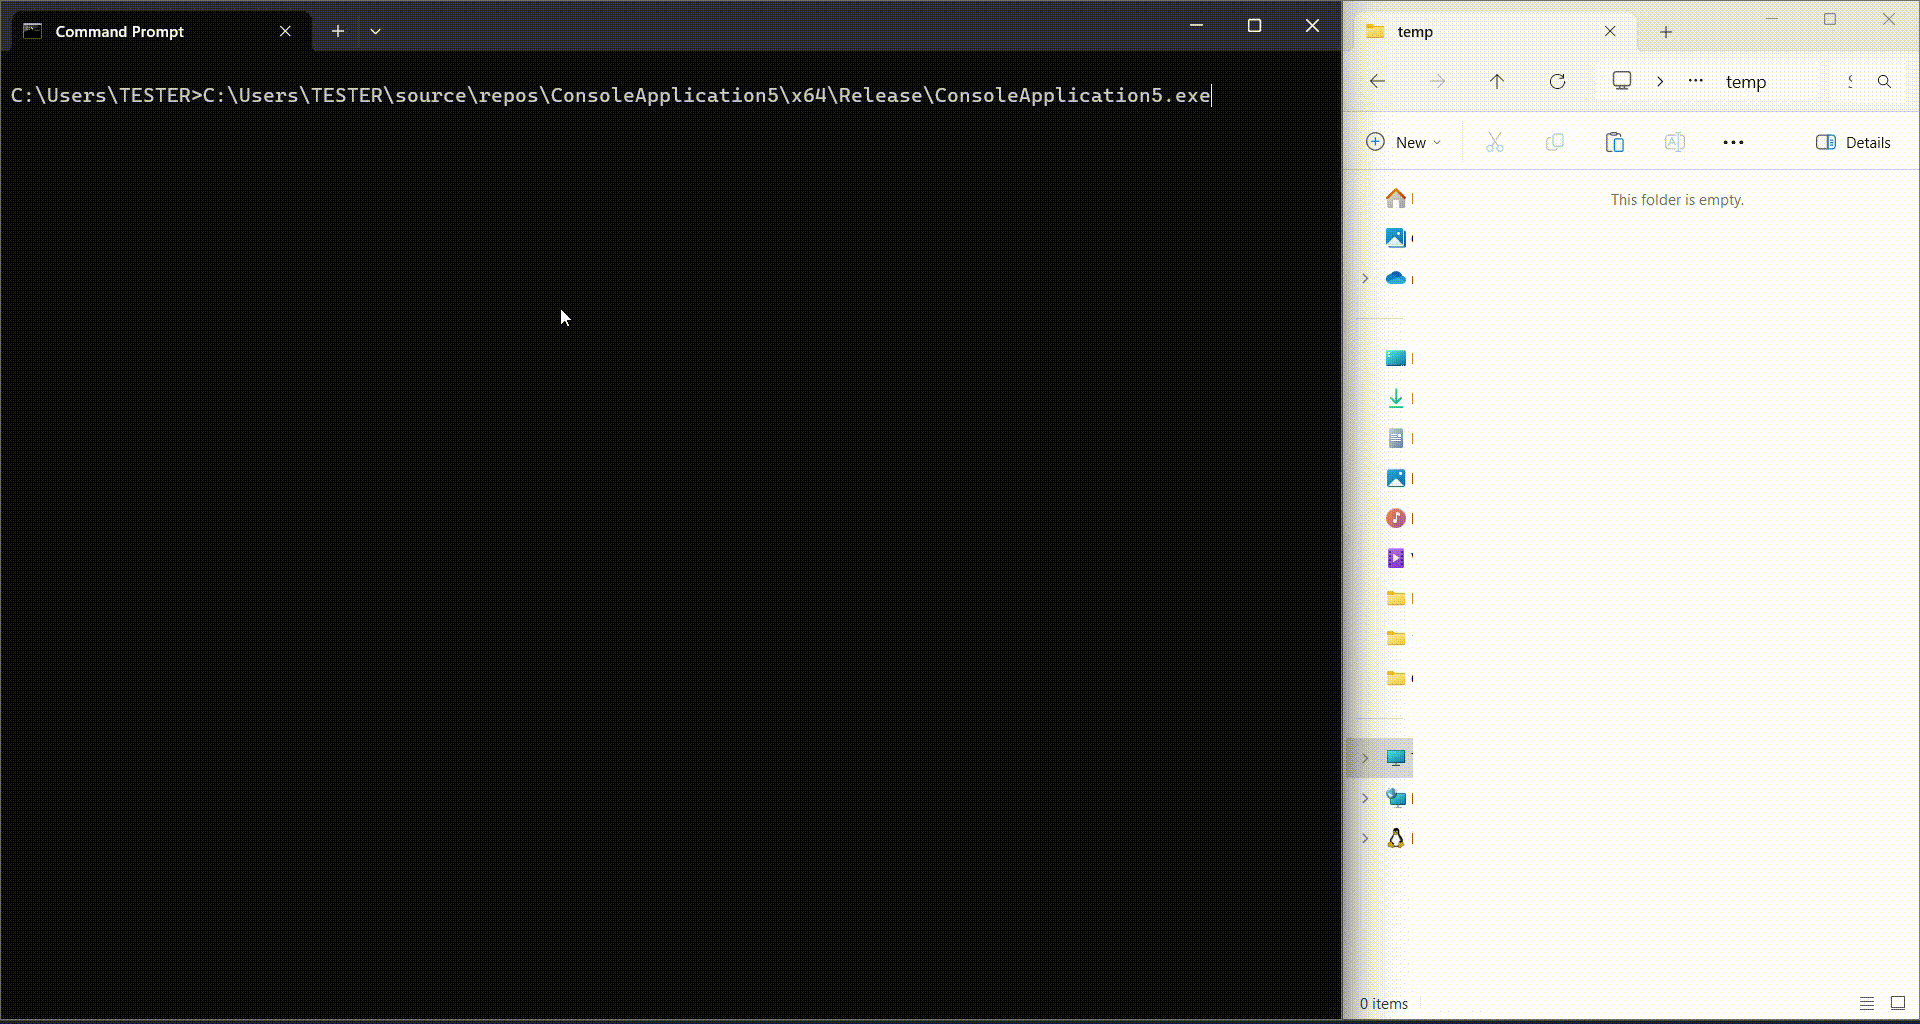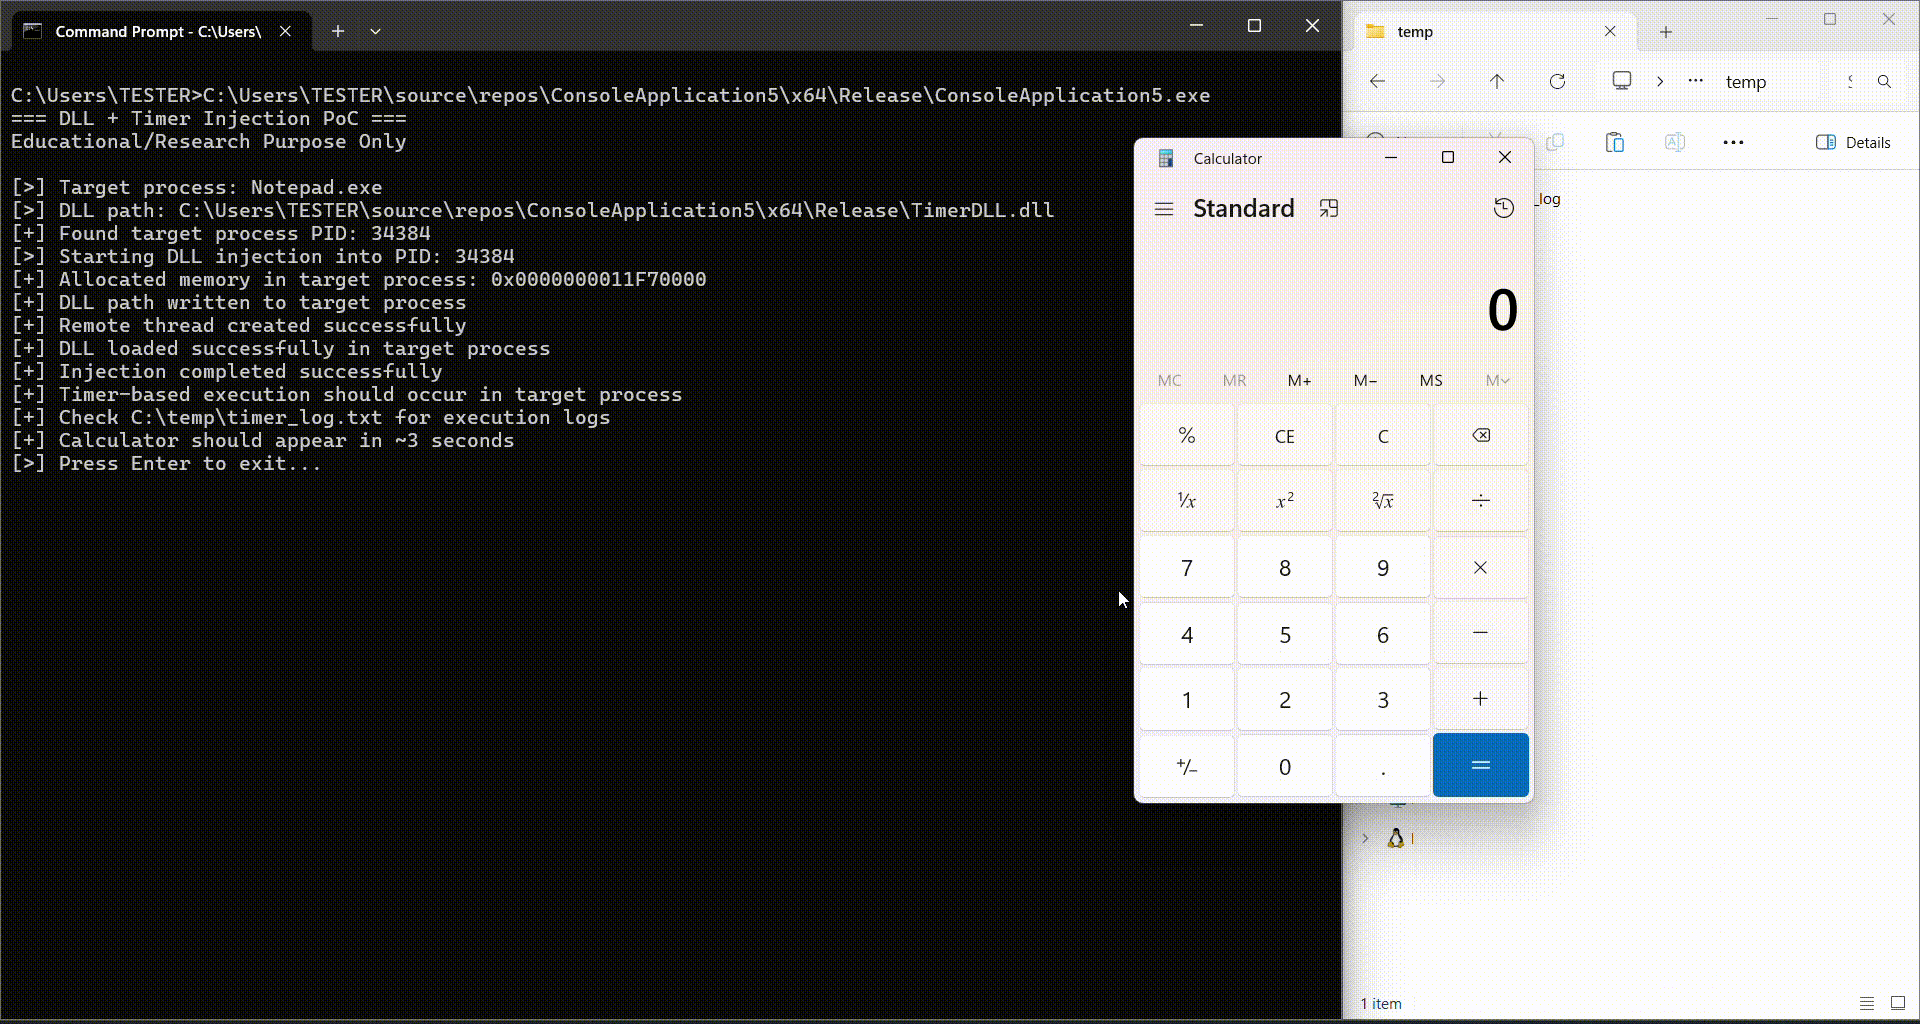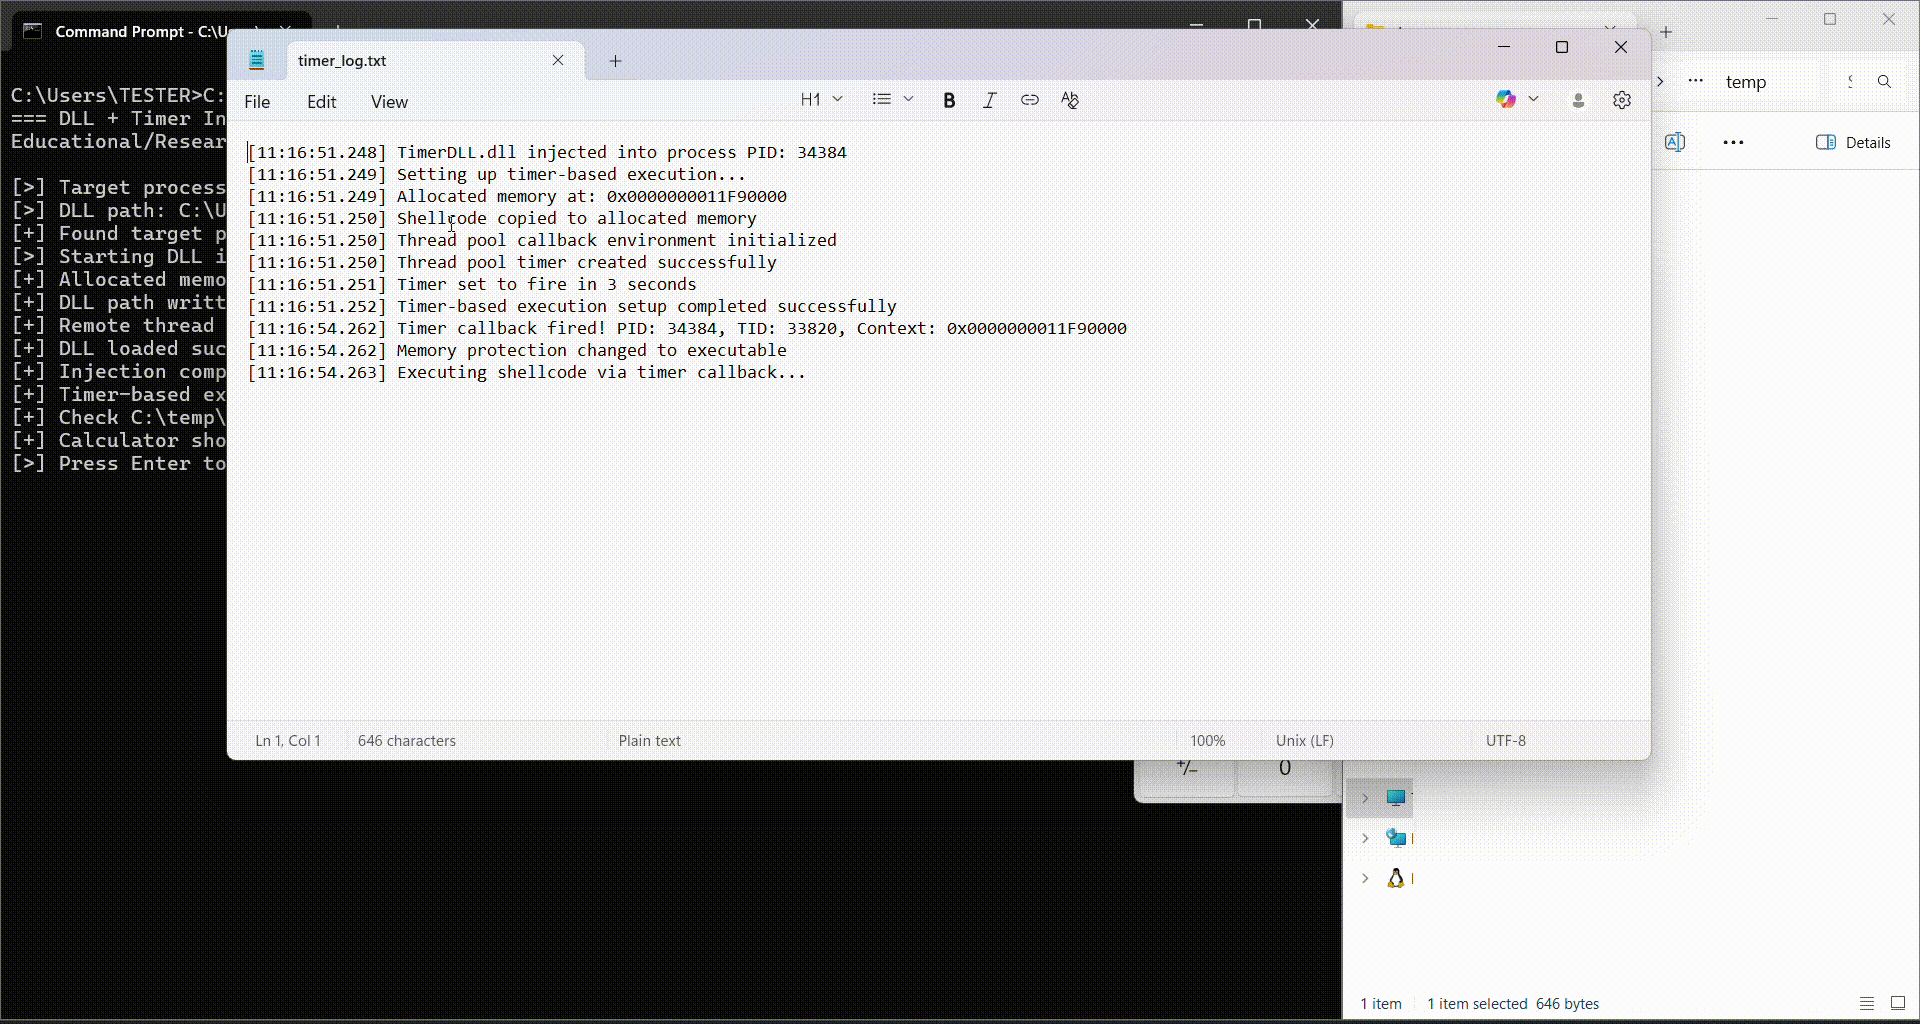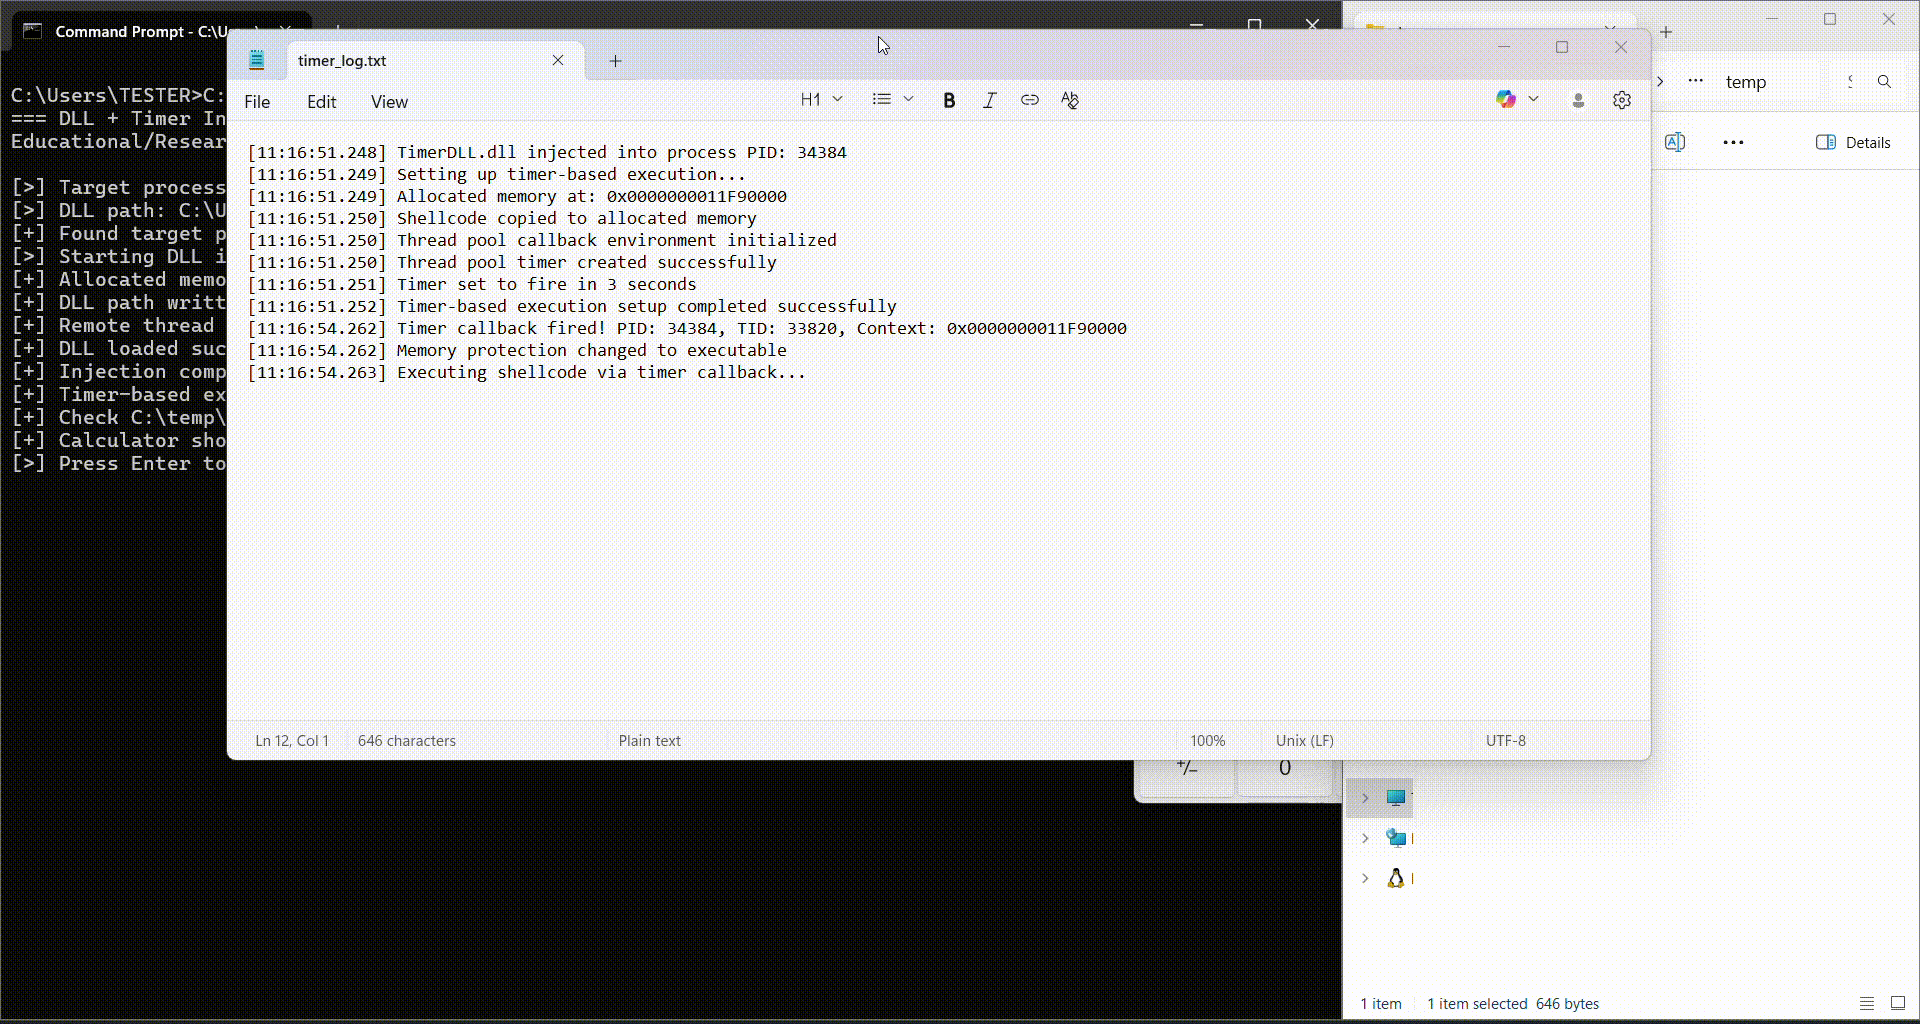 andreisss/remote-dll-injection-with-timer-based-shellcode-execution
Remote DLL Injection with Timer-based Shellcode Execution
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 wireghoul/htshells
Self contained htaccess shells and attacks
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
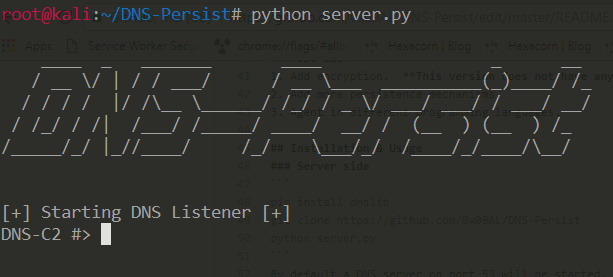 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 smaash/quasibot
complex webshell manager, quasi-http botnet.
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 makavellik/poc-cve-2021-42013-exploit
Una herramienta avanzada de escaneo, explotación e interacción remota diseñada para detectar y aprovechar la vulnerabilidad Apache Path Traversal +…
 nxploited/cve-2025-7955
RingCentral Communications 1.5 - 1.6.8 - Missing Server‑Side Verification to Authentication Bypass via ringcentral_admin_login_2fa_verify Function
 mind2hex/cve-2023-38035-mobileiron-rce
Script to exploit CVE-2023-38035
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 zhzyker/exphub
Exphub[漏洞利用脚本库] 包括Webloigc、Struts2、Tomcat、Nexus、Solr、Jboss、Drupal的漏洞利用脚本,最新添加CVE-2020-14882、CVE-2020-11444、CVE-2020-10204、CVE-2020-10199、CVE-2020-1938…