

Empire
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
bc-security/empireEmpire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
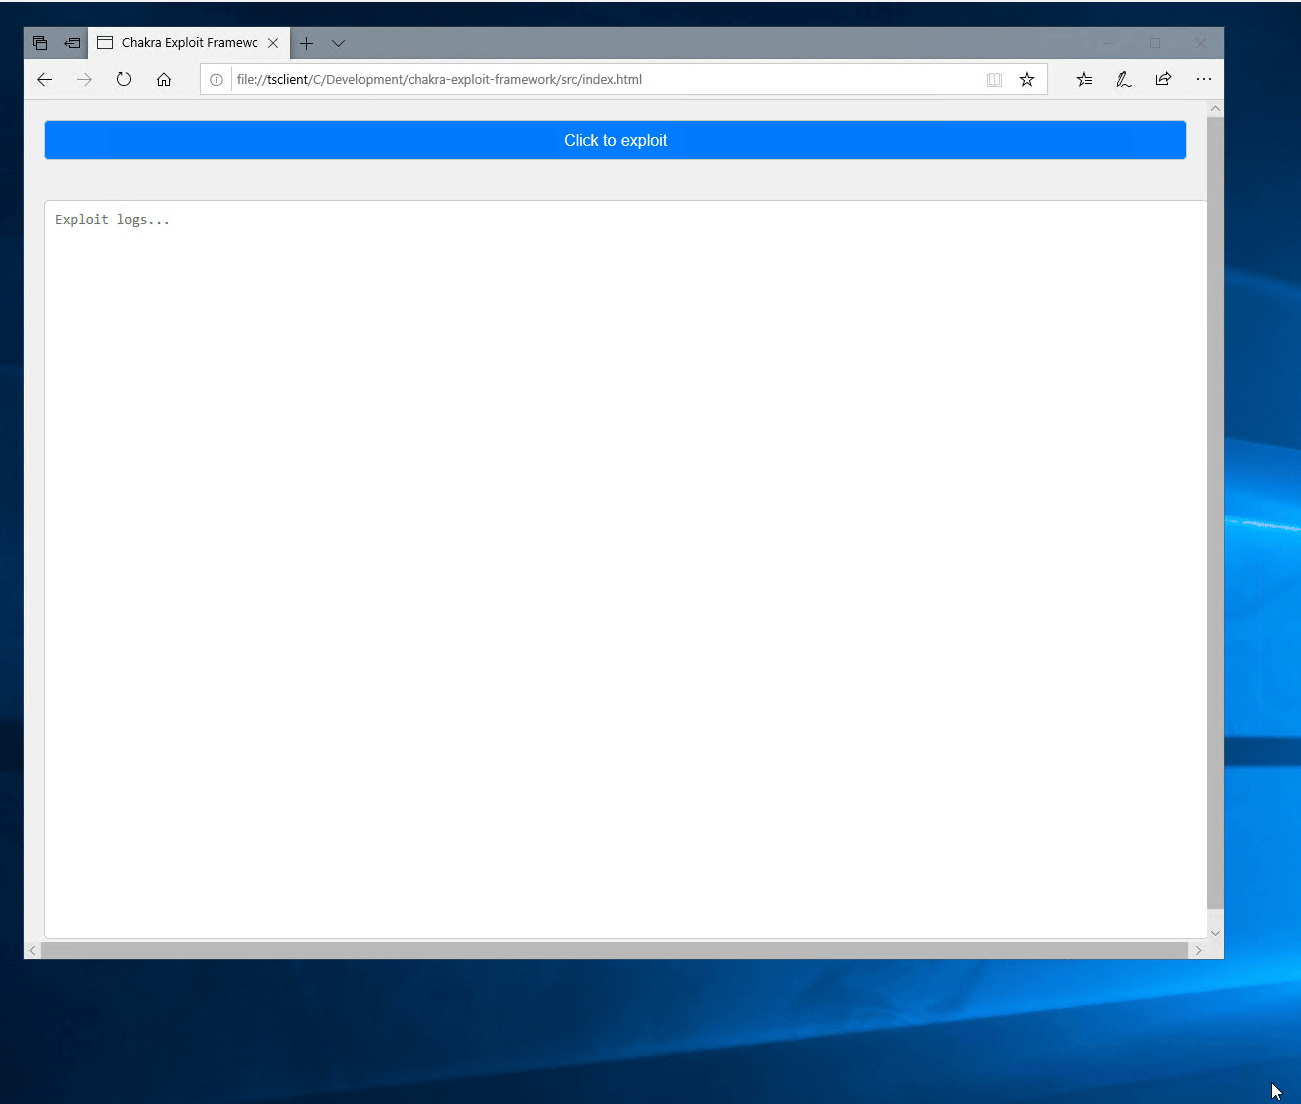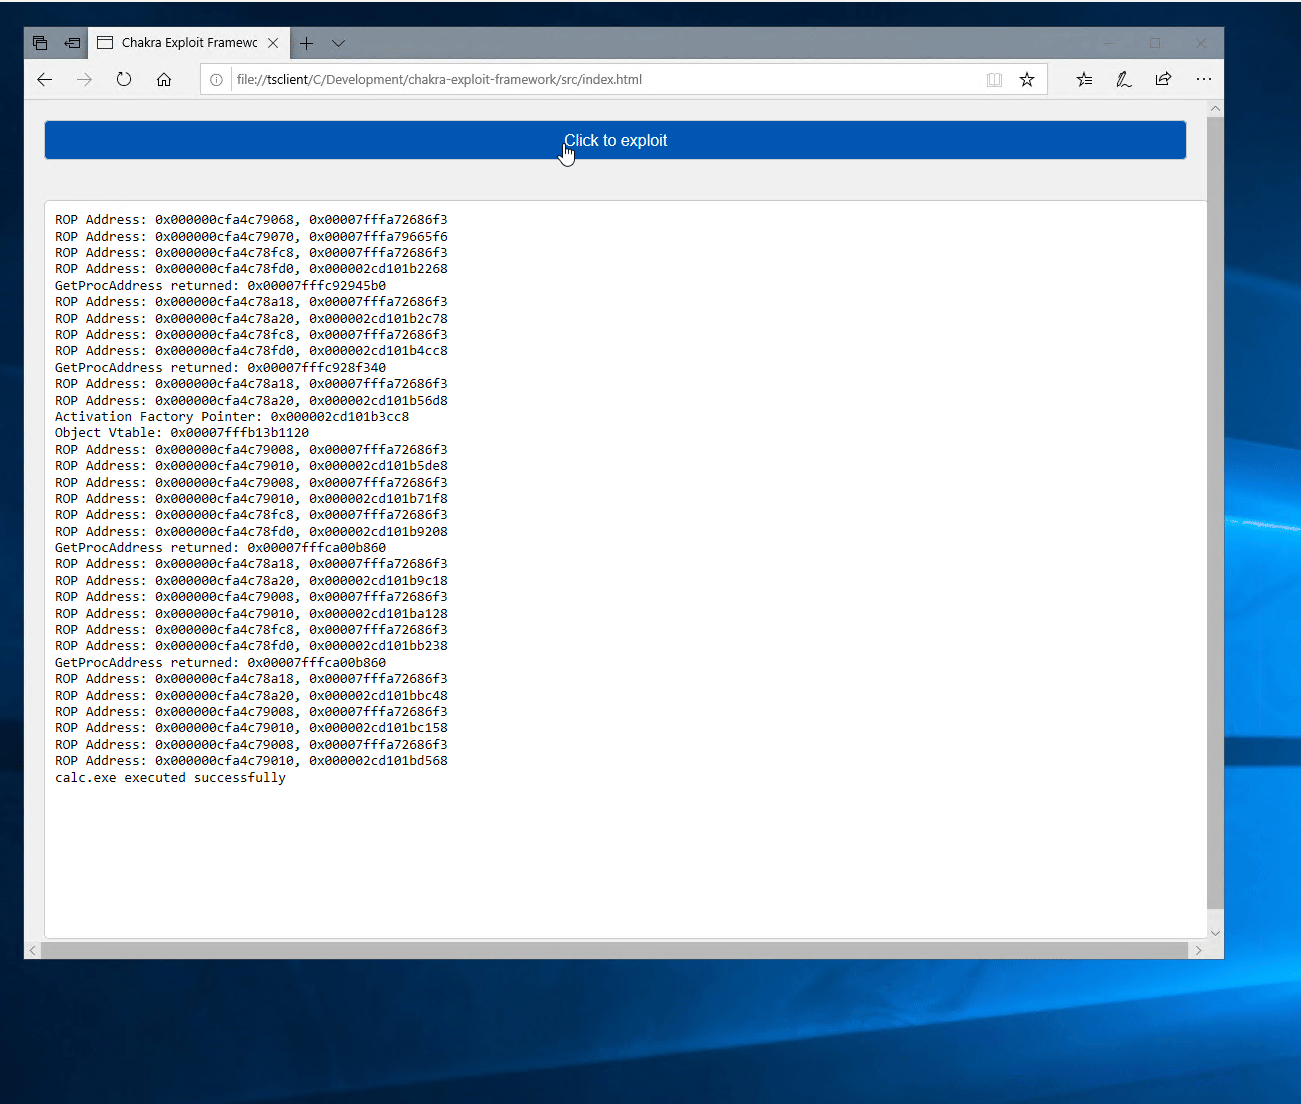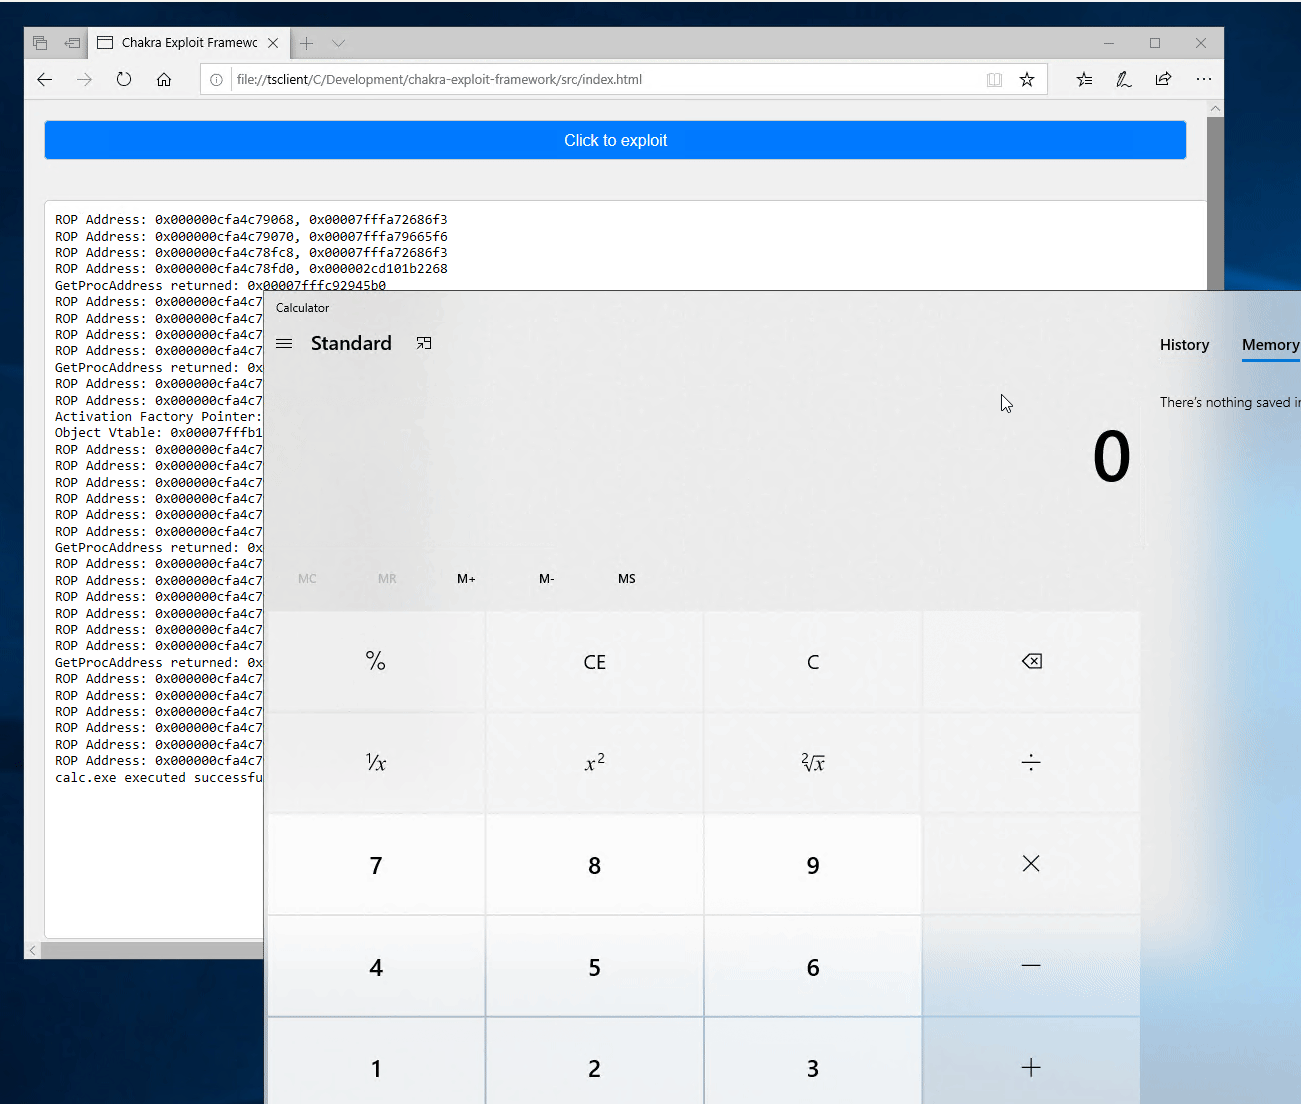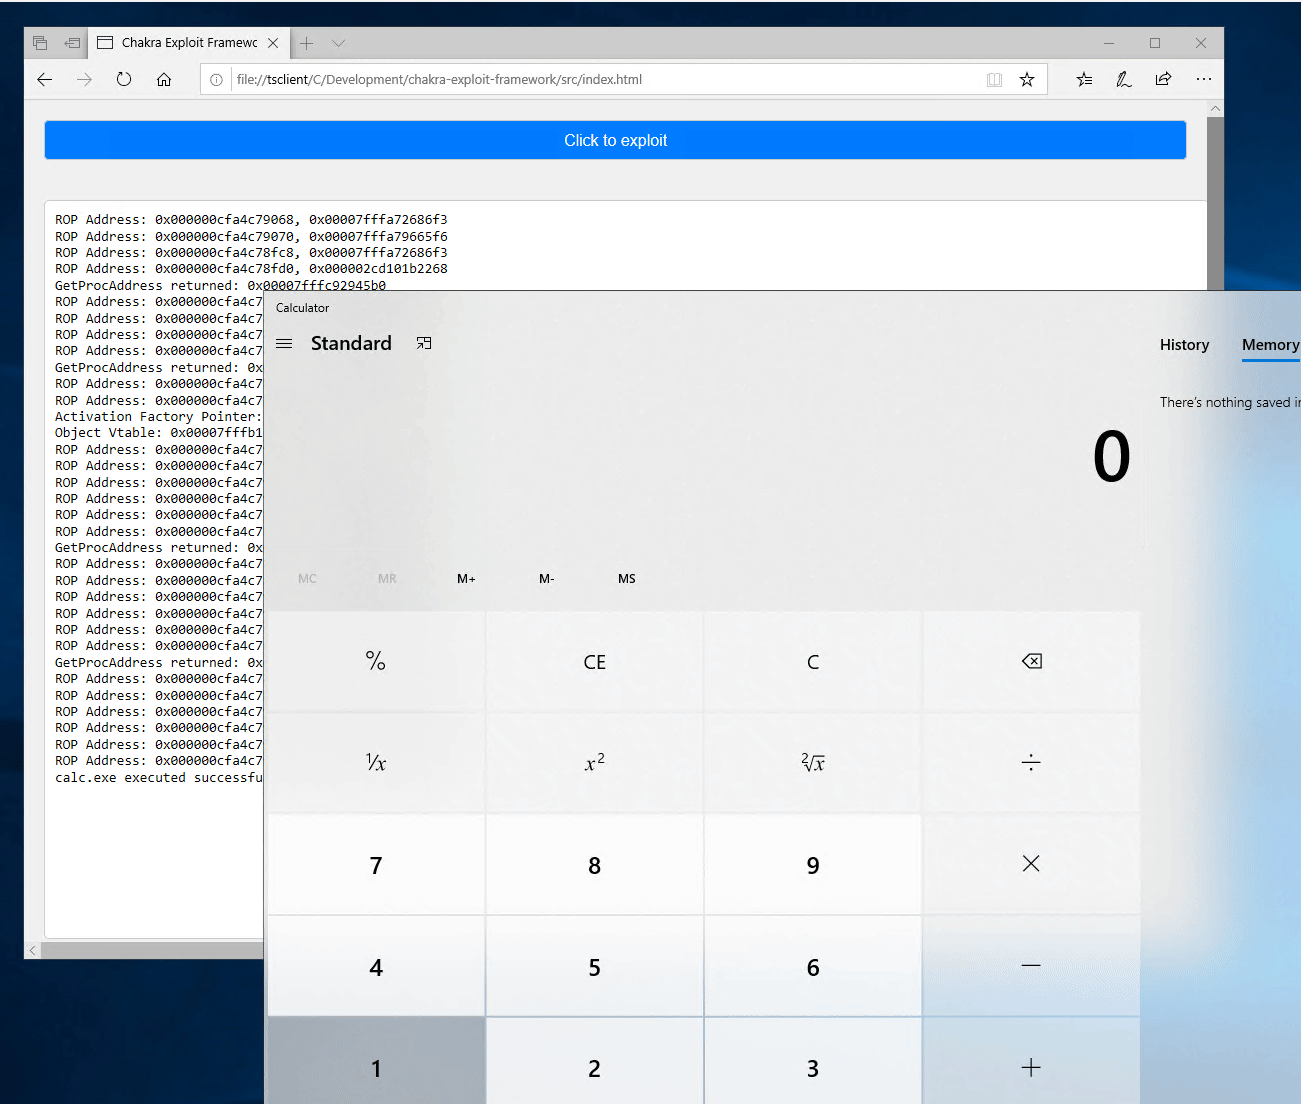 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…

 gallopsled/pwntools
CTF framework and exploit development library
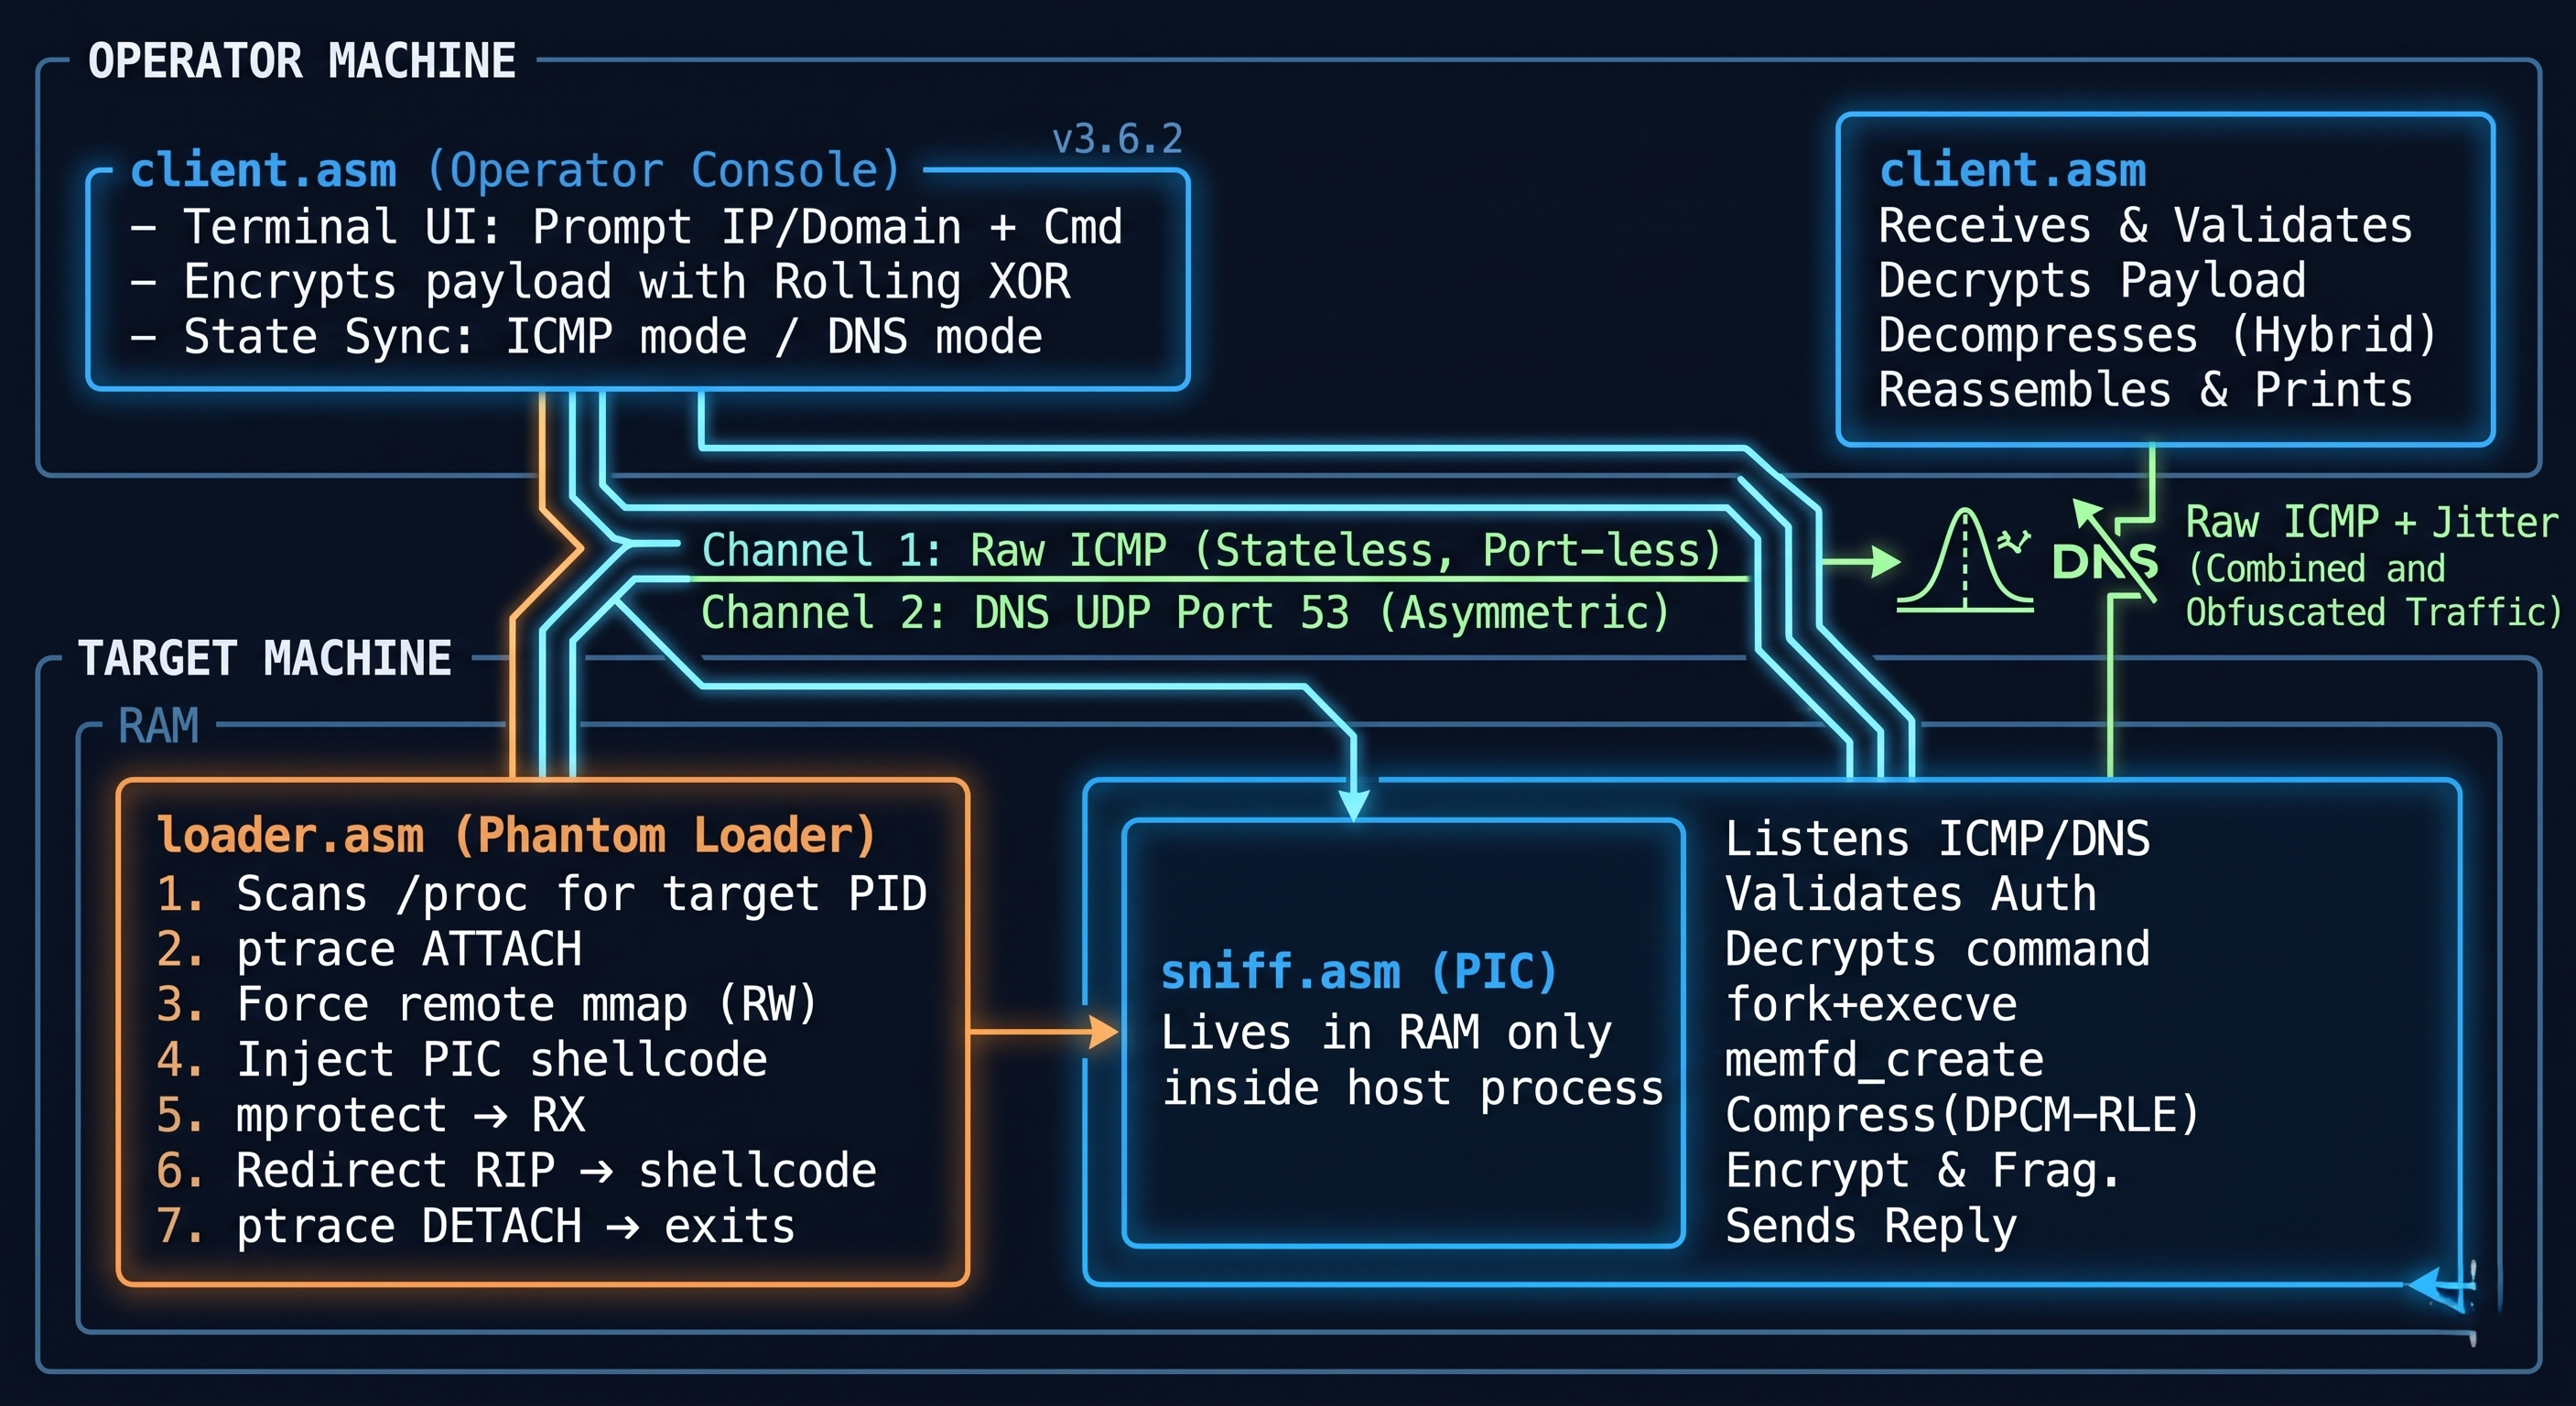 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
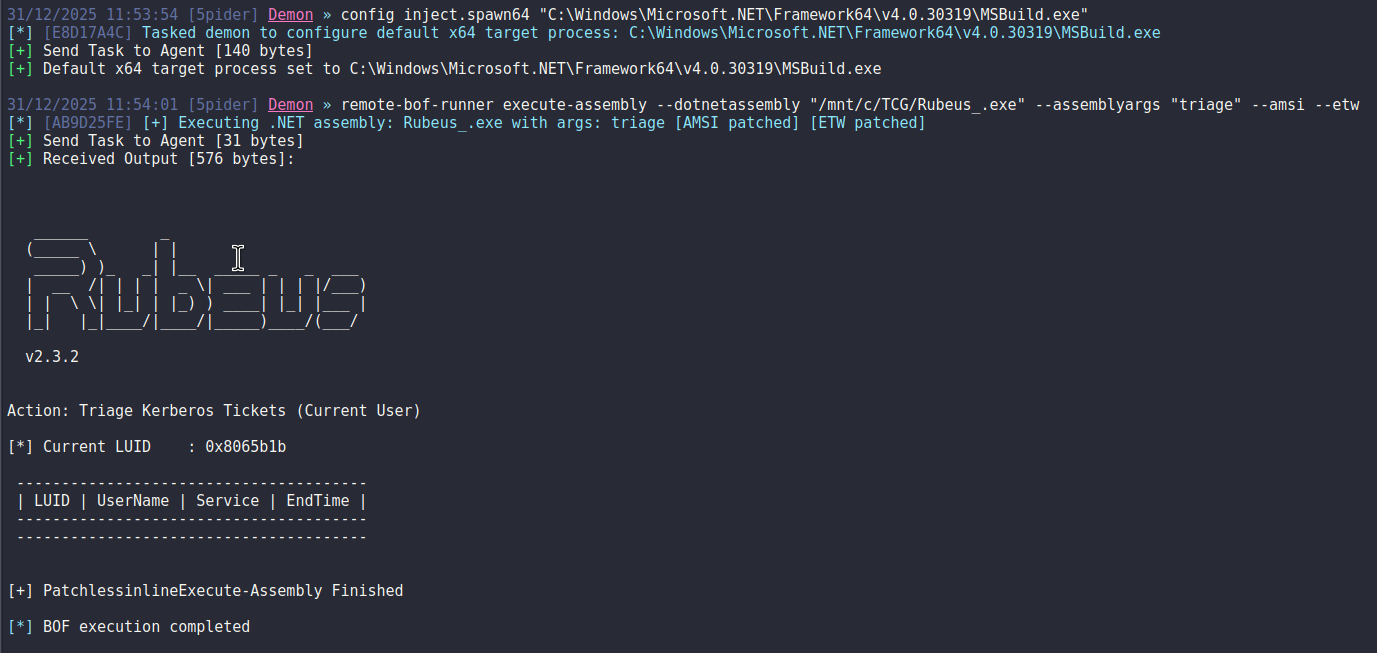 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 codextf2/cobaltstrike_bofloader
open source port/reimplementation of the Cobalt Strike BOF Loader as is
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…