

KDU
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
binary-exploitationdefensive-toolsexploitation+8
hfiref0x/kduWindows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 gmh5225/anti_suspend
Protect process by shellcode
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
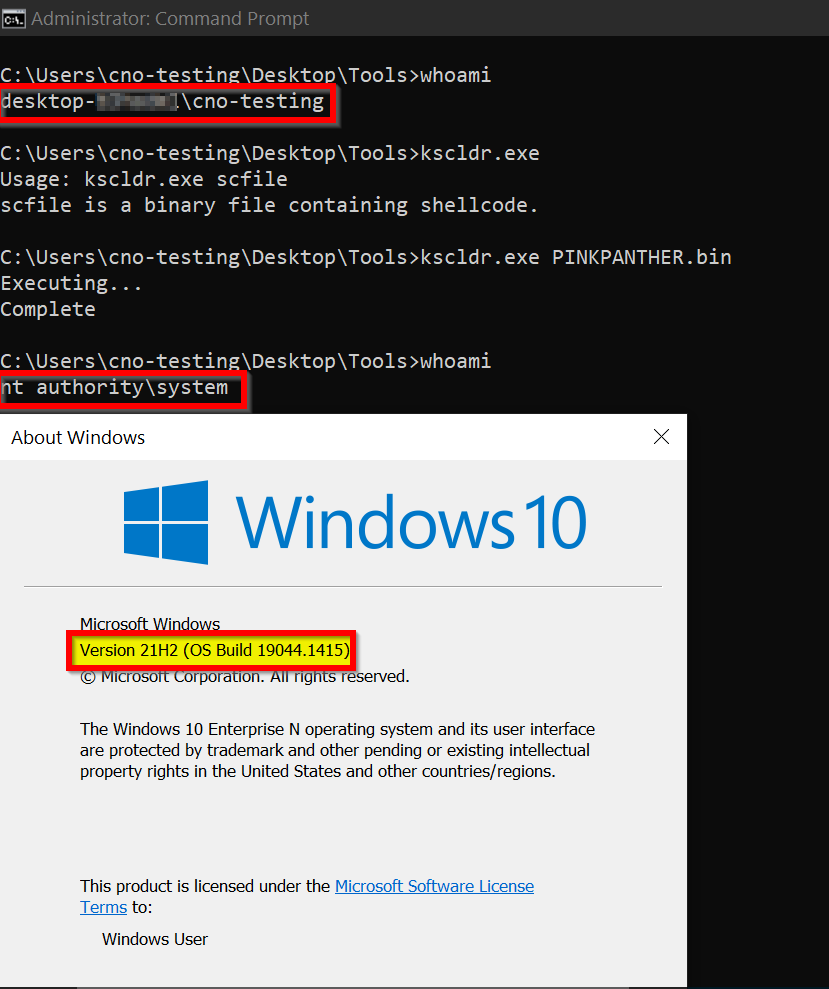 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 buzzer-re/shinigami
A dynamic unpacking tool

 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 d0rb/logofail-poc
This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.
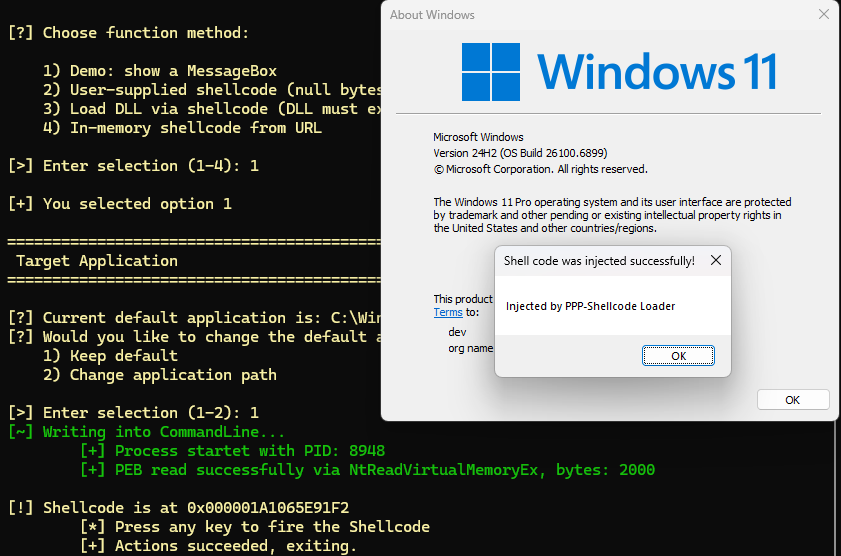 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
 ustayready/wnfexec
WNF Code Execution Library Using C#
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 mind2hex/cve-2023-38035-mobileiron-rce
Script to exploit CVE-2023-38035
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…