

memory-relocalloc
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…
binary-exploitationexploitationmalware-analysis+6
gmh5225/memory-relocallocC proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 gmh5225/anti_suspend
Protect process by shellcode
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 buzzer-re/shinigami
A dynamic unpacking tool

 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 d0rb/logofail-poc
This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.
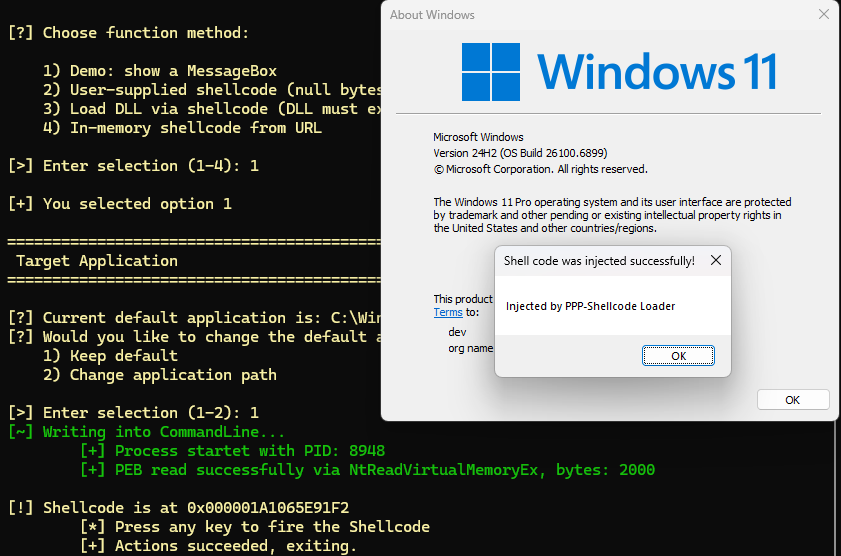 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
 ustayready/wnfexec
WNF Code Execution Library Using C#
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar