
CVE-2017-13089
 mzeyong/cve-2017-13089
CVE-2017-13089
exploitationpayload-generationpenetration-testing+2
mzeyong/cve-2017-13089CVE-2017-13089
 lowkey0808/cve-2022-29464
Python exploit for CVE-2022-29464 targeting WSO2 web servers with automated webshell upload and command execution capabilities.
 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.
 ruthvikvegunta/drupalgeddon2
CVE-2018-7600 | Drupal < 7.58 / < 8.3.9 / < 8.4.6 / < 8.5.1 - 'Drupalgeddon2' RCE
 substing/cve-2019-11447_reverse_shell_upload
Python exploit for CVE-2019-11447 that uploads a PHP reverse shell to CuteNews 2.1.2, enabling remote command execution on vulnerable web…
 kai-one001/wordpress-ht-contact-cve-2025-7340-rce
Python exploit for CVE-2025-7340, an unauthenticated file upload vulnerability in the WordPress HT Contact Form widget, enabling remote code…
 zaphoxx/zaphoxx-coldfusion
coldfusion exploit based on https://cvedetails.com/cve/CVE-2009-2265/
 randallbanner/spring-cloud-function-vulnerability-cve-2022-22963-rce
Python exploit for CVE-2022-22963 (Spring4Shell) targeting Spring Cloud Function RCE. Automates reverse shell delivery via wget and bash one-liner…
 h3rm1tr3b0rn/cve-2020-8644-playsms-1.4
Python script to exploit PlaySMS before 1.4.3
 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50526
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…
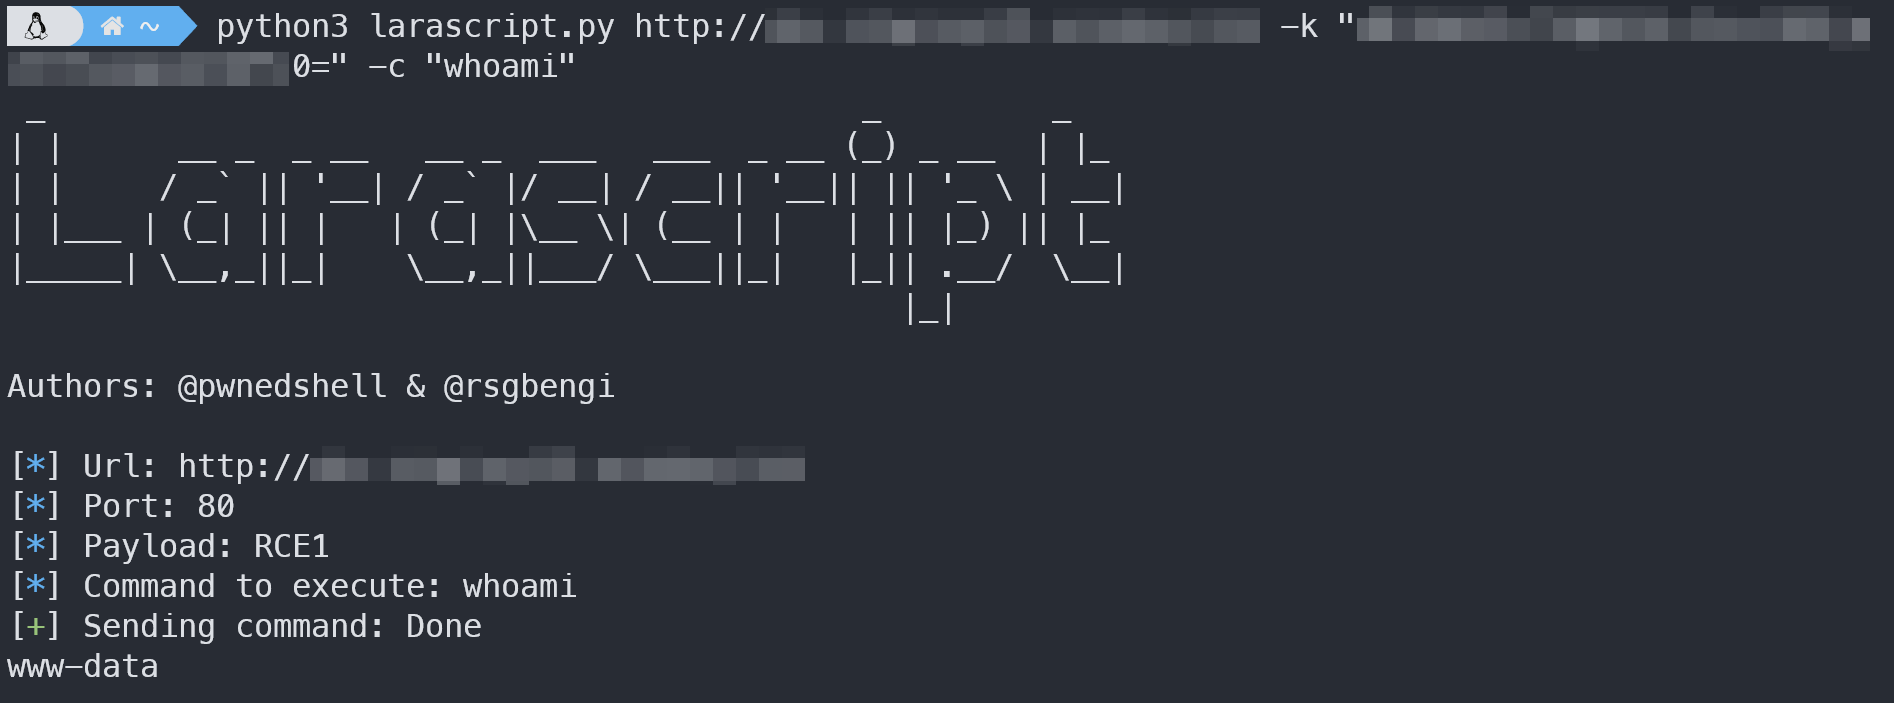 pwnedshell/larascript
Laravel RCE exploit. CVE-2018-15133
 wearehackers160/cve-2026-48907
CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 nxploited/cve-2025-32206
WordPress Processing Projects Plugin <= 1.0.2 is vulnerable to Arbitrary File Upload
 reggyraider/cve-2023-46604-rce
CVE-2023-46604-RCE exploit with Linux reverse shell payload
 rashidkhanpathan/cve-2022-40471
RCE Exploit and Research
 p1ckzi/cve-2022-22965
spring4shell | CVE-2022-22965