

glimmer
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
command-and-controlcryptographydata-exfiltration+8
45 months ago
linnemanlabs/glimmerAdversary emulation and C2 framework for security research
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
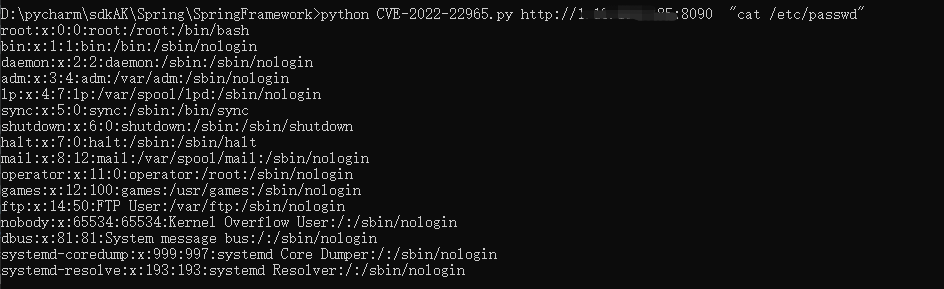 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
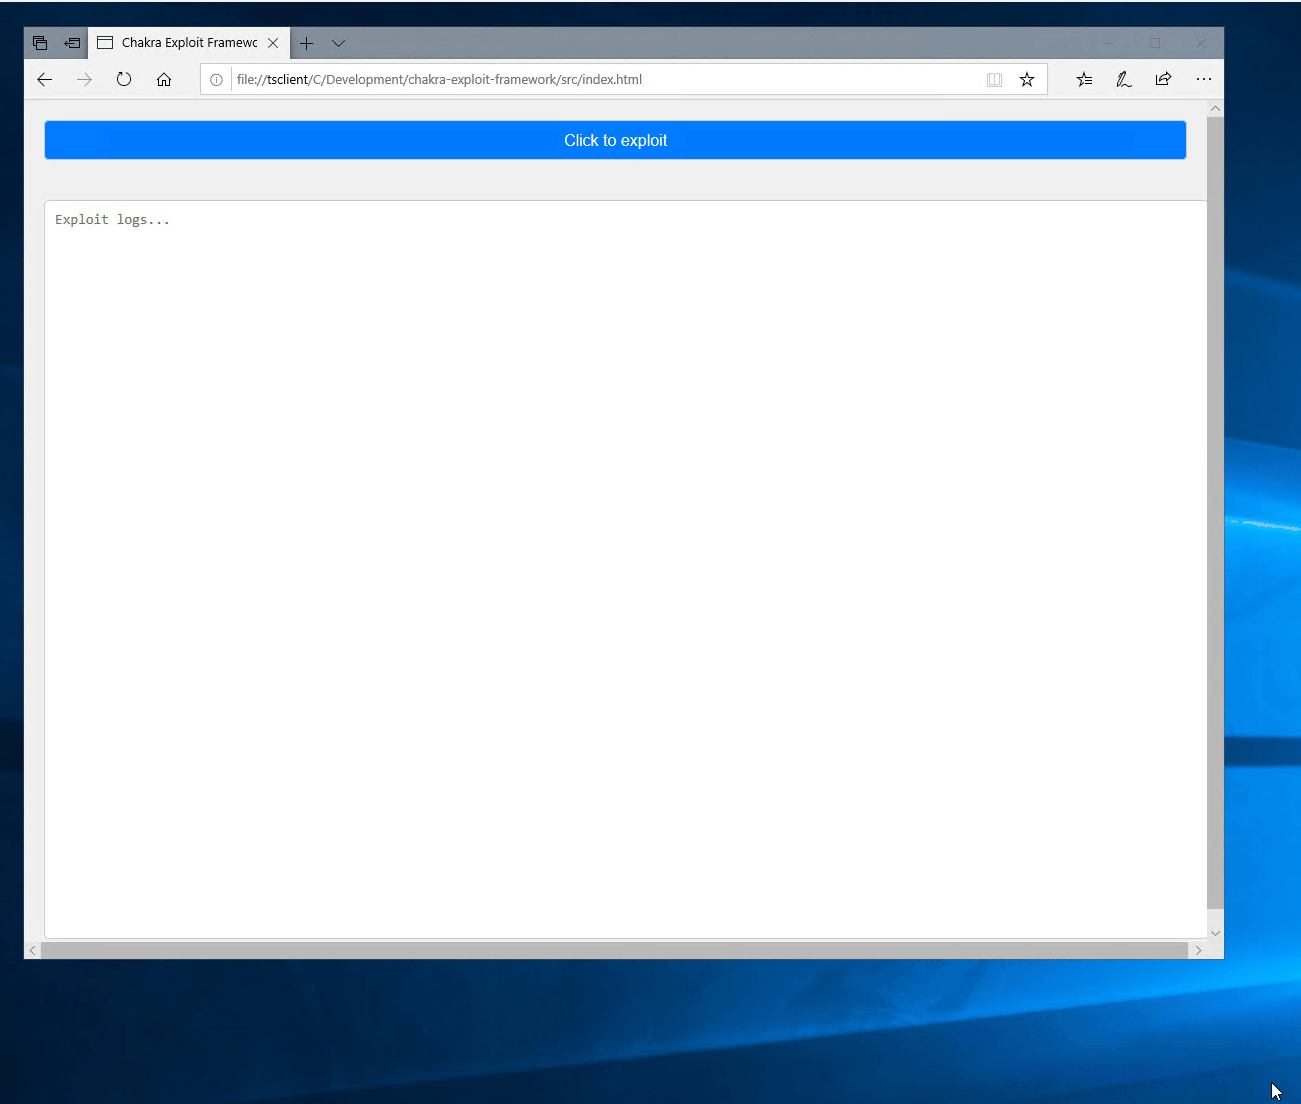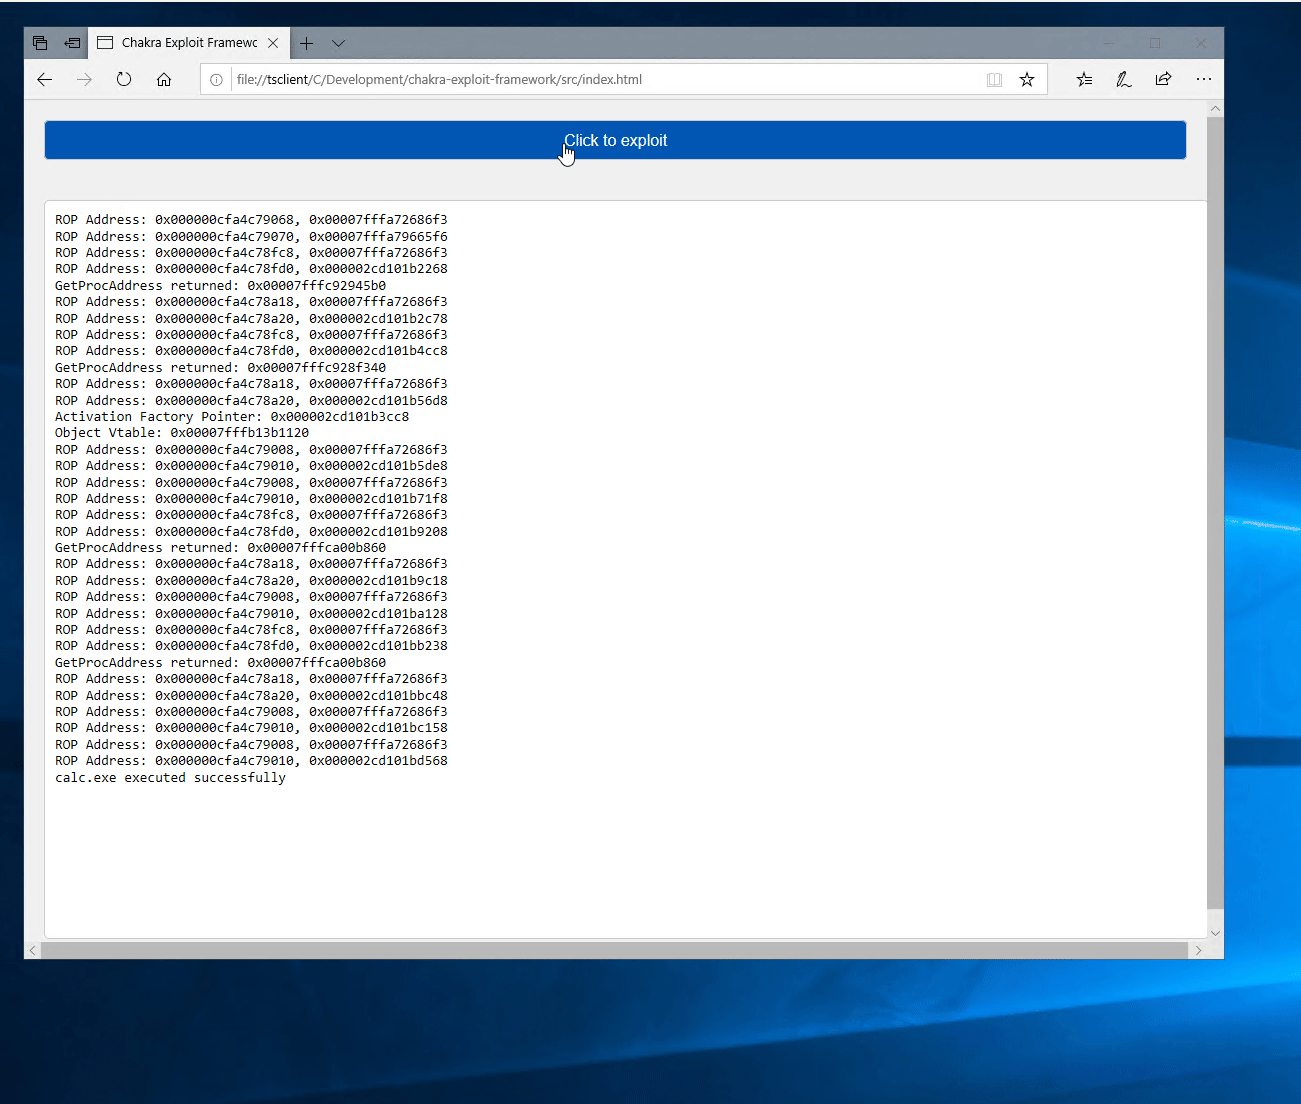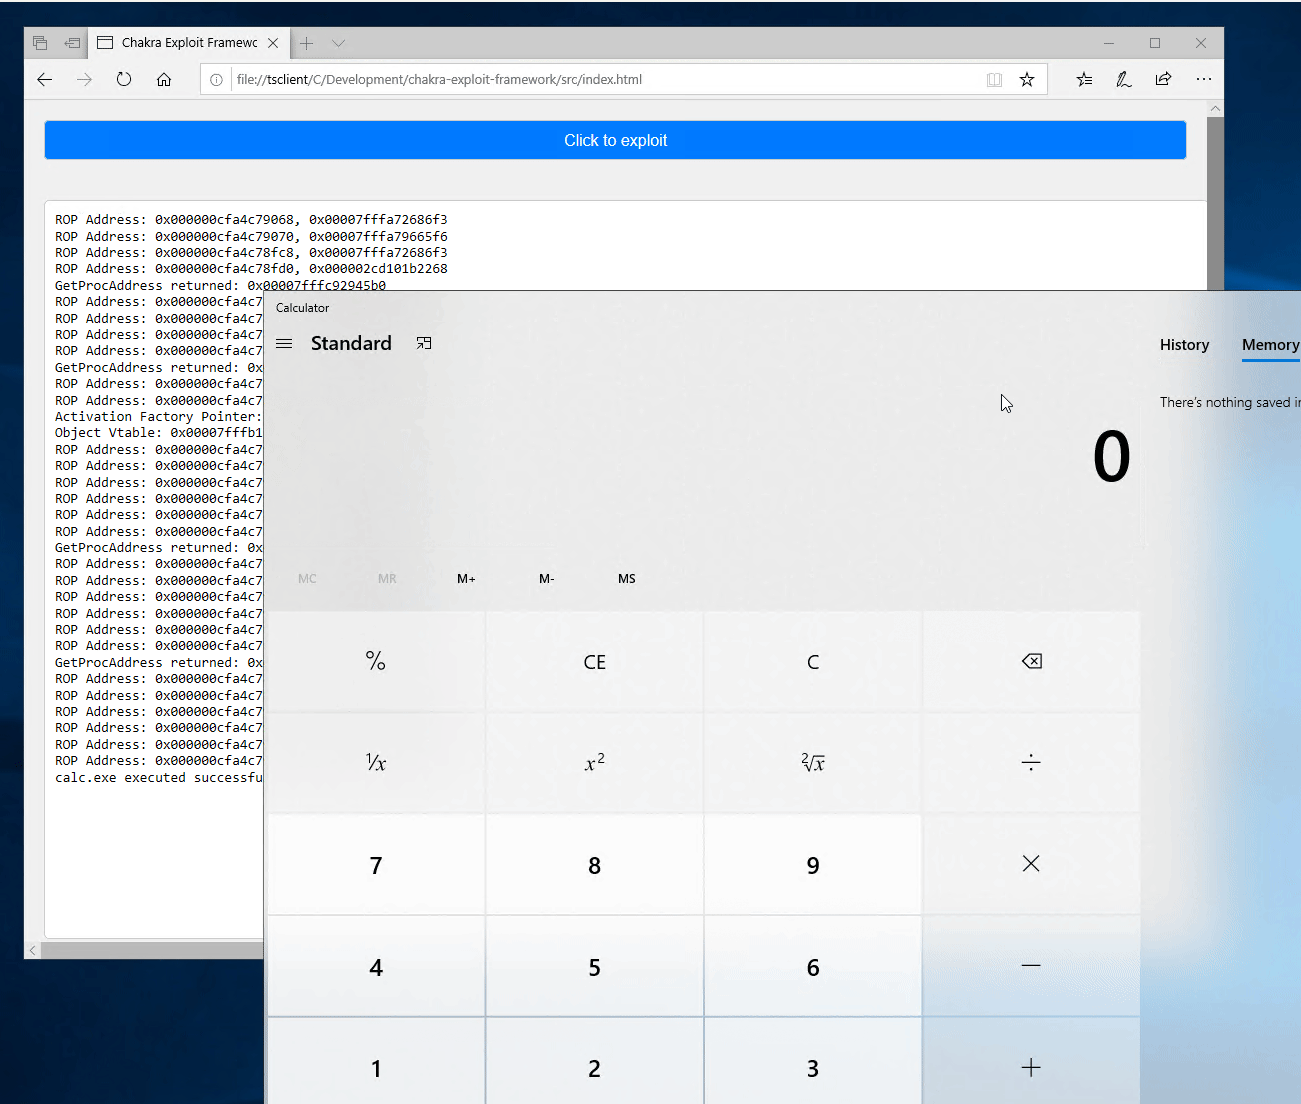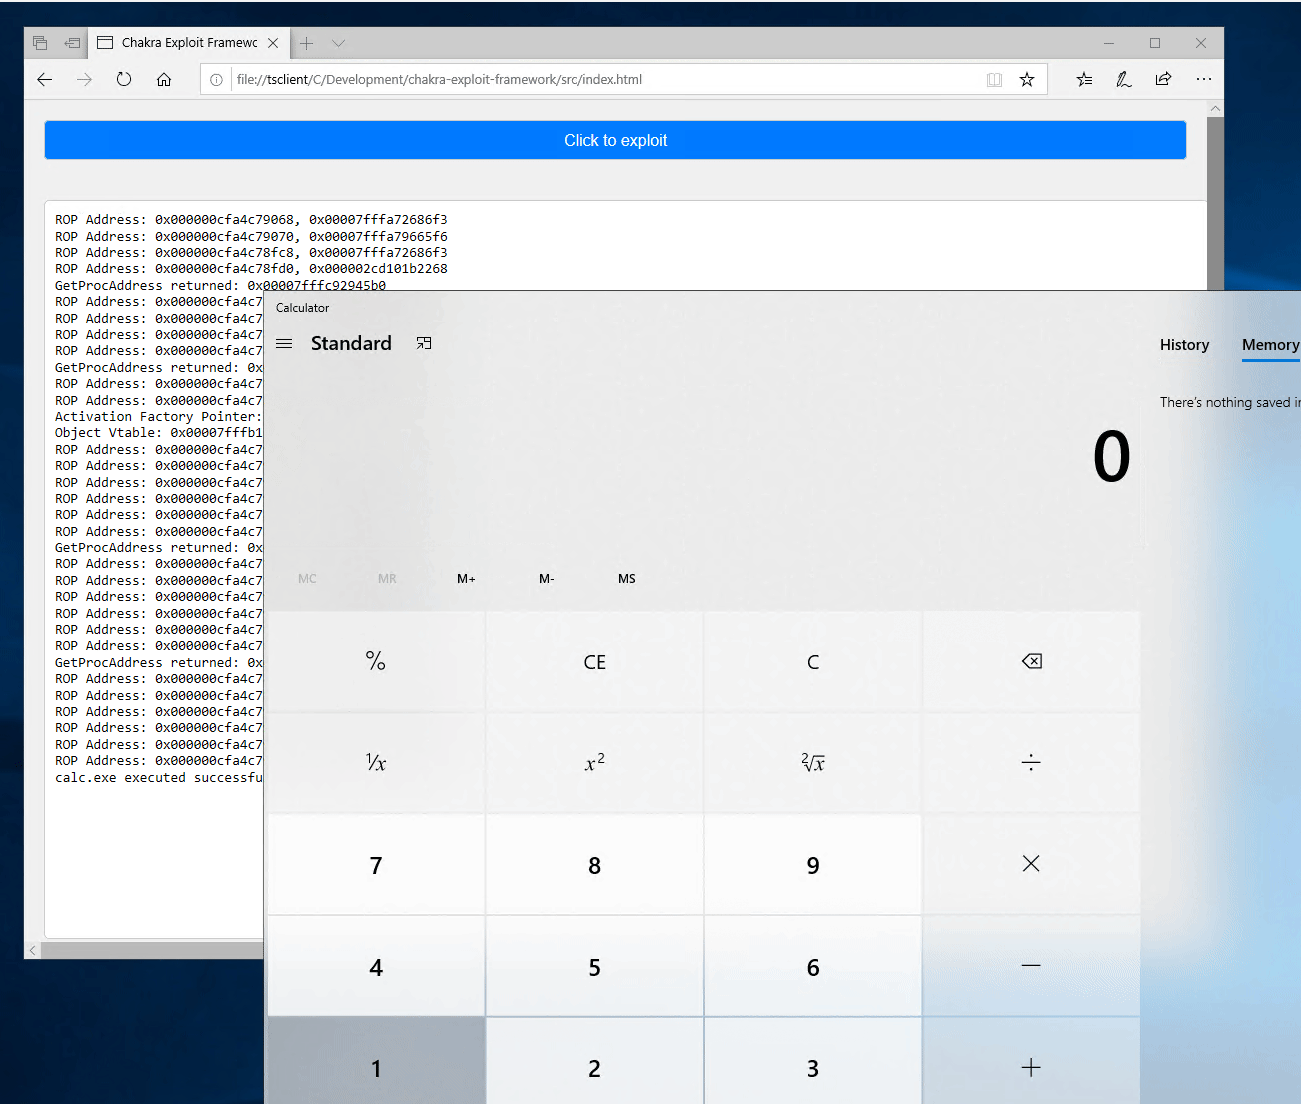 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 venglin/setcred
CVE-2026-45250: FreeBSD 14.4 setcred kernel buffer overflow (LPE)