
MSRKit
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
binary-exploitationexploitationpayload-development+5
63
rurixis/msrkitA concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 somecorp/copyfail-cve-2026-31431-workaround-bash
Provides a bash workaround script to mitigate CVE-2026-31431, preventing remote code execution via copy.fail exploit. Includes usage instructions for…
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 sneakynachos/cve-2026-2764-but-with-wasm
Proof-of-concept exploit chain for Firefox JIT CVE-2026-2764, chaining JIT miscompilation and use-after-free into arbitrary read/write and WASM…
 sneakynachos/cve-2026-2766-but-with-wasm
CVE-2026-2766, but with wasm
 yzddmr6/java-shellcode-loader
基于Java实现的Shellcode加载器
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
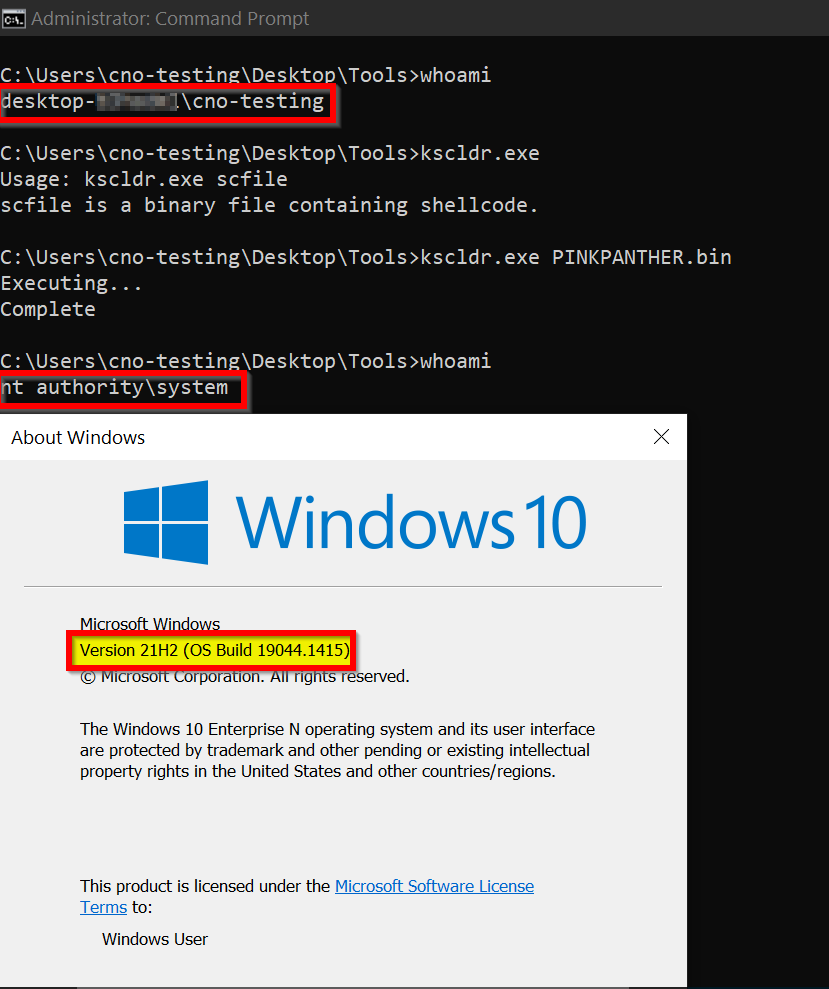 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 wra7h/flavortown
Various ways to execute shellcode
 s3cur3th1ssh1t/nimshellcodefluctuation
ShellcodeFluctuation PoC ported to Nim
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 dump-guy/sc2pe
Simple dotnet Native AOT app that uses AsmResolver to convert shellcode to PE