

KDU
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
binary-exploitationdefensive-toolsexploitation+8
2.8k
hfiref0x/kduWindows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
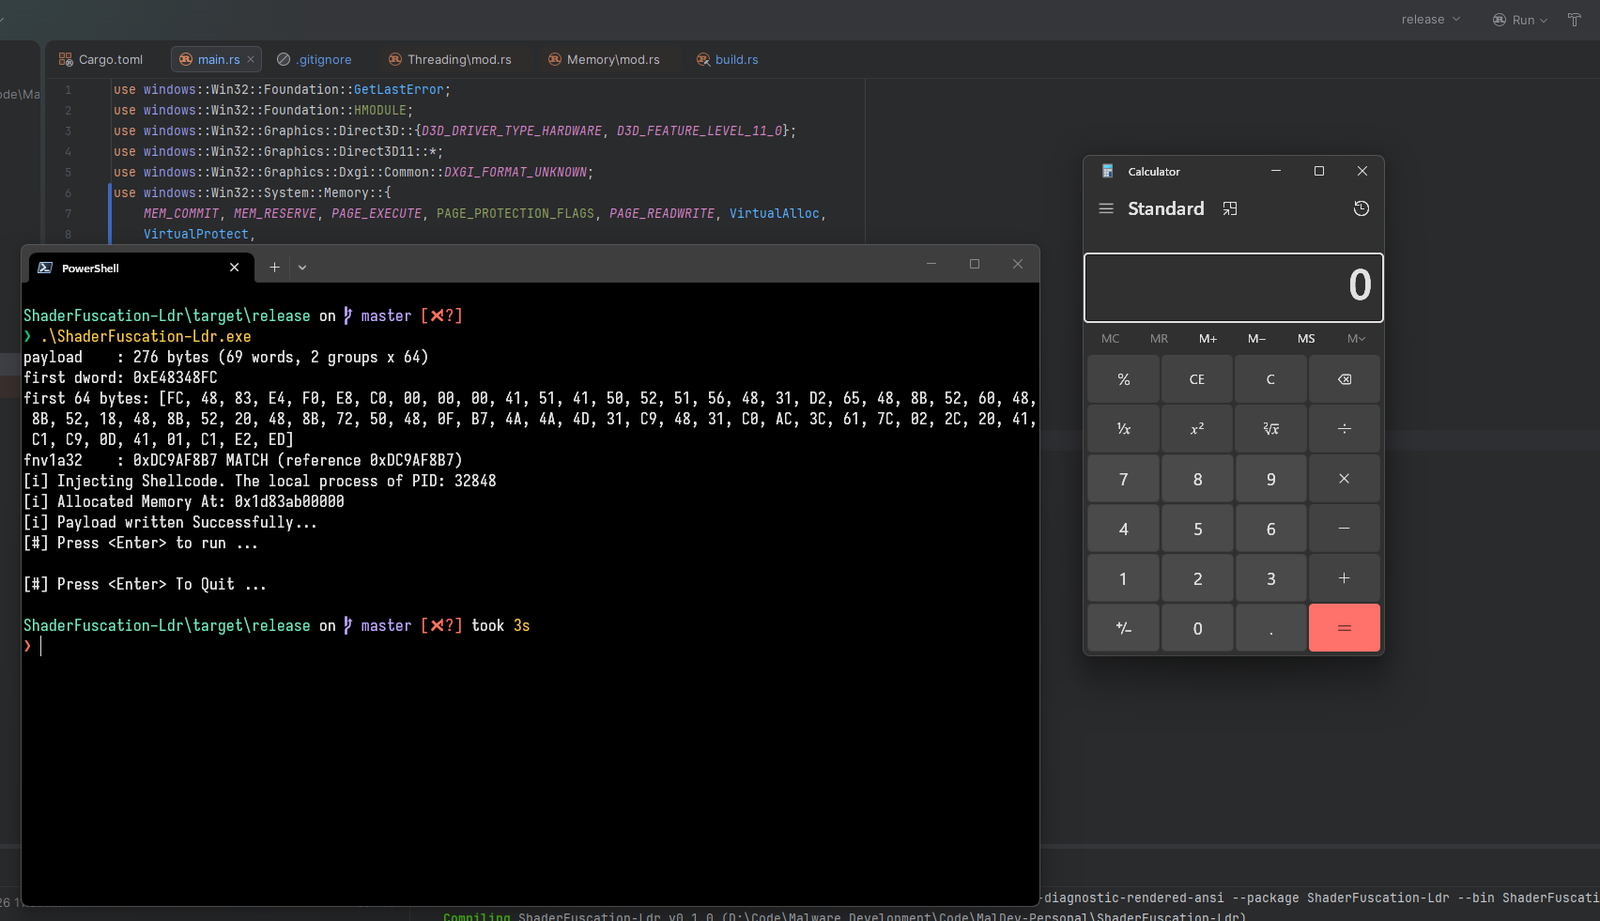 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
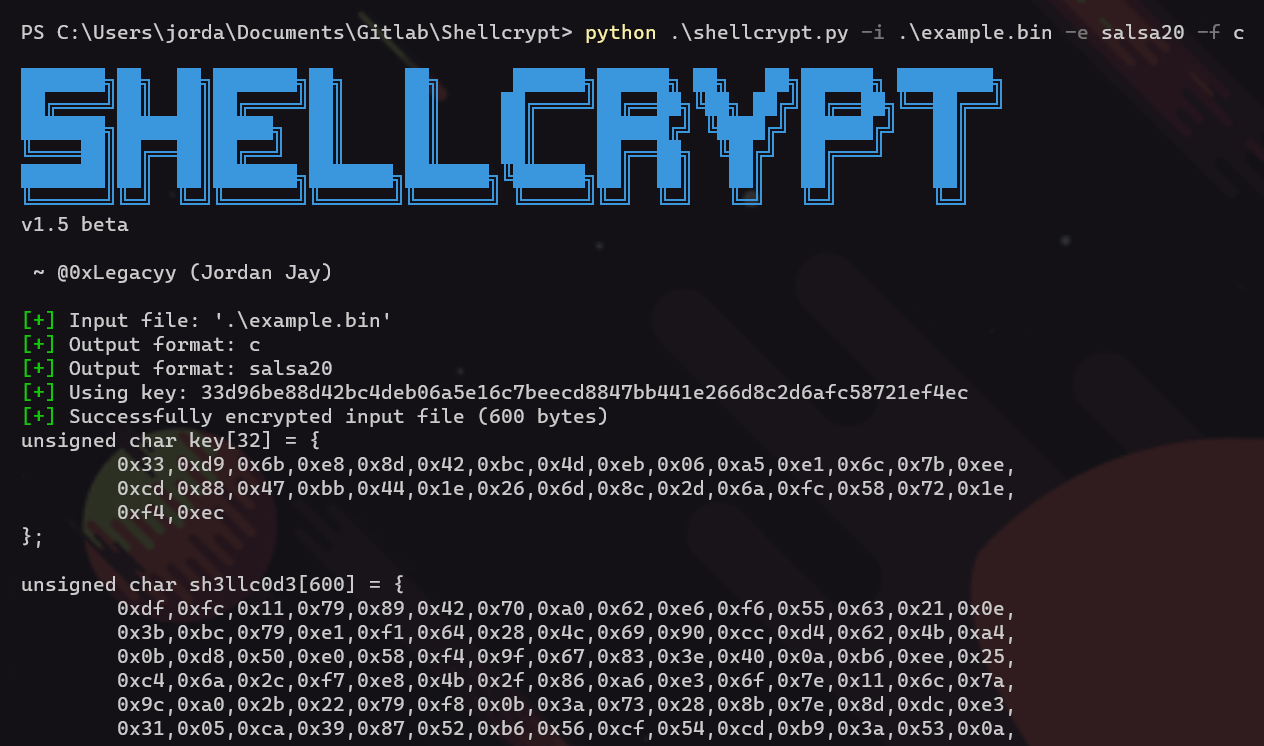 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 buzzer-re/shinigami
A dynamic unpacking tool
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 print3m/bytecaster
Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
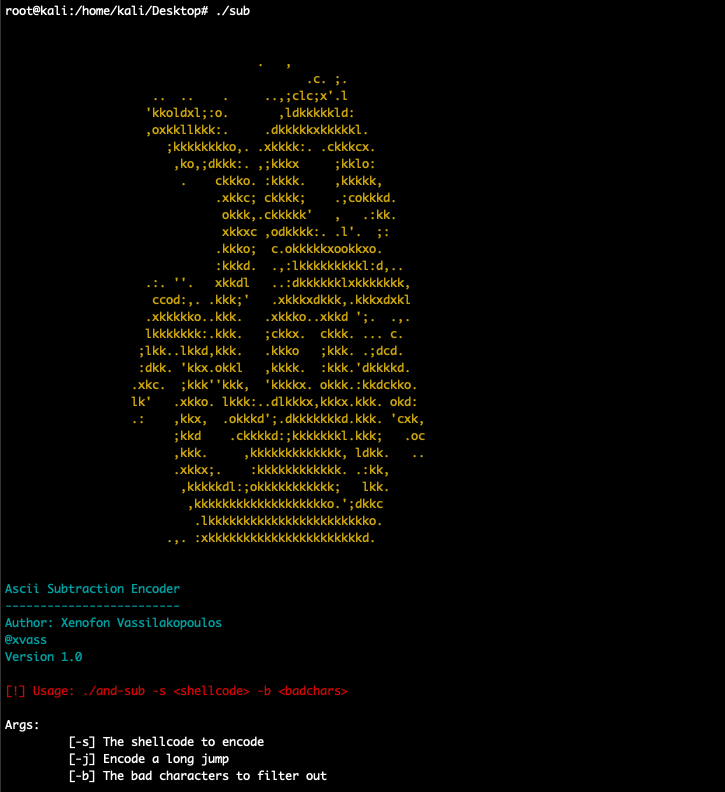 xen0vas/ascii-and-sub-encoder
This is a custom ASCII AND/SUB Encoder developed during my preparation for the legacy OSCE/CTP course
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
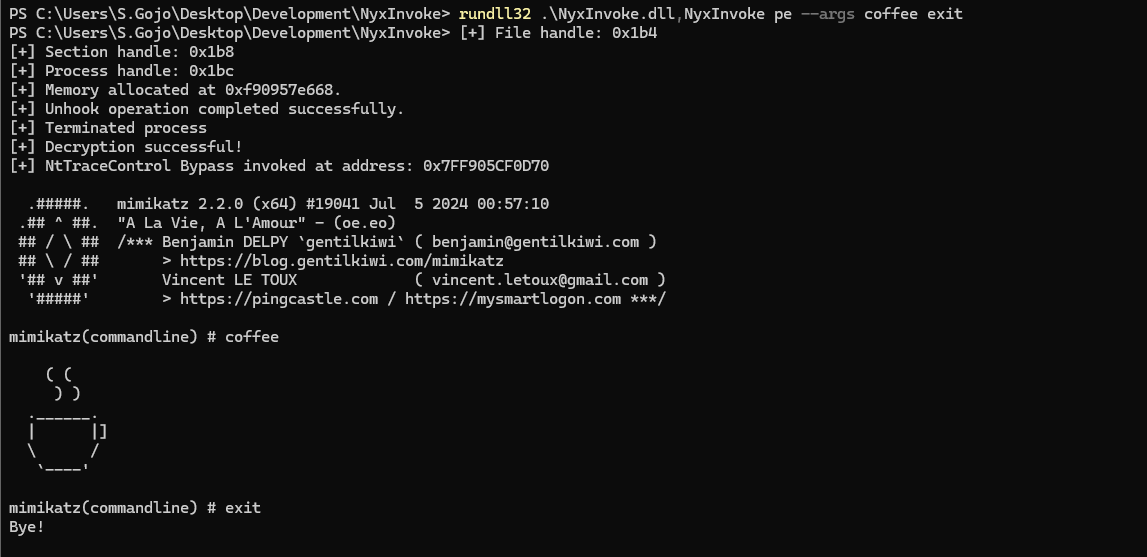 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 thecybermind/w48crash
PoC code for vulnerability in webmod v0.48. Originally written in 2007, assigned CVE-2007-1260.