
ICALL-GADGET
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
binary-exploitationexploitationids-ips-evasion+5
1
gmh5225/icall-gadgetExploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 racoten/reflectivepluginloader
Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
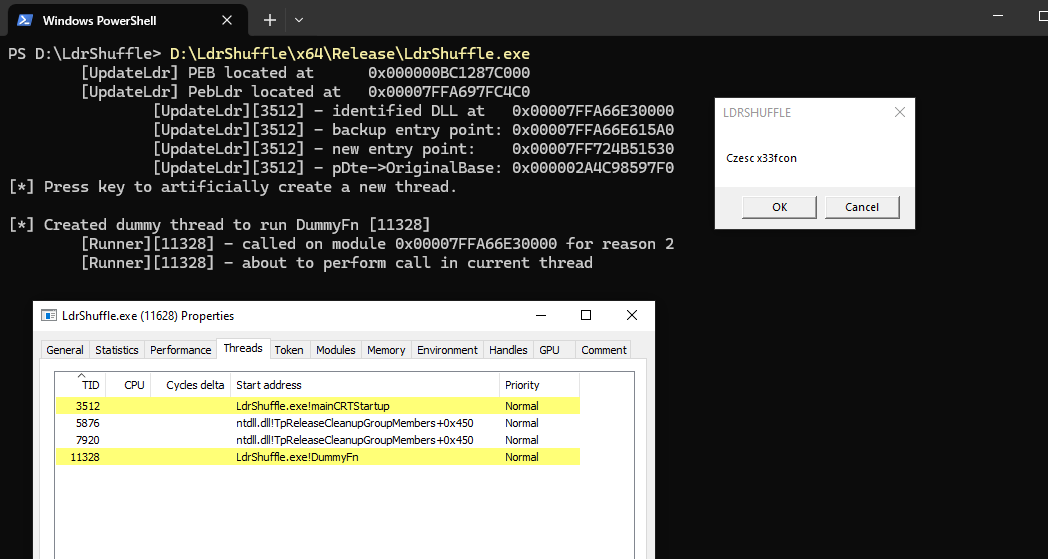 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 ivanitlearning/cve-2004-1561
Icecast Header Overwrite buffer overflow RCE < 2.0.1 (Win32)
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 maldev-academy/remotetlscallbackinjection
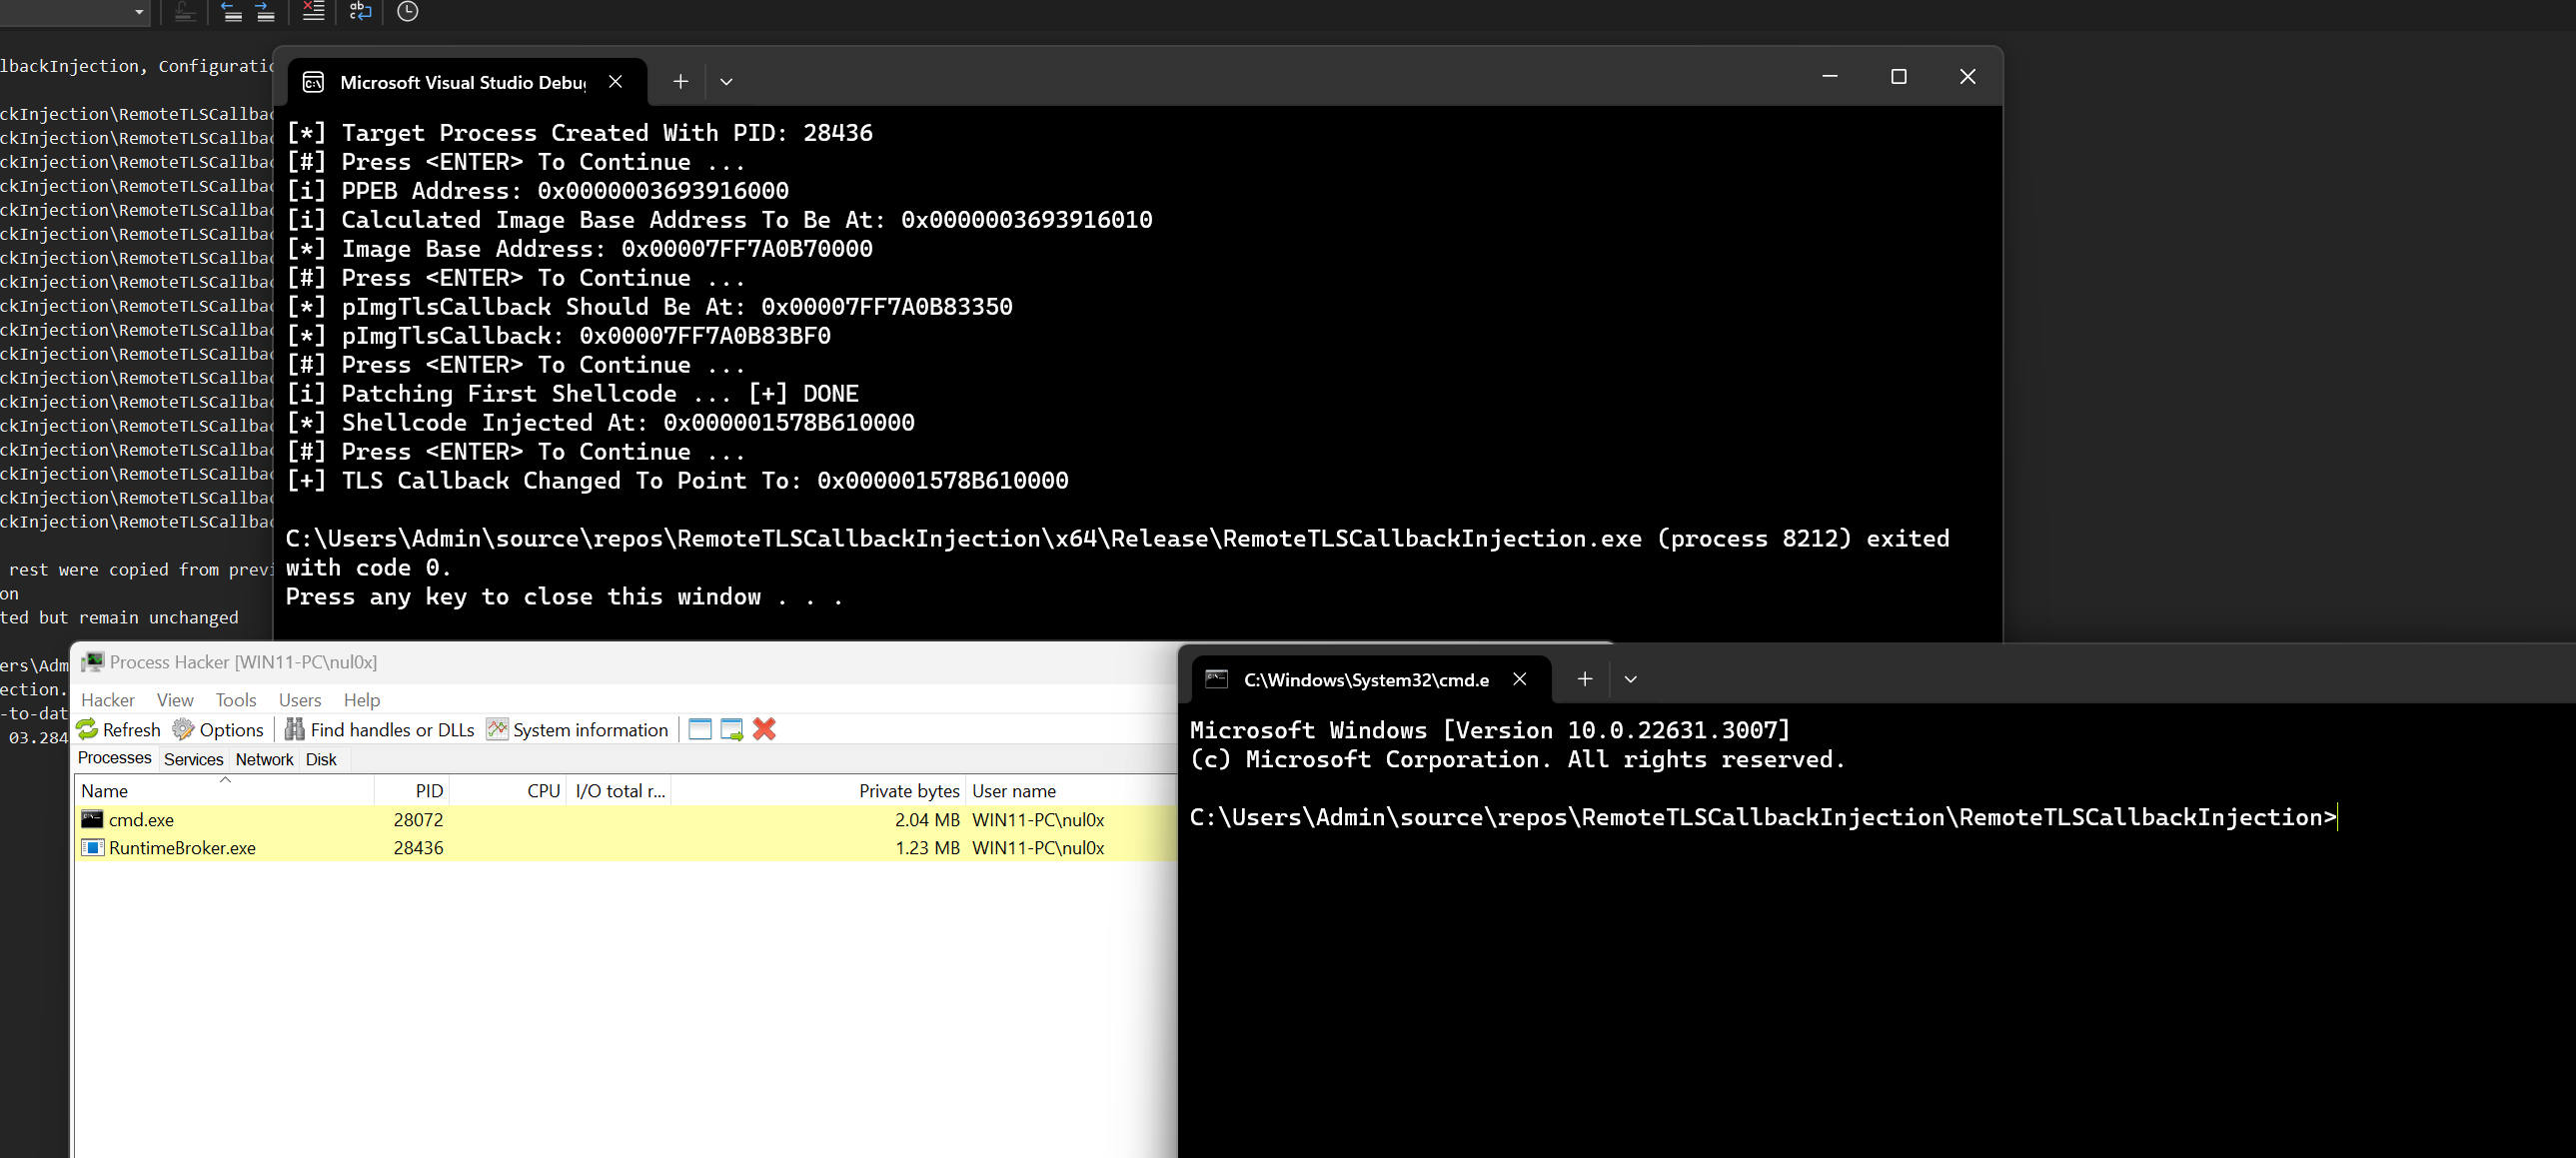
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process