

CVE-2026-43499-S26
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
android-securitybinary-exploitationexploitation+8
sammyenigma/cve-2026-43499-s26Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
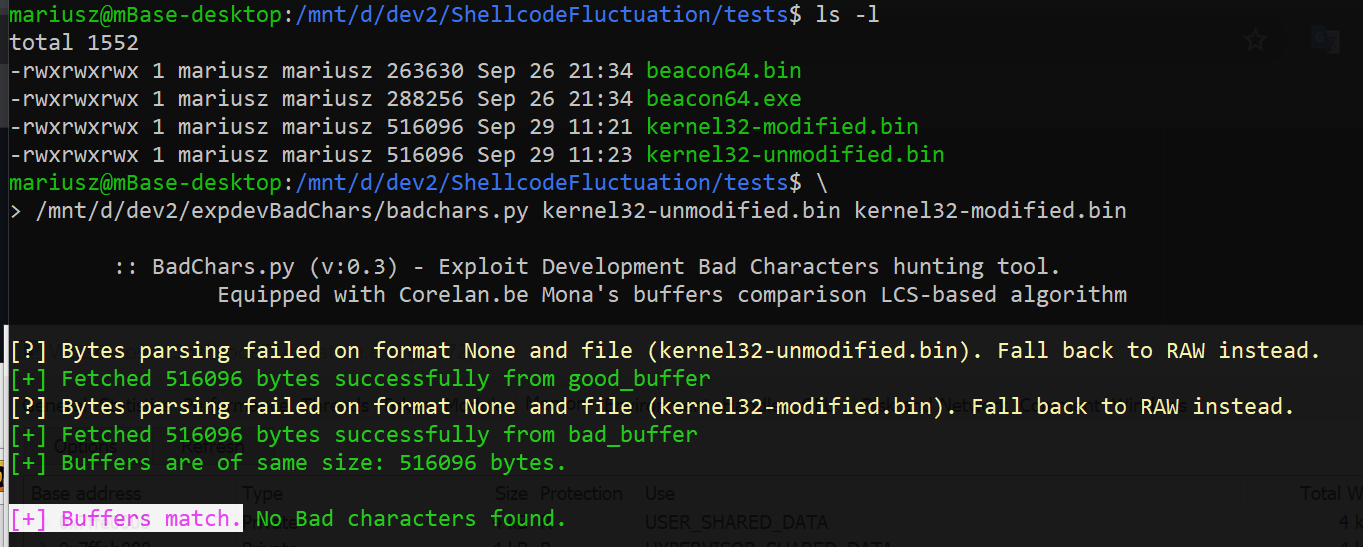 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 yo-yo-yo-jbo/msf_shellcode_analysis
Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 spiralbl0ck/partial-deobfuscated-sc-from-hackingteam-malware.-
This repo stores necessary files for the analysis blog which will come soon
 gartonchan/redis-cve-2025-62507
Exploit scripts for CVE-2025-62507, a stack buffer overflow in Redis 8.2.0. Provides x86-64 and ARM64 ROP chain exploits with shellcode generation…
 faithtiannn/cve-2025-55182
CVE-2025-55182漏洞检测工具
 yukinime/cve-2025-34085
Automated scanner and exploit for CVE-2025-34085, an unauthenticated RCE in the WordPress Simple File List plugin. Supports multi-target scanning,…
 wireghoul/htshells
Self contained htaccess shells and attacks
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
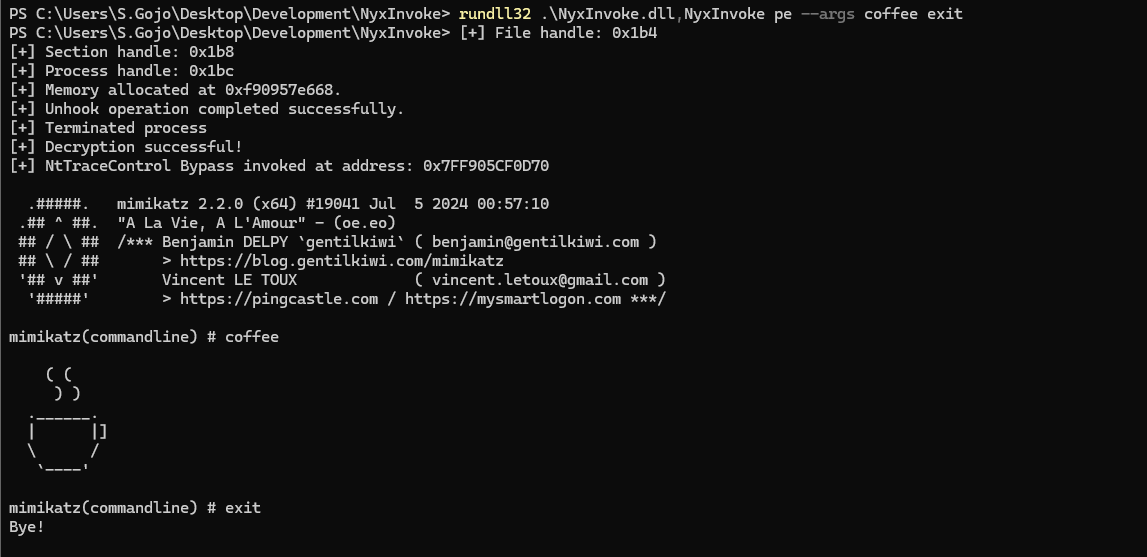 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 smaash/quasibot
complex webshell manager, quasi-http botnet.
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets