
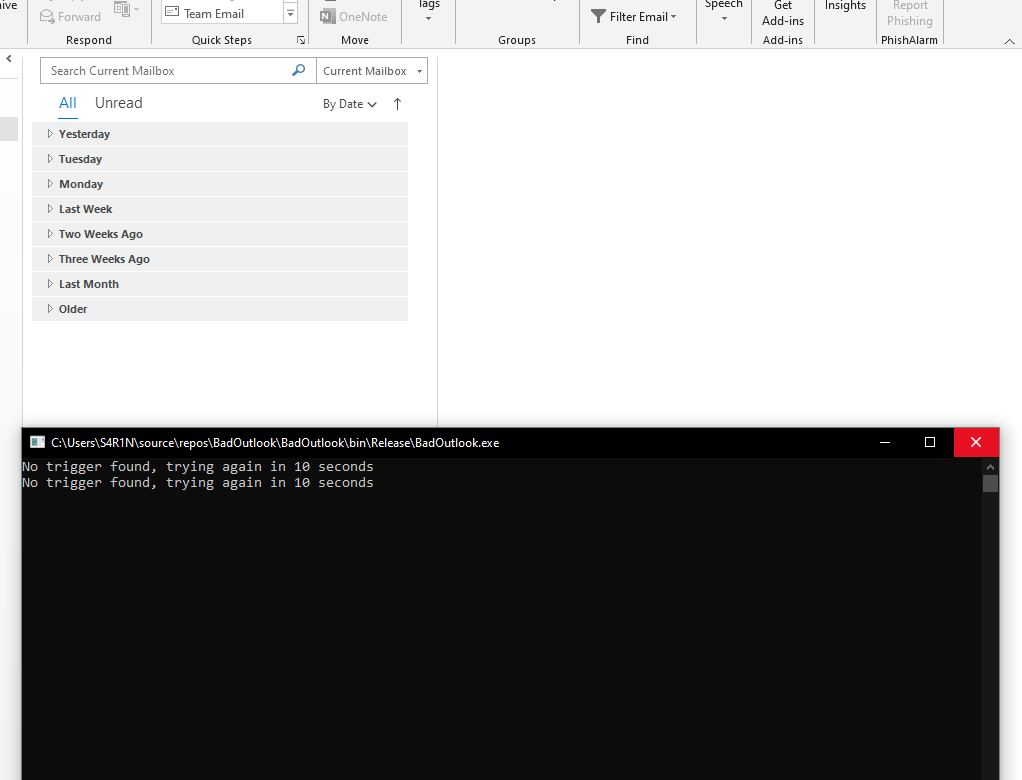
BadOutlook
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
command-and-controlemail-securityexploitation+3
137
aahmad097/badoutlookProof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 cookiengineer/actual-php2shell
🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
 jgs-developer/cve-2025-5548
Stack-based buffer overflow exploit for FreeFloat FTP Server, demonstrating reverse engineering, EIP control, and shellcode execution for educational…
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
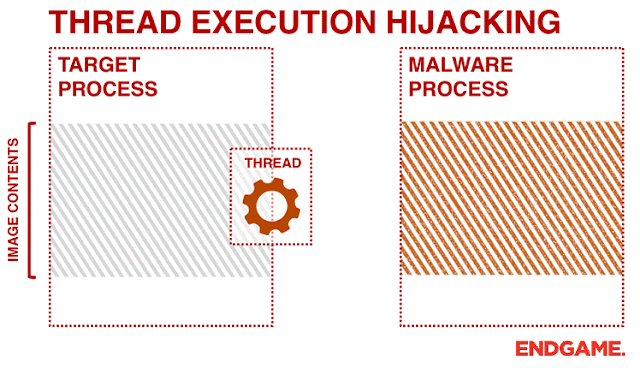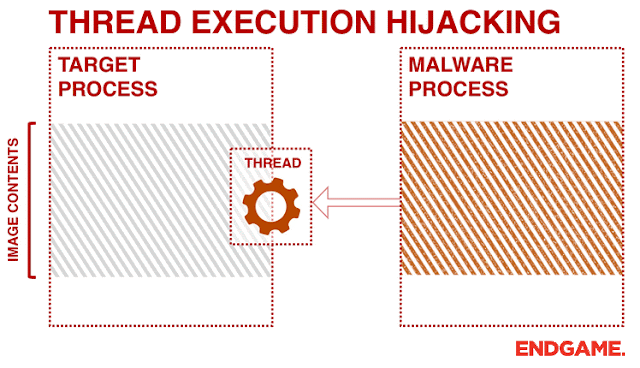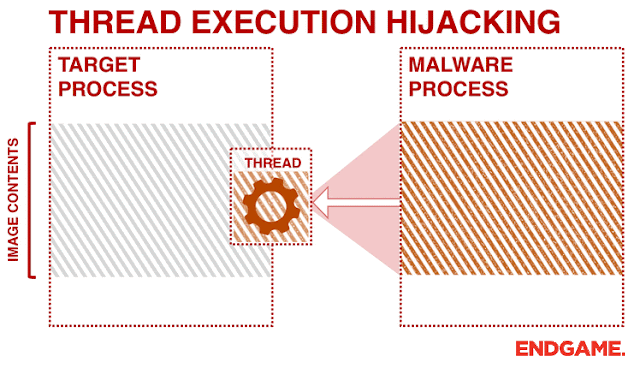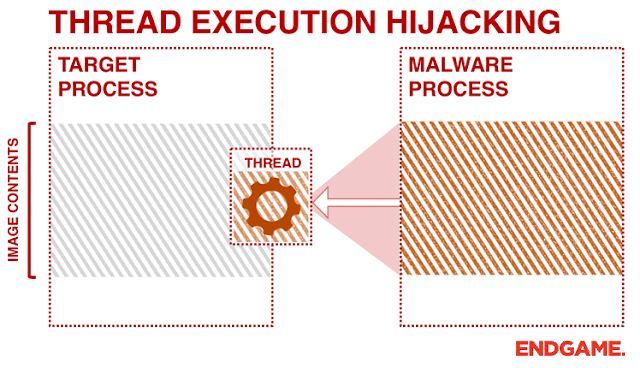 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
 aungsoepaing/cve-2024-39069
CVE-2024-39069
 tematemaru/cve-2026-31431-simple-test
Educational proof-of-concept demonstrating CVE-2026-31431 with a vulnerable target application, demonstration payload, and shellcode extraction…