

meterssh
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
command-and-controlexploitationpayload-development+4
530
trustedsec/metersshMeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
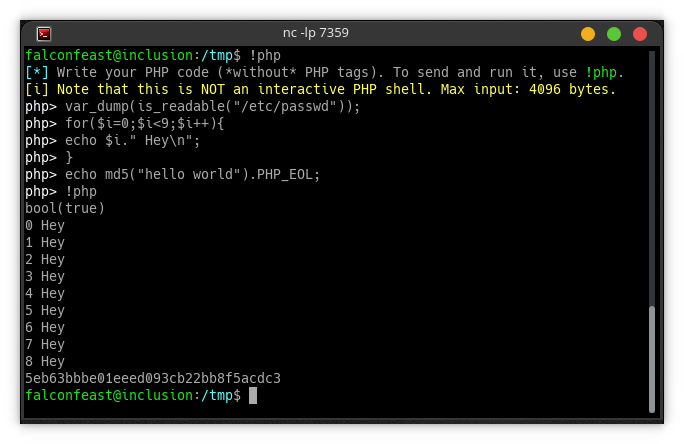 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 moisestapia/cve-2022-3218
Python exploit for CVE-2022-3218 that generates a reverse TCP payload via msfvenom and delivers it over HTTP to a target Windows host.