CVE-2015-1578-PoC-Metasploit

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…

Hide your Powershell script in plain sight. Bypass all Powershell security features

Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…

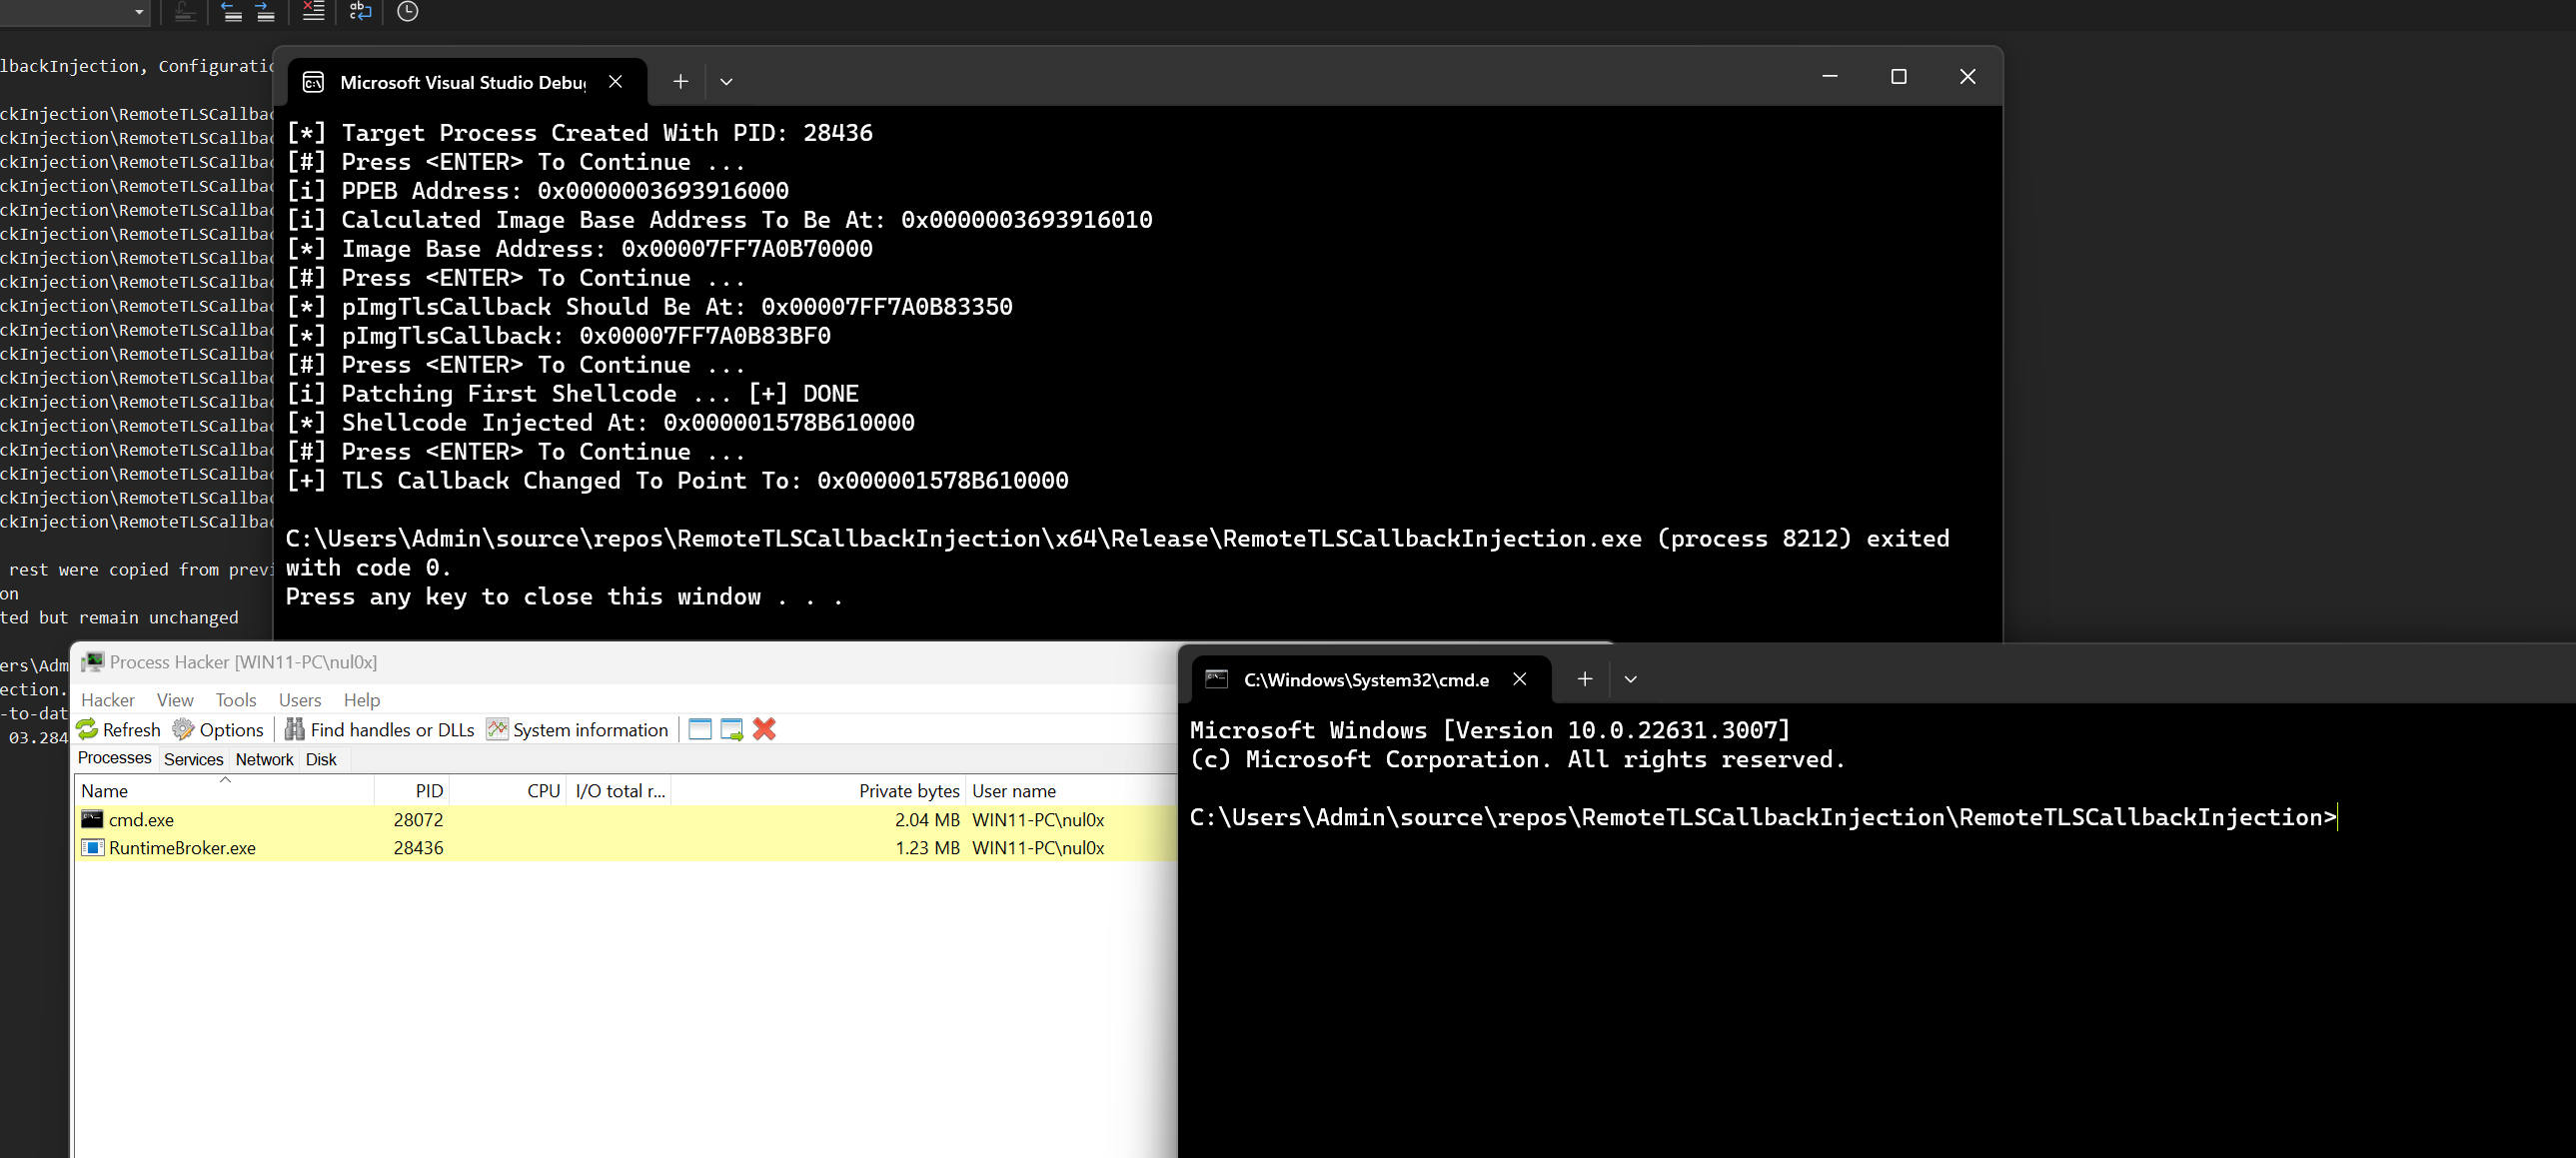
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system

BOF to run PE in Cobalt Strike Beacon without console creation

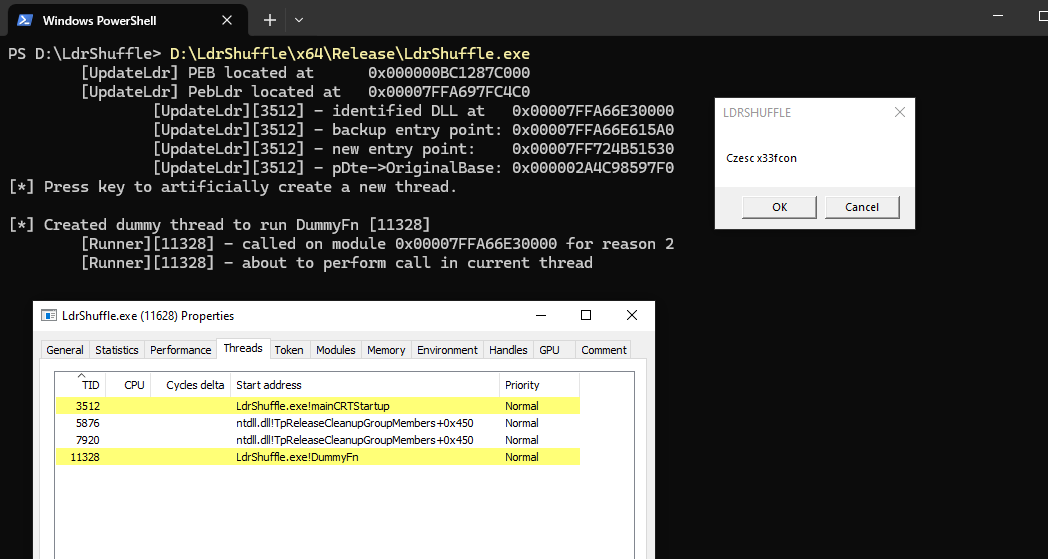
Code execution/injection technique using DLL PEB module structure manipulation

Icecast Header Overwrite buffer overflow RCE < 2.0.1 (Win32)

Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking