

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
71 results
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
12.1k20h 39m ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

adversarial-attackcommand-and-controldata-exfiltration+16
5.3k1 month ago
phantom-frida preview

phantom-frida

GitHubtheqmaks/phantom-frida

Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.

android-securitybinary-analysisdynamic-analysis-sandboxing+7
3962 months ago
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

binary-analysisencryption-decryption-toolsexploitation+5
2021 month ago
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

command-and-controldatabase-securitydata-exfiltration+20
39.2k1 day ago
reverse-shell-generator preview

reverse-shell-generator

GitHub0dayctf/reverse-shell-generator

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

ctfexploitationpayload-development+6
4.1k5 months ago
dropengine preview

dropengine

GitHubs0lst1c3/dropengine

DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…

defensive-toolsexploit-frameworkspayload-development+5
2145 years ago
Project-Onyx preview

Project-Onyx

GitHubx-3306/project-onyx

Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…

ai-securitycommand-and-controlcryptography+6
1191 month ago
nasm_linux_x86_64_pure_sharedlib preview

nasm_linux_x86_64_pure_sharedlib

GitHubtherealdreg/nasm_linux_x86_64_pure_sharedlib

NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection

exploitationpayload-developmentpost-exploitation+2
313 years ago
glimmer preview

glimmer

GitHublinnemanlabs/glimmer

Adversary emulation and C2 framework for security research

command-and-controlcryptographydata-exfiltration+8
55 months ago
Chimay-Red preview

Chimay-Red

GitHubbignerd95/chimay-red

Working POC of Mikrotik exploit from Vault 7 CIA Leaks

binary-exploitationembedded-systems-securityexploitation+8
6684 years ago
LazZzy_Dump preview

LazZzy_Dump

GitHubtrustedsec/lazzzy_dump

Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…

binary-analysiscode-analysisdigital-forensics+6
11 month ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
BadOutlook preview

BadOutlook

GitHubaahmad097/badoutlook

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
command-and-controlemail-securityexploitation+3
1375 years ago
Analysis-for-stage1-shellcode-loader-from-hacking- preview

Analysis-for-stage1-shellcode-loader-from-hacking-

GitHubspiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-

Analysis for stage1 shellcode loader from hacking
binary-analysiseducationmalware-analysis+2
31 year ago
SdoKeyCrypt-sys-local-privilege-elevation preview

SdoKeyCrypt-sys-local-privilege-elevation

GitHubhypersine/sdokeycrypt-sys-local-privilege-elevation

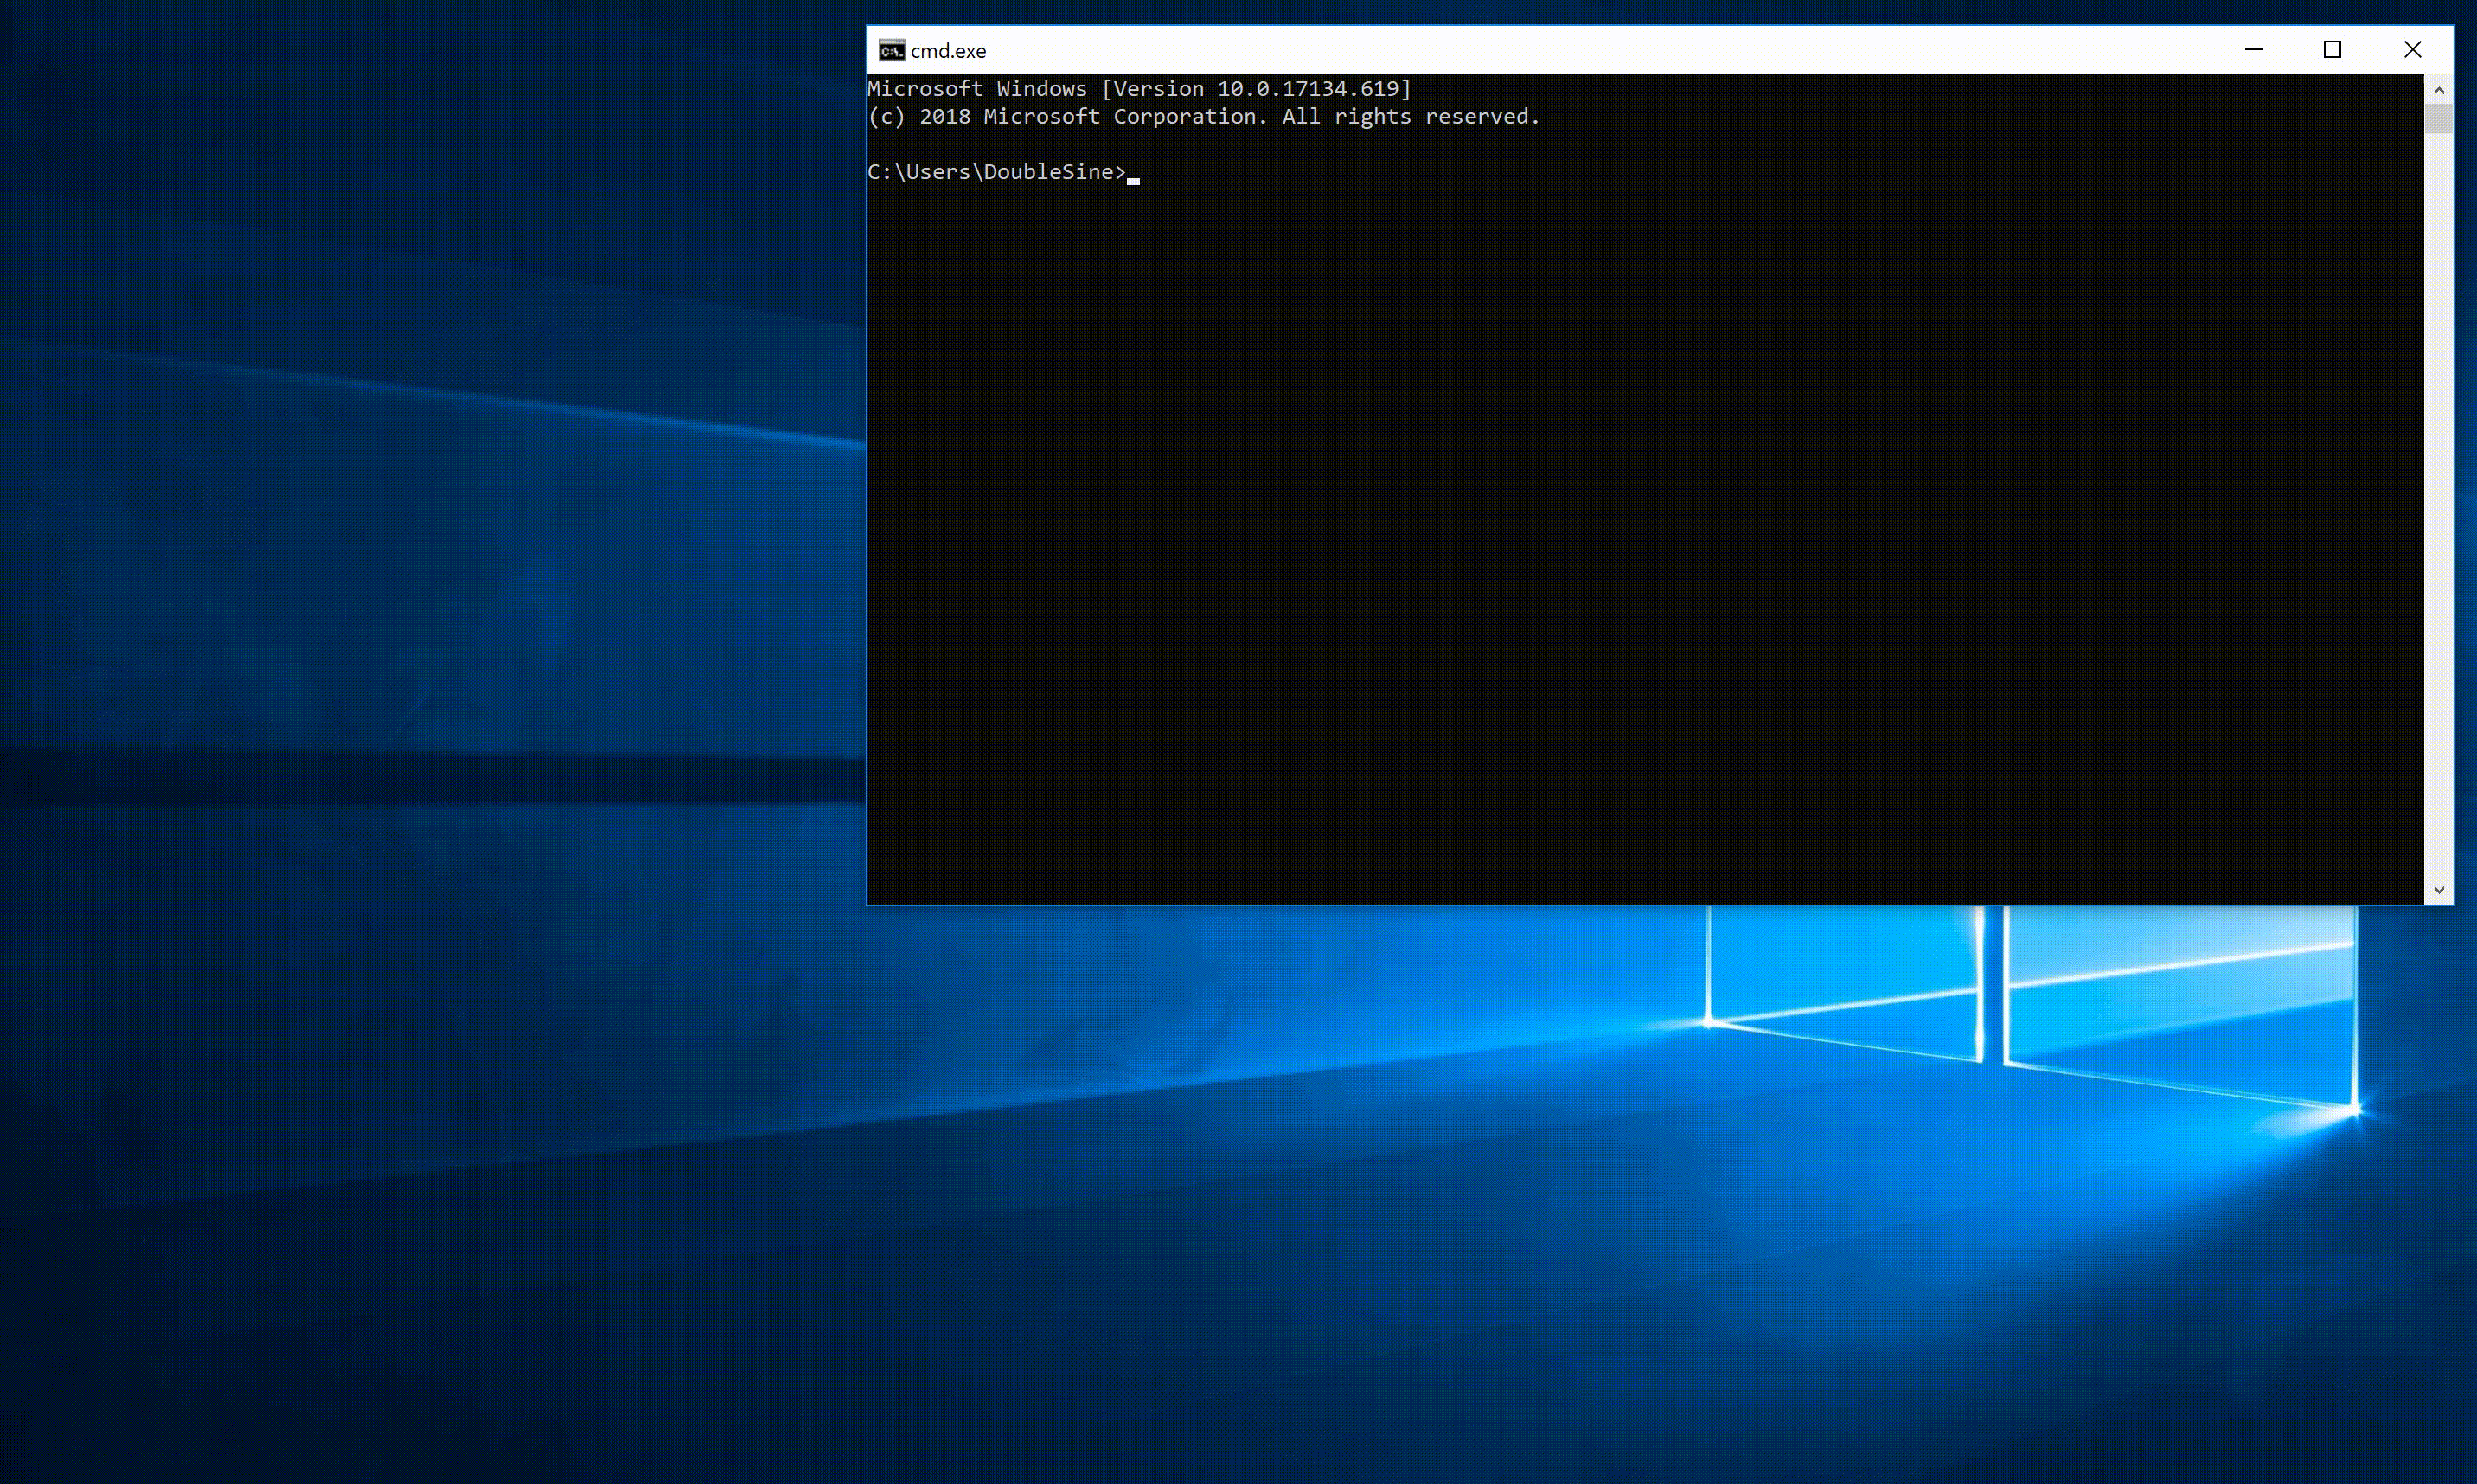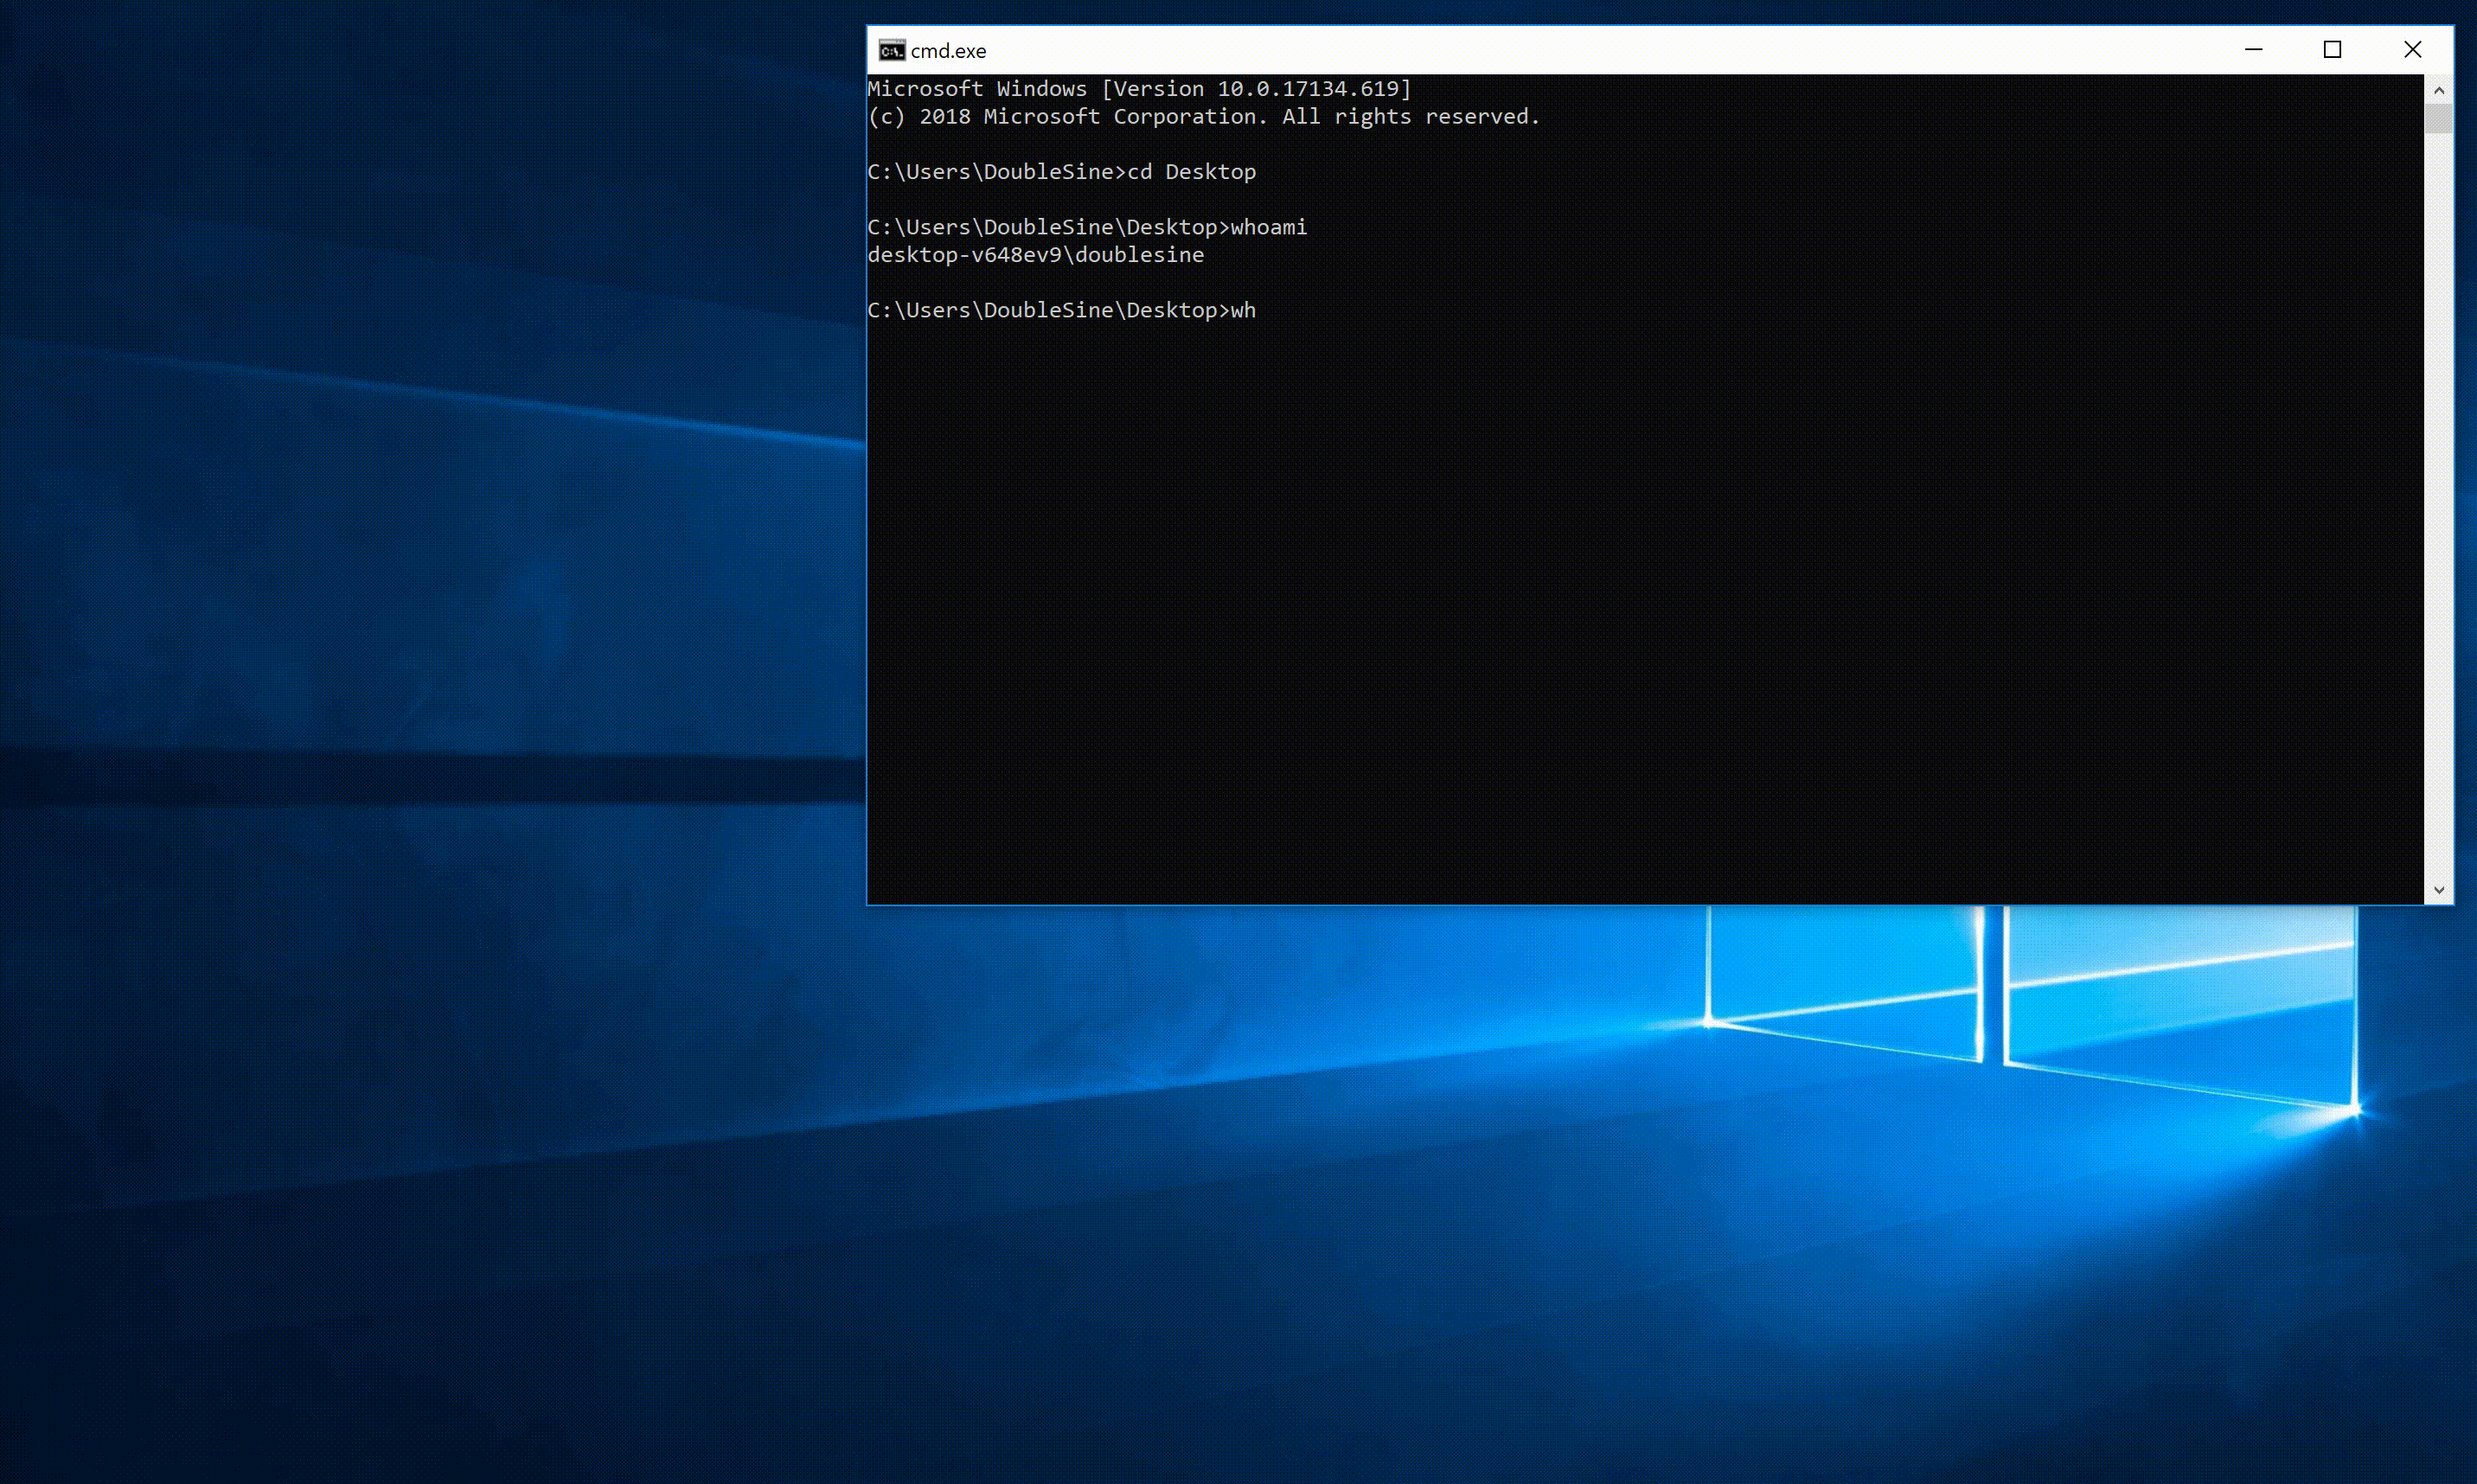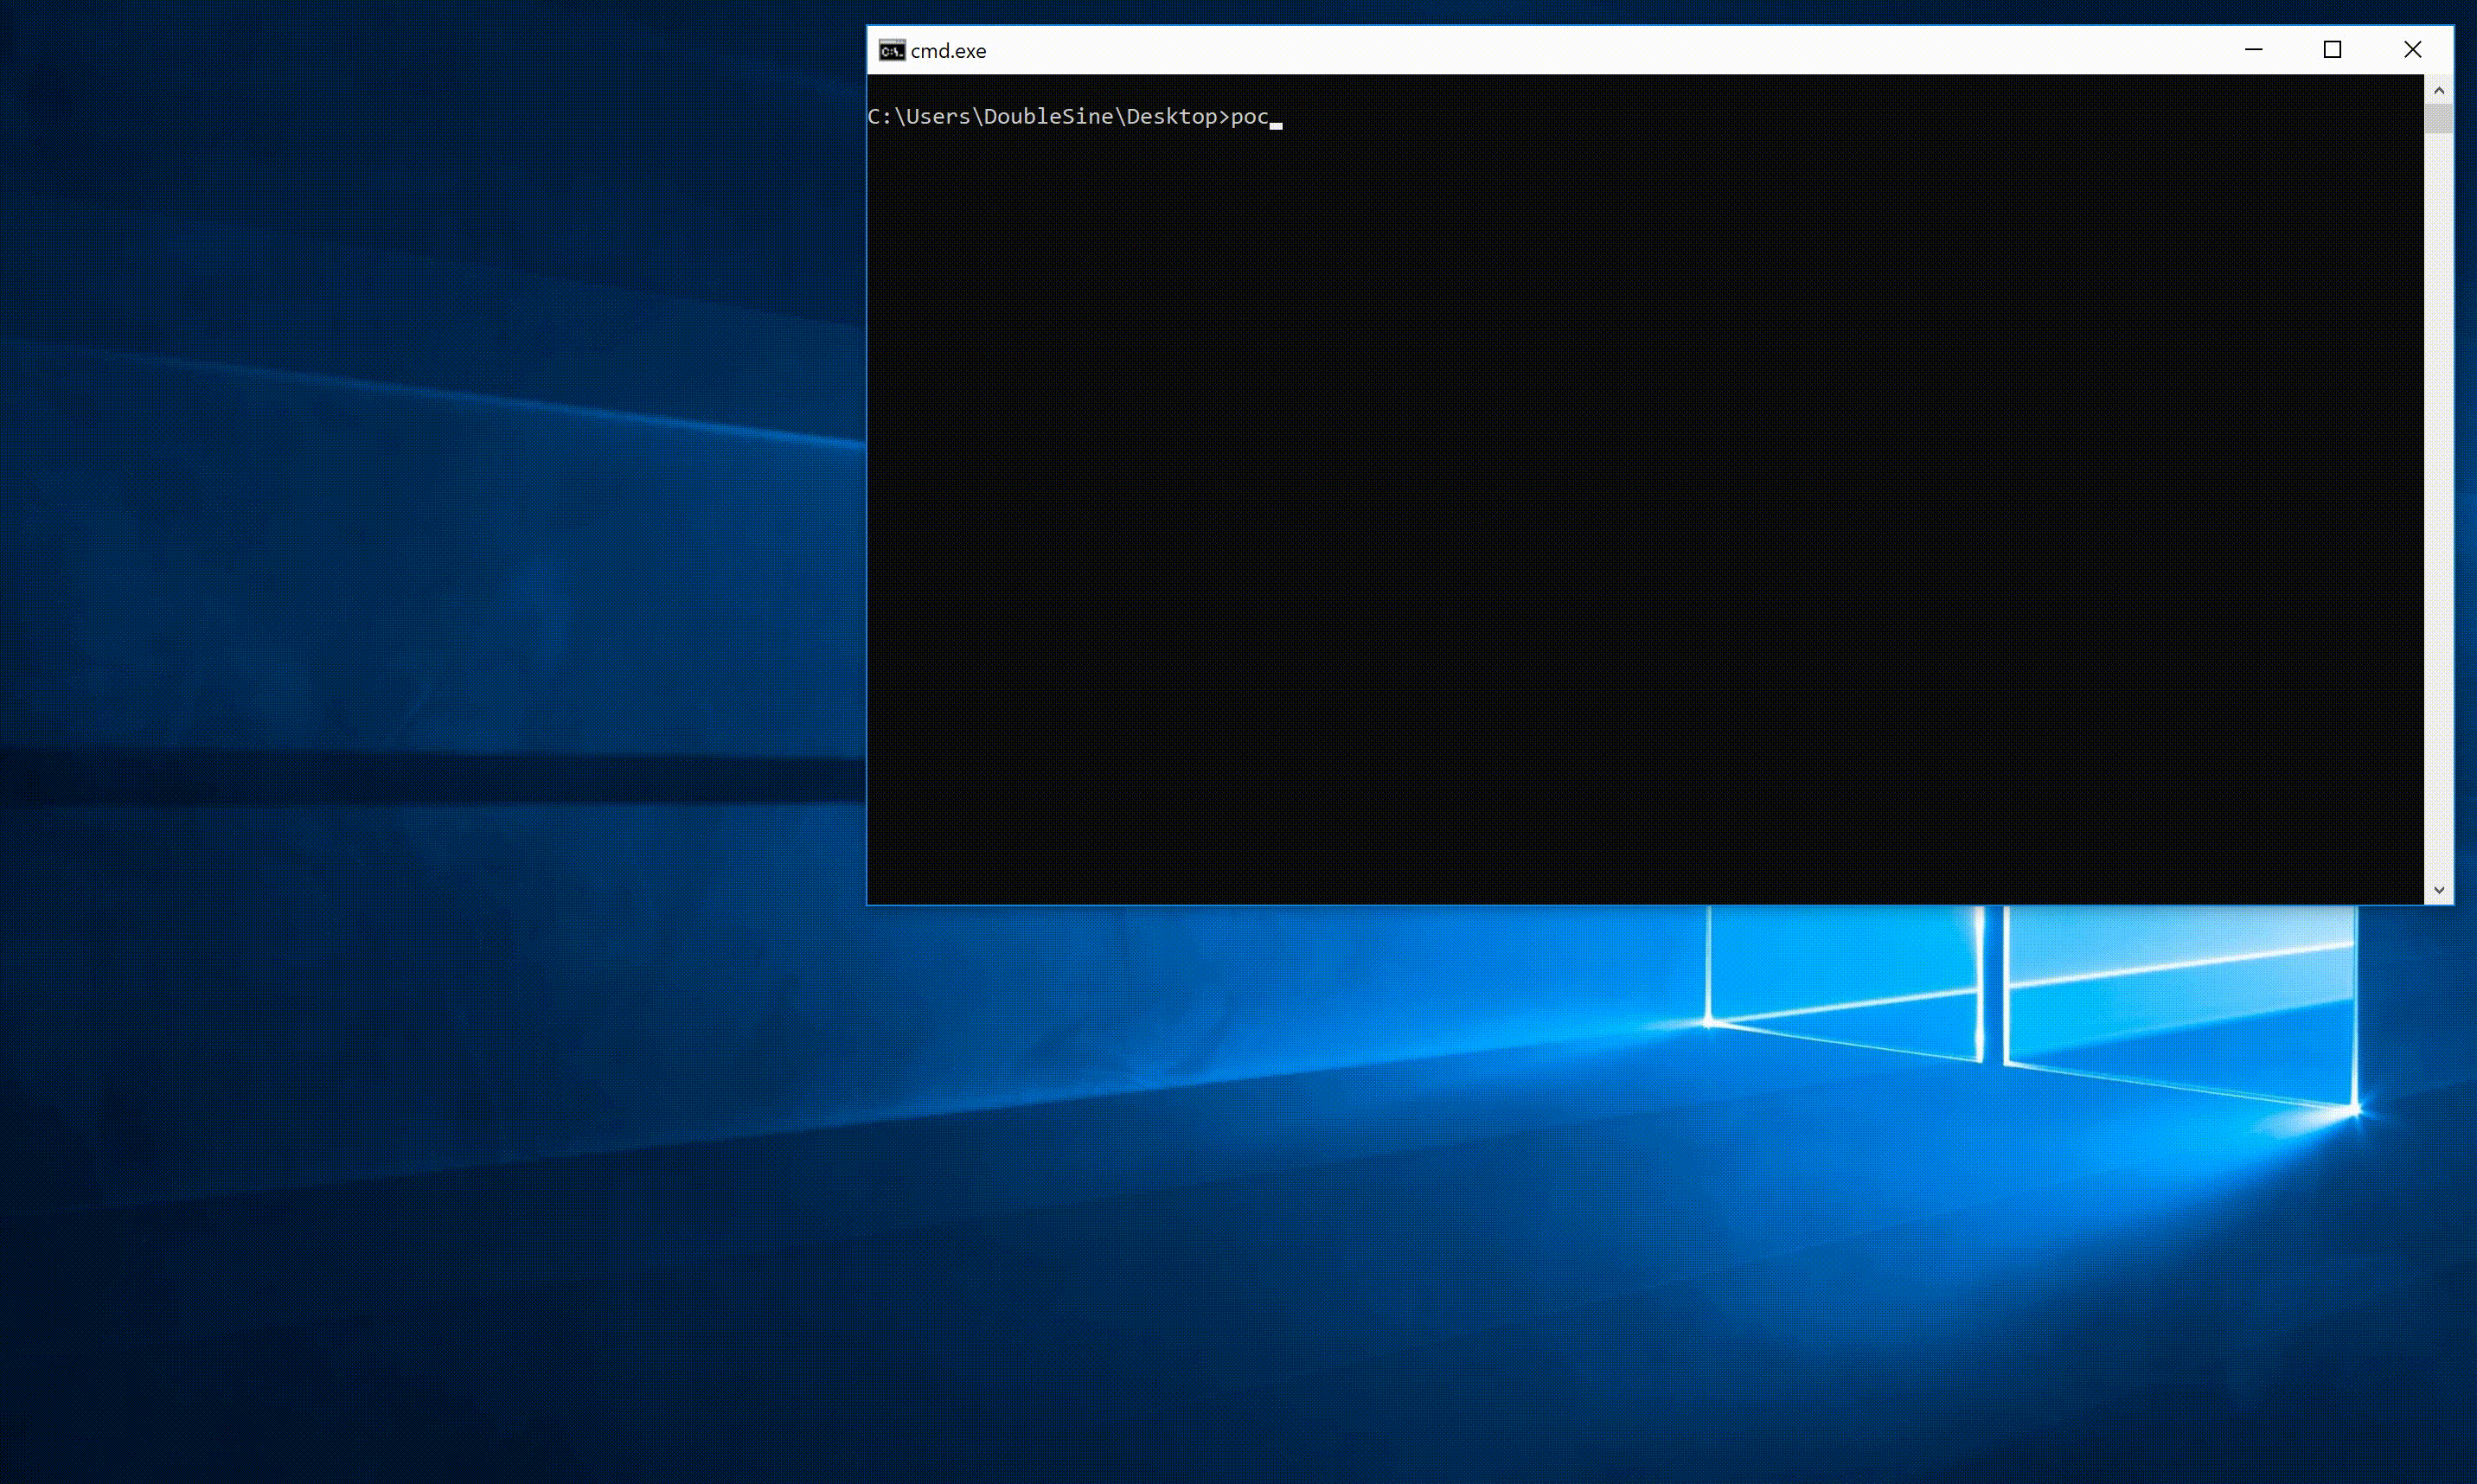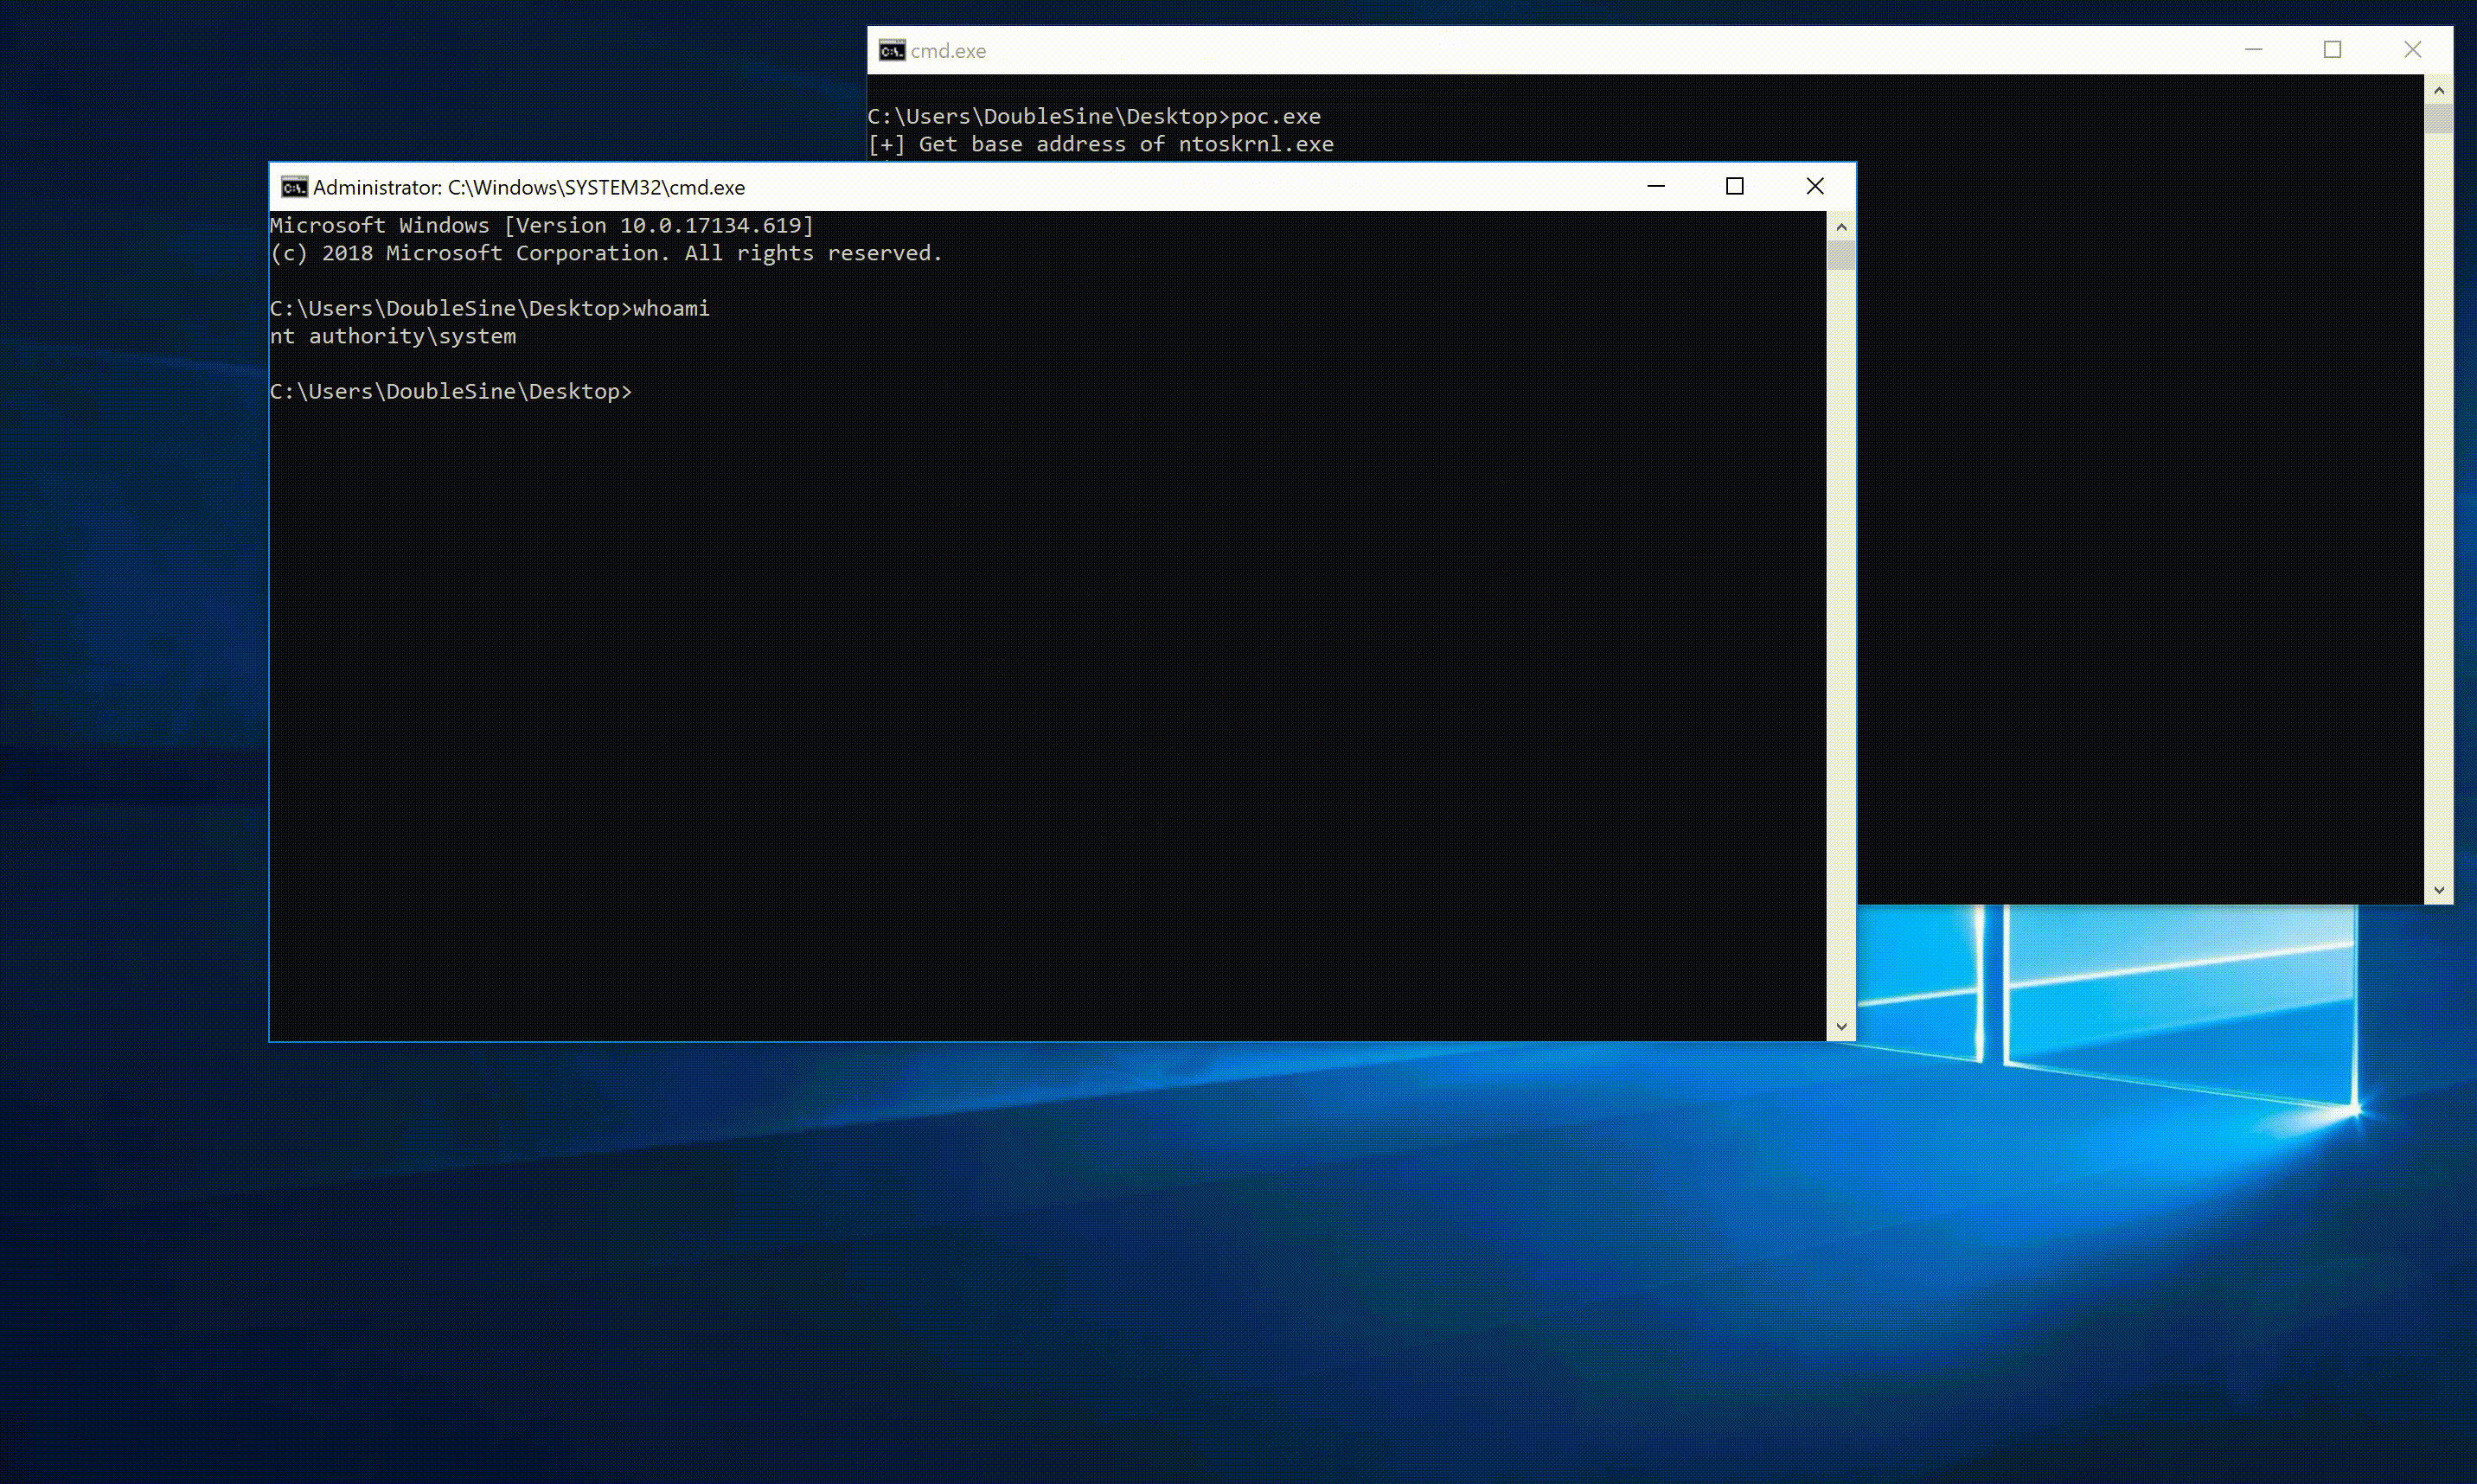
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
binary-exploitationexploitationprivilege-escalation+2
847 years ago
xsser preview

xsser

GitHubvarbaek/xsser

From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras

exploitationpayload-developmentpenetration-testing+3
4236 years ago
ShellGhost preview

ShellGhost

GitHublem0nsec/shellghost

A memory-based evasion technique which makes shellcode invisible from process start to end.

binary-analysisencryption-decryption-toolsexploitation+4
1.2k3 years ago
Previous1234Next
