
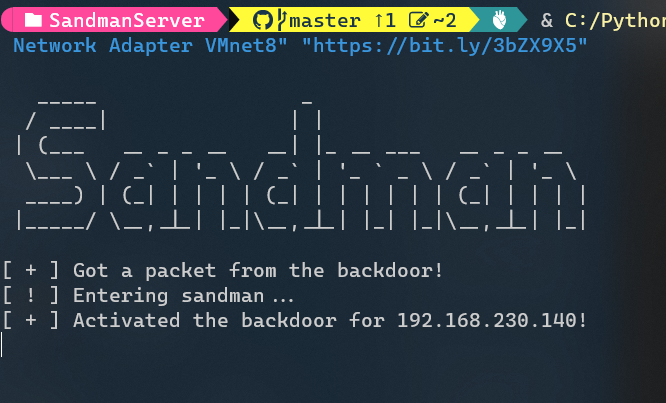
Sandman
 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
command-and-controlpayload-generationpersistence-mechanisms+2
816
idov31/sandmanNTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
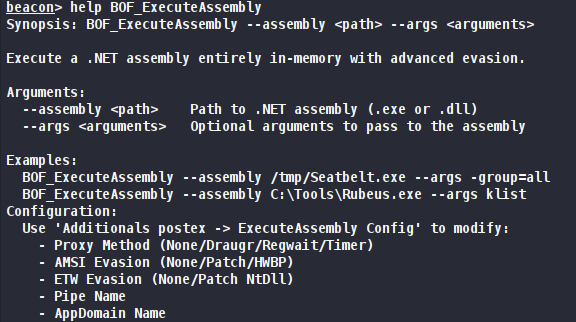 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
 rayanziani/bootjack
Exploit tooling for the EDK II UEFI PXE ICMP error overflow (CVE-2026-97631): crafts spoofed ICMP packets, plants a counterfeit EFI_EVENT, and dumps…