

CVE-2024-50986
 riftsandroses/cve-2024-50986
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
binary-exploitationexploitationpayload-generation+4
riftsandroses/cve-2024-50986An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 petrusviet/cve-2019-11581
Atlassian Jira unauthen template injection
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 hasherezade/masm_shc
A helper utility for creating shellcodes. Cleans MASM file generated by MSVC, gives refactoring hints.
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 rnnsz/cve-2008-4654
PoC exploit generator for CVE-2008-4654, a stack-based buffer overflow in VLC Media Player via crafted .ty+ files. Generates malicious payload file…

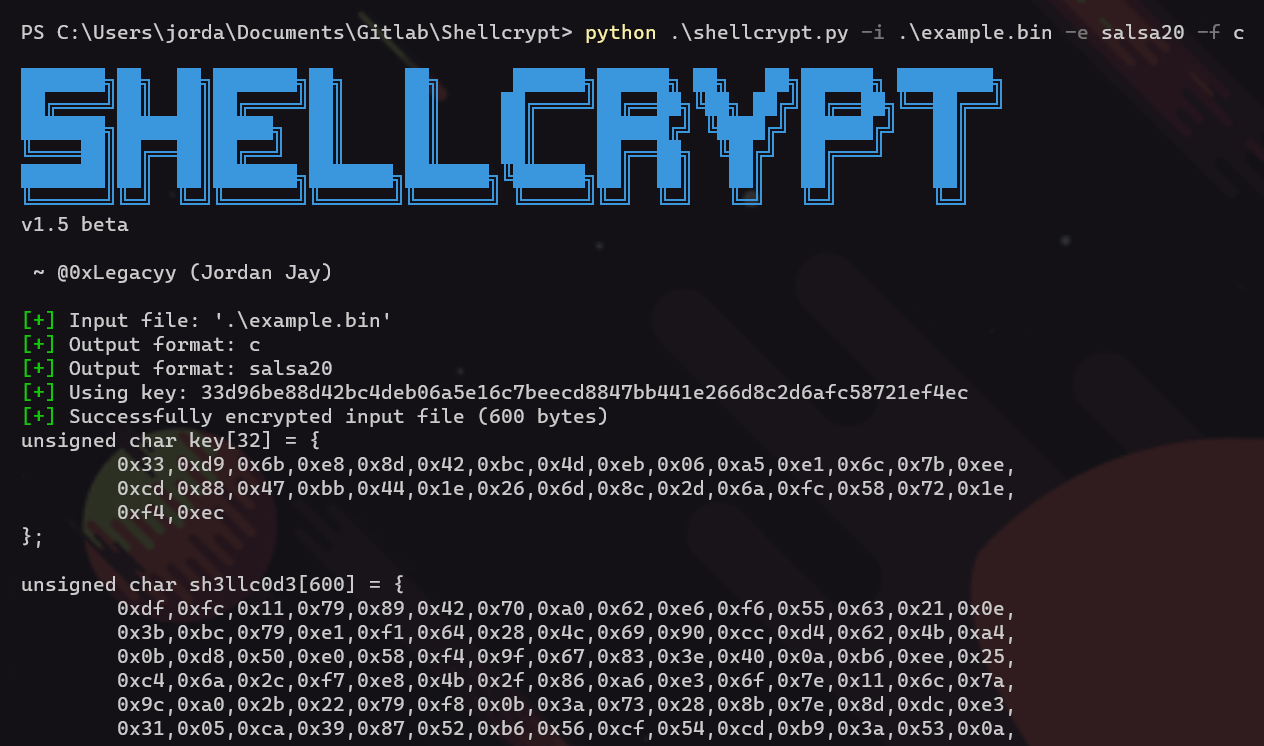 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
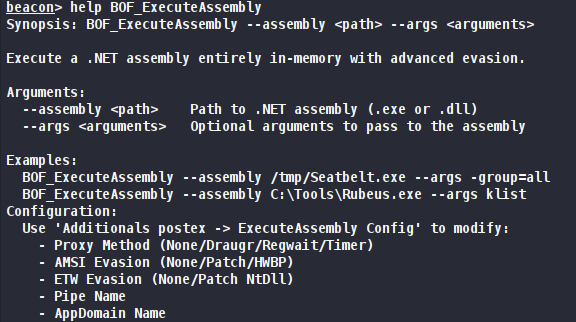 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 themalwareguardian/cve-2025-34096
SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.