CVE-2024-31317-PoC-Deployer

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.

AV/EDR evasion via direct system calls.

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)

Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…

Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…

Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…

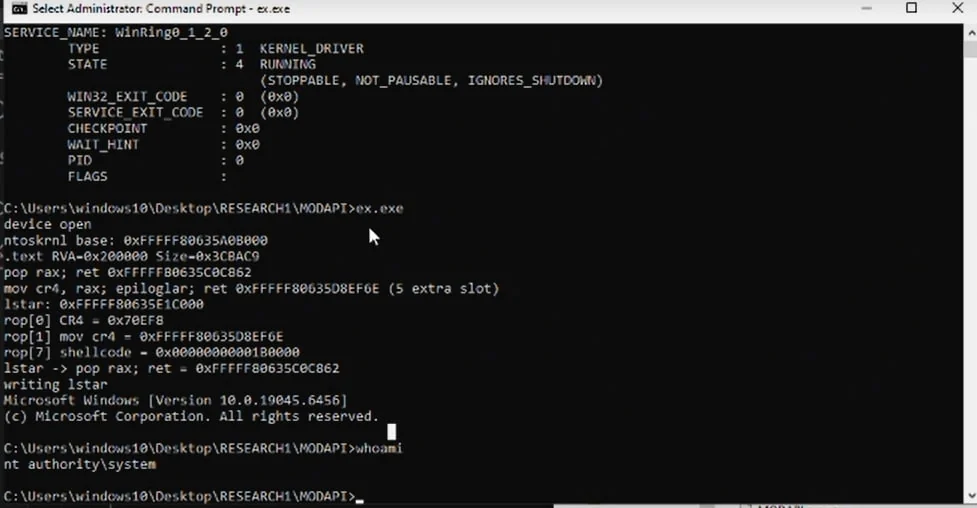
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.

Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched

A simple shell code encryptor/decryptor/executor to bypass anti virus.

A shellcode function to encrypt a running process image when sleeping.

Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…

Android 16 local privilege escalation exploit for realme RMX5200 using LD_PRELOAD-based preload.so chain to achieve temporary root access via…

A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass