

DVSA
 owasp/dvsa
a Damn Vulnerable Serverless Application
api-security-testingcloud-infrastructure-securitycloud-security+6
owasp/dvsaa Damn Vulnerable Serverless Application
 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
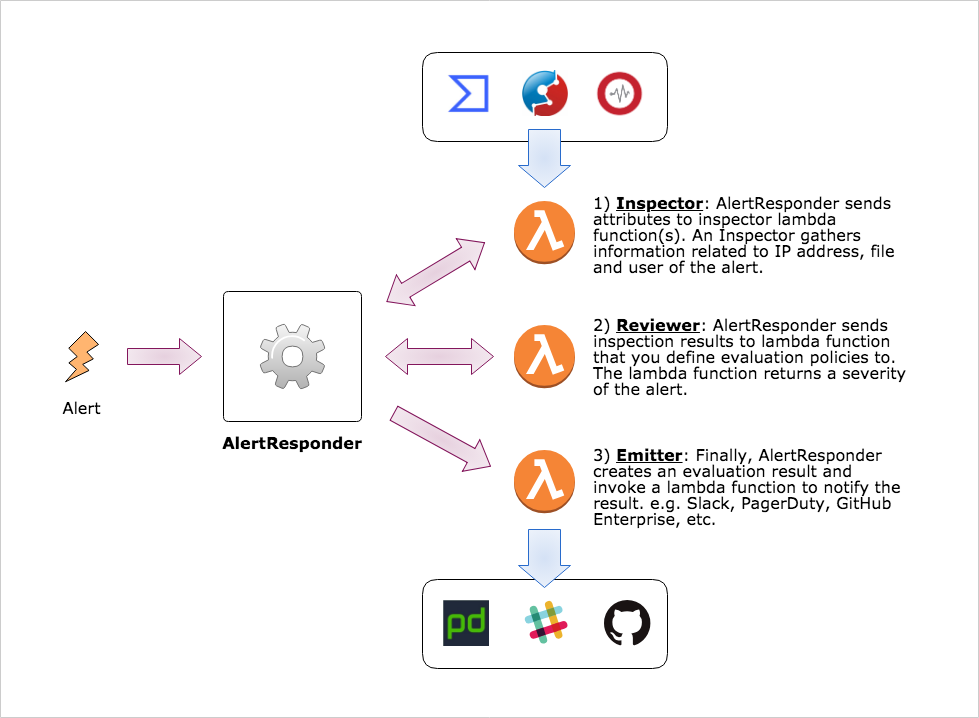 m-mizutani/alertresponder
Automatic security alert response framework by AWS Serverless Application Model
 aws/serverless-application-model
Transforms SAM templates into CloudFormation resources, generating Lambda functions, IAM roles, and policies with built-in serverless best practices.
 owasp/serverless-top-10-project
OWASP Serverless Top 10
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass