
pacu
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
cloud-infrastructure-securitycloud-securitydata-exfiltration+7
5.3k
rhinosecuritylabs/pacuThe AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 skyscanner/lambdaguard
AWS Serverless Security
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
 ivanesk315/cve-2026-28496
Docker lab reproducing the FOSSBilling pre-auth RCE chain (CVE-2026-27604 auth bypass + CVE-2026-28496 Twig SSTI) with a Python PoC and patched…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 cloud-custodian/cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
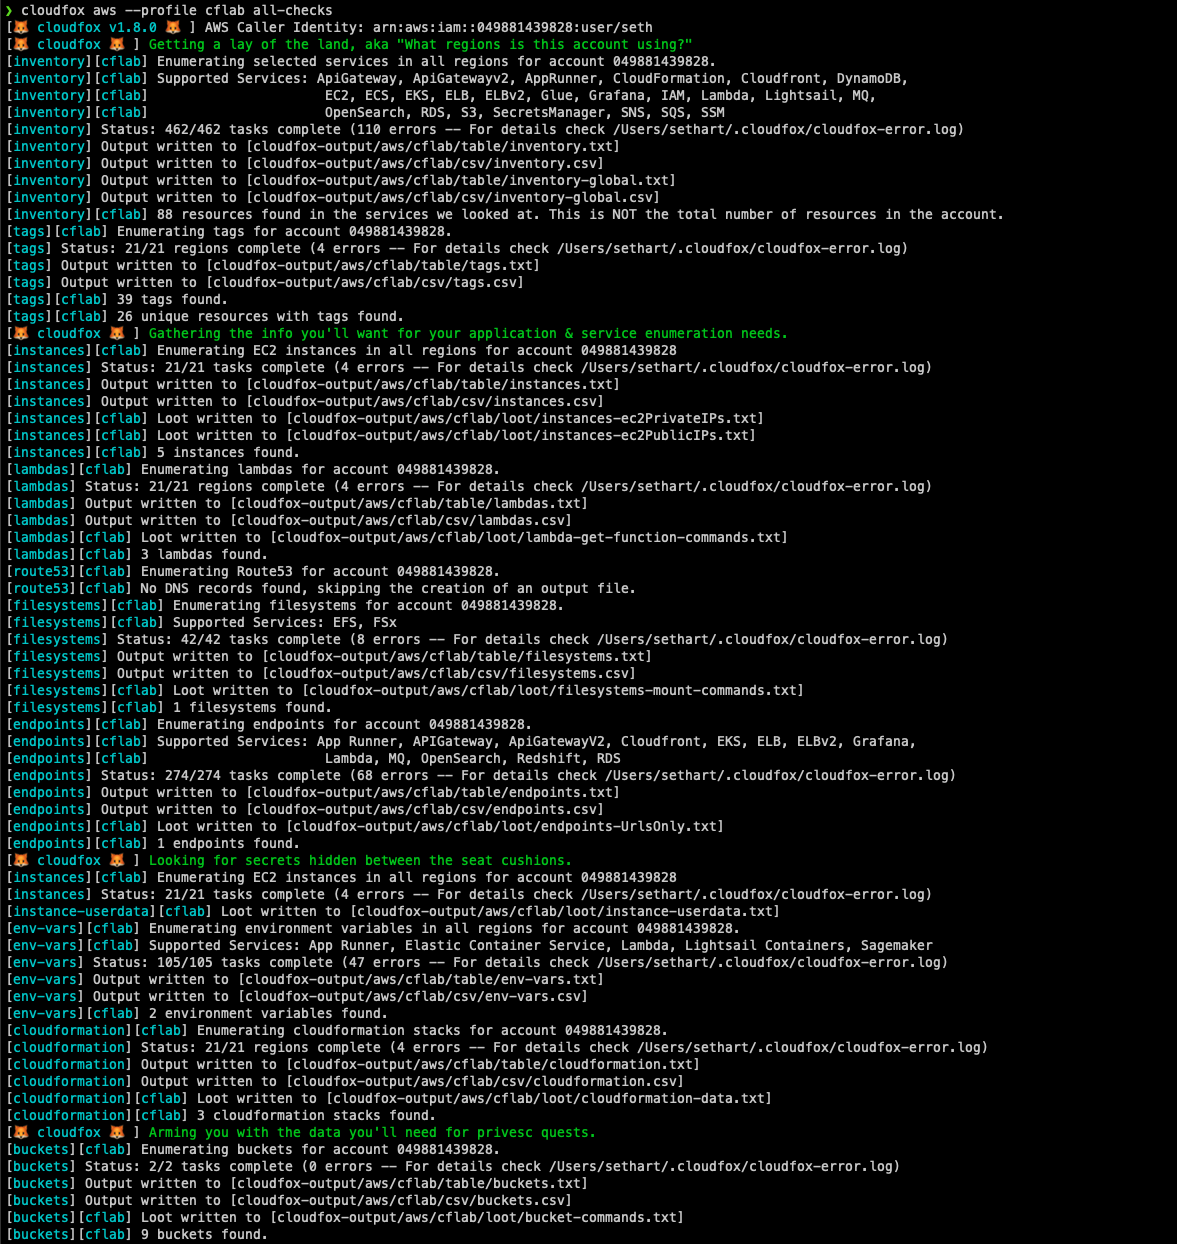 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.