
ScoutSuite
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+5
7.8k
nccgroup/scoutsuiteMulti-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
 cloud-custodian/cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources
 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 owasp/dvsa
a Damn Vulnerable Serverless Application
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 george0papasotiriou/cve-2026-9999-serverless-event-injection-to-code-overwrite
Proof-of-concept exploit for CVE-2026-9999, demonstrating path traversal in serverless object storage events that overwrites function source code to…
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 george0papasotiriou/cve-2026-21002-serverless-cold-start-credential-leakage-via-reused-tmp
PoC exploit for CVE-2026-21002 serverless cold-start credential leakage, demonstrating how reused Lambda /tmp directories expose AWS secrets to other…
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 serverless/serverless
CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
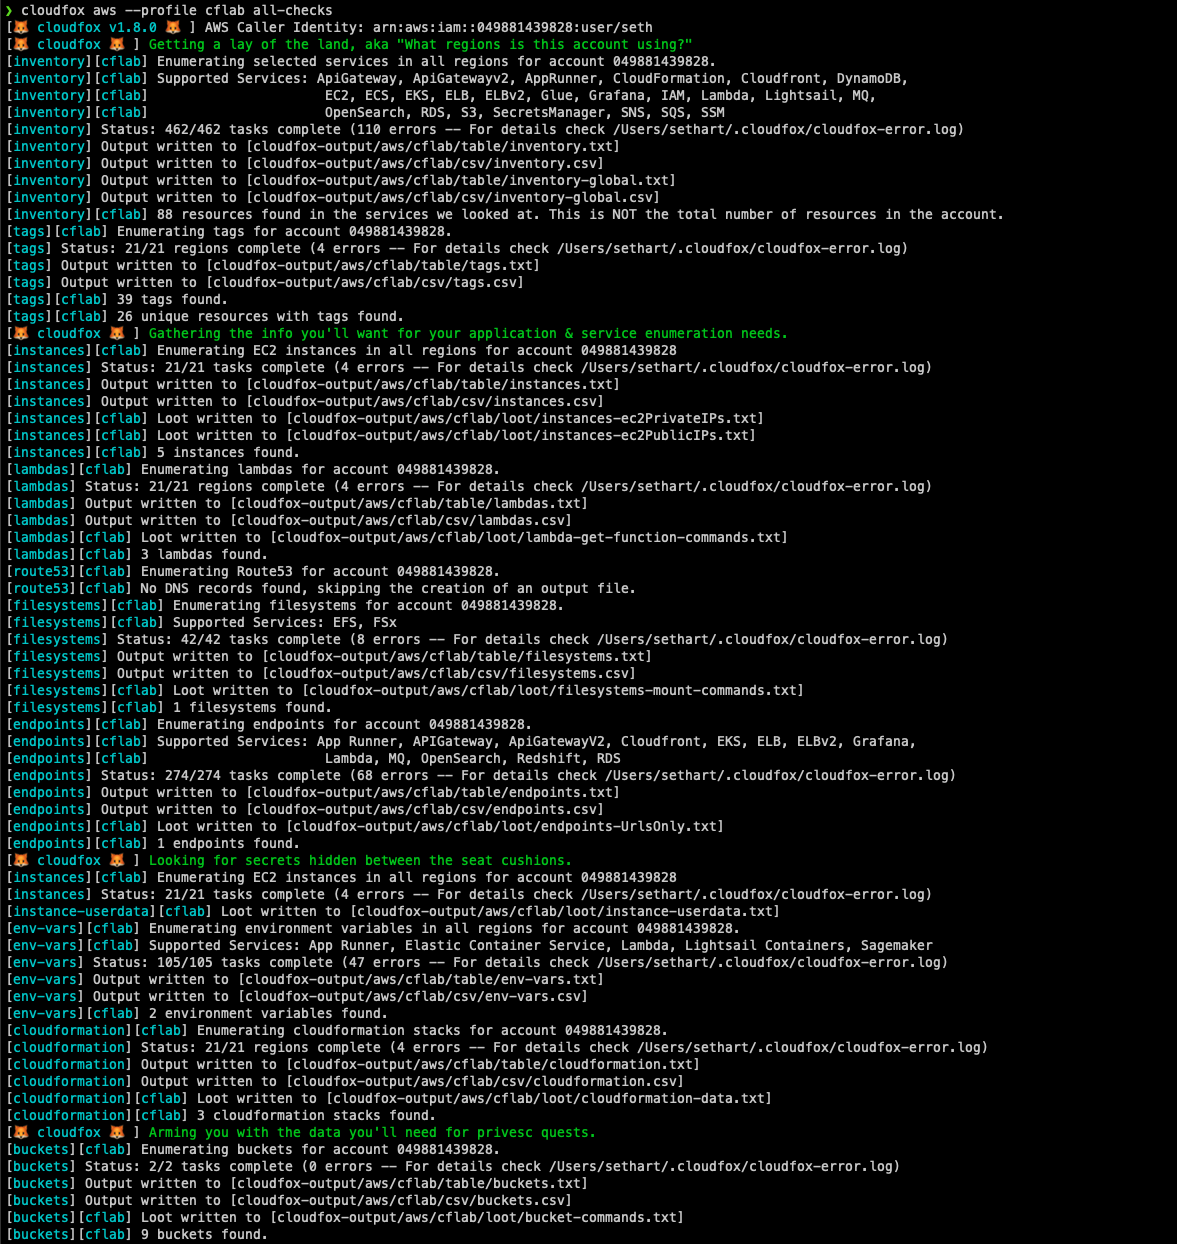 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…