
serverless
 serverless/serverless
CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
authenticationcloud-infrastructure-securitydevsecops+4
46.9k
serverless/serverlessCLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
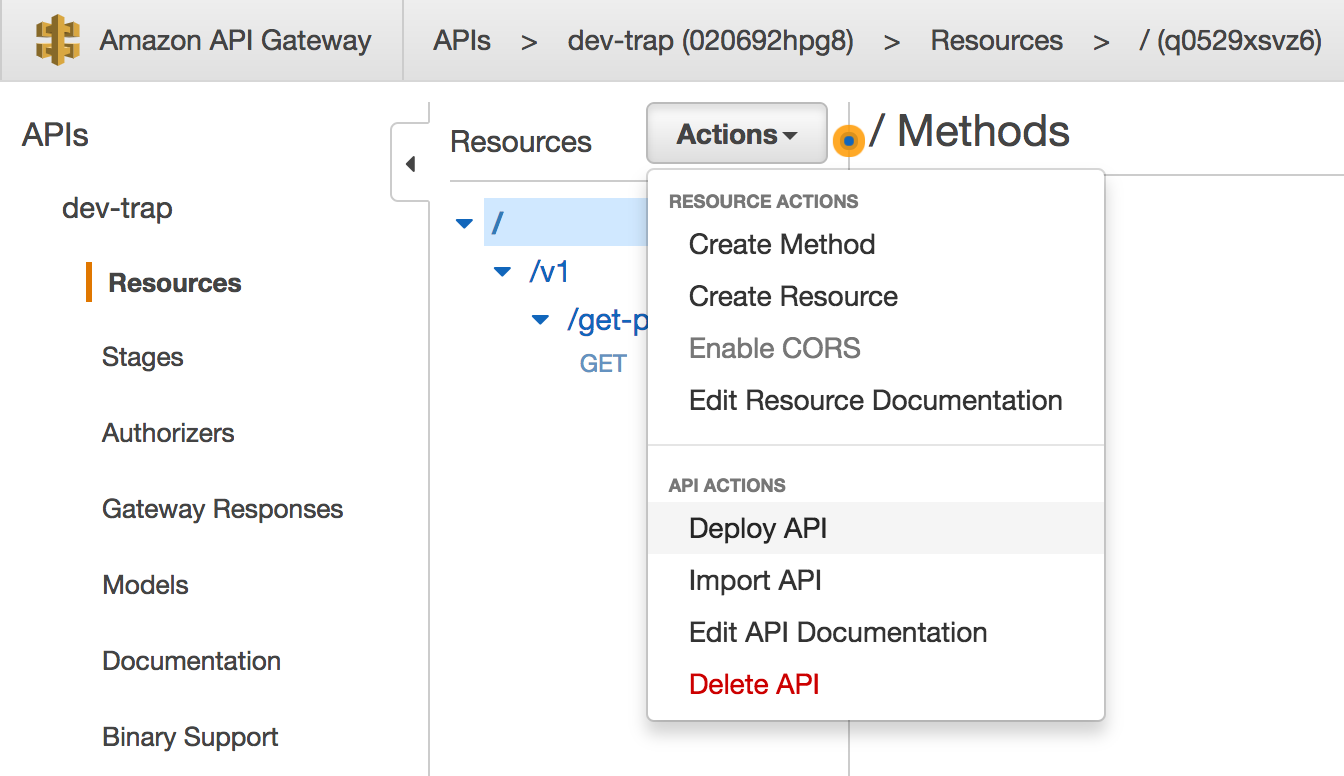 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
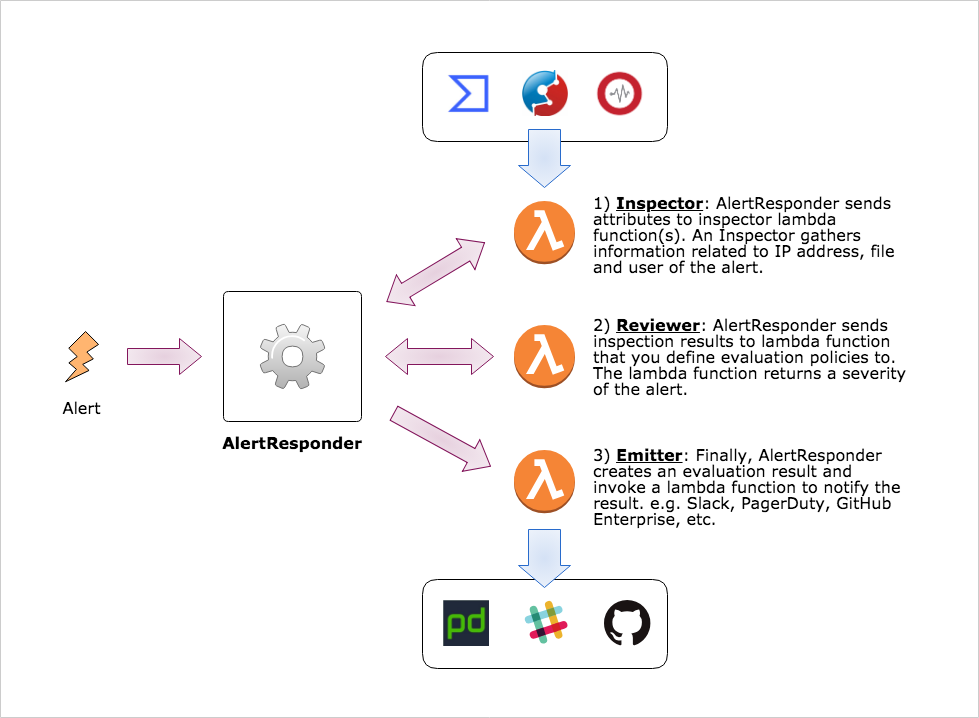 m-mizutani/alertresponder
Automatic security alert response framework by AWS Serverless Application Model
 airbnb/binaryalert
BinaryAlert: Serverless, Real-time & Retroactive Malware Detection.
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 fyoorer/shadowclone
Serverless task distribution framework that parallelizes CLI tools across thousands of cloud functions for rapid reconnaissance and data processing.
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 pumasecurity/serverless-prey
Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 george0papasotiriou/cve-2026-22015-serverless-function-environment-variable-injection-via-event
PoC for CVE-2026-22015: malicious event injects environment variables into serverless functions, overwriting secrets and enabling privilege…
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 we45/dvfaas-damn-vulnerable-functions-as-a-service
Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws