
honeyLambda
 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
cloud-securitydefensive-toolsincident-response+2
527
0x4d31/honeylambdahoneyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 we45/dvfaas-damn-vulnerable-functions-as-a-service
Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
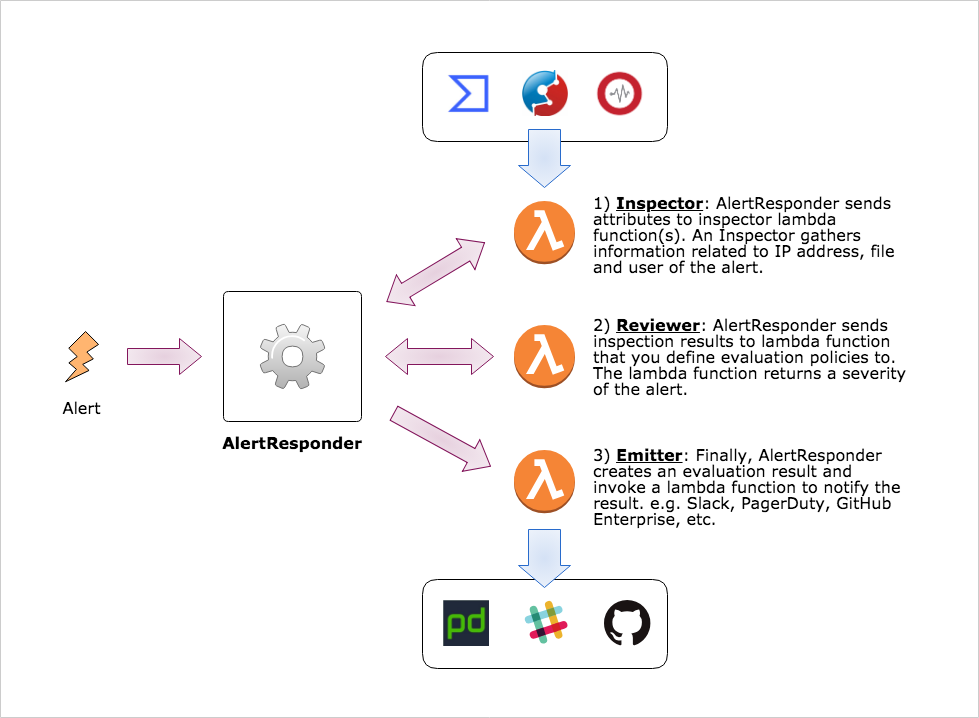 m-mizutani/alertresponder
Automatic security alert response framework by AWS Serverless Application Model
 fyoorer/shadowclone
Serverless task distribution framework that parallelizes CLI tools across thousands of cloud functions for rapid reconnaissance and data processing.
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 owasp/dvsa
a Damn Vulnerable Serverless Application
 pumasecurity/serverless-prey
Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 aws/serverless-application-model
Transforms SAM templates into CloudFormation resources, generating Lambda functions, IAM roles, and policies with built-in serverless best practices.
 serverless/serverless
CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
 skyscanner/lambdaguard
AWS Serverless Security
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool