CTT-Serverless-RCE-v1.0---Convergent-Time-Theory-Enhanced-MCP-Exploit

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

a Damn Vulnerable Serverless Application

Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.

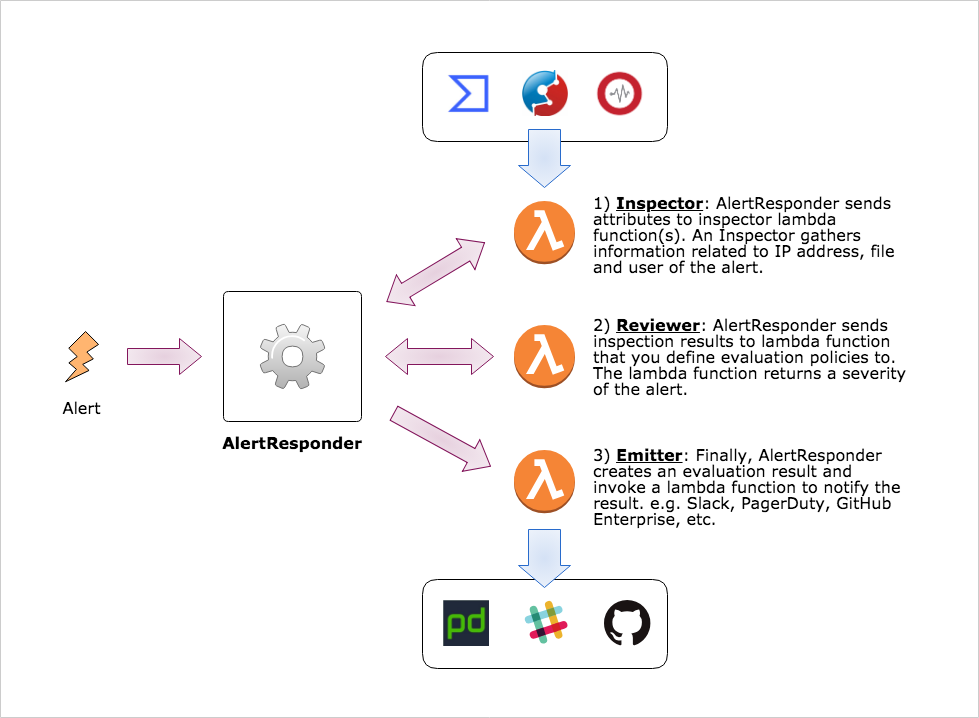
Automatic security alert response framework by AWS Serverless Application Model

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Transforms SAM templates into CloudFormation resources, generating Lambda functions, IAM roles, and policies with built-in serverless best practices.

Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…

CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool

Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.

BinaryAlert: Serverless, Real-time & Retroactive Malware Detection.

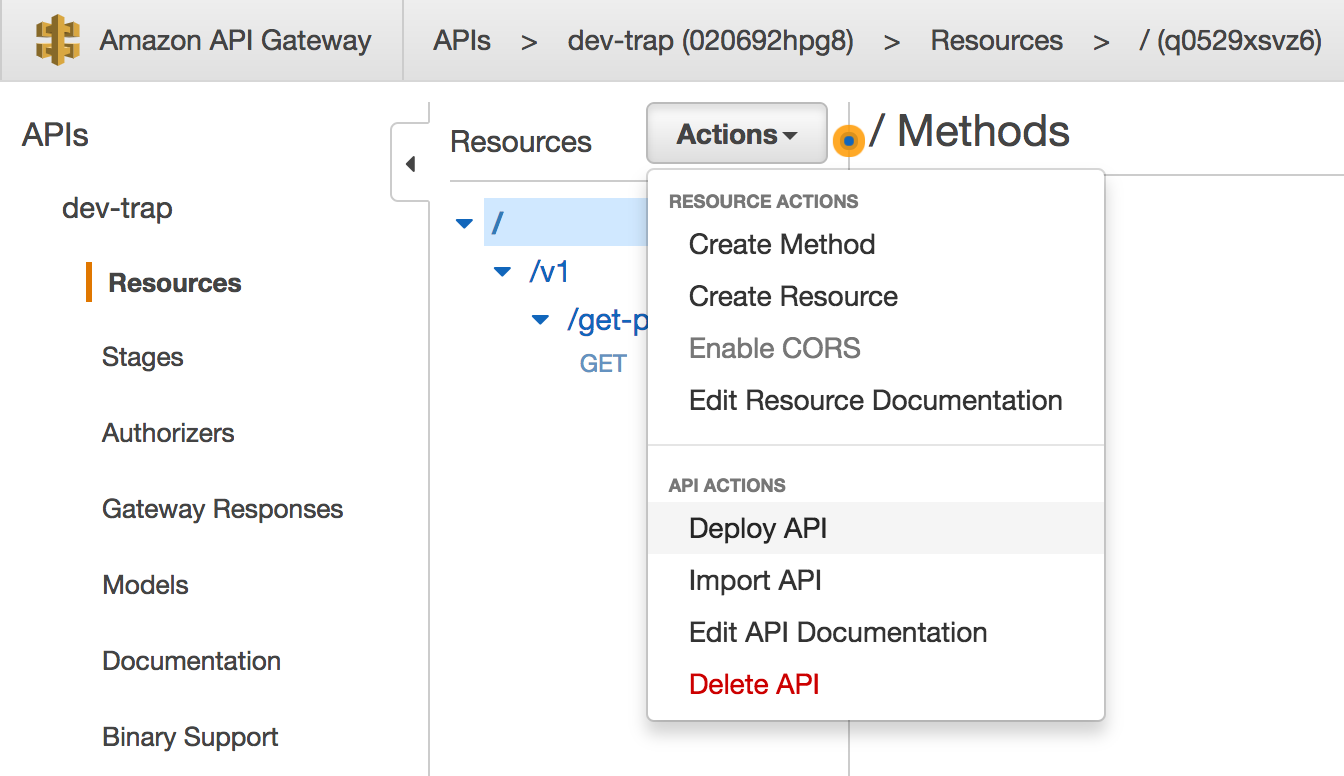
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…

OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws

OWASP Serverless Top 10

Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities

Simulates CVE-2026-23007 serverless cold-start memory remanence; demonstrates how persistent global state across Lambda invocations can leak secrets…

OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass

AWS Serverless Security