
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
CVE-2026-28496 preview

CVE-2026-28496

GitHubivanesk315/cve-2026-28496

Docker lab reproducing the FOSSBilling pre-auth RCE chain (CVE-2026-27604 auth bypass + CVE-2026-28496 Twig SSTI) with a Python PoC and patched…
educationexploitationlabs-practice+6
1 month ago
CVE-2026-15583 preview

CVE-2026-15583

GitHubabraxas/cve-2026-15583

Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…

api-securitydata-exfiltrationexploitation+6
4 days ago
CVE-2026-22015-Serverless-Function-Environment-Variable-Injection-via-Event preview

CVE-2026-22015-Serverless-Function-Environment-Variable-Injection-via-Event

GitHubgeorge0papasotiriou/cve-2026-22015-serverless-function-environment-variable-injection-via-event

PoC for CVE-2026-22015: malicious event injects environment variables into serverless functions, overwriting secrets and enabling privilege…
cloud-securityeducationexploitation+3
12 months ago
CTT-Serverless-RCE-v1.0---Convergent-Time-Theory-Enhanced-MCP-Exploit preview

CTT-Serverless-RCE-v1.0---Convergent-Time-Theory-Enhanced-MCP-Exploit

GitHubsimoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

ai-securitycloud-securitycommand-and-control+8
9 months ago
semgrep preview

semgrep

GitHubsemgrep/semgrep

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
api-securityapi-security-testingcode-analysis+9
16.2k4 days ago
stratus-red-team preview

stratus-red-team

GitHubdatadog/stratus-red-team

:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud

adversarial-attackcloud-infrastructure-securitycloud-security+5
2.4k3 days ago
cloudfox preview

cloudfox

GitHubbishopfox/cloudfox

Automating situational awareness for cloud penetration tests.

cloud-infrastructure-securitycloud-securityexploitation+7
2.6k2 days ago
DVSA preview

DVSA

GitHubowasp/dvsa

a Damn Vulnerable Serverless Application
api-security-testingcloud-infrastructure-securitycloud-security+6
5443 years ago
DVFaaS-Damn-Vulnerable-Functions-as-a-Service preview

DVFaaS-Damn-Vulnerable-Functions-as-a-Service

GitHubwe45/dvfaas-damn-vulnerable-functions-as-a-service

Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities
cloud-securityeducationlabs-practice+1
1397 years ago
CVE-2026-21002-Serverless-Cold-Start-Credential-Leakage-via-Reused-tmp preview

CVE-2026-21002-Serverless-Cold-Start-Credential-Leakage-via-Reused-tmp

GitHubgeorge0papasotiriou/cve-2026-21002-serverless-cold-start-credential-leakage-via-reused-tmp

PoC exploit for CVE-2026-21002 serverless cold-start credential leakage, demonstrating how reused Lambda /tmp directories expose AWS secrets to other…
cloud-infrastructure-securitycloud-securitydata-exfiltration+4
3 months ago
cloudgoat preview

cloudgoat

GitHubrhinosecuritylabs/cloudgoat

CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool

cloud-securityctfeducation+5
3.7k18 days ago
pacu preview

pacu

GitHubrhinosecuritylabs/pacu

The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
cloud-infrastructure-securitycloud-securitydata-exfiltration+7
5.3k7 months ago
binaryalert preview

binaryalert

GitHubairbnb/binaryalert

BinaryAlert: Serverless, Real-time & Retroactive Malware Detection.
cloud-securitydefensive-toolsmalware-analysis+2
1.5k6 years ago
capsule preview

capsule

GitHubcapsulerun/capsule

Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
ai-securitycloud-securitycontainer-security+5
29420 days ago
Serverless-Goat preview

Serverless-Goat

GitHubowasp/serverless-goat

OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws

cloud-securityeducationlabs-practice+3
3307 years ago
Serverless-Top-10-Project preview

Serverless-Top-10-Project

GitHubowasp/serverless-top-10-project

OWASP Serverless Top 10
cloud-securitycurated-resourceseducation+3
2176 years ago
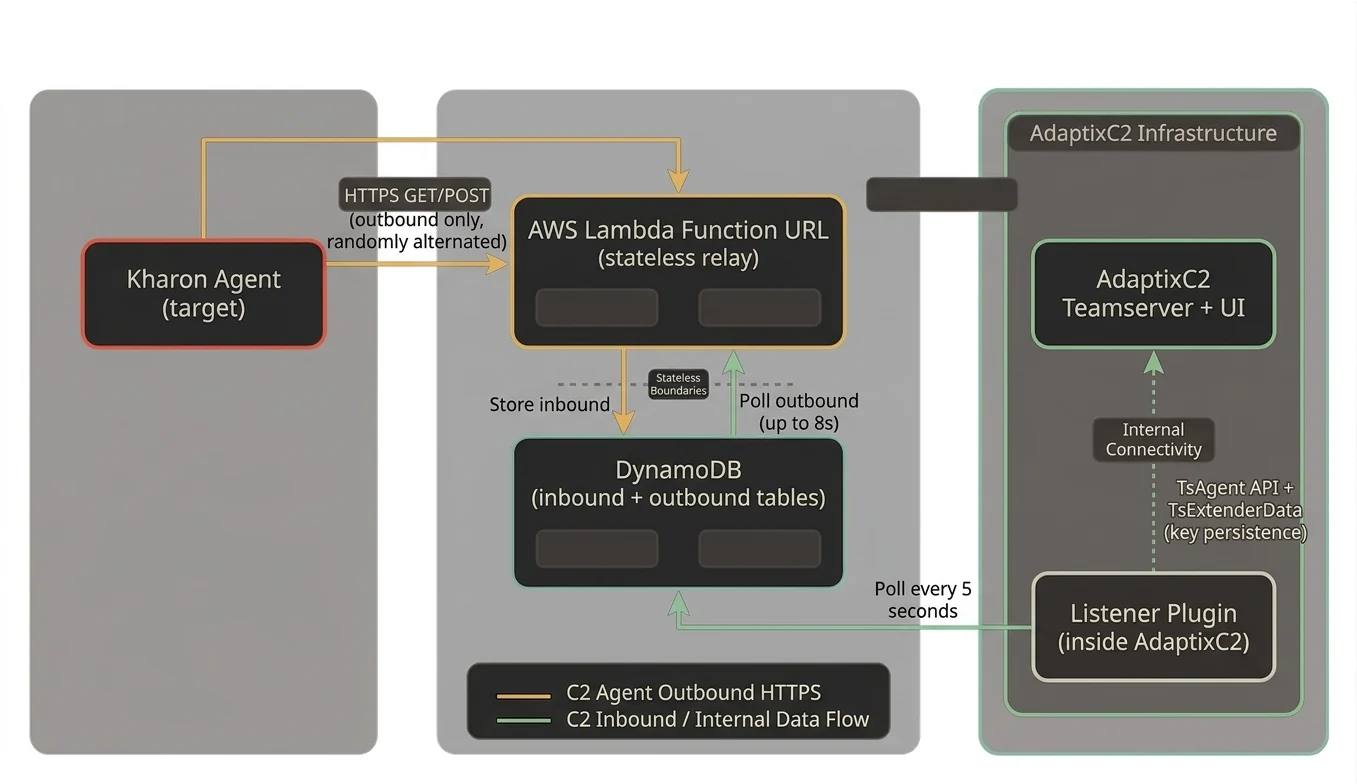
adaptix-serverless-c2 preview

adaptix-serverless-c2

GitHubstillbigjosh/adaptix-serverless-c2

Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.
cloud-infrastructure-securitycloud-securitycommand-and-control+8
333 days ago
CVE-2026-9999-Serverless-Event-Injection-to-Code-Overwrite preview

CVE-2026-9999-Serverless-Event-Injection-to-Code-Overwrite

GitHubgeorge0papasotiriou/cve-2026-9999-serverless-event-injection-to-code-overwrite

Proof-of-concept exploit for CVE-2026-9999, demonstrating path traversal in serverless object storage events that overwrites function source code to…

cloud-infrastructure-securitycloud-securityeducation+3
3 months ago
Previous123Next