
roninforge-hono
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
api-securitycloud-securitycode-analysis+8
roninforge/roninforge-honoCursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 owasp/dvsa
a Damn Vulnerable Serverless Application
 we45/dvfaas-damn-vulnerable-functions-as-a-service
Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities
 owasp/serverless-top-10-project
OWASP Serverless Top 10
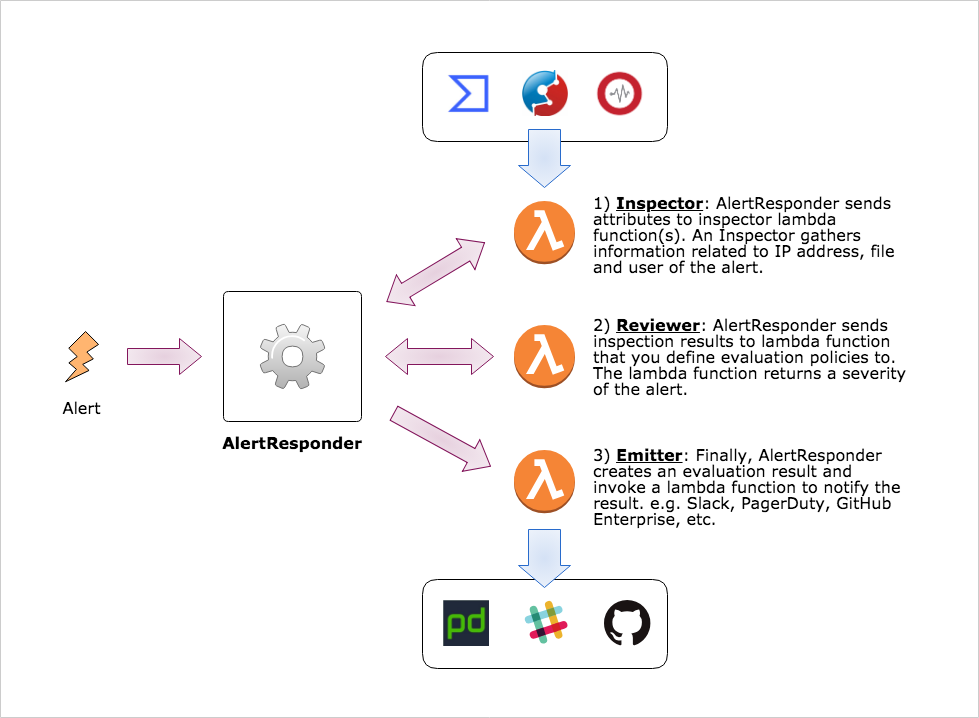 m-mizutani/alertresponder
Automatic security alert response framework by AWS Serverless Application Model
 airbnb/binaryalert
BinaryAlert: Serverless, Real-time & Retroactive Malware Detection.
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…