serverless-application-model

Transforms SAM templates into CloudFormation resources, generating Lambda functions, IAM roles, and policies with built-in serverless best practices.

Transforms SAM templates into CloudFormation resources, generating Lambda functions, IAM roles, and policies with built-in serverless best practices.

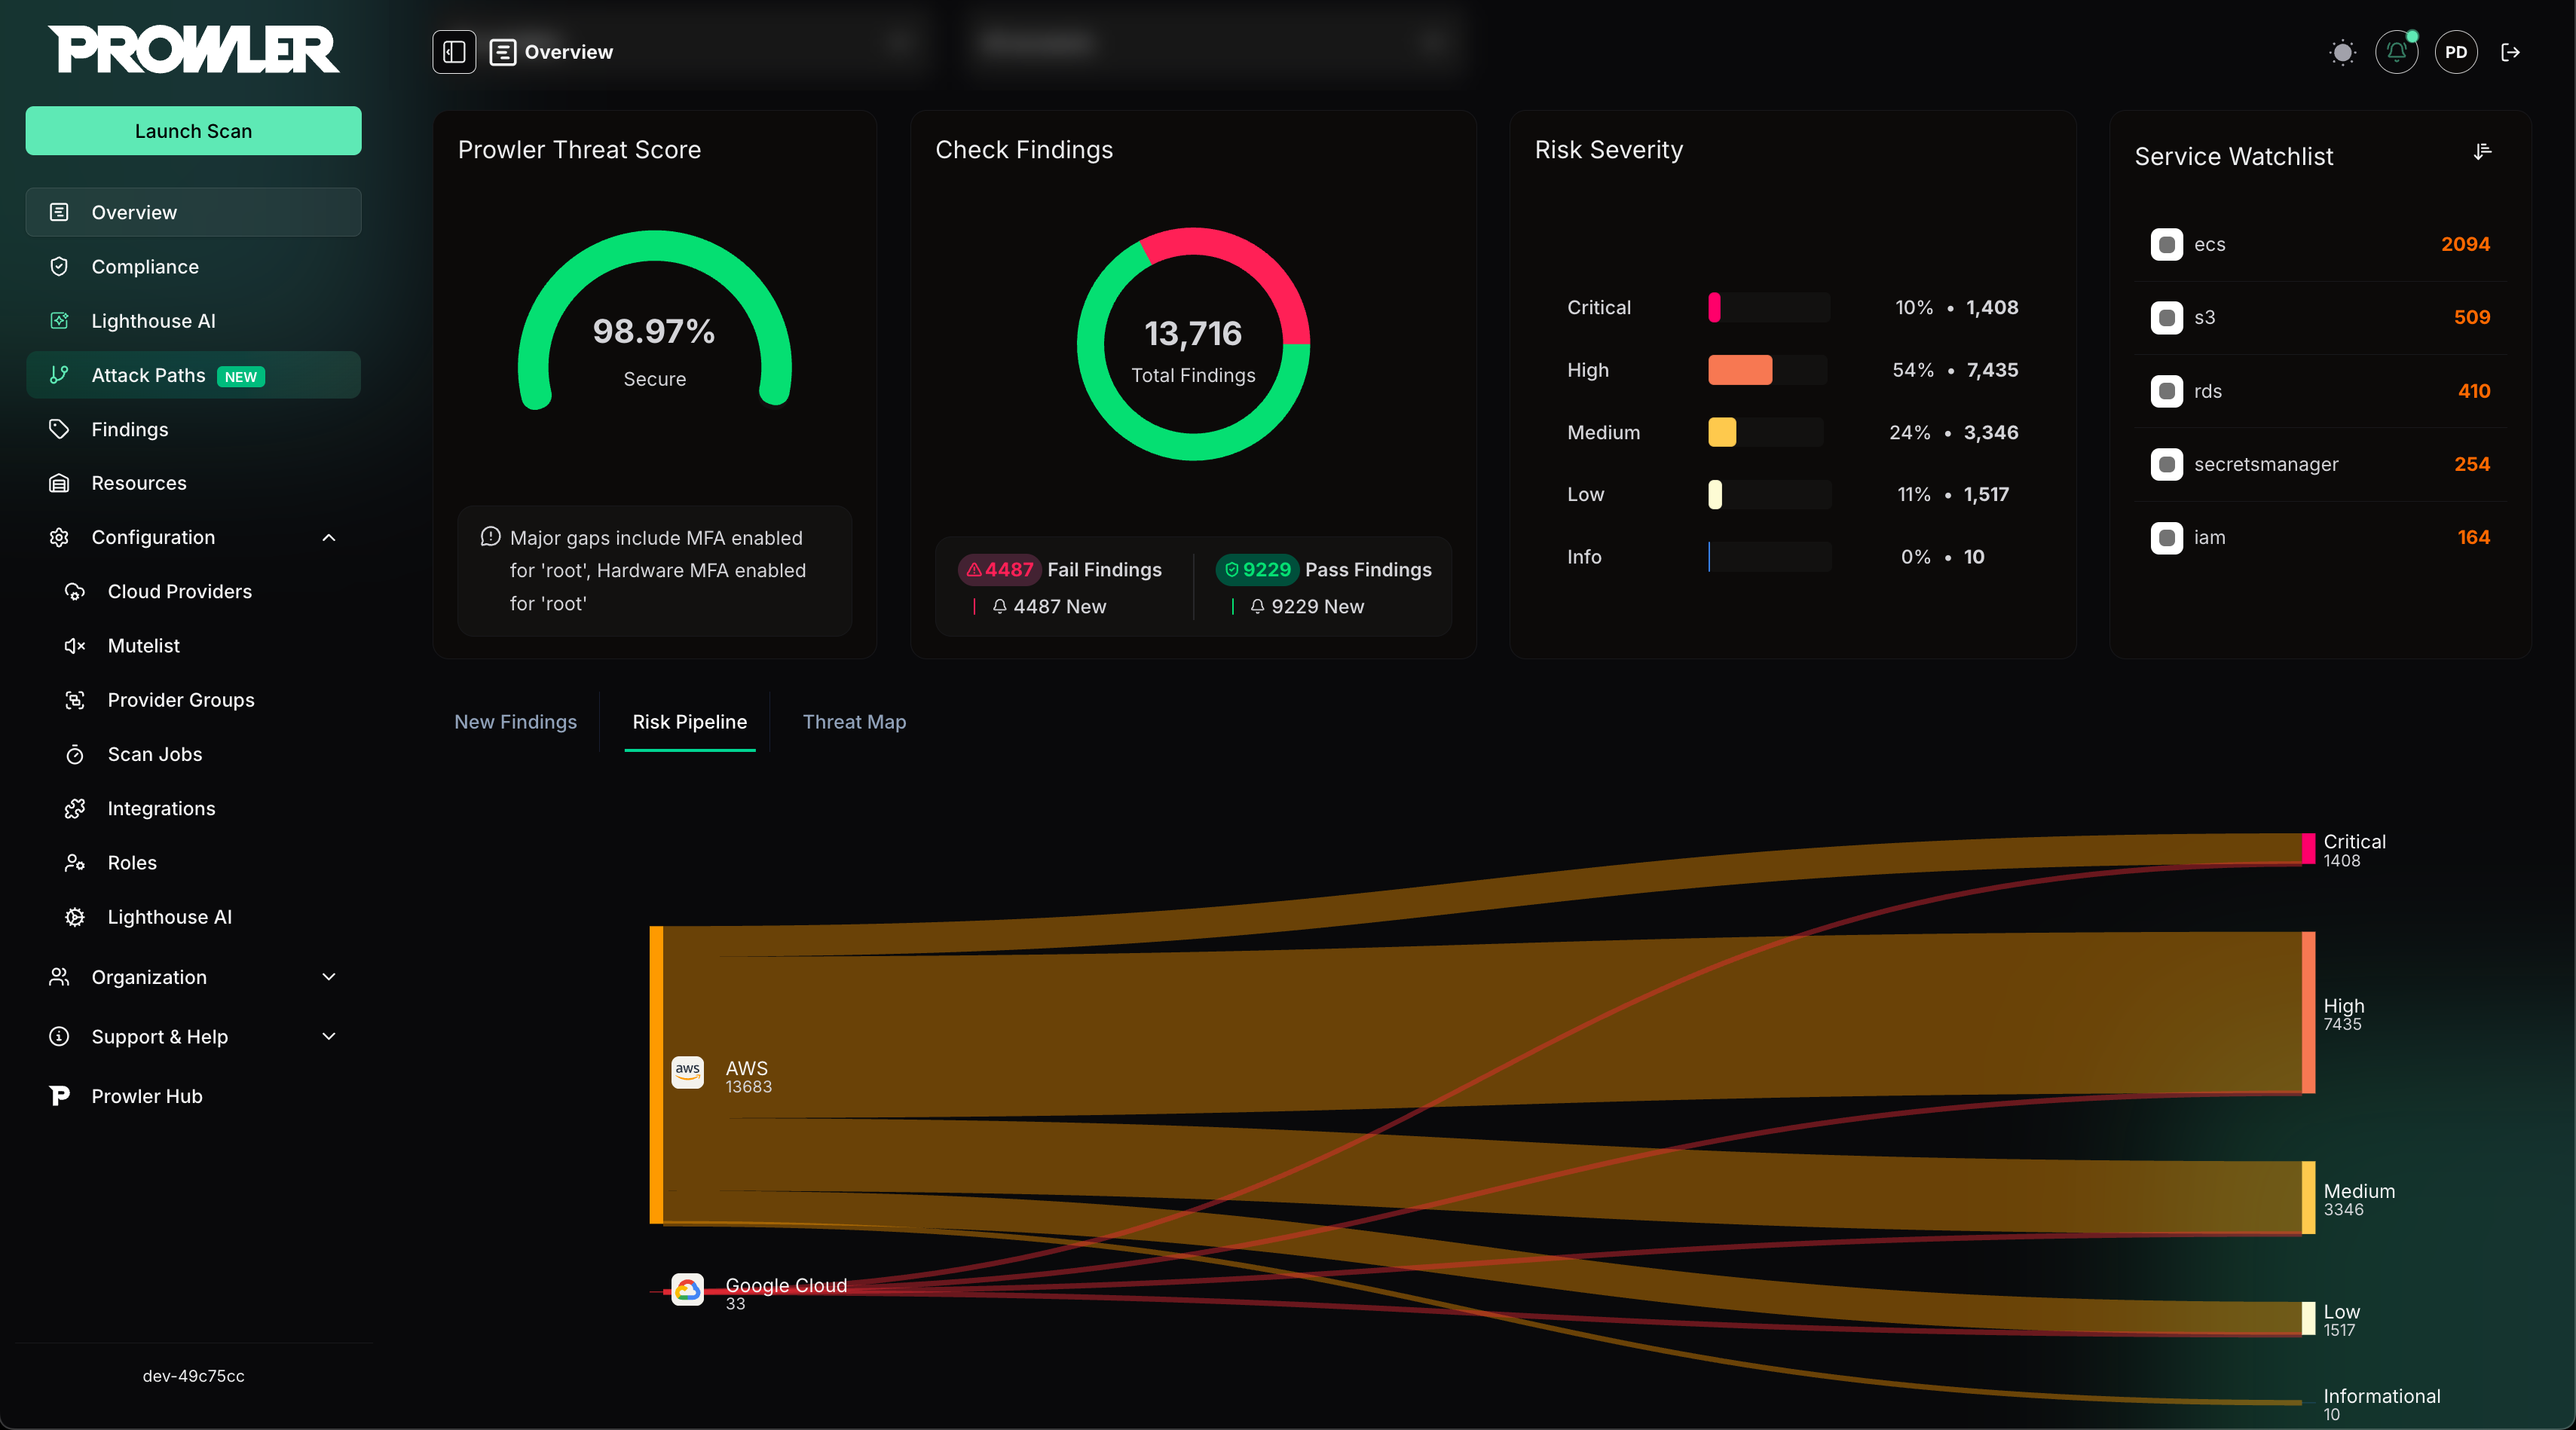
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources

Snyk CLI scans and monitors your projects for security vulnerabilities.

Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…

:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud

Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…

Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.

OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass

Secure and fast microVMs for serverless computing.

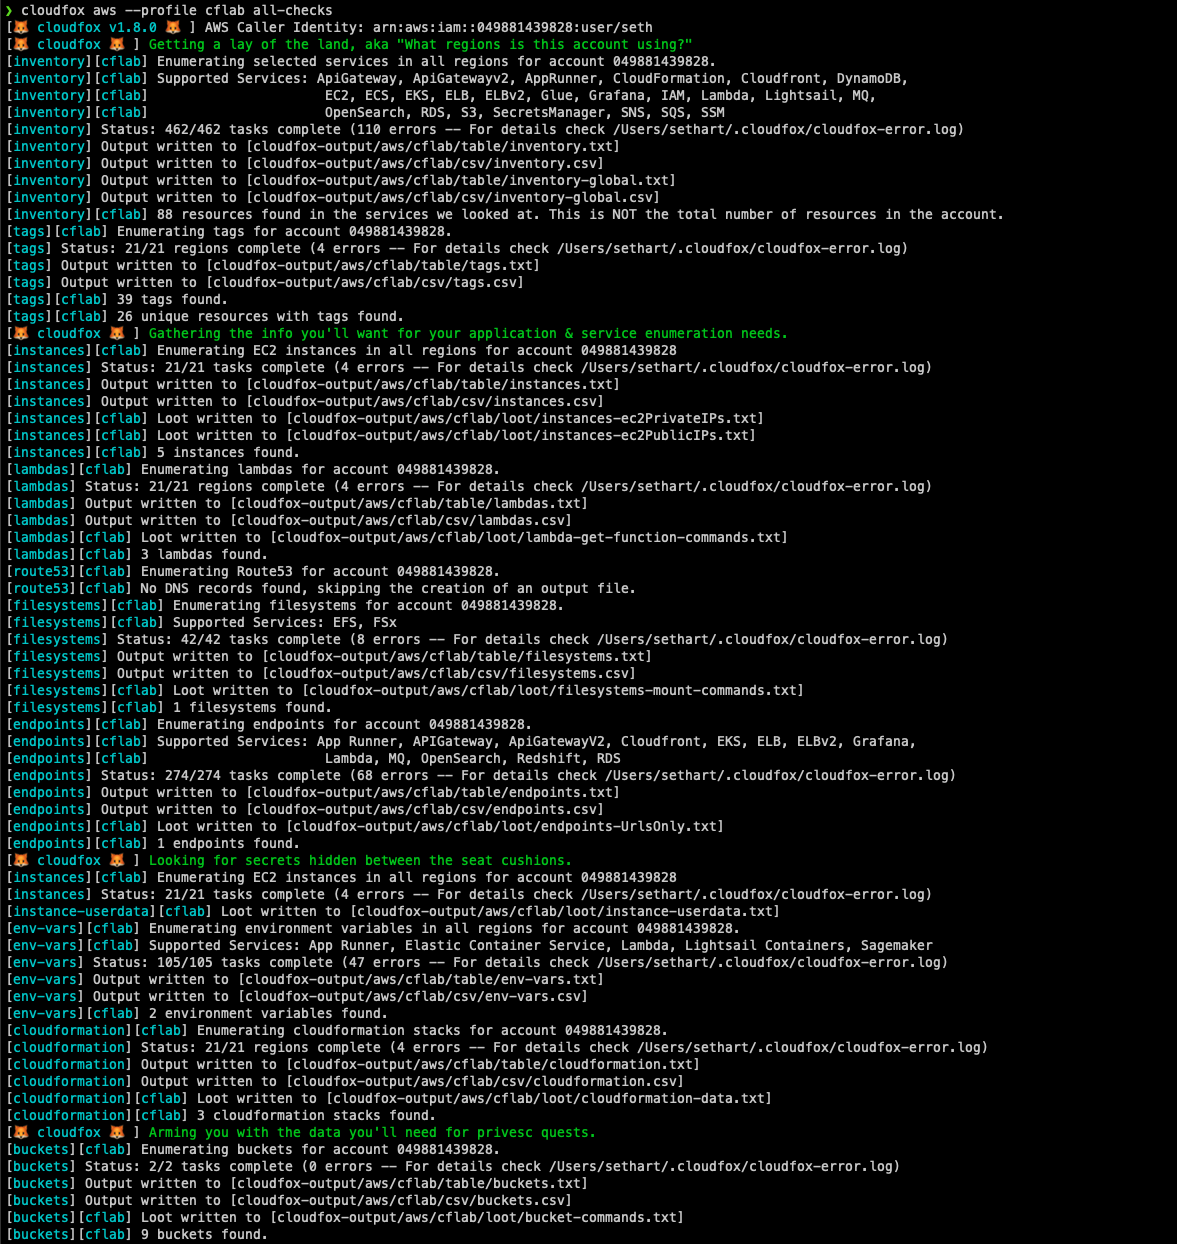
Automating situational awareness for cloud penetration tests.

PoC exploit for CVE-2026-21002 serverless cold-start credential leakage, demonstrating how reused Lambda /tmp directories expose AWS secrets to other…

Proof-of-concept exploit for CVE-2026-9999, demonstrating path traversal in serverless object storage events that overwrites function source code to…

Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.