
CVE-2026-86259
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
api-securitycloud-securitydata-exfiltration+6
uziii2208/cve-2026-86259OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 george0papasotiriou/cve-2026-23007-serverless-cold-start-memory-remanence-data-leakage-
Simulates CVE-2026-23007 serverless cold-start memory remanence; demonstrates how persistent global state across Lambda invocations can leak secrets…
 george0papasotiriou/cve-2026-22015-serverless-function-environment-variable-injection-via-event
PoC for CVE-2026-22015: malicious event injects environment variables into serverless functions, overwriting secrets and enabling privilege…
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 pumasecurity/serverless-prey
Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions
 fyoorer/shadowclone
Serverless task distribution framework that parallelizes CLI tools across thousands of cloud functions for rapid reconnaissance and data processing.
 owasp/dvsa
a Damn Vulnerable Serverless Application
 we45/dvfaas-damn-vulnerable-functions-as-a-service
Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
 owasp/serverless-top-10-project
OWASP Serverless Top 10
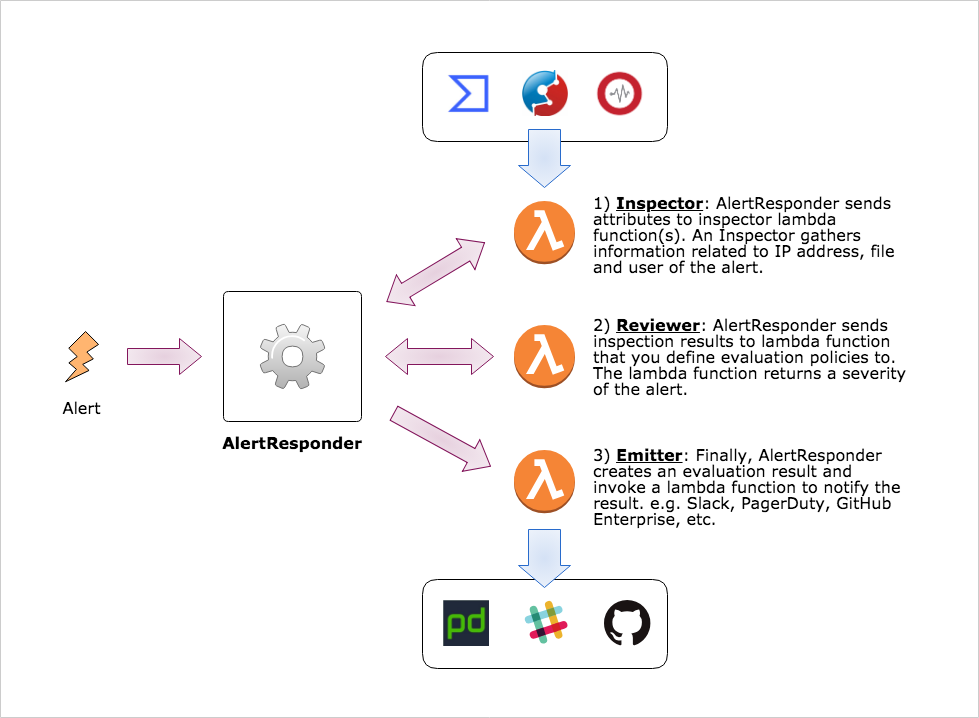 m-mizutani/alertresponder
Automatic security alert response framework by AWS Serverless Application Model
 airbnb/binaryalert
BinaryAlert: Serverless, Real-time & Retroactive Malware Detection.
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
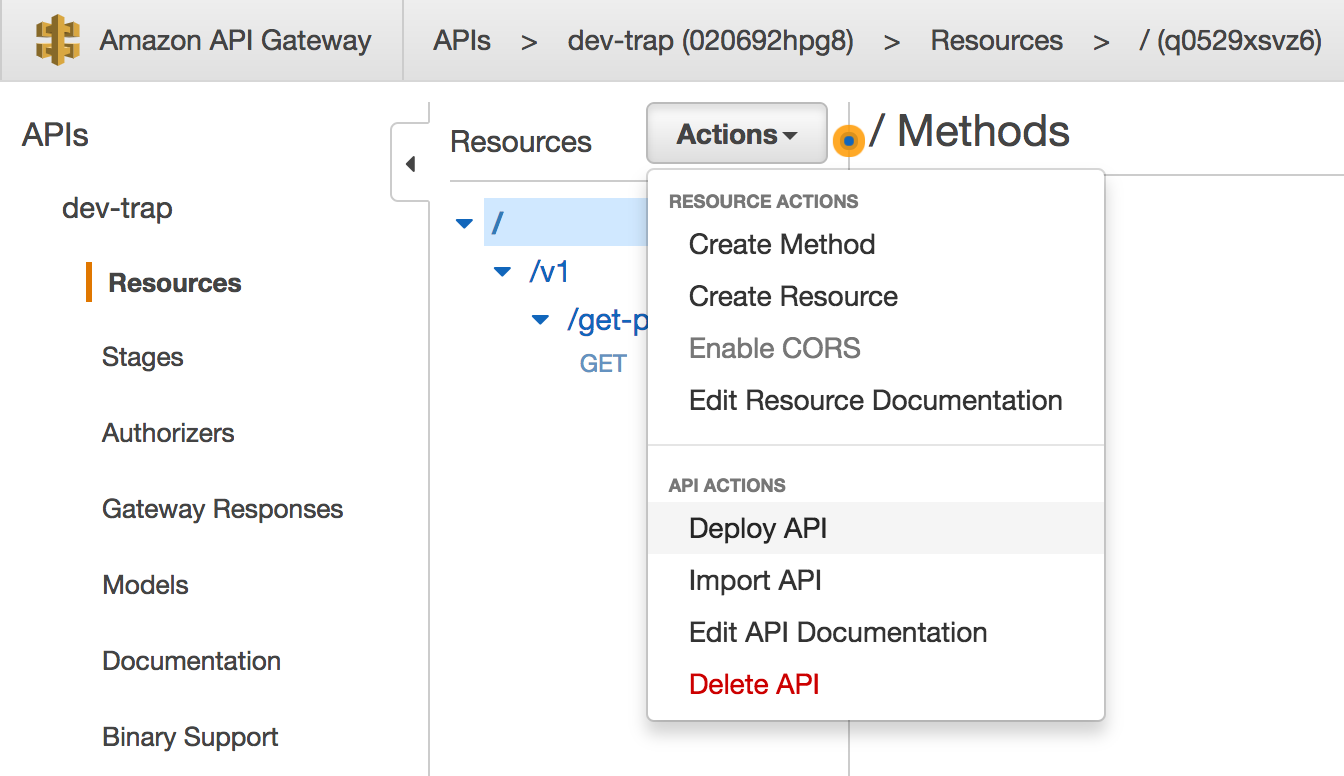 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…