
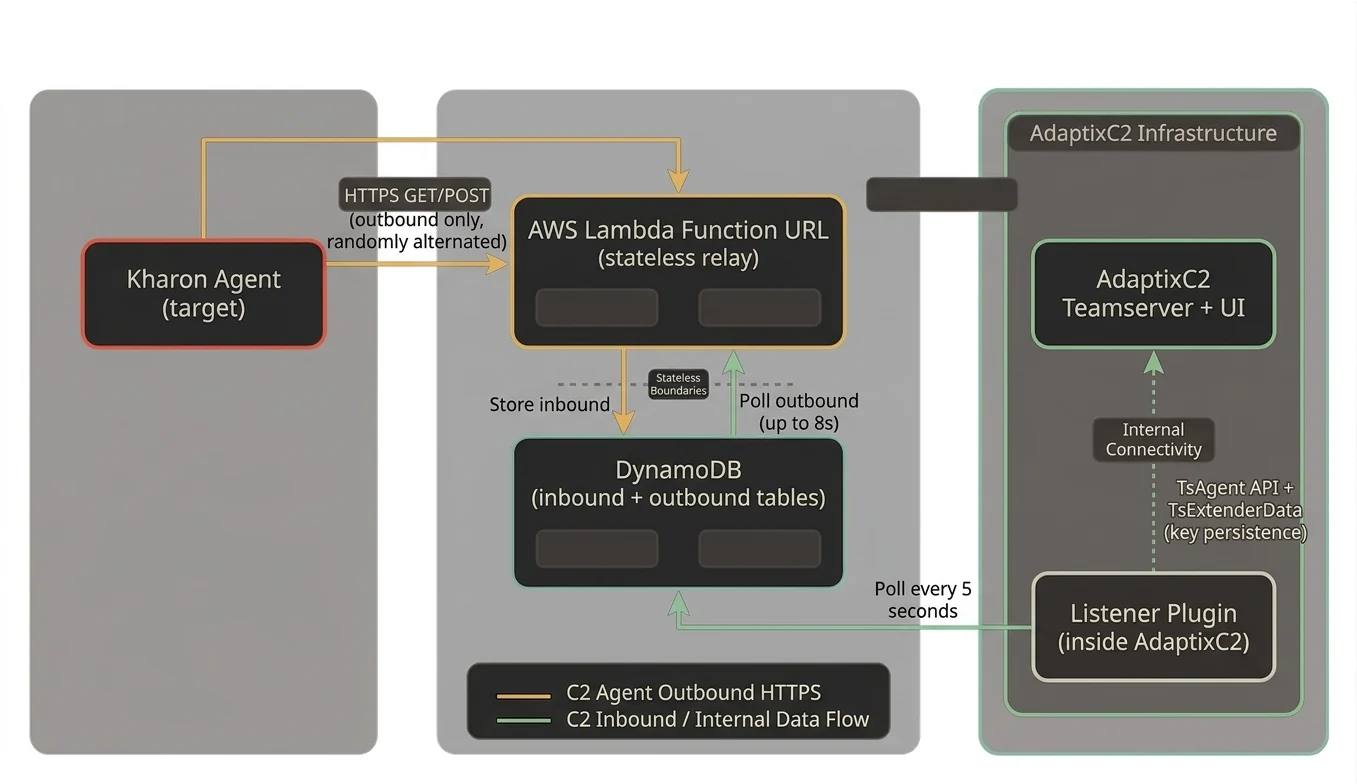
adaptix-serverless-c2
 stillbigjosh/adaptix-serverless-c2
Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.
cloud-infrastructure-securitycloud-securitycommand-and-control+8
33
stillbigjosh/adaptix-serverless-c2Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 ivanesk315/cve-2026-28496
Docker lab reproducing the FOSSBilling pre-auth RCE chain (CVE-2026-27604 auth bypass + CVE-2026-28496 Twig SSTI) with a Python PoC and patched…
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 george0papasotiriou/cve-2026-21002-serverless-cold-start-credential-leakage-via-reused-tmp
PoC exploit for CVE-2026-21002 serverless cold-start credential leakage, demonstrating how reused Lambda /tmp directories expose AWS secrets to other…
 george0papasotiriou/cve-2026-23007-serverless-cold-start-memory-remanence-data-leakage-
Simulates CVE-2026-23007 serverless cold-start memory remanence; demonstrates how persistent global state across Lambda invocations can leak secrets…
 george0papasotiriou/cve-2026-9999-serverless-event-injection-to-code-overwrite
Proof-of-concept exploit for CVE-2026-9999, demonstrating path traversal in serverless object storage events that overwrites function source code to…
 owasp/dvsa
a Damn Vulnerable Serverless Application
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
 owasp/serverless-top-10-project
OWASP Serverless Top 10
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.