prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Snyk CLI scans and monitors your projects for security vulnerabilities.

CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…

Transforms SAM templates into CloudFormation resources, generating Lambda functions, IAM roles, and policies with built-in serverless best practices.

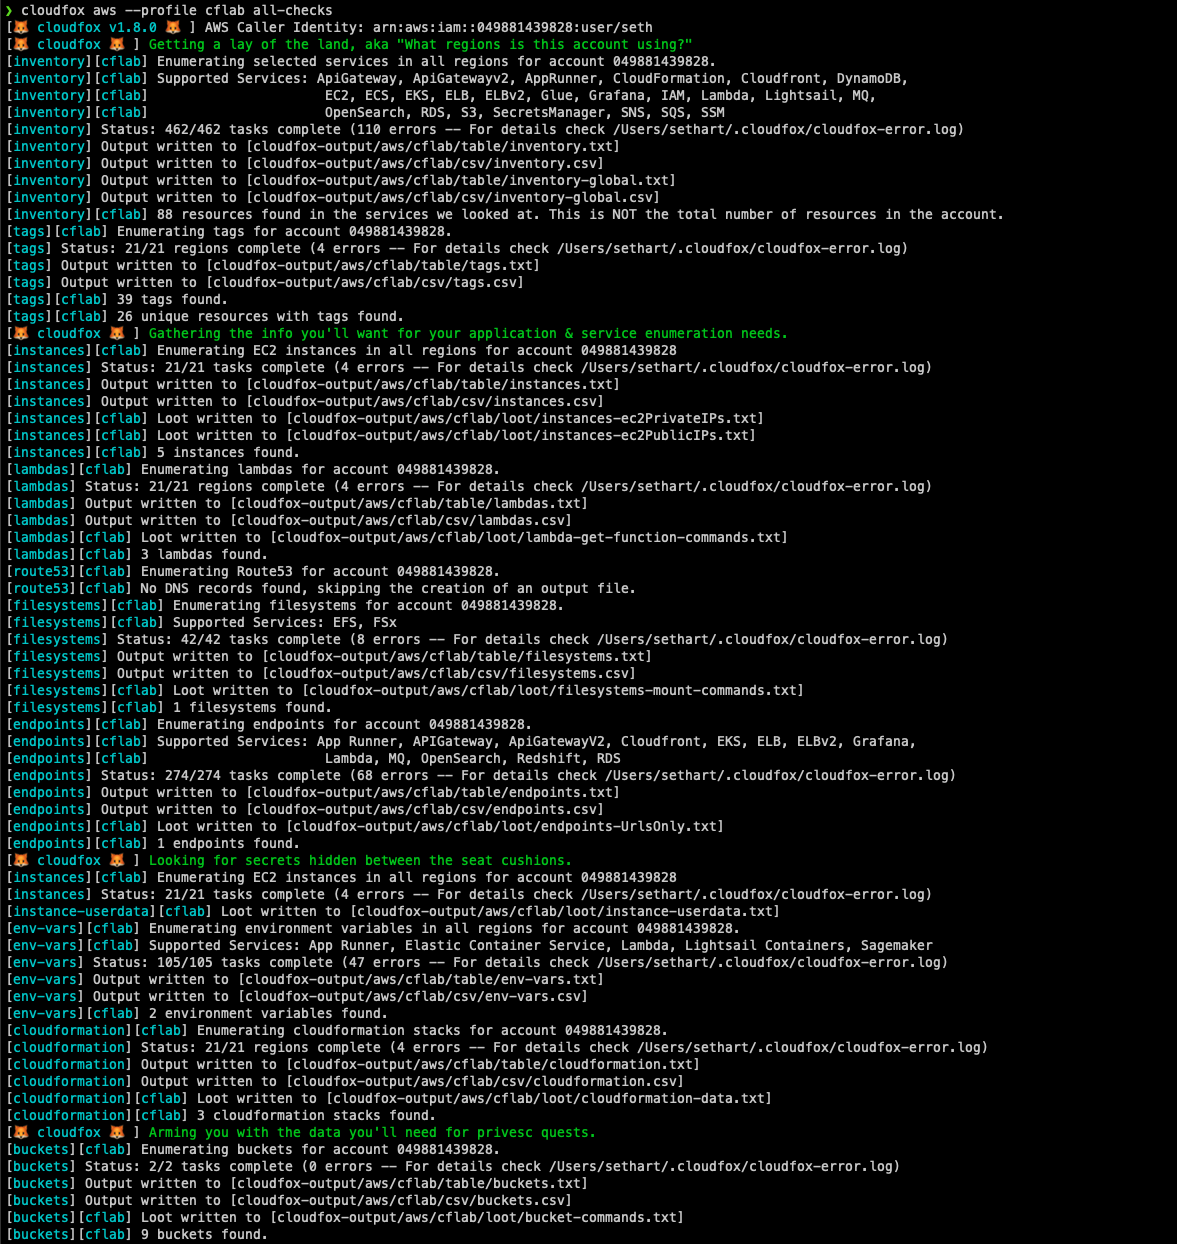
Automating situational awareness for cloud penetration tests.

Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Intentionally Vulnerable Serverless Functions to understand the specifics of Serverless Security Vulnerabilities

:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud

The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.

Serverless task distribution framework that parallelizes CLI tools across thousands of cloud functions for rapid reconnaissance and data processing.

Proof-of-concept exploit for CVE-2026-9999, demonstrating path traversal in serverless object storage events that overwrites function source code to…

CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool

a Damn Vulnerable Serverless Application

OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws

Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions

OWASP Serverless Top 10

SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…