
deny-af-alg-bpf
eBPF LSM program that blocks AF_ALG socket creation to mitigate CVE-2026-31431, with userspace daemon logging denied attempts via ring buffer.

eBPF LSM program that blocks AF_ALG socket creation to mitigate CVE-2026-31431, with userspace daemon logging denied attempts via ring buffer.

Manages the core lifecycle of Qubes OS domains via a Python admin API, handling secure compartmentalization with Xen and exposing an event system for…

JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…

Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…

Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…

Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…

Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…

Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…

Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…

Executes untrusted Python, JavaScript, and Bash in a hardened jail with 5-second, 128 MB, 0.5-core, PID and output limits.

A secure low code deception runtime framework, leveraging AI for System Virtualization.

A durable process per agent, with memory that survives restarts

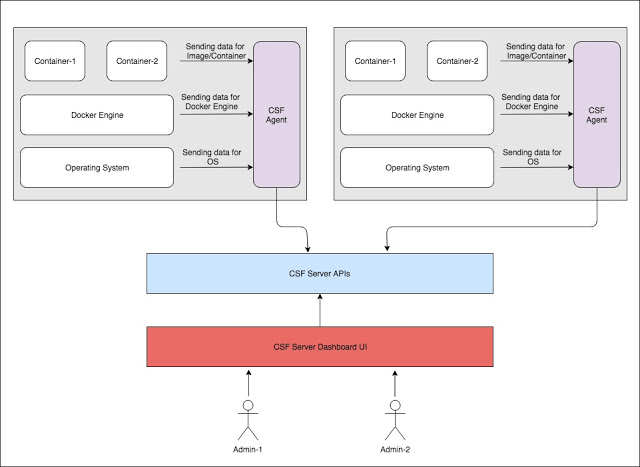
ArmourBird CSF - Container Security Framework

Run untrusted AI code safely, fast

Proof-of-concept lab for a Gitea authorization bypass where a public-only PAT with write:organization creates a private organization via POST…

Domain-specific language for writing fast functional device models for virtual platforms. Compiles DML to C with API calls tailored for the Intel…

Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.

Report summary and local proof-of-concept script demonstrating the unauthenticated WikiLambda fragment execution flaw in CVE-2026-103446.