
cuckoo3
 cert-ee/cuckoo3
Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
dynamic-analysis-sandboxingmalware-analysissecurity-virtualization
cert-ee/cuckoo3Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
 phalanx-ccs/copy-fail
Passive diagnostic tool that checks if a Linux system is vulnerable to CVE-2026-31431 by testing AF_ALG socket reachability, providing mitigation…
 yym8538/cve-2026-40897
Proof-of-concept exploit for CVE-2026-40897, a Math.js expression parser sandbox bypass enabling remote code execution via crafted payloads and a…
 cypherpunkarmory/userland
Main UserLAnd Repository
 nishitm/gobox
GO sandbox to run untrusted code
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 wgnet/wg.copyfail.patch
eBPF-based workaround for CVE-2026-31431 (Copy.Fail) that filters or kills AF_ALG socket creation to prevent local privilege escalation and container…
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 abraxas/n8n-databricks-path-join
Proof-of-concept for an n8n path-traversal (CWE-22) in Databricks nodes: unauthenticated webhook input escapes the Genie path to leak workspace PAT…
 ungabunga-ctf/cve-2026-34990
Python proof-of-concept for CVE-2026-34990 in OpenPrinting CUPS, coercing cupsd to leak a Local auth token and overwrite root files via a file://…
 abraxas/stirling-h2-import-leftover
Stirling-PDF v3.2.0 - Critical - Remote - H2 RUNSCRIPT leftover - CREATE OR REPLACE ALIAS import-database
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 rianjuniorsf/exploit-js2py
The CVE-2024-28397 vulnerability affects versions of js2py up to v0.74, a Python library that allows JavaScript code to be executed within the Python…
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
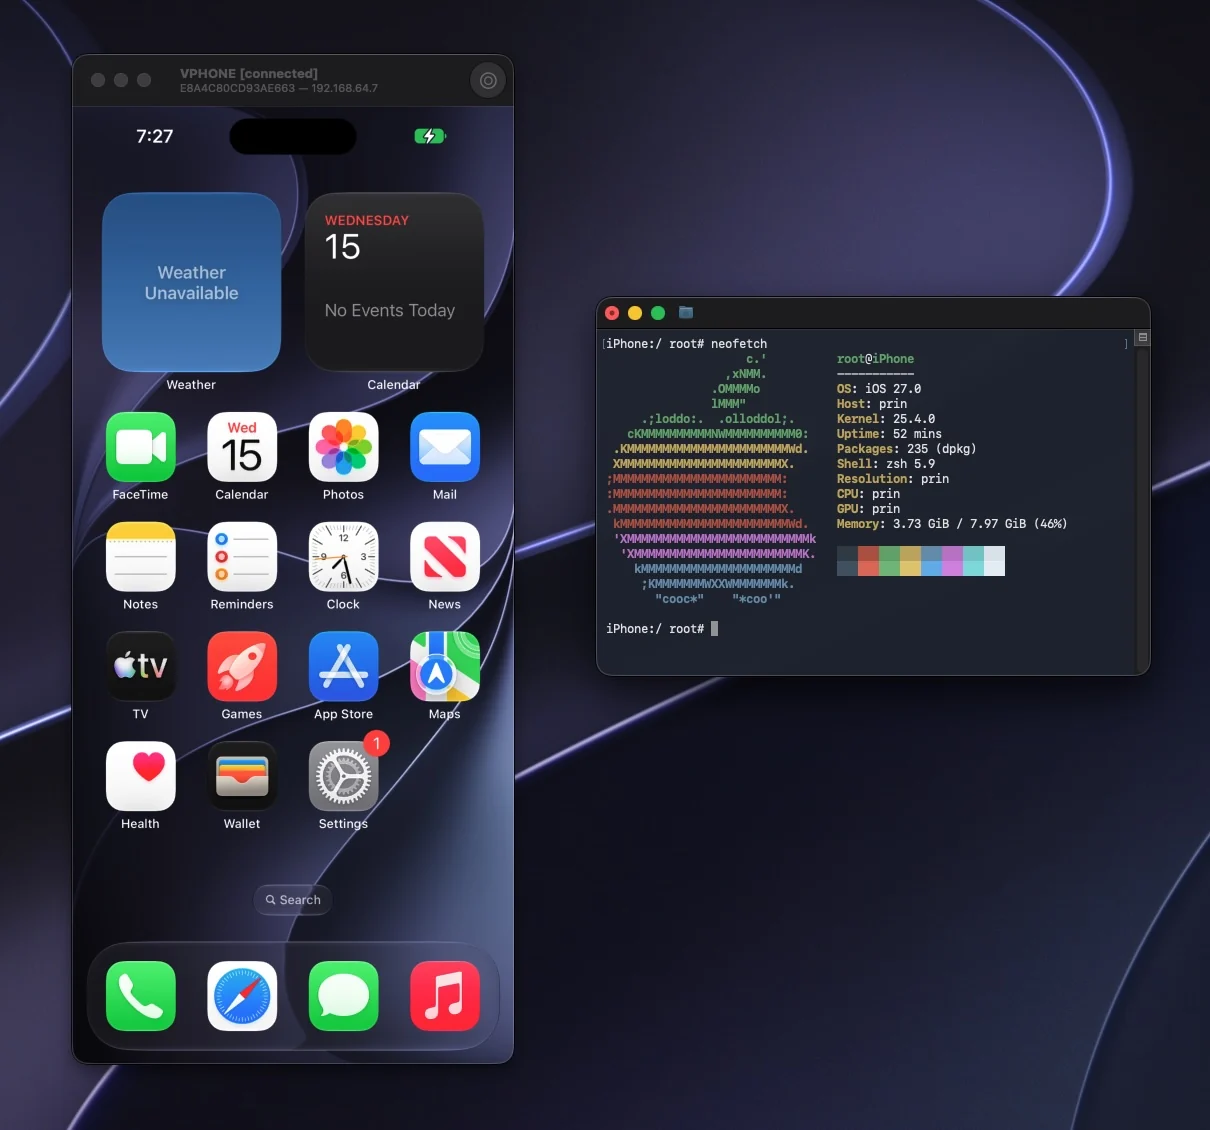 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…