cve-2022-0847-poc-dockerimage

Docker image packaging a proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel privilege escalation vulnerability.

Docker image packaging a proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel privilege escalation vulnerability.

Kali Linux Docker

kali-linux-docker

Run Windows inside a Docker container with KVM acceleration, automatic installation, and customizable resources. Supports multiple Windows versions,…

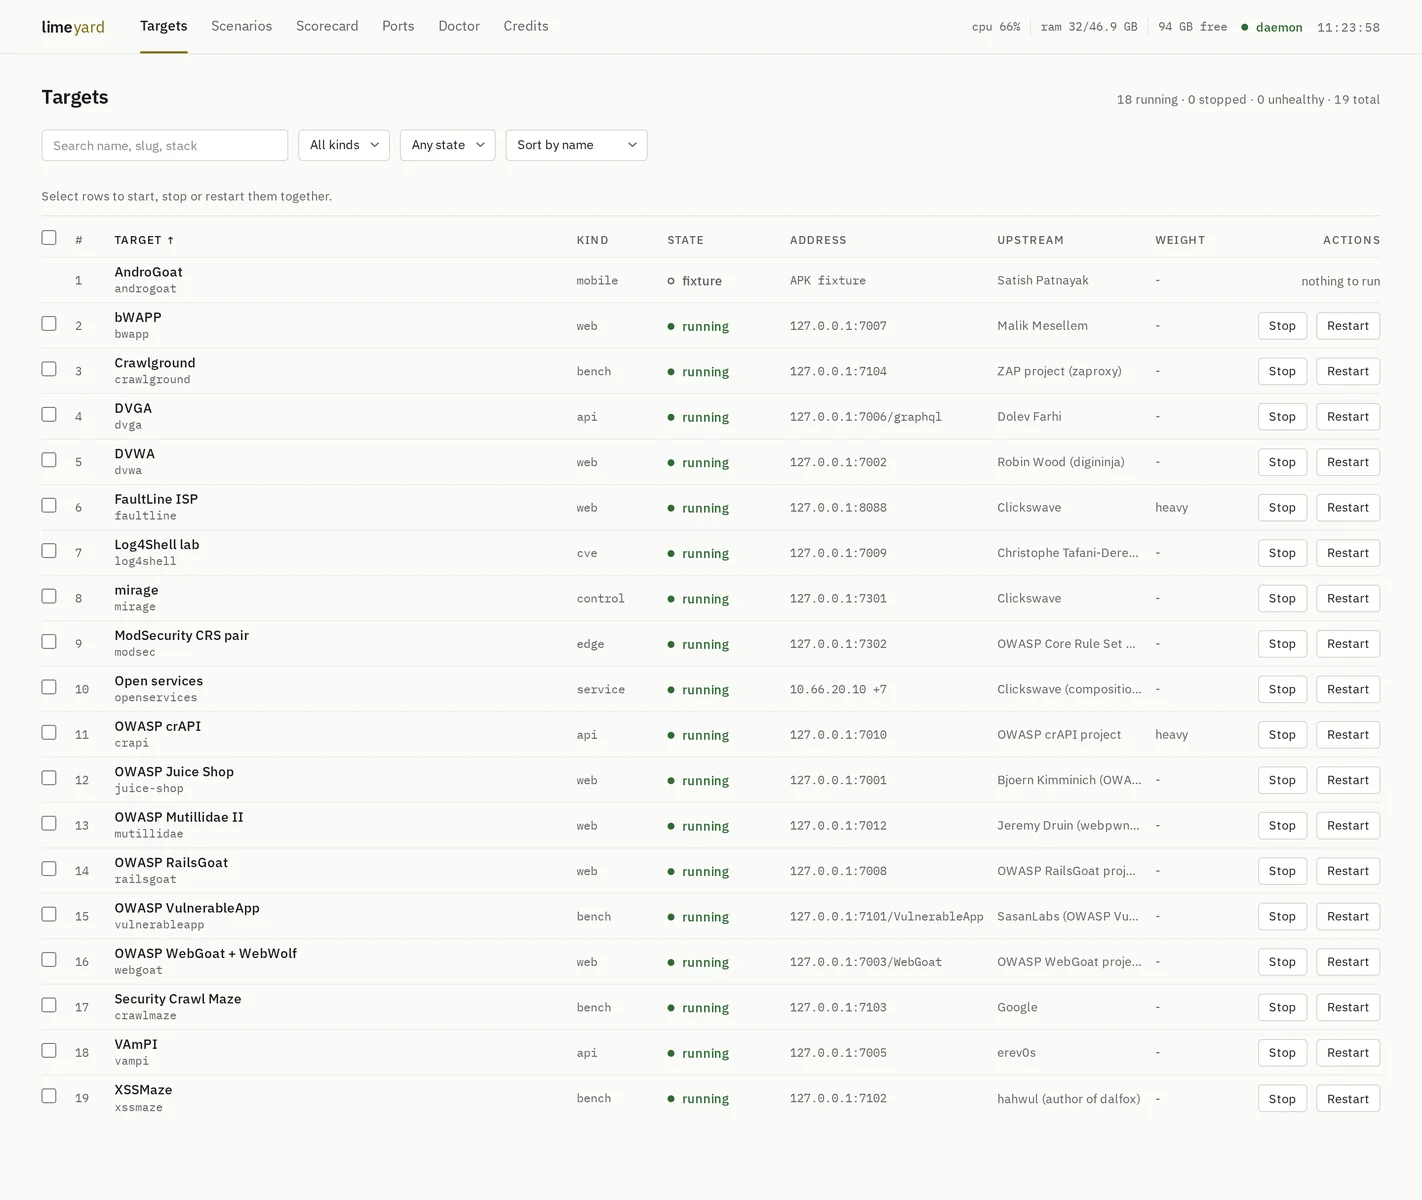
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…

JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…

WASM sandbox with capability enforcement for AI agent code. Agents can only call explicitly provided tools with defined constraints. Sandboxed…

Low-level unprivileged sandboxing tool used by Flatpak and similar projects

A Microservices-based framework for the study of Network Security and Penetration Test techniques

Cross Distribution Exploit Testing

Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.

Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML

Linux application sandboxing and distribution framework

A security-focused library OS supporting kernel- and user-mode execution

Sandboxed devcontainer for running Claude Code in bypass mode safely. Built for security audits and untrusted code review.

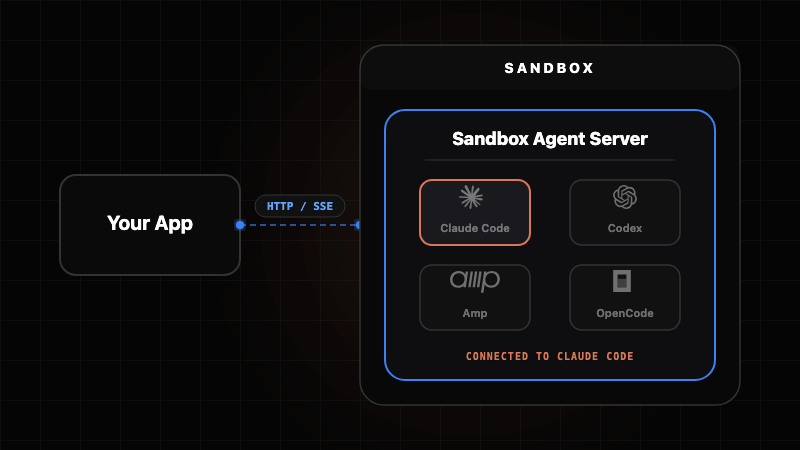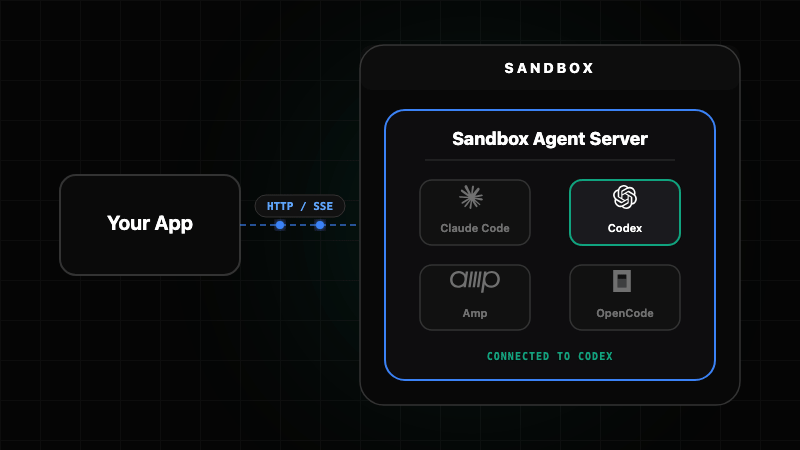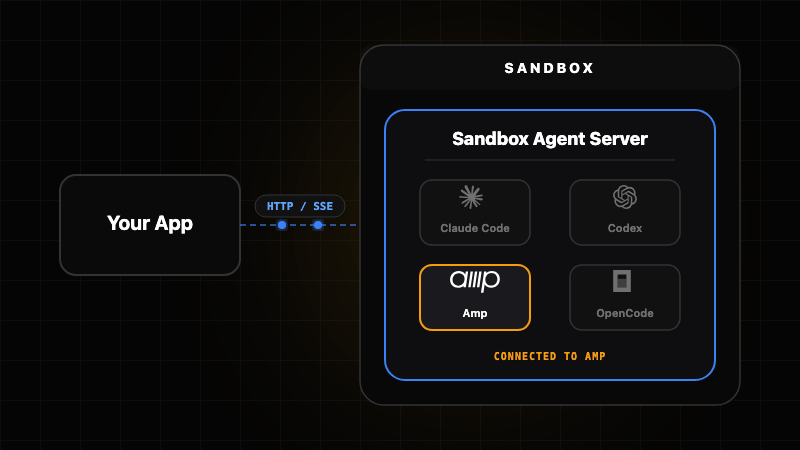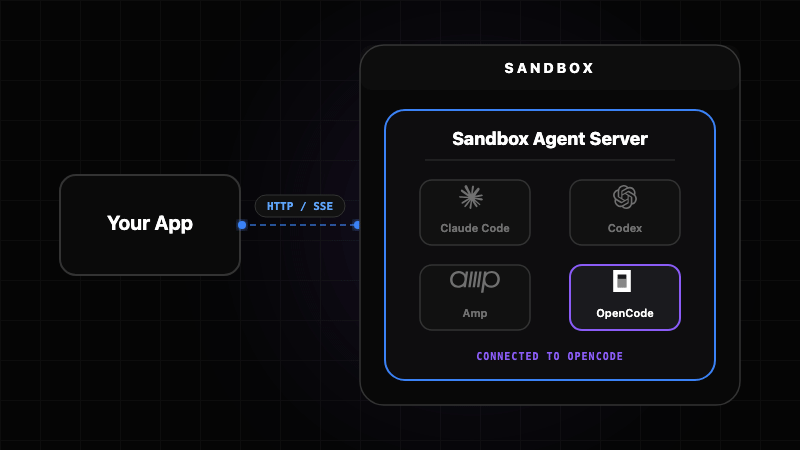
Run Coding Agents in Sandboxes. Control Them Over HTTP. Supports Claude Code, Codex, OpenCode, and Amp.

A local sandbox for your AI agents

Let your AI go full send. Your home directory stays home.