
CVE-2026-64531
 0xblackash/cve-2026-64531
Reference analysis of a Linux kernel Open vSwitch memory-corruption vulnerability, covering root cause, impact, detection commands, and mitigation…
cloud-infrastructure-securityeducationnetwork-security+2
2
0xblackash/cve-2026-64531Reference analysis of a Linux kernel Open vSwitch memory-corruption vulnerability, covering root cause, impact, detection commands, and mitigation…
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 gerhart01/hyperv_local_dos_poc
CVE-2020-0890 | Windows Hyper-V Denial of Service Vulnerability proof-of-concept code
 anantaakotal/agentcyte
Generates reproducible CORE network topologies from XML scenario files for cybersecurity training and experimentation. Provides Web GUI and CLI for…
 aarif450/aarif450.github.io
Exploit KVM/x86 guest-to-host escape CVE-2026-64561 with Zapscape, a proof-of-concept demonstrating hypervisor vulnerability.
 atiilla/cve-2026-2441_poc
Proof-of-concept exploit for CVE-2026-2441, demonstrating the vulnerability and providing a working exploit for security testing and validation.
 nikeee/cve-2026-27607
Proof-of-concept exploit for CVE-2026-27607, a missing post-policy validation in RustFS, demonstrating the vulnerability with a Node.js script and…
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 fevar54/cve-2026-76461-detection-kit-
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…
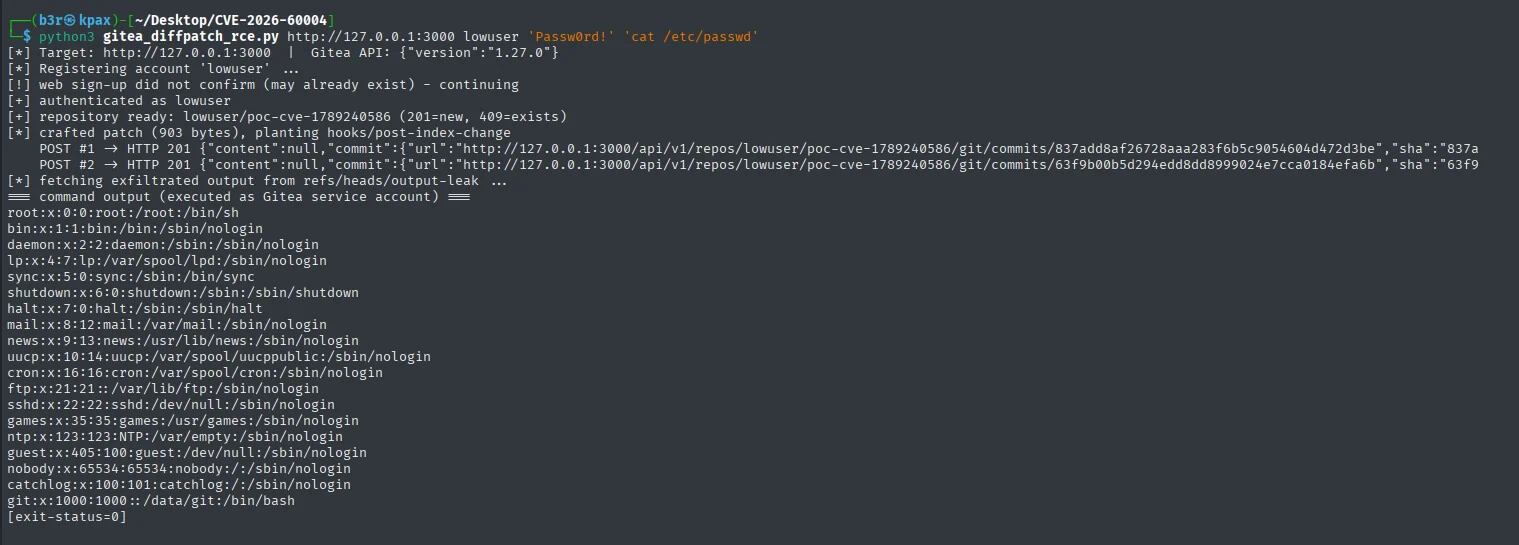 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
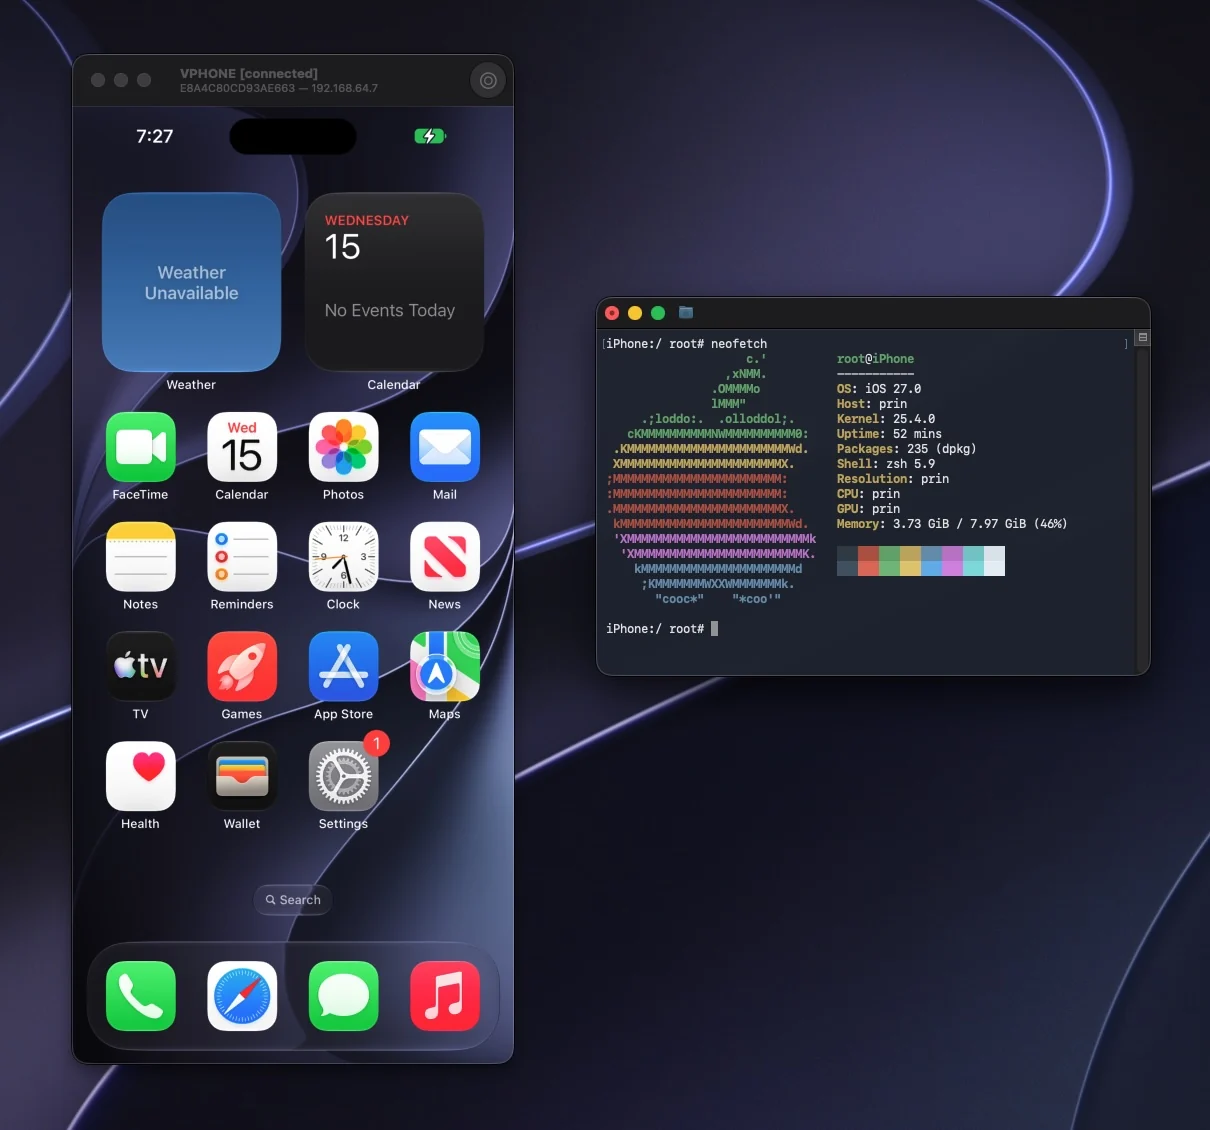 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 squeeze440/supernote-obsidian-plugin-poc
PoC — path traversal via malicious device sync in the Supernote Obsidian plugin (GHSA-3gx3-r874-5pp4, CVE-2026-86999, CVSS 5.6).