
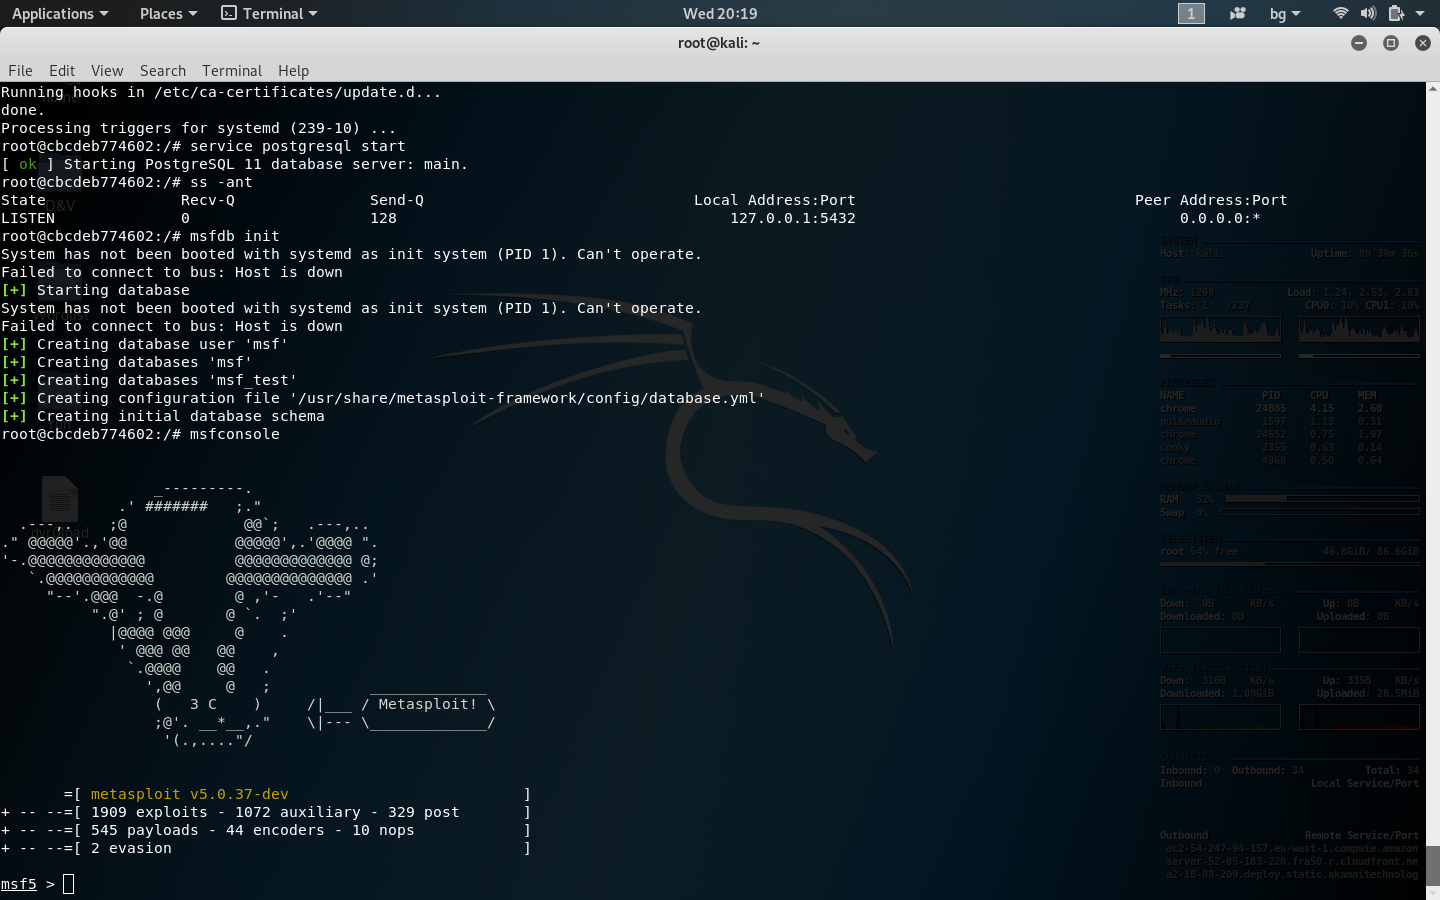
kali-linux-docker
 nu11secur1ty/kali-linux-docker
kali-linux-docker
cloud-securitycontainer-securitydevsecops+8
16 years ago
nu11secur1ty/kali-linux-dockerkali-linux-docker
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 cisagov/esxiargs-recover
A tool to recover from ESXiArgs ransomware
 nikeee/cve-2026-27607
Proof-of-concept exploit for CVE-2026-27607, a missing post-policy validation in RustFS, demonstrating the vulnerability with a Node.js script and…
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 ionescu007/simplevisor
Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…
 orangecertcc/security-research
Hosts Orange CERT security advisories with accompanying proof-of-concept code for disclosed vulnerabilities, organized by CVE identifier.
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 nicolasriverocorvalan/cloud-sniper
Virtual Security Operations Center
 guneykabel/cve-2026-85706
Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…
 predyy/cve-2026-34990
Minimal PoC for CVE-2026-34990: local privilege escalation in CUPS <= 2.4.16 that leaks cupsd's Local auth token and writes a NOPASSWD sudoers…
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 abraxas/cve-2026-52782
Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
 ungabunga-ctf/cve-2026-34990
Python proof-of-concept for CVE-2026-34990 in OpenPrinting CUPS, coercing cupsd to leak a Local auth token and overwrite root files via a file://…
 fevar54/cve-2026-76461-detection-kit-
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…
 bombobombone/cve-2026-102971
Sanitized report and loopback-only PoC for CVE-2026-102971, a MediaWiki REST revision response leaking hidden revision author user IDs.
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction