
litebox
 microsoft/litebox
A security-focused library OS supporting kernel- and user-mode execution
cloud-securitycontainer-securityembedded-systems-security+1
2.7k
microsoft/liteboxA security-focused library OS supporting kernel- and user-mode execution
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 microsoft/mxc
Policy-driven, layered isolation and containment
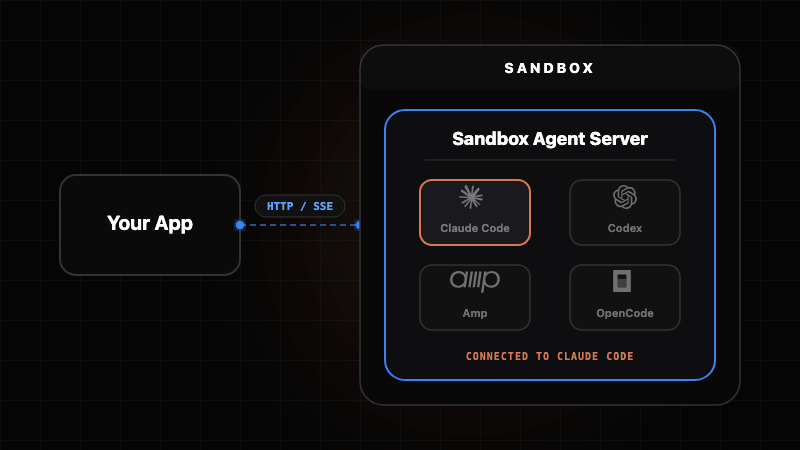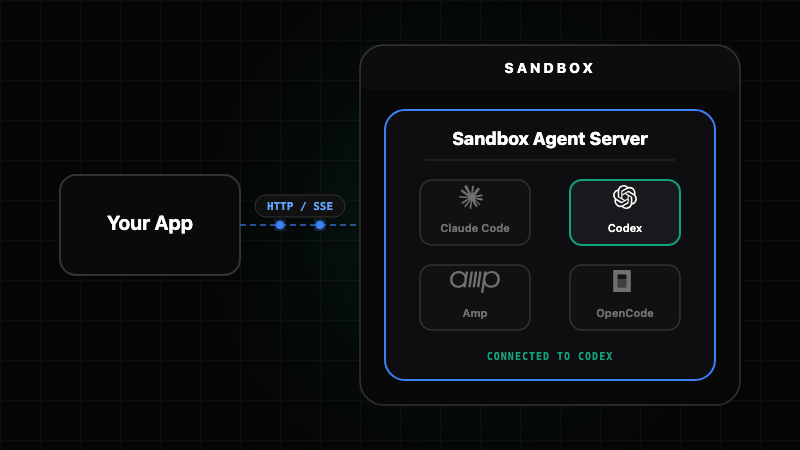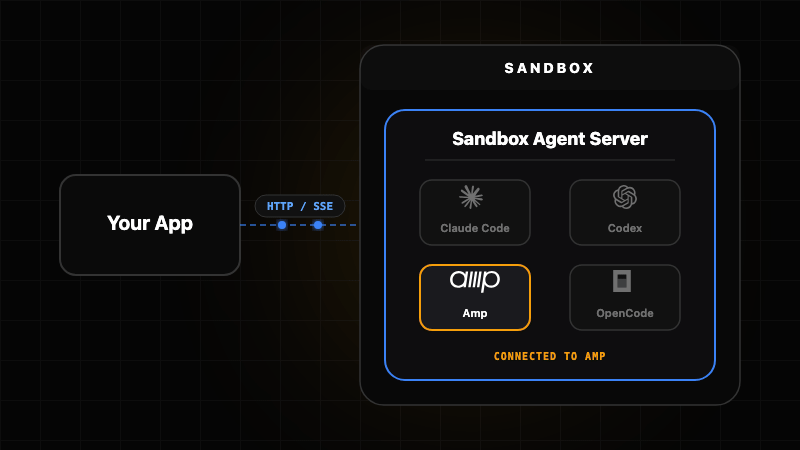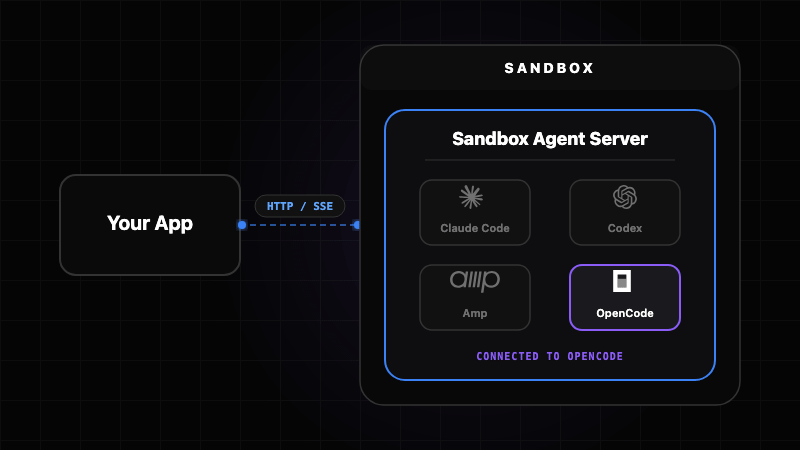 rivet-dev/sandbox-agent
Run Coding Agents in Sandboxes. Control Them Over HTTP. Supports Claude Code, Codex, OpenCode, and Amp.
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
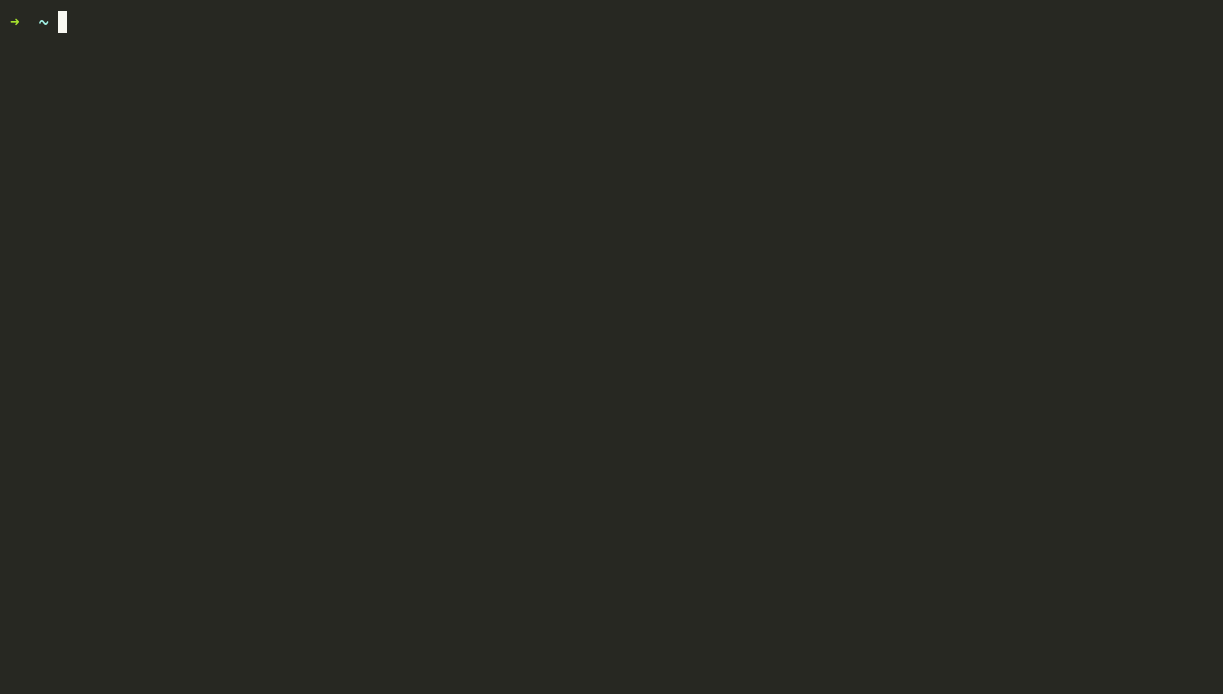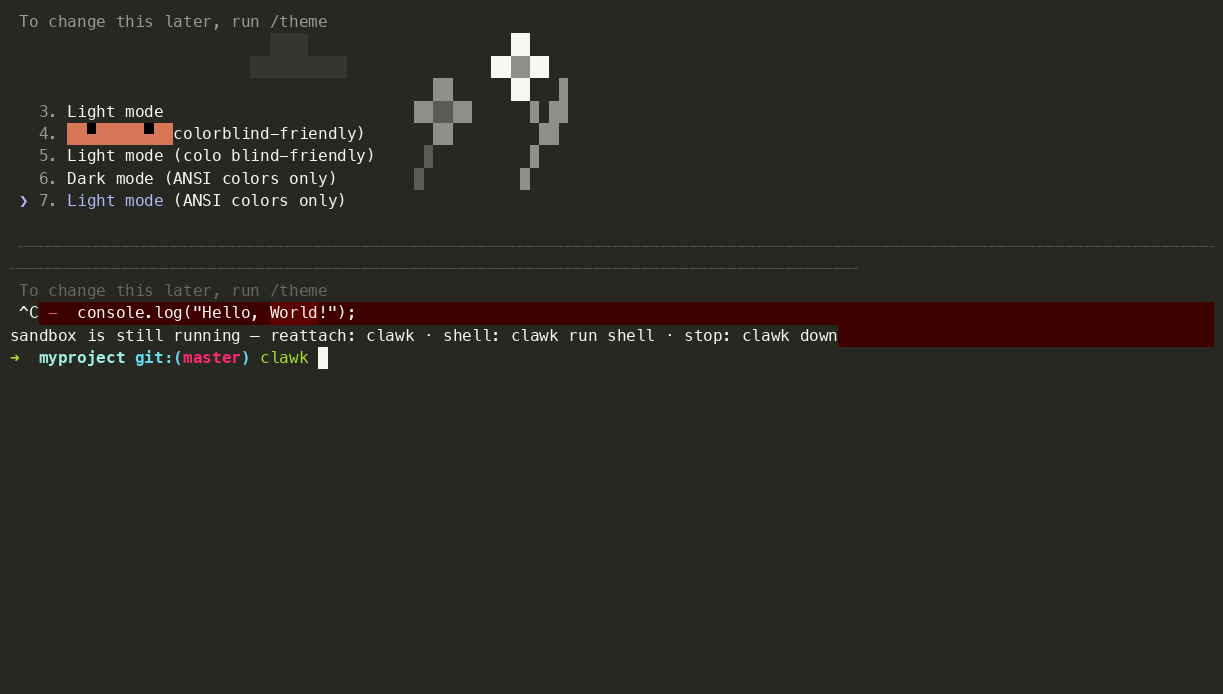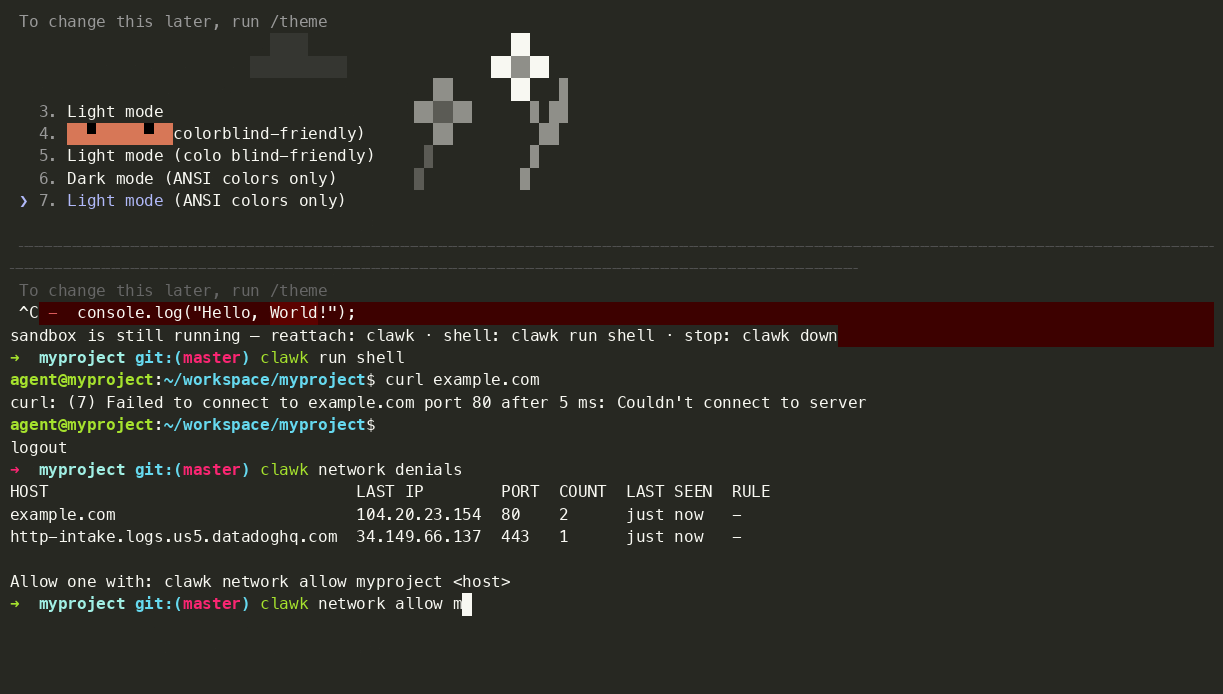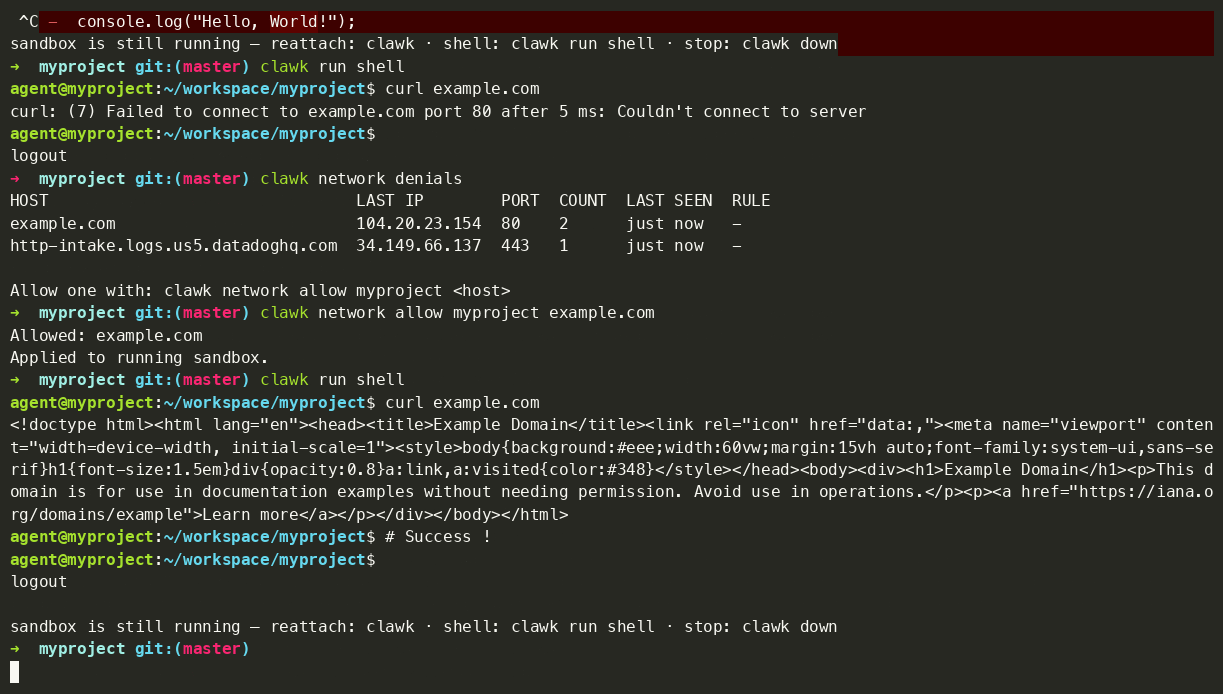 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 nccgroup/wubes
Qubes containerization on Windows
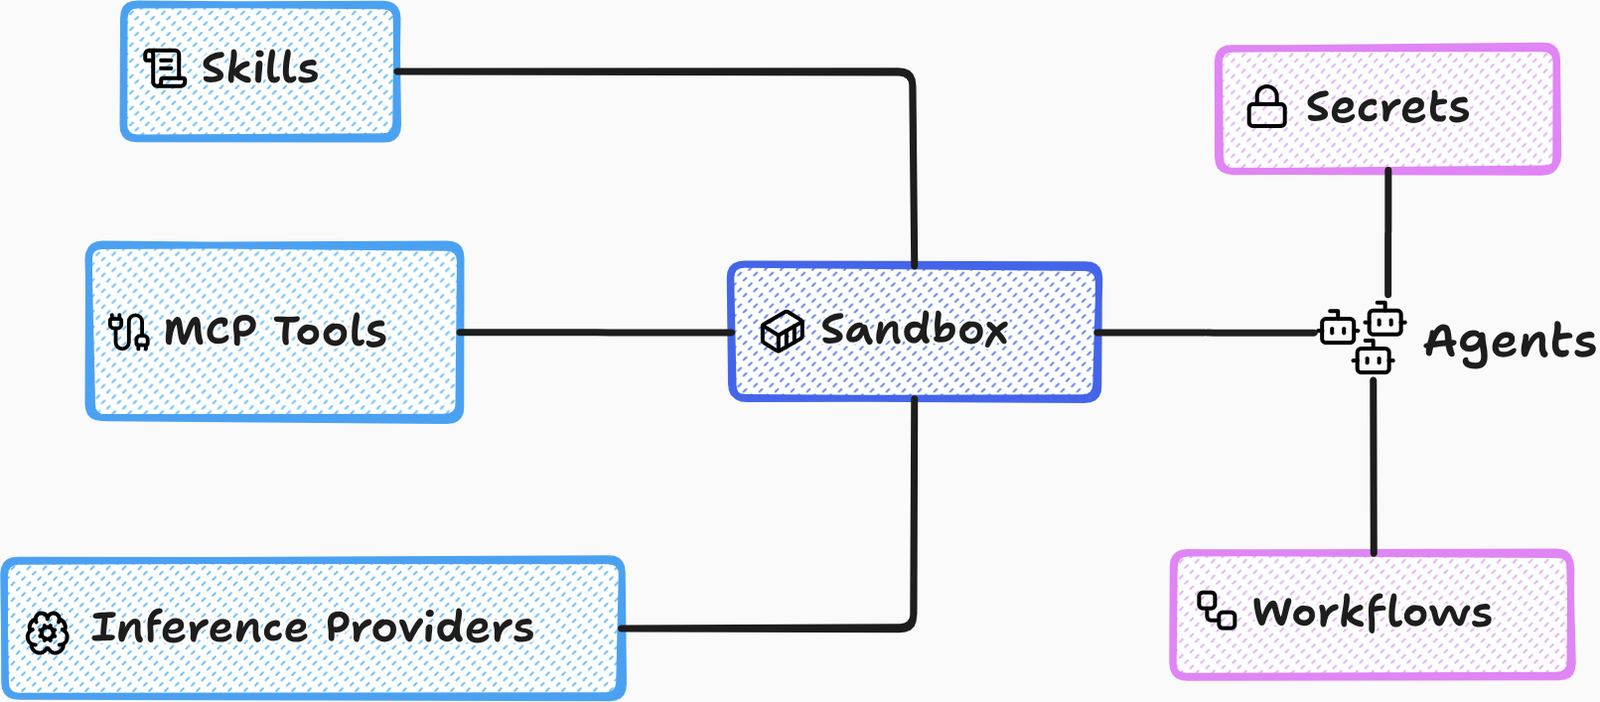 accuknox/agentz
Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.
 pwnfunction/sandbox
Run untrusted AI code safely, fast
 nicolasriverocorvalan/cloud-sniper
Virtual Security Operations Center
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
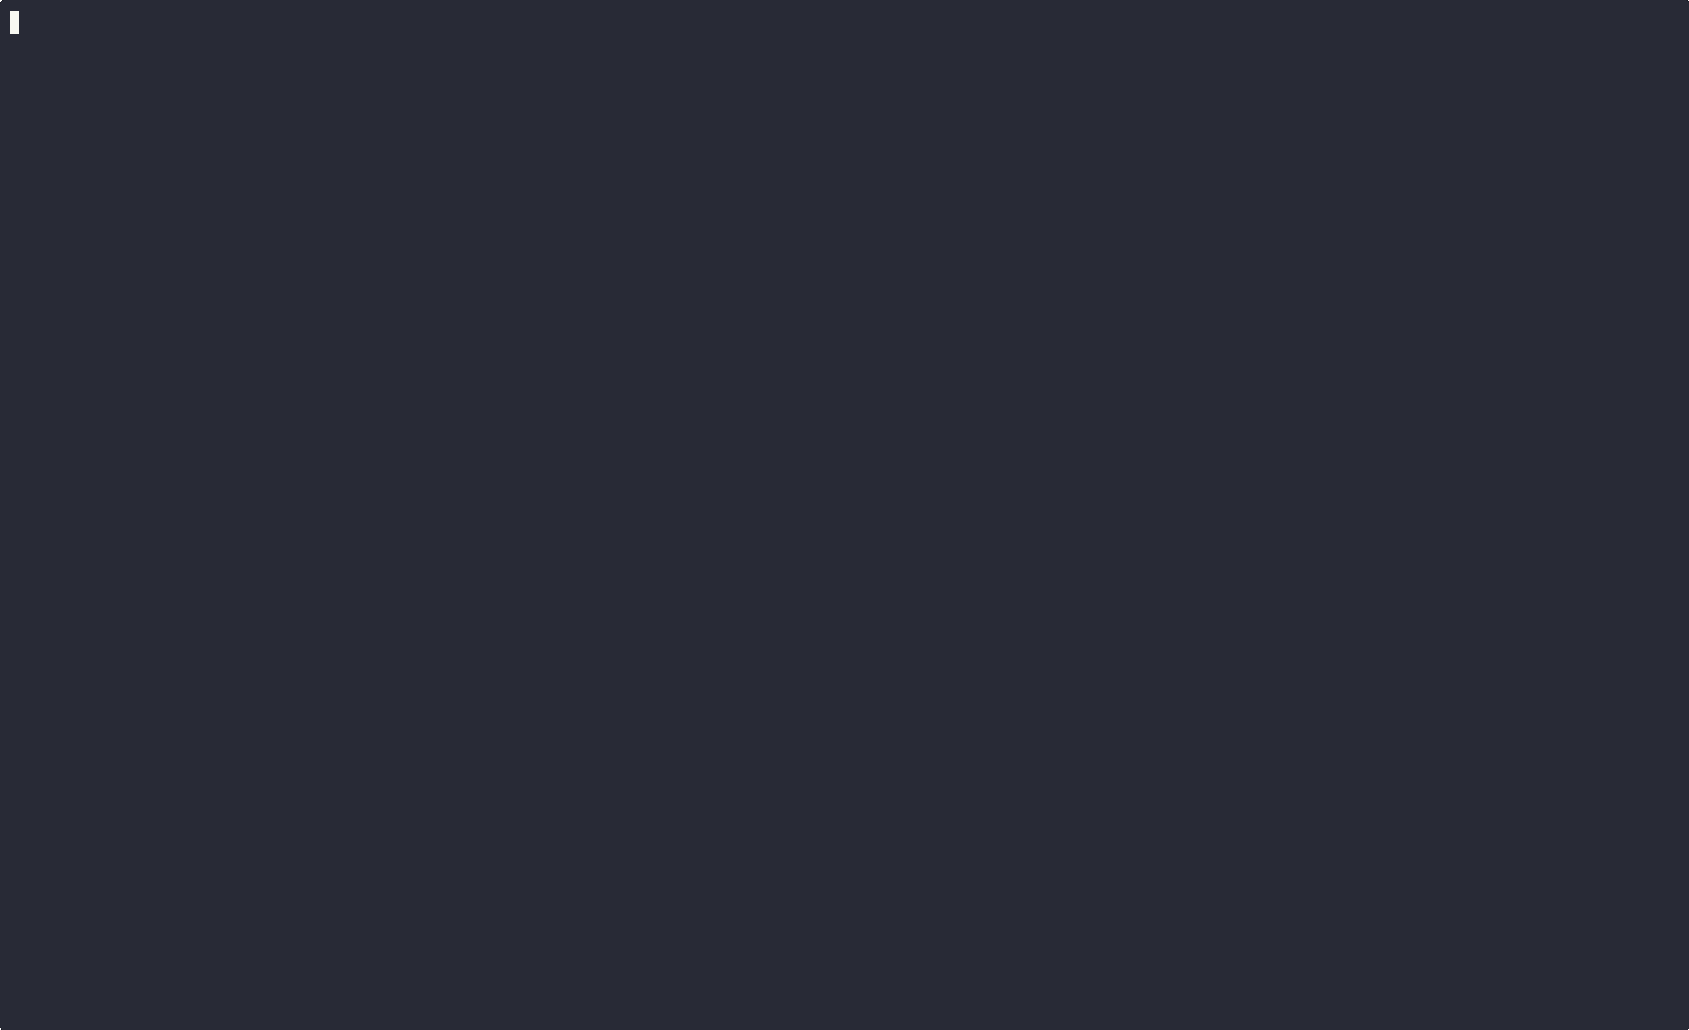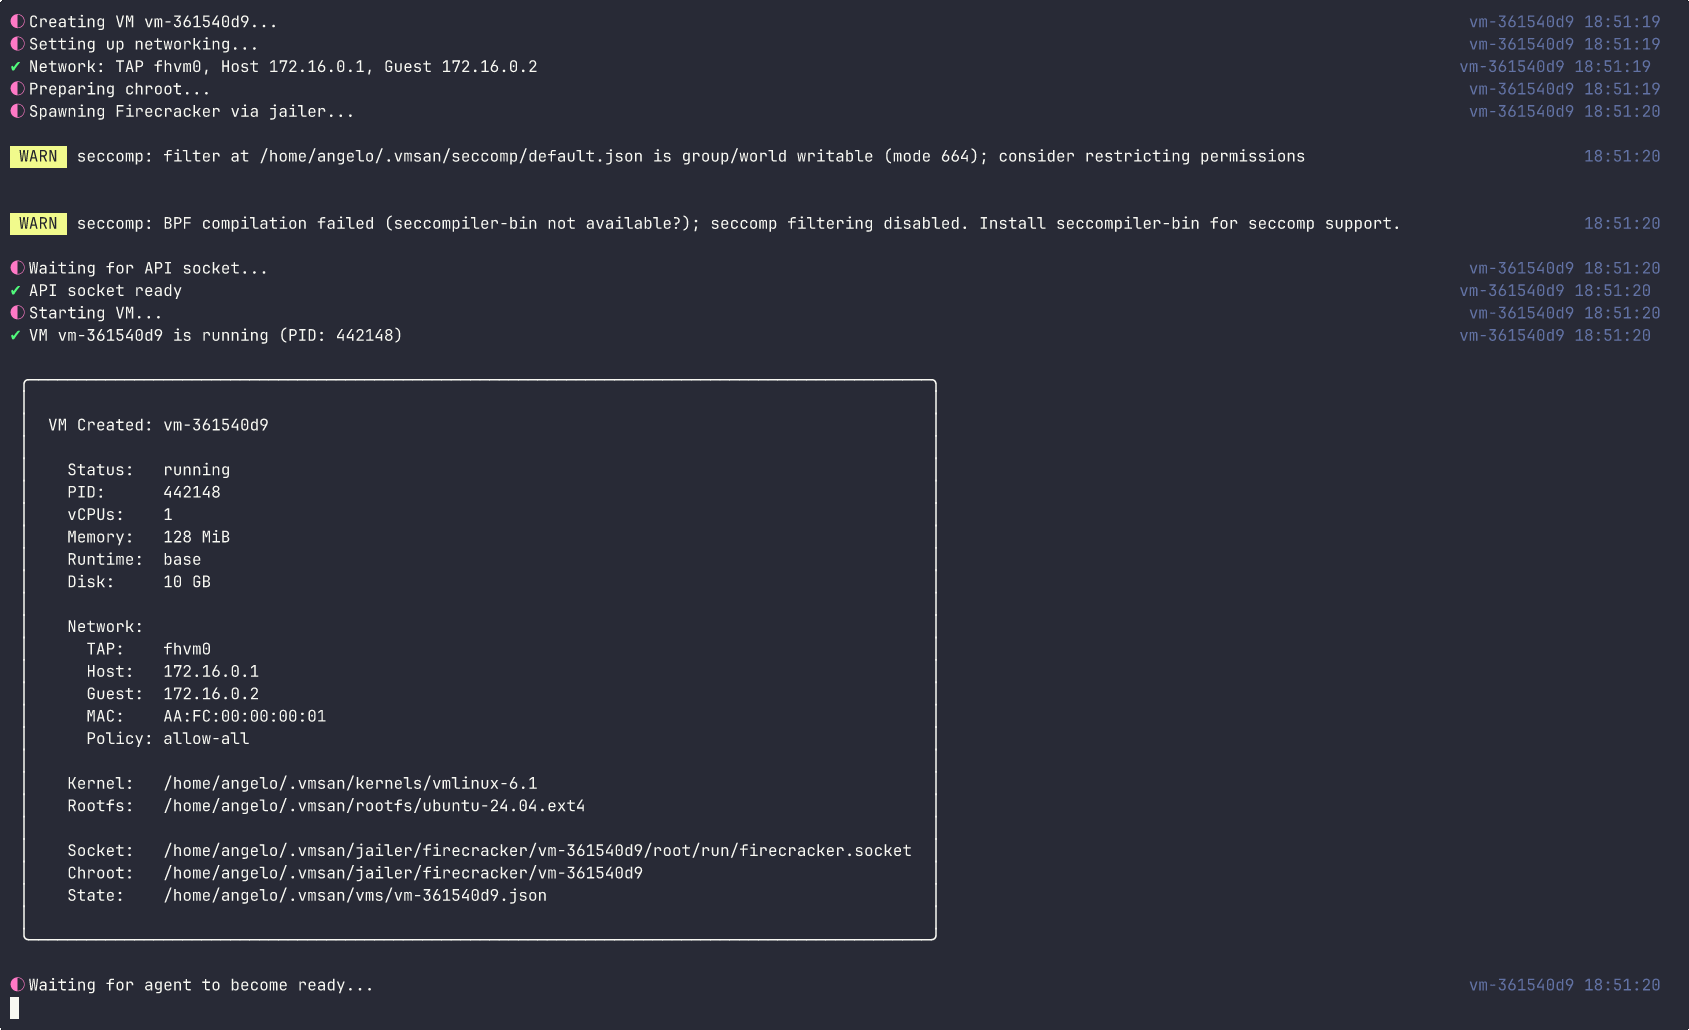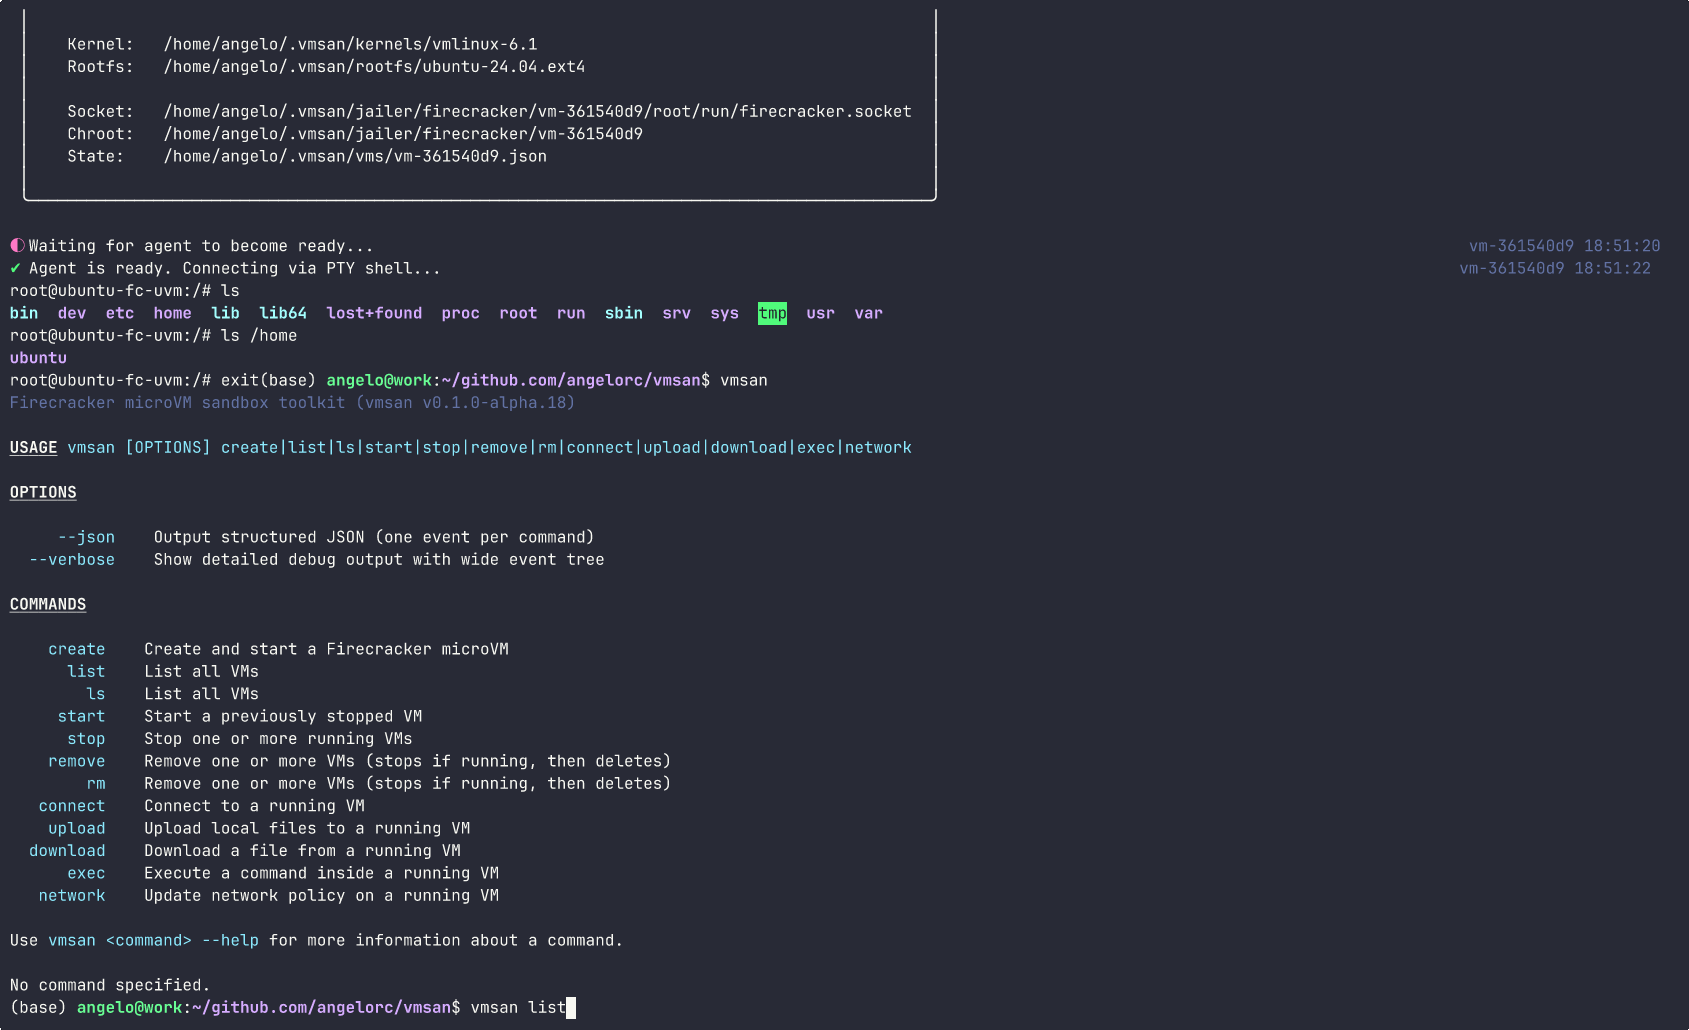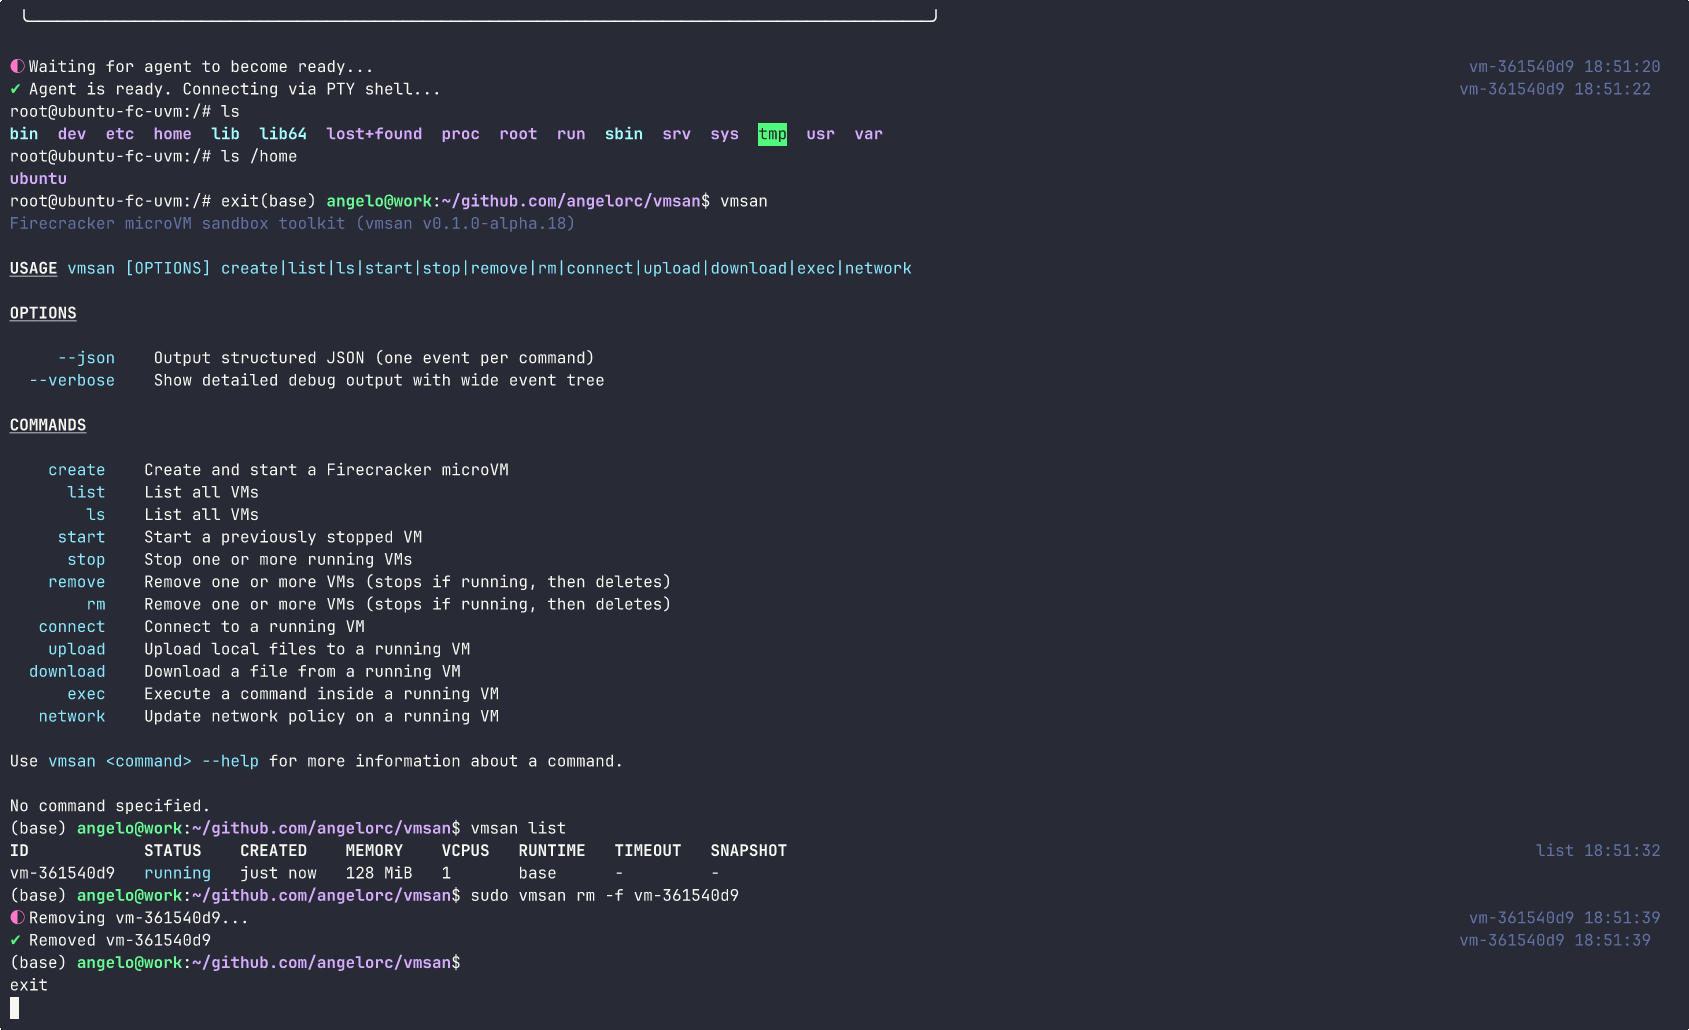 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 infobyte/distro_checker
Cross Distribution Exploit Testing
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
 squeeze440/zotlit-poc
PoC — attachment import copies files from unapproved local paths in ZotLit (GHSA-4qh7-66xv-h329, CVE-2026-87000, CVSS 5.5).